Blog
/
Network
/
April 22, 2025

Obfuscation Overdrive: Next-Gen Cryptojacking with Layers

Docker is a prime target for malware, with new strains emerging daily. This blog explores a novel campaign showcasing advanced obfuscation and cryptojacking techniques.
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Nate Bill
Threat Researcher
man looking at multiple computer screensDefault blog image
22
Apr 2025

Out of all the services honeypotted by Darktrace, Docker is the most commonly attacked, with new strains of malware emerging daily. This blog will analyze a novel malware campaign with a unique obfuscation technique and a new cryptojacking technique.

What is obfuscation?

Obfuscation is a common technique employed by threat actors to prevent signature-based detection of their code, and to make analysis more difficult. This novel campaign uses an interesting technique of obfuscating its payload.

Docker image analysis

The attack begins with a request to launch a container from Docker Hub, specifically the kazutod/tene:ten image. Using Docker Hub’s layer viewer, an analyst can quickly identify what the container is designed to do. In this case, the container is designed to run the ten.py script which is built into itself.

 Docker Hub Image Layers, referencing the script ten.py.
Figure 1: Docker Hub Image Layers, referencing the script ten.py.

To gain more information on the Python file, Docker’s built in tooling can be used to download the image (docker pull kazutod/tene:ten) and then save it into a format that is easier to work with (docker image save kazutod/tene:ten -o tene.tar). It can then be extracted as a regular tar file for further investigation.
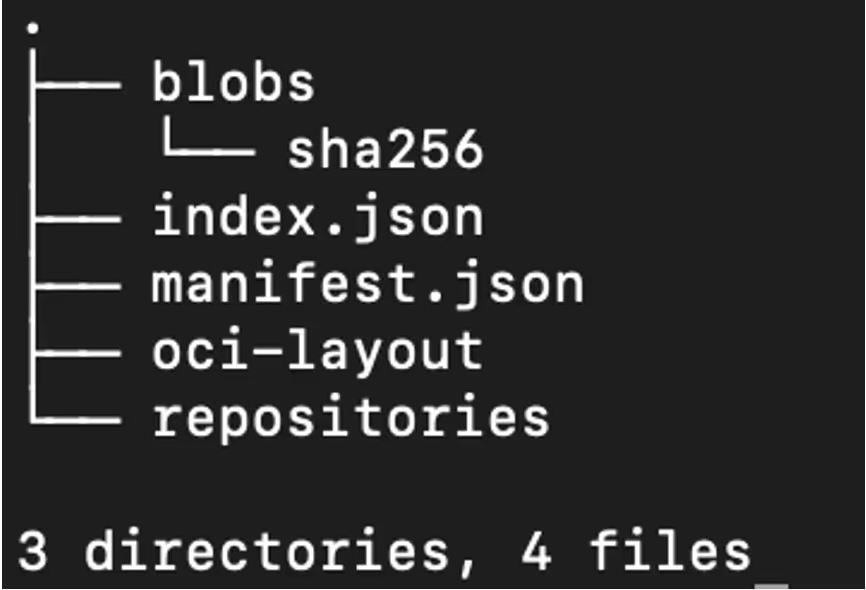
Extraction of the resulting tar file.
Figure 2: Extraction of the resulting tar file.

The Docker image uses the OCI format, which is a little different to a regular file system. Instead of having a static folder of files, the image consists of layers. Indeed, when running the file command over the sha256 directory, each layer is shown as a tar file, along with a JSON metadata file.

Output of the file command over the sha256 directory.
Figure 3: Output of the file command over the sha256 directory.

As the detailed layers are not necessary for analysis, a single command can be used to extract all of them into a single directory, recreating what the container file system would look like:

find blobs/sha256 -type f -exec sh -c 'file "{}" | grep -q "tar archive" && tar -xf "{}" -C root_dir' \;

Result of running the command above.
Figure 4: Result of running the command above.

The find command can then be used to quickly locate where the ten.py script is.

find root_dir -name ten.py

root_dir/app/ten.py

Details of the above ten.py script.
Figure 5: Details of the above ten.py script.

This may look complicated at first glance, however after breaking it down, it is fairly simple. The script defines a lambda function (effectively a variable that contains executable code) and runs zlib decompress on the output of base64 decode, which is run on the reversed input. The script then runs the lambda function with an input of the base64 string, and then passes it to exec, which runs the decoded string as Python code.

To help illustrate this, the code can be cleaned up to this simplified function:

def decode(input):
   reversed = input[::-1]

   decoded = base64.decode(reversed)
   decompressed = zlib.decompress(decoded)
   return decompressed

decoded_string = decode(the_big_text_blob)
exec(decoded_string) # run the decoded string

This can then be set up as a recipe in Cyberchef, an online tool for data manipulation, to decode it.

Use of Cyberchef to decode the ten.py script.
Figure 6: Use of Cyberchef to decode the ten.py script.

The decoded payload calls the decode function again and puts the output into exec. Copy and pasting the new payload into the input shows that it does this another time. Instead of copy-pasting the output into the input all day, a quick script can be used to decode this.

The script below uses the decode function from earlier in order to decode the base64 data and then uses some simple string manipulation to get to the next payload. The script will run this over and over until something interesting happens.

# Decode the initial base64

decoded = decode(initial)
# Remove the first 11 characters and last 3

# so we just have the next base64 string

clamped = decoded[11:-3]

for i in range(1, 100):
   # Decode the new payload

   decoded = decode(clamped)
   # Print it with the current step so we

   # can see what’s going on

   print(f"Step {i}")

   print(decoded)
   # Fetch the next base64 string from the

   # output, so the next loop iteration will

   # decode it

   clamped = decoded[11:-3]

Result of the 63rd iteration of this script.
Figure 7: Result of the 63rd iteration of this script.

After 63 iterations, the script returns actual code, accompanied by an error from the decode function as a stopping condition was never defined. It not clear what the attacker’s motive to perform so many layers of obfuscation was, as one round of obfuscation versus several likely would not make any meaningful difference to bypassing signature analysis. It’s possible this is an attempt to stop analysts or other hackers from reverse engineering the code. However,  it took a matter of minutes to thwart their efforts.

Cryptojacking 2.0?

Cleaned up version of the de-obfuscated code.
Figure 8: Cleaned up version of the de-obfuscated code.

The cleaned up code indicates that the malware attempts to set up a connection to teneo[.]pro, which appears to belong to a Web3 startup company.

Teneo appears to be a legitimate company, with Crunchbase reporting that they have raised USD 3 million as part of their seed round [1]. Their service allows users to join a decentralized network, to “make sure their data benefits you” [2]. Practically, their node functions as a distributed social media scraper. In exchange for doing so, users are rewarded with “Teneo Points”, which are a private crypto token.

The malware script simply connects to the websocket and sends keep-alive pings in order to gain more points from Teneo and does not do any actual scraping. Based on the website, most of the rewards are gated behind the number of heartbeats performed, which is likely why this works [2].

Checking out the attacker’s dockerhub profile, this sort of attack seems to be their modus operandi. The most recent container runs an instance of the nexus network client, which is a project to perform distributed zero-knowledge compute tasks in exchange for cryptocurrency.

Typically, traditional cryptojacking attacks rely on using XMRig to directly mine cryptocurrency, however as XMRig is highly detected, attackers are shifting to alternative methods of generating crypto. Whether this is more profitable remains to be seen. There is not currently an easy way to determine the earnings of the attackers due to the more “closed” nature of the private tokens. Translating a user ID to a wallet address does not appear to be possible, and there is limited public information about the tokens themselves. For example, the Teneo token is listed as “preview only” on CoinGecko, with no price information available.

Conclusion

This blog explores an example of Python obfuscation and how to unravel it. Obfuscation remains a ubiquitous technique employed by the majority of malware to aid in detection/defense evasion and being able to de-obfuscate code is an important skill for analysts to possess.

We have also seen this new avenue of cryptominers being deployed, demonstrating that attackers’ techniques are still evolving - even tried and tested fields. The illegitimate use of legitimate tools to obtain rewards is an increasingly common vector. For example,  as has been previously documented, 9hits has been used maliciously to earn rewards for the attack in a similar fashion.

Docker remains a highly targeted service, and system administrators need to take steps to ensure it is secure. In general, Docker should never be exposed to the wider internet unless absolutely necessary, and if it is necessary both authentication and firewalling should be employed to ensure only authorized users are able to access the service. Attacks happen every minute, and even leaving the service open for a short period of time may result in a serious compromise.

References

1. https://www.crunchbase.com/funding_round/teneo-protocol-seed--a8ff2ad4

2. https://teneo.pro/

Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Nate Bill
Threat Researcher

More in this series

No items found.

Blog

/

AI

/

September 17, 2026

The Problem of Re-defining Human Value in the Agentic Age

Default blog imageDefault blog image

Newsfeeds are constantly informing us about the rapid escalation of agentic AI systems. These systems move far beyond simple machine-based computations, and  the focused, defined and bounded assistance that most AI systems started out as.

The next evolution of AI will harness the agentic properties of orchestration, automation, and heightened value-chains in IT, taking on the burden of workflow management, not just workflow delivery.

In nearly all of these instances, promises are made such as ‘this will free up human time’ or ‘this will allow people to focus on higher-order strategy’. However that message is delivered, one thing is clear: in ceding the orchestration and management of work to increasingly sophisticated AI agents and agentic systems, human value will be elevated to a particular and specific layer: the ability to judge its outputs.  As AI takes on more tasks, humans should be able to focus on a higher level of governance; making sure the decisions that AI offers us are ethical, responsible and worthwhile.  

But there are two major problems with that approach.

This blog discusses the problem of how Agentic systems are re-shaping how we review information, where we fit in, and when we make decisions.  It also discusses the problem of how the increased flow of confident, generated information affects the way we make judgement.  This blog considers how human judgement needs to adapt, and how a behavioral defense approach – using techniques pioneered by Darktrace – can help us do that.

The challenge of knowing where human judgement belongs

As we confer more automated decision-making to agentic systems, it might look increasingly less like ‘granting permissions’, and more like ‘surrendering authority’.  

The judgement layer for AI-generated work is not a fixed boundary. We have become used to the idea of a ‘human in the loop’ (HITL) and, historically, relationships between humans and IT systems were reasonably clear and bounded.  Computer and software systems were programmed to carry out certain tasks or automated functions, and humans could control the gates and decision points where actions were undertaken. Even across highly complex computational workflows, human interaction was a controllable node within the process; we were able to configure and regulate. But in the agentic age, where that human interaction sits, and what it can influence shifts every time AI systems are granted autonomy.  

This leads us to the first problem: if humans are moving themselves (or are being moved) into the ‘judgement’ part of the value chain, exactly where and when do we exercise that judgement?  

Humans are no longer the sole shepherds of computer-based or software-controlled outputs.  We are at times at least one step further (and slower) behind the new agentic shepherds.  We might also be blind to what they are doing.  Not only might we be removed and blind to the actions of our AI shepherds, but with the challenge of unknown, unapproved AI systems operating beyond our control, humans might not even know that our work is being shepherded by an AI at all.  Simply put, with the advent of greater levels of autonomy and orchestration, humans are at risk of not even knowing where to apply our newly-extended powers of strategic judgement.

Shadow AI – the use of unapproved AI systems or processes – is a growing threat to the role of effective governance and oversight. Shadow AI isn't just the AI you can't see. Its the AI you already know about being used in an unapproved way. The ability to generate effective oversight of the AI systems you use (or that are used on your behalf) will be increasingly important to ensure that human judgement in the AI value chain is effective, and deliberately placed.

The problem of what makes good judgement

The second problem lies in how flawed human judgement can be.  Humans are historically, notoriously, and, sometimes dangerously, unreliable when it comes to exercising judgement.  Humans are prone to the worst kinds of bias, the seduction of malign influence, and the sometimes-overwhelming urge to succeed. AI has long had a known flaw of operating with sycophancy, providing outputs that tend to agree with or flatter the human user.  But as AI grows ever more effective, there is a risk of both hyper-enablement (where humans increasingly and knowingly enable AI despite potential harm), as well as the greater risk of suggestion. Both of these aspects could skew the newly-elevated input of human judgement.

Imagine a highly competent AI system that has just orchestrated and managed a dizzying array of processes and workflows.  The AI is designed to present the human decision-maker with recommendations; based on analysis, comparison and other programmed factors.  This is where the human judgement layer is enabled.  But what if that judgement is summarily diffused by an AI-based recommendation that emulates the decision, provides plausible but unattractive alternatives, then suggests (or, worse, directs) the human end-user to take a particular course of action.

The risk here is that you are given a recommendation, tailored to your preferences (which the AI has learned, or which you have divulged), and which appears to make perfect sense.  It appears to be a well-weighted recommendation, with sound arguments that tap into our inherent biases or inclinations so that a specific decision-path is followed. With the growth of agentic systems specifically designed to match user profiles (from Cowork agents to ‘digital twin’ models), the likelihood of agentic influence could badly skew human judgement or, at the least, devalue the proposition that humans are taking a higher-layer of strategic control over AI-based decisions.

If AI convincingly recommends something that may be problematic, it can be difficult to discern both accurate data, and the context required to make the right judgement.

Given the two problems described above, the job of exercising valuable human judgement in the agentic age can draw down to these two questions:

  • When should humans intervene in the agentic process?  
  • How can we make the best possible judgement calls?

What humans contribute that AI cannot

For all the flaws that make human judgement unreliable, people have the edge over even the most sophisticated and powerful AI systems when it comes to issues such as ethics and social context.  An AI system can, with startling granularity, rank the value of adopting a new business proposal: offering predictive metrics on costs, returns, market value, time-to-deliver operations, conformance with legal registers, etc.  But it can’t tell if the business proposal is ethically sound, or if the business venture will potentially affect groups outside of the analyzed proposal. It can’t tell you if the CEO has a ‘bad feeling’ about this effort.  It can’t tell you if this is the right thing to do.  

The ability to add social context, balance complex interpersonal dynamics, understand nuance, and to go beyond what seems economically reasonable is where human judgement can add value.  

Human judgement is difficult to encapsulate in metrics. And the way we train our development may need to adapt too. Rather than building up a gradual, experiential knowledge base, we should think about training the skill of judgement itself; especially for an agentic age.

How behavioral security strengthens AI governance

If this all feels like a vicious circle (‘I need AI help to make good judgements’ / ‘AI can twist what I need to judge’) it needn’t be. The key to this is having a defense-in-depth approach, with tools that can actually help.

This is precisely where behavioral security becomes important. The complex and nuanced way that humans exercise judgement is often rooted in our ability to recognize behavior that doesn't look right. We may not always be able to articulate it immediately, but we can often identify when an action, recommendation, or outcome feels inconsistent with the context around it. As AI systems take on more responsibility across the decision chain, preserving that ability to recognize meaningful deviations becomes increasingly important.

Darktrace’s / SECURE AI is designed to do exactly that. It applies behavioral security to AI ecosystems, helping organizations understand how people, AI tools, identities, and agents interact across the business. By learning the patterns of normal AI usage and surfacing activity that deviates from those patterns, it provides security teams with the context needed to investigate risk, understand unusual behavior, and make informed governance decisions. Rather than relying solely on predefined rules or assumptions, this behavioral understanding helps organizations distinguish between expected AI activity and behavior that warrants closer scrutiny.

This matters because we are already in an era of information overload. If humans are expected to elevate their value through strategic judgement, the ability to do this without being overwhelmed by data (good or bad) will be critical.  

We need the ability to discern when we're being misled by AI, and whether our judgement calls are being made on the basis of accurate, contextual information. Darktrace / SECURE AI provides that additional layer of defensive security for activity we cannot easily see. Whether it is suspected Shadow AI or skewed recommendations, the net result is a protected organization, where users can more effectively use AI to make positive judgements.

For those where that judgement is a critical skill (both individuals, as well as those working in security teams), improving our metacognition - the ability to understand information in a broader context - will supercharge the value of human judgement. When those judgements are grounded in context rather than assumptions we have better information to make sound decisions.

Conclusion

Human judgement is a skill that is honed over time and experience.  Darktrace’s / SECURE AI employs the same principles, but at machine-speed. Rather than influencing or directing, Darktrace / SECURE AI offers AI-enabled assurance; providing human-based judgement with the right context to make a balanced decision.  

What we judge can be valued by the legitimacy of its outputs. For AI, those outputs are valued on the speed and accuracy of the information provided.  Increasingly for humans, the value of our outputs will be based on the validity of our judgement, and how we justify our decisions in ways that engineer confidence.  

Humans often know more than we can express, while AI is prone to expressing more than it truly understands. Humans can bridge the context AI often fails to appreciate. When that judgement is supported by relevant, impartial AI systems, this is the future space where good AI governance will be exercised.

Discover Darktrace / SECURE AI.

[related-resource]

Continue reading
About the author
Jason Lusted
AI Governance Advisor

Blog

/

AI

/

September 4, 2026

Darktrace Advances Incident Investigation and AI-Agent Security with OpenAI Daybreak Models

Default blog imageDefault blog image

Earlier this year, Darktrace joined OpenAI’s Daybreak Defense Network to explore how their cyber capabilities can be integrated within Darktrace products and services to transform how security teams move from signal to action.

At the heart of this work is Darktrace's behavioral understanding of customer environments and identification of complex security incidents, combined with OpenAI models that can add context to help explain why an incident matters and its potential impact on the business. By bringing these capabilities into defensive workflows security teams already use, the goal is to give defenders not just greater visibility, but the context and guidance they need to act with confidence.

Since joining the program, we've been working with OpenAI to explore how these capabilities can address specific security challenges for defenders.

The problem we're solving

Attackers continue to change how they operate, including by using AI to increase the speed and scale of some techniques. Security teams are already managing a large volume of alerts, and the question isn't just what's happening, but how it could affect the organization. Even when an incident is fully investigated and correlated, technical severity alone doesn't tell a security team how much it actually matters to the business. That same challenge extends to internal AI adoption. As organizations adopt more AI systems and agents, security teams need visibility into their behavior, access and activity, along with the broader business context needed to identify and investigate potential risk.

Darktrace's Adaptive AI™ builds a detailed, organization-specific picture of what's normal for each environment, and uses that picture to investigate threats and identify complex security activity across domains. OpenAI's models can build on Darktrace's correlated, technically prioritized incidents by adding context that can help defenders understand what may be at stake.

What we're building

Our work is focused on two areas: supporting security investigation and response, and helping defenders identify risky behavior across enterprise AI systems and agents.

The first aligns Darktrace's behavioral understanding with OpenAI models to support  security investigation and prioritization. Darktrace's Adaptive AI continuously learns the unique patterns of normal behavior within each customer it protects, creating a deep, organization-specific understanding of its digital estate. When unusual activity emerges, OpenAI's models can draw on that context to help analysts investigate the incident, understand its significance and assess potential business consequences — reducing the need to manually assemble context from fragmented signals.

Second, we are exploring how these capabilities can support AI-agent and runtime security through Darktrace / SECURE AI™. OpenAI’s Daybreak models can build on the detections and visibility Darktrace / SECURE AI provides, connecting signals across a customer's environment and help defenders identify potentially risky behavior involving AI systems and agents. Activity that might appear isolated can instead be connected with related signals, helping defenders investigate the broader context and determine appropriate remediation.

Darktrace brings deep cybersecurity expertise, an evolving understanding of each customer's environment, and AI-driven identification of threats across the digital estate. Through the Daybreak Defense Network, Darktrace is exploring how OpenAI models can augment those capabilities in defensive security workflows — supporting incident investigation and response and improving visibility into AI-agent and runtime risk.

These capabilities are still in development, and we're excited to continue building on this work.

To learn more about how Darktrace continues to innovate to meet today's most pressing security challenges, register for our upcoming launch broadcast here.

Continue reading
About the author
Dr. Tim Bazalgette
Chief AI Officer, Darktrace
Your data. Our AI.
Elevate your network security with Darktrace AI