Blog
/
Network
/
June 10, 2024

Darktrace Investigation Into Medusa Ransomware

See how Darktrace empowers organizations to fight back against Medusa ransomware, enhancing their cybersecurity posture with advanced technology.
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Maria Geronikolou
Cyber Analyst
Default blog image
10
Jun 2024

What is Living off the Land attack?

In the face of increasingly vigilant security teams and adept defense tools, attackers are continually looking for new ways to circumvent network security and gain access to their target environments. One common tactic is the leveraging of readily available utilities and services within a target organization’s environment in order to move through the kill chain; a popular method known as living off the land (LotL). Rather than having to leverage known malicious tools or write their own malware, attackers are able to easily exploit the existing infrastructure of their targets.

The Medusa ransomware group in particular are known to extensively employ LotL tactics, techniques and procedures (TTPs) in their attacks, as one Darktrace customer in the US discovered in early 2024.

What is Medusa Ransomware?

Medusa ransomware (not to be confused with MedusaLocker) was first observed in the wild towards the end of 2022 and has been a popular ransomware strain amongst threat actors since 2023 [1]. Medusa functions as a Ransomware-as-a-Service (RaaS) platform, providing would-be attackers, also know as affiliates, with malicious software and infrastructure required to carry out disruptive ransomware attacks. The ransomware is known to target organizations across many different industries and countries around the world, including healthcare, education, manufacturing and retail, with a particular focus on the US [2].

How does Medusa Ransomware work?

Medusa affiliates are known to employ a number of TTPs to propagate their malware, most predominantly gaining initial access by exploiting vulnerable internet-facing assets and targeting valid local and domain accounts that are used for system administration.

The ransomware is typically delivered via phishing and spear phishing campaigns containing malicious attachments [3] [4], but it has also been observed using initial access brokers to access target networks [5]. In terms of the LotL strategies employed in Medusa compromises, affiliates are often observed leveraging legitimate services like the ConnectWise remote monitoring and management (RMM) software and PDQ Deploy, in order to evade the detection of security teams who may be unable to distinguish the activity from normal or expected network traffic [2].

According to researchers, Medusa has a public Telegram channel that is used by threat actors to post any data that may have been stolen, likely in an attempt to extort organizations and demand payment [2].  

Darktrace’s Coverage of Medusa Ransomware‍

Established Foothold and C2 activity

In March 2024, Darktrace / NETWORK identified over 80 devices, including an internet facing domain controller, on a customer network performing an unusual number of activities that were indicative of an emerging ransomware attack. The suspicious behavior started when devices were observed making HTTP connections to the two unusual endpoints, one of which is “go-sw6-02.adventos[.]de”, with the PowerShell and JWrapperDownloader user agents.

Darktrace’s Cyber AI Analyst™ launched an autonomous investigation into the connections and was able to connect the seemingly separate events into one wider incident spanning multiple different devices. This allowed the customer to visualize the activity in chronological order and gain a better understanding of the scope of the attack.

At this point, given the nature and rarity of the observed activity, Darktrace /NETWORK's autonomous response would have been expected to take autonomous action against affected devices, blocking them from making external connections to suspicious locations. However, autonomous response was not configured to take autonomous action at the time of the attack, meaning any mitigative actions had to be manually approved by the customer’s security team.

Internal Reconnaissance

Following these extensive HTTP connections, between March 1 and 7, Darktrace detected two devices making internal connection attempts to other devices, suggesting network scanning activity. Furthermore, Darktrace identified one of the devices making a connection with the URI “/nice ports, /Trinity.txt.bak”, indicating the use of the Nmap vulnerability scanning tool. While Nmap is primarily used legitimately by security teams to perform security audits and discover vulnerabilities that require addressing, it can also be leveraged by attackers who seek to exploit this information.

Darktrace / NETWORK model alert showing the URI “/nice ports, /Trinity.txt.bak”, indicating the use of Nmap.
Figure 1: Darktrace /NETWORK model alert showing the URI “/nice ports, /Trinity.txt.bak”, indicating the use of Nmap.

Darktrace observed actors using multiple credentials, including “svc-ndscans”, which was also seen alongside DCE-RPC activity that took place on March 1. Affected devices were also observed making ExecQuery and ExecMethod requests for IWbemServices. ExecQuery is commonly utilized to execute WMI Query Language (WQL) queries that allow the retrieval of information from WI, including system information or hardware details, while ExecMethod can be used by attackers to gather detailed information about a targeted system and its running processes, as well as a tool for lateral movement.

Lateral Movement

A few hours after the first observed scanning activity on March 1, Darktrace identified a chain of administrative connections between multiple devices, including the aforementioned internet-facing server.

Cyber AI Analyst was able to connect these administrative connections and separate them into three distinct ‘hops’, i.e. the number of administrative connections made from device A to device B, including any devices leveraged in between. The AI Analyst investigation was also able to link the previously detailed scanning activity to these administrative connections, identifying that the same device was involved in both cases.

Cyber AI Analyst investigation into the chain of lateral movement activity.
Figure 2: Cyber AI Analyst investigation into the chain of lateral movement activity.

On March 7, the internet exposed server was observed transferring suspicious files over SMB to multiple internal devices. This activity was identified as unusual by Darktrace compared to the device's normal SMB activity, with an unusual number of executable (.exe) and srvsvc files transferred targeting the ADMIN$ and IPC$ shares.

Cyber AI Analyst investigation into the suspicious SMB write activity.
Figure 3: Cyber AI Analyst investigation into the suspicious SMB write activity.
Graph highlighting the number of successful SMB writes and the associated model alerts.
Figure 4: Graph highlighting the number of successful SMB writes and the associated model alerts.

The threat actor was also seen writing SQLite3*.dll files over SMB using a another credential this time. These files likely contained the malicious payload that resulted in the customer’s files being encrypted with the extension “.s3db”.

Darktrace’s visibility over an affected device performing successful SMB writes.
Figure 5: Darktrace’s visibility over an affected device performing successful SMB writes.

Encryption of Files

Finally, Darktrace observed the malicious actor beginning to encrypt and delete files on the customer’s environment. More specifically, the actor was observed using credentials previously seen on the network to encrypt files with the aforementioned “.s3db” extension.

Darktrace’s visibility over the encrypted files.
Figure 6: Darktrace’s visibility over the encrypted files.


After that, Darktrace observed the attacker encrypting  files and appending them with the extension “.MEDUSA” while also dropping a ransom note with the file name “!!!Read_me_Medusa!!!.txt”

Darktrace’s detection of threat actors deleting files with the extension “.MEDUSA”.
Figure 7: Darktrace’s detection of threat actors deleting files with the extension “.MEDUSA”.
Darktrace’s detection of the Medusa ransom note.
Figure 8: Darktrace’s detection of the Medusa ransom note.

At the same time as these events, Darktrace observed the attacker utilizing a number of LotL techniques including SSL connections to “services.pdq[.]tools”, “teamviewer[.]com” and “anydesk[.]com”. While the use of these legitimate services may have bypassed traditional security tools, Darktrace’s anomaly-based approach enabled it to detect the activity and distinguish it from ‘normal’ network activity. It is highly likely that these SSL connections represented the attacker attempting to exfiltrate sensitive data from the customer’s network, with a view to using it to extort the customer.

Cyber AI Analyst’s detection of “services.pdq[.]tools” usage.
Figure 9: Cyber AI Analyst’s detection of “services.pdq[.]tools” usage.

If this customer had been subscribed to Darktrace's Proactive Threat Notification (PTN) service at the time of the attack, they would have been promptly notified of these suspicious activities by the Darktrace Security Operation Center (SOC). In this way they could have been aware of the suspicious activities taking place in their infrastructure before the escalation of the compromise. Despite this, they were able to receive assistance through the Ask the Expert service (ATE) whereby Darktrace’s expert analyst team was on hand to assist the customer by triaging and investigating the incident further, ensuring the customer was well equipped to remediate.  

As Darktrace /NETWORK's autonomous response was not enabled in autonomous response mode, this ransomware attack was able to progress to the point of encryption and data exfiltration. Had autonomous response been properly configured to take autonomous action, Darktrace would have blocked all connections by affected devices to both internal and external endpoints, as well as enforcing a previously established “pattern of life” on the device to stop it from deviating from its expected behavior.

Conclusion

The threat actors in this Medusa ransomware attack attempted to utilize LotL techniques in order to bypass human security teams and traditional security tools. By exploiting trusted systems and tools, like Nmap and PDQ Deploy, attackers are able to carry out malicious activity under the guise of legitimate network traffic.

Darktrace’s Self-Learning AI, however, allows it to recognize the subtle deviations in a device’s behavior that tend to be indicative of compromise, regardless of whether it appears legitimate or benign on the surface.

Further to the detection of the individual events that made up this ransomware attack, Darktrace’s Cyber AI Analyst was able to correlate the activity and collate it under one wider incident. This allowed the customer to track the compromise and its attack phases from start to finish, ensuring they could obtain a holistic view of their digital environment and remediate effectively.

[related-resource]

Appendices

Credit to Maria Geronikolou, Cyber Analyst, Ryan Traill, Threat Content Lead

Darktrace DETECT Model Detections

Anomalous Connection / SMB Enumeration

Device / Anomalous SMB Followed By Multiple Model Alerts

Device / Suspicious SMB Scanning Activity

Device / Attack and Recon Tools

Device / Suspicious File Writes to Multiple Hidden SMB Share

Compromise / Ransomware / Ransom or Offensive Words Written to SMB

Device / Internet Facing Device with High Priority Alert

Device / Network Scan

Anomalous Connection / Powershell to Rare External

Device / New PowerShell User Agent

Possible HTTP Command and Control

Extensive Suspicious DCE-RPC Activity

Possible SSL Command and Control to Multiple Endpoints

Suspicious Remote WMI Activity

Scanning of Multiple Devices

Possible Ransom Note Accessed over SMB

List of Indicators of Compromise (IoCs)

IoC – Type – Description + Confidence‍

207.188.6[.]17      -     IP address   -      C2 Endpoint

172.64.154[.]227 - IP address -        C2 Endpoint

go-sw6-02.adventos[.]de.  Hostname  - C2 Endpoint

.MEDUSA             -        File extension     - Extension to encrypted files

.s3db               -             File extension    -  Created file extension

SQLite3-64.dll    -        File           -               Used tool

!!!Read_me_Medusa!!!.txt - File -   Ransom note

Svc-ndscans         -         Credential     -     Possible compromised credential

Svc-NinjaRMM      -       Credential      -     Possible compromised credential

MITRE ATT&CK Mapping

Discovery  - File and Directory Discovery - T1083

Reconnaissance    -  Scanning IP            -          T1595.001

Reconnaissance -  Vulnerability Scanning -  T1595.002

Lateral Movement -Exploitation of Remote Service -  T1210

Lateral Movement - Exploitation of Remote Service -   T1210

Lateral Movement  -  SMB/Windows Admin Shares     -    T1021.002

Lateral Movement   -  Taint Shared Content          -            T1080

Execution   - PowerShell     - T1059.001

Execution  -   Service Execution   -    T1059.002

Impact   -    Data Encrypted for Impact  -  T1486

References

[1] https://unit42.paloaltonetworks.com

[2] https://thehackernews.com

[3] https://trustwave.com

[4] https://www.sangfor.com

[5] https://thehackernews.com

[6]https://any.run

Get the latest insights on emerging cyber threats

This report explores the latest trends shaping the cybersecurity landscape and what defenders need to know in 2026.

Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Maria Geronikolou
Cyber Analyst

More in this series

No items found.

Blog

/

/

November 3, 2026

From One Alert to a Wider Campaign: Uncovering Novel Threats Through Behavioral Analysis

Default blog imageDefault blog image

Key Findings

  • Darktrace’s Threat Research team is exploring a new method to identify malicious campaigns by correlating similar anomalous activity across its customer fleet.
  • The method uses unsupervised clustering to identify shared behavioral patterns across multiple customer deployments without relying on prior indicators of compromise (IoCs).
  • The approach identified shared infrastructure across dozens of customers, with activity linked to the likely POPA botnet.
  • A second cluster identified anomalous activity associated with Monero cryptocurrency mining.

‍

How does Darktrace conduct threat research?

The Darktrace Threat Research team aims to identify malicious campaign activity affecting multiple customers. By their nature, these campaigns will lead to shared behavioral patterns across multiple victims.

In this piece, we describe a method for identifying malicious campaign activity that uses this simple observation as a guiding principle. We begin by outlining a few key facts about the modern threat landscape and why behavioral detection is necessary to meet the challenges it presents. We then explore how fleet-wide behavioral detections can be leveraged using the principle above to systematically identify multi-deployment campaigns impacting the Darktrace customer fleet. Finally, we demonstrate that this research is not purely theoretical, using real examples of campaign activity detected through this novel approach.

Shifting to a behavioral-focused approach

The modern era of cyber-defense necessitates detection capabilities beyond traditional signature-based methods. Technologies such as antivirus signatures, hash-based malware identification, and IP blocklists have historically been successful in defending against known threats. However, they are easily circumvented by attackers and inherently limited in defending against the novel attack techniques that today's threat landscape is producing.

Recent breakthroughs in AI represent a transformational risk multiplier that cannot be ignored. AI systems do not merely execute existing attacks at machine speed; there are signs they can also synthesize novel tradecraft [1], increasing the likelihood that defenders will encounter attack patterns that have never previously been observed. Meanwhile vulnerability disclosures continue to accelerate. More than 48,000 CVEs were published in 2025, and published statistics to date indicate that 2026 is already on track to significantly exceed that figure [2]. While multiple factors may contribute to vulnerability discovery, AI is seen as a key factor in this rapid growth. Organizations should expect a growing proportion of malicious activity to fall outside the scope of detections that rely solely on prior knowledge of known threats.

By design, Darktrace’s behavioral and anomaly-focused detection capabilities are well-suited to this testing landscape. With a focus on detecting unknown and unexpected activity that deviates from the baseline of “normal” behavior, detection of CVE exploitation without prior knowledge of the vulnerability and before public disclosure, for example, is achievable [3][4].

Darktrace’s diverse customer base benefits from a further layer of protection: working with only deidentified alert metadata, our threat researchers hunt proactively across the fleet. Beyond the level of the individual customer, there is a second, larger vantage to be leveraged.

Darktrace data provides unique insight into the unexpected behavioral patterns that occur across its customer fleet. What can we see if we look at this fleet-wide telemetry and hunt for systematic behavioral campaigns that impact our customer base?

Correlating across the customer base

At the deployment level, Darktrace focuses on whether activity is unusual in the context of an organization's normal behavior, but as we zoom out and look at these alerts at the fleet level, the problem fundamentally changes . We are no longer seeking anomalies in largely normal data; we are seeking systematic patterns within data already known to be anomalous. An isolated behavior anomaly may be notable for a single customer; the same fingerprint across dozens is a signal of a structured campaign. Hunting for such campaigns and sharing our findings are key areas of focus for Darktrace’s Threat Research team.  In this spirit, Darktrace is  actively exploring a a new research approach that leverages deidentified alert metadata to increase campaign detection ability.

This approach is based on the premise that an expert human analyst presented with a set of alerts will identify likely related activity by assessing whether the metadata fields indicate a relationship. For example, two connections to a rare endpoint that exhibits naming structure that is likely from a single algorithm are a strong indicator, as is the use of an unusual port carrying a given protocol (e.g. port 6000 for SSL). Darktrace’s approach to campaign detection encodes this expert human judgement process through deterministic embedding functions that obtain reproducible vector representations of alert data. Unsupervised clustering is then applied to these vector representations to obtain groups of alerts that describe semantically similar alert data across multiple customers. These clusters therefore represent similar anomalous activity that has occurred across multiple customers. In other words, these clusters are candidates for malicious campaign activity.

‍

Figure 1: Layers of AI-based analysis provided through Darktrace products and cross-customer correlation.

‍

Case study 1 – unusual connections to shared underlying infrastructure

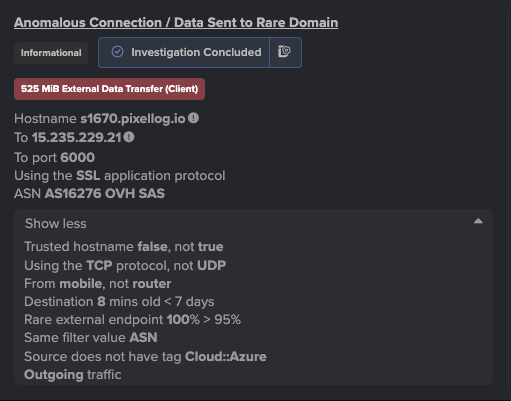
In one recent case, the clustering produced several tight groups of alerts spanning dozens of customers. Each group centered on a single domain whose subdomains were algorithmically generated (e.g. s01699, s1736, s91). Examined side by side, these clusters shared an unmistakable behavioral shape: each involved a domain with a clear naming pattern (e.g. s016841786.net-echo[.]com, s1670.pixellog[.]io, s217.pixellog[.]io) , with connections over SSL on the unusual port 6000 to servers hosted by non-mainstream providers (e.g. OVH, Hetzner, GTHost, Leaseweb), rather than generally expected content-delivery networks.

‍

Figure 2: An example model alert triggering on unusual outbound connections and data transfer to s1670.pixellog[.]io.

‍

Closer inspection revealed that the same subdomain label appeared under different domains (e.g. s1786.net-echo[.]com and s1786.pixellog[.]io). Following this lead, Darktrace’s threat researchers pivoted across the customer base and found numerous distinct subdomain labels reused under more than one registered domain. In several cases, the same label resolved to the same IP across different domains (e.g. s1704 under both pixellog[.]io and net-echo[.]com → 148.113.222[.]244; s01684 → 15.235.67[.]95), suggesting the use of ephemeral subdomain infrastructure in an attempt to avoid signature-based defense techniques.

This example demonstrates how multi-deployment data can uncover shared infrastructure that may be difficult to identify at the individual deployment level alone. In particular, the presented method facilitated this discovery by producing coherent, tight clusters of geometrically similar vector embeddings of malicious activity from large-scale fleet data, which could then be presented to a researcher for further investigation. This  activity highlighted across the Darktrace customer base was ultimately linked to likely POPA botnet activity through use of open-source intelligence (OSINT) [5].

Case Study 2 – anomalous user agent and txt URI

A second example shows the method surfacing a single, self-contained cluster. The clustering was not given any indicators to look for; instead, it grouped devices that shared an unusual combination of features. On inspection, that shared consisted of:

-      unusual user agent (tes)

-      specific request path (/md5_GIP.txt)

-      uncommon destination port (83)

-      hostname impersonating Google (matching regular expression ^www\.google\.com\.[a-zA-Z0-9]+\.fast-dns-host\.com$)

Treating these shared features as IoCs, Darktrace’s threat researchers then pivoted to an exploration across the customer base to investigate the full breadth of the campaign. This search identified further commonalities; additional domains which shared the same IP as the domain family highlighted in the cluster, as well as evidence of cryptocurrency mining on affected devices. Additional OSINT research also aligned with these findings, linking the discovered payloads and infrastructure to Monero cryptocurrency mining [6].

Conclusion

The method outlined in this blog is under active development, with ongoing technical refinement providing opportunities to further enhance its capabilities. While the capability continues to mature, this approach to threat hunting leverages the powerful vantage point of fleetwide telemetry across a diverse customer base to help protect Darktrace customers. This method allows campaigns that at the deployment level appear as isolated alerts to be seen at their true scale and spread. It enables proactive fleet-wide analysis without prior IoCs to identify campaigns impacting Darktrace customers.

This is possible because of what the method is built on: the atomic unit is the Darktrace alert, a signal that encodes years of cyber expertise, while the multi-deployment nature of the method allows organizations to indirectly benefit from findings from other networks through shared intelligence by Darktrace’s Threat Research team.

Credit to Daniel Levy (Threat Hunting Data Scientist), Paul Jennings (Principal Cyber Analyst), Emma Foulger (Global Head, Threat Operations)

Edited by Ryan Traill (Content Manager)

References

1. https://www.aisi.gov.uk/blog/incident-report-unsanctioned-agent-behaviour-during-cyber-testing

2. https://www.cvefind.com/en/cve-statistic-date.html

3. https://www.darktrace.com/blog/security-after-signatures-operating-in-a-world-of-pre-cve-disclosure-exploitation-collapsed-trust-boundaries-and-autonomous-systems

4. https://www.darktrace.com/blog/pre-cve-threat-detection-10-examples-identifying-malicious-activity-prior-to-public-disclosure-of-a-vulnerability

5. https://github.com/synthient/public-research/blob/main/2026/06/popa/Popa.md

6. https://www.deepwatch.com/blog/pirated-adobe-photoshop-2023-installers-lead-to-monero-cryptocurrency-mining/

Continue reading
About the author
Daniel Levy
Threat Hunting Data Scientist

Blog

/

AI

/

November 2, 2026

PHP Vulnerabilities, ARTEX and the Growing Role of AI in Cyber Attacks

Default blog imageDefault blog image

The disclosure of CVE-2026-109618 and CVE-2026-109619 placed immediate pressure on organizations running PHP. Both vulnerabilities can allow unauthenticated remote code execution, including in products and appliances where PHP is embedded, and updates depend on third-party vendors [1].

Early guidance focused on patching internet-facing systems and monitoring for behavior associated with successful exploitation, including unexpected command execution, Webroot changes and outbound connections from PHP servers.

Darktrace observed widespread scanning across monitored environments involving hundreds of distinct source IP addresses that public reporting has associated with activity targeting the PHP vulnerabilities. The volume of scanning was significantly greater than the evidence available for successful exploitation. For analysts, that distinction is important. Scanning demonstrates interest in exposed infrastructure; establishing compromise requires evidence of subsequent behavior on the targeted system, including command execution, file modification or unexpected outbound communication.

PHP is not an isolated example. Imperva subsequently demonstrated remote code execution against a vulnerable Node.js build through malicious Brotli data, reproducing execution through compressed HTTP responses and configured request parsers. The same inputs were rejected by the patched runtime. Imperva linked its Node2Shell and PHP2Shell research to the increasing speed of vulnerability discovery and exploit development. [2]

While Darktrace has not observed direct evidence of CVE-2026-109618 or CVE-2026-109619 exploitation, on October 21st we observed a six-month high in detections consistent with zero-day exploitation activity, representing a 64% increase compared to historic data. This increase has not been confirmed as related to the PHP vulnerabilities. Darktrace’s behavioral approach is designed to detect anomalous activity without relying solely on rules written for a specific exploit. Comparable increases were observed around the Log4j disclosure and other globally significant vulnerability disclosures.

AI-assisted vulnerability research

The PHP disclosure arrives as AI systems have become more capable at vulnerability research [3]. OpenAI launched Daybreak in June 2026, combining GPT-5.5-Cyber, Codex Security and partnerships with security researchers and software maintainers. OpenAI says its models have been applied to discovering and generating patches for vulnerabilities in browsers, network infrastructure, FreeBSD and the Linux kernel. Darktrace joined the OpenAI Daybreak Cyber Partner Program in June to explore how OpenAI's cyber capabilities could be integrated within Darktrace products and services [4][10].

OpenAI reported in August that Codex Security Cloud had analyzed more than 30 million commits across more than 30,000 codebases. According to OpenAI, Cloudflare uses models accessed through Daybreak to investigate customer-authorized code and combines findings with live traffic and security signals to assess whether affected routes are active or receiving suspicious traffic, with proposed mitigations and patches remaining subject to customer review [5][6].

Faster discovery still leaves defenders with the work of locating affected software, testing fixes and completing remediation. The PHP case shows that gap clearly, particularly when vulnerable runtimes are embedded inside other products.

Enterprise agents as an attack surface

Darktrace Signal Labs has also examined how a trusted enterprise agent could be abused after an attacker has already obtained access to an environment. In a controlled simulation, researchers demonstrated that, in that post-compromise scenario, the Claude platform’s memory stores feature could be abused to establish a live C2 channel between an external operator and internal Claude Code agents. The external operator was able to dynamically assign network discovery, credential access, and data exfiltration tasks to the agents via this C2 channel. Detection of the agents’ activities relied on the correlation of process creation and network traffic activity from agent harness processes, alongside behavioral analysis to identify deviations from expected behavior. Darktrace has not claimed it observed this memory-store command-and-control technique in operational attacks [7].

AI-assisted attacks in Japan

Evidence from Japan indicates AI being used for vulnerability scanning and attacks outside controlled research. On 21 October, JPCERT/CC published findings from an investigation into recent unauthorized access incidents affecting organizations in Japan. JPCERT/CC states that it confirmed attackers had used AI to scan for known vulnerabilities and conduct attacks through APIs. According to JPCERT/CC, its examination of attack infrastructure found evidence of Android application analysis, API discovery and testing for weaknesses including server-side request forgery, and the infrastructure also targeted services intended for users outside Japan [8].

JPCERT/CC does not identify ARTEX by name in that publication. The named ARTEX attribution comes from separate investigations, including Microsoft's analysis of Storm-0940.

AI in offensive operations

Microsoft describes ARTEX as an open-source, multi-agent penetration-testing system capable of automating activity with limited human interaction. Microsoft reported that Storm-0940, which it assesses to be a China state-aligned actor active since 2021, used ARTEX against hundreds of organizations, and Microsoft attributed the ConnectWise supply-chain compromise [9].

Microsoft observed ARTEX accelerating scanning, reconnaissance, password spraying and OAuth application abuse. Several ARTEX-driven operations reached privileged cloud access less than three hours after initial targeting. Following the ConnectWise compromise, Storm-0940 attempted to authenticate to more than 2,250 tenants at rates of up to 2,900 attempts per minute [9].

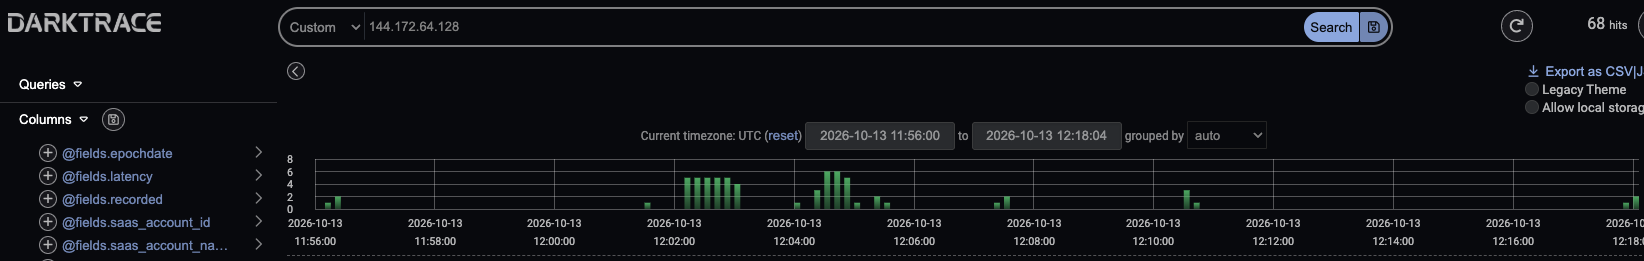
Darktrace Threat Research found activity in its own telemetry involving infrastructure later associated with the campaign. On 13 October, Darktrace recorded failed authentication activity involving 144.172.64[.]128, one of the addresses Microsoft later identified as performing sign-ins and Microsoft Graph activity in ConnectWise customer environments. Darktrace analysis identified 65 failed authentication attempts in around 20 minutes.

Figure 1: Darktrace Advanced Search showing failed authentication events involving 144.172.64[.]128 on 13 October 2026, (customer-identifying information redacted).

The telemetry establishes repeated failed authentication from infrastructure later associated with the campaign. It does not establish ARTEX execution or successful compromise. At the time of observation, Microsoft's later attribution was unavailable. Analysts therefore had the behavior itself: repeated failed authentication from the same source over a short period, together with any related identity, application or network activity inside the environment.

Microsoft documented a wider password-spray campaign against 327 accounts across eight organizations between 10 and 14 October. It recorded more than 151,000 failed logons, including more than 111,000 on 11 October, but no successful authentication, token issuance, Graph call or directory change from that campaign. Microsoft also reported that most Storm-0940 targeting was unsuccessful [9].

Where the actor progressed beyond authentication, Microsoft observed service-principal sign-ins followed by Graph and directory operations. Activity included reconnaissance, application credential changes and attempts to modify privileges. Microsoft recommends correlating service-principal sign-ins with Graph activity, directory changes and resource access [9].

Behavior before attribution

The PHP and ARTEX cases begin with different information. PHP defenders knew which software required urgent remediation but initially had limited information about exploitation. Process execution, file modification and outbound communication could still provide evidence of compromise.

The PHP and ARTEX observations also illustrate the difference between volume and impact. Darktrace observed broad scanning around the PHP disclosure, while the ARTEX-associated infrastructure produced concentrated authentication activity. Neither observation independently demonstrates compromise and in each case examining the behavior that follows the initial interaction is the investigative clue.

The Darktrace ARTEX-related observation began with authentication behavior. Microsoft publicly attributed the source infrastructure eight days later. That attribution added context, but it did not change what had originally been recorded in the environment.

AI is now present at several points in this cycle. Daybreak applies models to vulnerability discovery and remediation. Darktrace Signal Labs demonstrated how a trusted enterprise agent could be co-opted in a controlled environment. JPCERT/CC confirmed AI-assisted vulnerability scanning and API attacks in recent incidents. Microsoft documented ARTEX being used by Storm-0940 in active operations [4][7][8][9].

Microsoft's findings also show why scale and impact must be assessed separately. One ARTEX-associated campaign produced more than 151,000 failed logons without successful access, while other operations reached privileged cloud access in less than three hours. Security teams have to distinguish high-volume attempts from activity that progresses through authentication, privilege changes and resource access.

The evidence required to assess these cases remains familiar: authentication records, process execution, application and directory changes, file activity and network communication. AI can increase the rate at which those behaviors occur. Defenders still need to establish their sequence and impact.

Credit to Emma Foulger, Sam Lister, Dylan Evans, Moishe Tajtelbaum

References

[1] NCSC-NL, php2shell vulnerabilities (CVE-2026-109618, CVE-2026-109619), 21 October 2026. https://github.com/NCSC-NL/php2shell

[2] Imperva, https://www.imperva.com/blog/node2shell-from-brotli-data-to-remote-code-execution/

[3] Cyber Security Agency of Singapore, https://www.csa.gov.sg/alerts-and-advisories/alerts/al-2026-151/

[4] OpenAI, Daybreak: Tools for securing every organization in the world, 22 June 2026. https://openai.com/index/daybreak-securing-the-world/

[5] OpenAI Developers, Scaling cyber defenders with Daybreak, 21 August 2026. https://developers.openai.com/blog/scaling-cyber-defenders-with-daybreak

[6] OpenAI, Cloudflare links vulnerability discovery to defense with OpenAI, 21 October 2026. https://openai.com/index/cloudflare-cyber/

[7] Darktrace Signal Labs, Shared Memories as a Covert C2 Channel, draft research supplied for review.

[8] JPCERT/CC, Recent AI-Assisted Cyber Attacks in Japan: Investigating Attack Infrastructure and Techniques, 21 October 2026. https://blogs.jpcert.or.jp/en/2026/10/web_api_attacks.html

[9] Microsoft Security Research and Microsoft Threat Intelligence, AI-driven, large-scale nation-state campaign using ARTEX enables supply chain compromise, 21 October 2026. https://www.microsoft.com/en-us/security/blog/2026/10/21/storm-0940-uses-artex-agentic-ai-connectwise-supply-chain-compromise/

[10] Darktrace, Advancing the Use of Frontier AI in Cybersecurity: Darktrace Joins the OpenAI Daybreak Cyber Partner Program to Explore Defensive AI Integrations, 22 June 2026. https://www.darktrace.com/blog/advancing-the-use-of-frontier-ai-in-cybersecurity-darktrace-joins-the-openai-daybreak-cyber-partner-program-to-explore-defensive-ai-integrations

Continue reading
About the author
Nathaniel Jones
SVP, Global Threat Intelligence
Your data. Our AI.
Elevate your network security with Darktrace AI