Blog
/
Network
/
September 18, 2024

FortiClient EMS Exploited: Attack Chain & Post Exploitation Tactics

Read about the methods used to exploit FortiClient EMS and the critical post-exploitation tactics that affect cybersecurity defenses.
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Emily Megan Lim
Cyber Analyst
Default blog image
18
Sep 2024

Cyber attacks on internet-facing systems

In the first half of 2024, the Darktrace Threat Research team observed multiple campaigns of threat actors targeting vulnerabilities in internet-facing systems, including Ivanti CS/PS appliances, Palo Alto firewall devices, and TeamCity on-premises.

These systems, which are exposed to the internet, are often targeted by threat actors to gain initial access to a network. They are constantly being scanned for vulnerabilities, known or unknown, by opportunistic actors hoping to exploit gaps in security. Unfortunately, this exposure remains a significant blind spot for many security teams, as monitoring edge infrastructure can be particularly challenging due to its distributed nature and the sheer volume of external traffic it processes.

In this blog, we discuss a vulnerability that was exploited in Fortinet’s FortiClient Endpoint Management Server (EMS) and the post-exploitation activity that Darktrace observed across multiple customer environments.

What is FortiClient EMS?

FortiClient is typically used for endpoint security, providing features such as virtual private networks (VPN), malware protection, and web filtering. The FortiClient EMS is a centralized platform used by administrators to enforce security policies and manage endpoint compliance. As endpoints are remote and distributed across various locations, the EMS needs to be accessible over the internet.

However, being exposed to the internet presents significant security risks, and exploiting vulnerabilities in the system may give an attacker unauthorized access. From there, they could conduct further malicious activities such as reconnaissance, establishing command-and-control (C2), moving laterally across the network, and accessing sensitive data.

CVE-2023-48788

CVE-2023-48788 is a critical SQL injection vulnerability in FortiClient EMS that can allow an attacker to gain unauthorized access to the system. It stems from improper neutralization of special elements used in SQL commands, which allows attackers to exploit the system through specially crafted requests, potentially leading to Remote Code Execution (RCE) [1]. This critical vulnerability was given a CVSS score of 9.8 and can be exploited without authentication.

The affected versions of FortiClient EMS include:

  • FortiClient EMS 7.2.0 to 7.2.2 (fixed in 7.2.3)
  • FortiClient EMS 7.0.1 to 7.0.10 (fixed in 7.0.11)

The vulnerability was publicly disclosed on March 12, 2024, and an exploit proof of concept was released by Horizon3.ai on March 21 [2]. Starting from March 24, almost two weeks after the initial disclosure, Darktrace began to observe at least six instances where the FortiClient EMS vulnerability had likely been exploited on customer networks. Seemingly exploited devices in multiple customer environments were observed performing anomalous activities, including the installation of Remote Monitoring and Management (RMM) tools, which was also reported by other security vendors around the same time [3].

Darktrace’s Coverage

Initial Access

To understand how the vulnerability can be exploited to gain initial access, we first need to explain some components of the FortiClient EMS:

  • The service FmcDaemon.exe is used for communication between the EMS and enrolled endpoint clients. It listens on port 8013 for incoming client connections.
  • Incoming requests are then sent to FCTDas.exe, which translates requests from other server components into SQL requests. This service interacts with the Microsoft SQL database.
  • Endpoint clients communicate with the FmcDaemon on the server on port 8013 by default.

Therefore, an SQL injection attack can be performed by crafting a malicious payload and sending it over port 8013 to the server. To carry out RCE, an attacker may send further SQL statements to enable and use the xp_cmdshell functionality of the Microsoft SQL server [2].

Shortly before post-exploitation activity began, Darktrace had observed incoming connections to some of the FortiClient EMS devices over port 8013 from the external IPs 77.246.103[.]110, 88.130.150[.]101, and 45.155.141[.]219. This likely represented the threat actors sending an SQL injection payload over port 8013 to the EMS device to validate the exploit.

Establish C2

After exploiting the vulnerability and gaining access to an EMS device on one customer network, two additional devices were seen with HTTP POST requests to 77.246.103[.]110 and 212.113.106[.]100 with a new PowerShell user agent.

Interestingly, the IP 212.113.106[.]100 has been observed in various other campaigns where threat actors have also targeted internet-facing systems and exploited other vulnerabilities. Open-source intelligence (OSINT) suggests that this indicator of compromise (IoC) is related to the Sliver C2 framework and has been used by threat actors such as APT28 (Fancy Bear) and APT29 (Cozy Bear) [4].

Unusual file downloads were also observed on four devices, including:

  • “SETUP.MSI” from 212.32.243[.]25 and 89.149.200[.]91 with a cURL user agent
  • “setup.msi” from 212.113.106[.]100 with a Windows Installer user agent
  • “run.zip” from 95.181.173[.]172 with a PowerShell user agent

The .msi files would typically contain the RMM tools Atera or ScreenConnect [5]. By installing RMM tools for C2, attackers can leverage their wide range of functionalities to carry out various tasks, such as file transfers, without the need to install additional tools. As RMM tools are designed to maintain a stable connection to remote systems, they may also allow the attackers to ensure persistent access to the compromised systems.

A scan of the endpoint 95.181.173[.]172 shows various other files such as “RunSchedulerTask.ps1” and “anydesk.exe” being hosted.

Screenshot of the endpoint 95.181.173[.]172 hosting various files [6].
Figure 1: Screenshot of the endpoint 95.181.173[.]172 hosting various files [6].

Shortly after these unusual file downloads, many of the devices were also seen with usage of RMM tools such as Splashtop, Atera, and AnyDesk. The devices were seen connecting to the following endpoints:

  • *[.]relay.splashtop[.]com
  • agent-api[.]atera[.]com
  • api[.]playanext[.]com with user agent AnyDesk/8.0.9

RMM tools have a wide range of legitimate capabilities that allow IT administrators to remotely manage endpoints. However, they can also be repurposed for malicious activities, allowing threat actors to maintain persistent access to systems, execute commands remotely, and even exfiltrate data. As the use of RMM tools can be legitimate, they offer threat actors a way to perform malicious activities while blending into normal business operations, which could evade detection by human analysts or traditional security tools.

One device was also seen making repeated SSL connections to a self-signed endpoint “azure-documents[.]com” (104.168.140[.]84) and further HTTP POSTs to “serv1[.]api[.]9hits[.]com/we/session” (128.199.207[.]131). Although the contents of these connections were encrypted, they were likely additional infrastructure used for C2 in addition to the RMM tools that were used. Self-signed certificates may also be used by an attacker to encrypt C2 communications.

Internal Reconnaissance

Following the exploit, two of the compromised devices then started to conduct internal reconnaissance activity. The following figure shows a spike in the number of internal connections made by one of the compromised devices on the customer’s environment, which typically indicates a network scan.

Advanced Search results of internal connections made an affected device.
Figure 2: Advanced Search results of internal connections made an affected device.

Reconnaissance tools such as Advanced Port Scanner (“www[.]advanced-port-scanner[.]com”) and Nmap were also seen being used by one of the devices to conduct scanning activities. Nmap is a network scanning tool commonly used by security teams for legitimate purposes like network diagnostics and vulnerability scanning. However, it can also be abused by threat actors to perform network reconnaissance, a technique known as Living off the Land (LotL). This not only reduces the need for custom or external tools but also reduces the risk of exposure, as the use of a legitimate tool in the network is unlikely to raise suspicion.

Privilege Escalation

In another affected customer network, the threat actor’s attempt to escalate their privileges was also observed, as a FortiClient EMS device was seen with an unusually large number of SMB/NTLM login failures, indicative of brute force activity. This attempt was successful, and the device was later seen authenticating with the credential “administrator”.

Figure 3: Advanced Search results of NTLM (top) and SMB (bottom) login failures.

Lateral Movement

After escalating privileges, attempts to move laterally throughout the same network were seen. One device was seen transferring the file “PSEXESVC.exe” to another device over SMB. This file is associated with PsExec, a command-line tool that allows for remote execution on other systems.

The threat actor was also observed leveraging the DCE-RPC protocol to move laterally within the network. Devices were seen with activity such as an increase in new RPC services, unusual requests to the SVCCTL endpoint, and the execution of WMI commands. The DCE-RPC protocol is typically used to facilitate communication between services on different systems and can allow one system to request services or execute commands on another.

These are further examples of LotL techniques used by threat actors exploiting CVE-2023-48788, as PsExec and the DCE-RPC protocol are often also used for legitimate administrative operations.

Accomplish Mission

In most cases, the threat actor’s end goal was not clearly observed. However, Darktrace did detect one instance where an unusually large volume of data had been uploaded to “put[.]io”, a cloud storage service, indicating that the end goal of the threat actor had been to steal potentially sensitive data.

In a recent investigation of a Medusa ransomware incident that took place in July 2024, Darktrace’s Threat Research team found that initial access to the environment had likely been gained through a FortiClient EMS device. An incoming connection from 209.15.71[.]121 over port 8013 was seen, suggesting that CVE-2023-48788 had been exploited. The device had been compromised almost three weeks before the ransomware was actually deployed, eventually resulting in the encryption of files.

Mitigating risk with proactive exposure management and real-time detection

Threat actors have continued to exploit unpatched vulnerabilities in internet-facing systems to gain initial access to a network. This highlights the importance of addressing and patching vulnerabilities as soon as they are disclosed and a fix is released. However, due to the rapid nature of exploitation, this may not always be enough. Furthermore, threat actors may even be exploiting vulnerabilities that are not yet publicly known.

As the end goals for a threat actor can differ – from data exfiltration to deploying ransomware – the post-exploitation behavior can also vary from actor to actor. However, AI security tools such as Darktrace / NETWORK can help identify and alert for post-exploitation behavior based on abnormal activity seen in the network environment.

Despite CVE-2023-48788 having been publicly disclosed and fixed in March, it appears that multiple threat actors, such as the Medusa ransomware group, have continued to exploit the vulnerability on unpatched systems. With new vulnerabilities being disclosed almost every other day, security teams may find it challenging continuously patch their systems.

As such, Darktrace / Proactive Exposure Management could also alleviate the workload of security teams by helping them identify and prioritize the most critical vulnerabilities in their network.

Insights from Darktrace’s First 6: Half-year threat report for 2024

First 6: half year threat report darktrace screenshot

Darktrace’s First 6: Half-Year Threat Report 2024 highlights the latest attack trends and key threats observed by the Darktrace Threat Research team in the first six months of 2024.

  • Focuses on anomaly detection and behavioral analysis to identify threats
  • Maps mitigated cases to known, publicly attributed threats for deeper context
  • Offers guidance on improving security posture to defend against persistent threats

‍

‍

Appendices

Credit to Emily Megan Lim (Cyber Security Analyst) and Ryan Traill (Threat Content Lead)

References

[1] https://nvd.nist.gov/vuln/detail/CVE-2023-48788

[2] https://www.horizon3.ai/attack-research/attack-blogs/cve-2023-48788-fortinet-forticlientems-sql-injection-deep-dive/

[3] https://redcanary.com/blog/threat-intelligence/cve-2023-48788/

[4] https://www.fortinet.com/blog/threat-research/teamcity-intrusion-saga-apt29-suspected-exploiting-cve-2023-42793

[5] https://redcanary.com/blog/threat-intelligence/cve-2023-48788/

[6] https://urlscan.io/result/3678b9e2-ad61-4719-bcef-b19cadcdd929/

List of IoCs

IoC - Type - Description + Confidence

  • 212.32.243[.]25/SETUP.MSI - URL - Payload
  • 89.149.200[.]9/SETUP.MSI - URL - Payload
  • 212.113.106[.]100/setup.msi - URL - Payload
  • 95.181.173[.]172/run.zip - URL - Payload
  • serv1[.]api[.]9hits[.]com - Domain - Likely C2 endpoint
  • 128.199.207[.]131 - IP - Likely C2 endpoint
  • azure-documents[.]com - Domain - C2 endpoint
  • 104.168.140[.]84 - IP - C2 endpoint
  • 77.246.103[.]110 - IP - Likely C2 endpoint
  • 212.113.106[.]100 - IP - C2 endpoint

Darktrace Model Detections

Anomalous Connection / Callback on Web Facing Device

Anomalous Connection / Multiple HTTP POSTs to Rare Hostname

Anomalous Connection / New User Agent to IP Without Hostname

Anomalous Connection / Posting HTTP to IP Without Hostname

Anomalous Connection / Powershell to Rare External

Anomalous Connection / Rare External SSL Self-Signed

Anomalous Connection / Suspicious Self-Signed SSL

Anomalous Server Activity / Rare External from Server

Anomalous Server Activity / New User Agent from Internet Facing System

Anomalous Server Activity / Server Activity on New Non-Standard Port - External

Compliance / Remote Management Tool On Server

Device / New User Agent

Device / New PowerShell User Agent

Device / Attack and Recon Tools

Device / ICMP Address Scan

Device / Network Range Scan

Device / Network Scan

Device / RDP Scan

Device / Suspicious SMB Scanning Activity

Anomalous Connection / Multiple SMB Admin Session

Anomalous Connection / New or Uncommon Service Control

Anomalous Connection / Unusual Admin SMB Session

Device / Increase in New RPC Services

Device / Multiple Lateral Movement Breaches

Device / New or Uncommon WMI Activity

Device / New or Unusual Remote Command Execution

Device / SMB Lateral Movement

Device / Possible SMB/NTLM Brute Force

Unusual Activity / Successful Admin Brute-Force Activity

User / New Admin Credentials on Server

Unusual Activity / Enhanced Unusual External Data Transfer

Unusual Activity / Unusual External Data Transfer

Unusual Activity / Unusual External Data to New Endpoint

Device / Large Number of Model Breaches

Device / Large Number of Model Breaches from Critical Network Device

MITRE ATT&CK Mapping

Tactic – ID: Technique

Initial Access – T1190: Exploit Public-Facing Application

Resource Development – T1587.003: Develop Capabilities: Digital Certificates

Resource Development – T1608.003: Stage Capabilities: Install Digital Certificate

Command and Control – T1071.001: Application Layer Protocol: Web Protocols

Command and Control – T1219: Remote Access Software

Execution – T1059.001: Command and Scripting Interpreter: PowerShell

Reconnaissance – T1595: Active Scanning

Reconnaissance – T1590.005: Gather Victim Network Information: IP Addresses

Discovery – T1046: Network Service Discovery

Credential Access – T1110: Brute Force

Defense Evasion,Initial Access,Persistence,Privilege Escalation – T1078: Valid Accounts

Lateral Movement – T1021.002: Remote Services: SMB/Windows Admin Shares

Lateral Movement – T1021.003: Remote Services: Distributed Component Object Model

Execution – T1569.002: System Services: Service Execution

Execution – T1047: Windows Management Instrumentation

Exfiltration – T1041: Exfiltration Over C2 Channel

Exfiltration – T1567.002: Exfiltration Over Web Service: Exfiltration to Cloud Storage

‍

Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Emily Megan Lim
Cyber Analyst

More in this series

No items found.

Blog

/

AI

/

November 17, 2026

How Microsoft and Darktrace Secure the AI-Powered Enterprise

Default blog imageDefault blog image

When legitimate activity creates business risk

AI is making information more accessible and enabling autonomous agents to act across enterprise systems. But legitimate access can still result in sensitive-data exposure, unintended actions, or activity that deviates from business expectations.

Microsoft's evolving security strategy recognizes this shift, emphasizing continuous risk assessment, stronger identity protection, and security that adapts as AI systems operate. For enterprises, the challenge is increasingly about recognizing when trusted activity introduces risk, even when existing controls are functioning as intended.

Where global intelligence meets deep business context

Microsoft brings global threat intelligence and comprehensive security capabilities, helping organizations protect identities, data, applications, and infrastructure. Its integrated approach connects security signals, governance, detection, and response across increasingly complex environments.

Darktrace complements these strengths with deep, organization-specific behavioral understanding. Powered by Adaptive AI, Darktrace continuously learns the patterns and relationships unique to each business, developing a Unique Behavioral Profile for each organization that helps distinguish meaningful threats from legitimate activity. By connecting identity, activity, context, and intent, it adds another dimension to security intelligence.

Together, Microsoft and Darktrace combine global intelligence with deeper knowledge of how each customer operates. Through supported integrations, this behavioral context enriches existing Microsoft security workflows, enabling more informed investigations and precise response.

This complementary approach extends across three interconnected areas of enterprise security- AI, People and Infrastructure. From understanding how AI and agents operate to protecting trusted communications and the infrastructure businesses depend on, Darktrace strengthens Microsoft's security capabilities with behavioral insight specific to each organization.

Understanding AI beyond permissions and policies

As AI moves into business-critical operations, security teams need to understand more than which applications and agents are approved. They need visibility into how AI is used, what information it accesses, and whether its actions remain aligned with business intent.

Microsoft provides extensive AI development, governance, and security capabilities. Darktrace / SECURE AI complements these with behavioral analysis across Shadow AI, prompts, agent identities and actions, and development risk. Policy Manager helps evaluate activity against organizational AI policies, while the announced integration with Microsoft Agent 365 is designed to enrich agent risk assessments with organization-specific behavioral signals. Together, these capabilities help organizations scale AI adoption with greater confidence.

Recognizing risk within trusted relationships

Sophisticated threats increasingly exploit established business relationships, familiar communications, and legitimate accounts. A message from a trusted supplier or an action taken through an authorized identity may appear routine until considered against the organization's normal behavior.

Darktrace / EMAIL complements Microsoft's native email, identity, and data protection capabilities by understanding how people and organizations communicate. This enables more precise detection of targeted phishing, business email compromise, account takeover, and data loss, supported by proportionate response. Integrations such as Unified Quarantine within Microsoft Defender for Office 365 bring this additional protection into existing security workflows.

Seeing the bigger picture behind an attack across domains

Threats rarely unfold within a single security domain. Suspicious identity activity, unexpected cloud connections, and unusual network behavior may appear unrelated until the relationships between them reveal a developing attack.

Darktrace / HYBRID NETWORK complements Microsoft's security capabilities with organization-specific behavioral detection across network, cloud, identity, and operational technology. Real-Time AI Analyst, including Cyber AI Analyst, connects related activity into investigated incidents that can be delivered into Microsoft Sentinel, helping security teams accelerate investigations and support targeted containment across the hybrid enterprise.

Turning security intelligence into business confidence

As AI becomes more deeply integrated into business operations, organizations need security that understands not only what technology can access, but how it behaves within their unique environment.

Microsoft and Darktrace bring complementary strengths to that challenge. By connecting global threat intelligence and integrated security capabilities with deep behavioral understanding, the partnership helps organizations recognize emerging risks, respond with greater precision, and strengthen their existing security investments.

The opportunity is to turn security intelligence into meaningful business context, enabling organizations to innovate and operate AI with confidence.

Darktrace named a 2026 Microsoft Partner of the Year Finalist for ISV Innovation

Darktrace has been named a finalist for the 2026 Microsoft Partner of the Year Award in the ISV Innovation category.  

This recognition reflects our collaboration with Microsoft to bring business context to enterprise security. By connecting Microsoft's global threat intelligence and integrated security capabilities with Darktrace's deep behavioral understanding, we help organizations recognize emerging risks and respond with greater precision across AI, People and Infrastructure.

Thank you to Microsoft, our customers, and our teams for their continued collaboration.

Meet Darktrace at Microsoft Ignite and the Microsoft Frontier Tour

Explore how Darktrace and Microsoft are bringing behavioral security to AI, people, and infrastructure.

Join Darktrace at Microsoft Ignite in San Francisco, November 17–19, or connect with our experts as we join the Microsoft Frontier Tour across 21 cities worldwide.

Meet Darktrace at Microsoft Ignite

Connect with Darktrace at the Microsoft Frontier Tour

[related-resource]

Continue reading
About the author

Blog

/

AI

/

November 13, 2026

Introducing Darktrace MCP: Connect your AI assistants to the Darktrace Behavioral Defense Platform

Default blog imageDefault blog image

The Darktrace MCP Server is now generally available to users of the Darktrace Platform Portal. It enables compatible AI assistants to query security data, retrieve Cyber AI Analyst findings, and execute supported actions across actively licensed Darktrace products. Customers can now use these capabilities in their own AI workflows to gather incident context, search telemetry, enrich investigations with information from other services, and carry out triage tasks.

What is MCP?
MCP is an open standard developed by Anthropic that lets AI systems connect to and use enterprise tools and data. Adoption of MCP servers creates an opportunity for SOC teams to move beyond isolated AI experiences toward truly operational AI workflows.

Available capabilities

The server exposes tools for three areas of security work:

  • Incident discovery and threat hunting. Retrieve model alerts and incident groups, search for relevant devices and investigate indicators of compromise. Assistants with access to other services can combine these results with external threat intelligence.
  • Investigation and analysis. Retrieve Cyber AI Analyst incident findings, examine related event data, and enrich the investigation with information from other platforms or external documentation.
  • Triage and workflow actions. Add comments, tags and statuses to alerts and assets, modify supported settings such as trusted domains and subnet details, or trigger a Cyber AI Analyst investigation.

Available capabilities depend on the licensed products connected to the server. The toolset also includes access to Secure AI prompt and shadow AI information, cloud misconfigurations and external exposure information, and Email threat trends and supported management functions.

The following examples show how the server’s discovery, investigation, and action capabilities can be combined within an AI assistant.

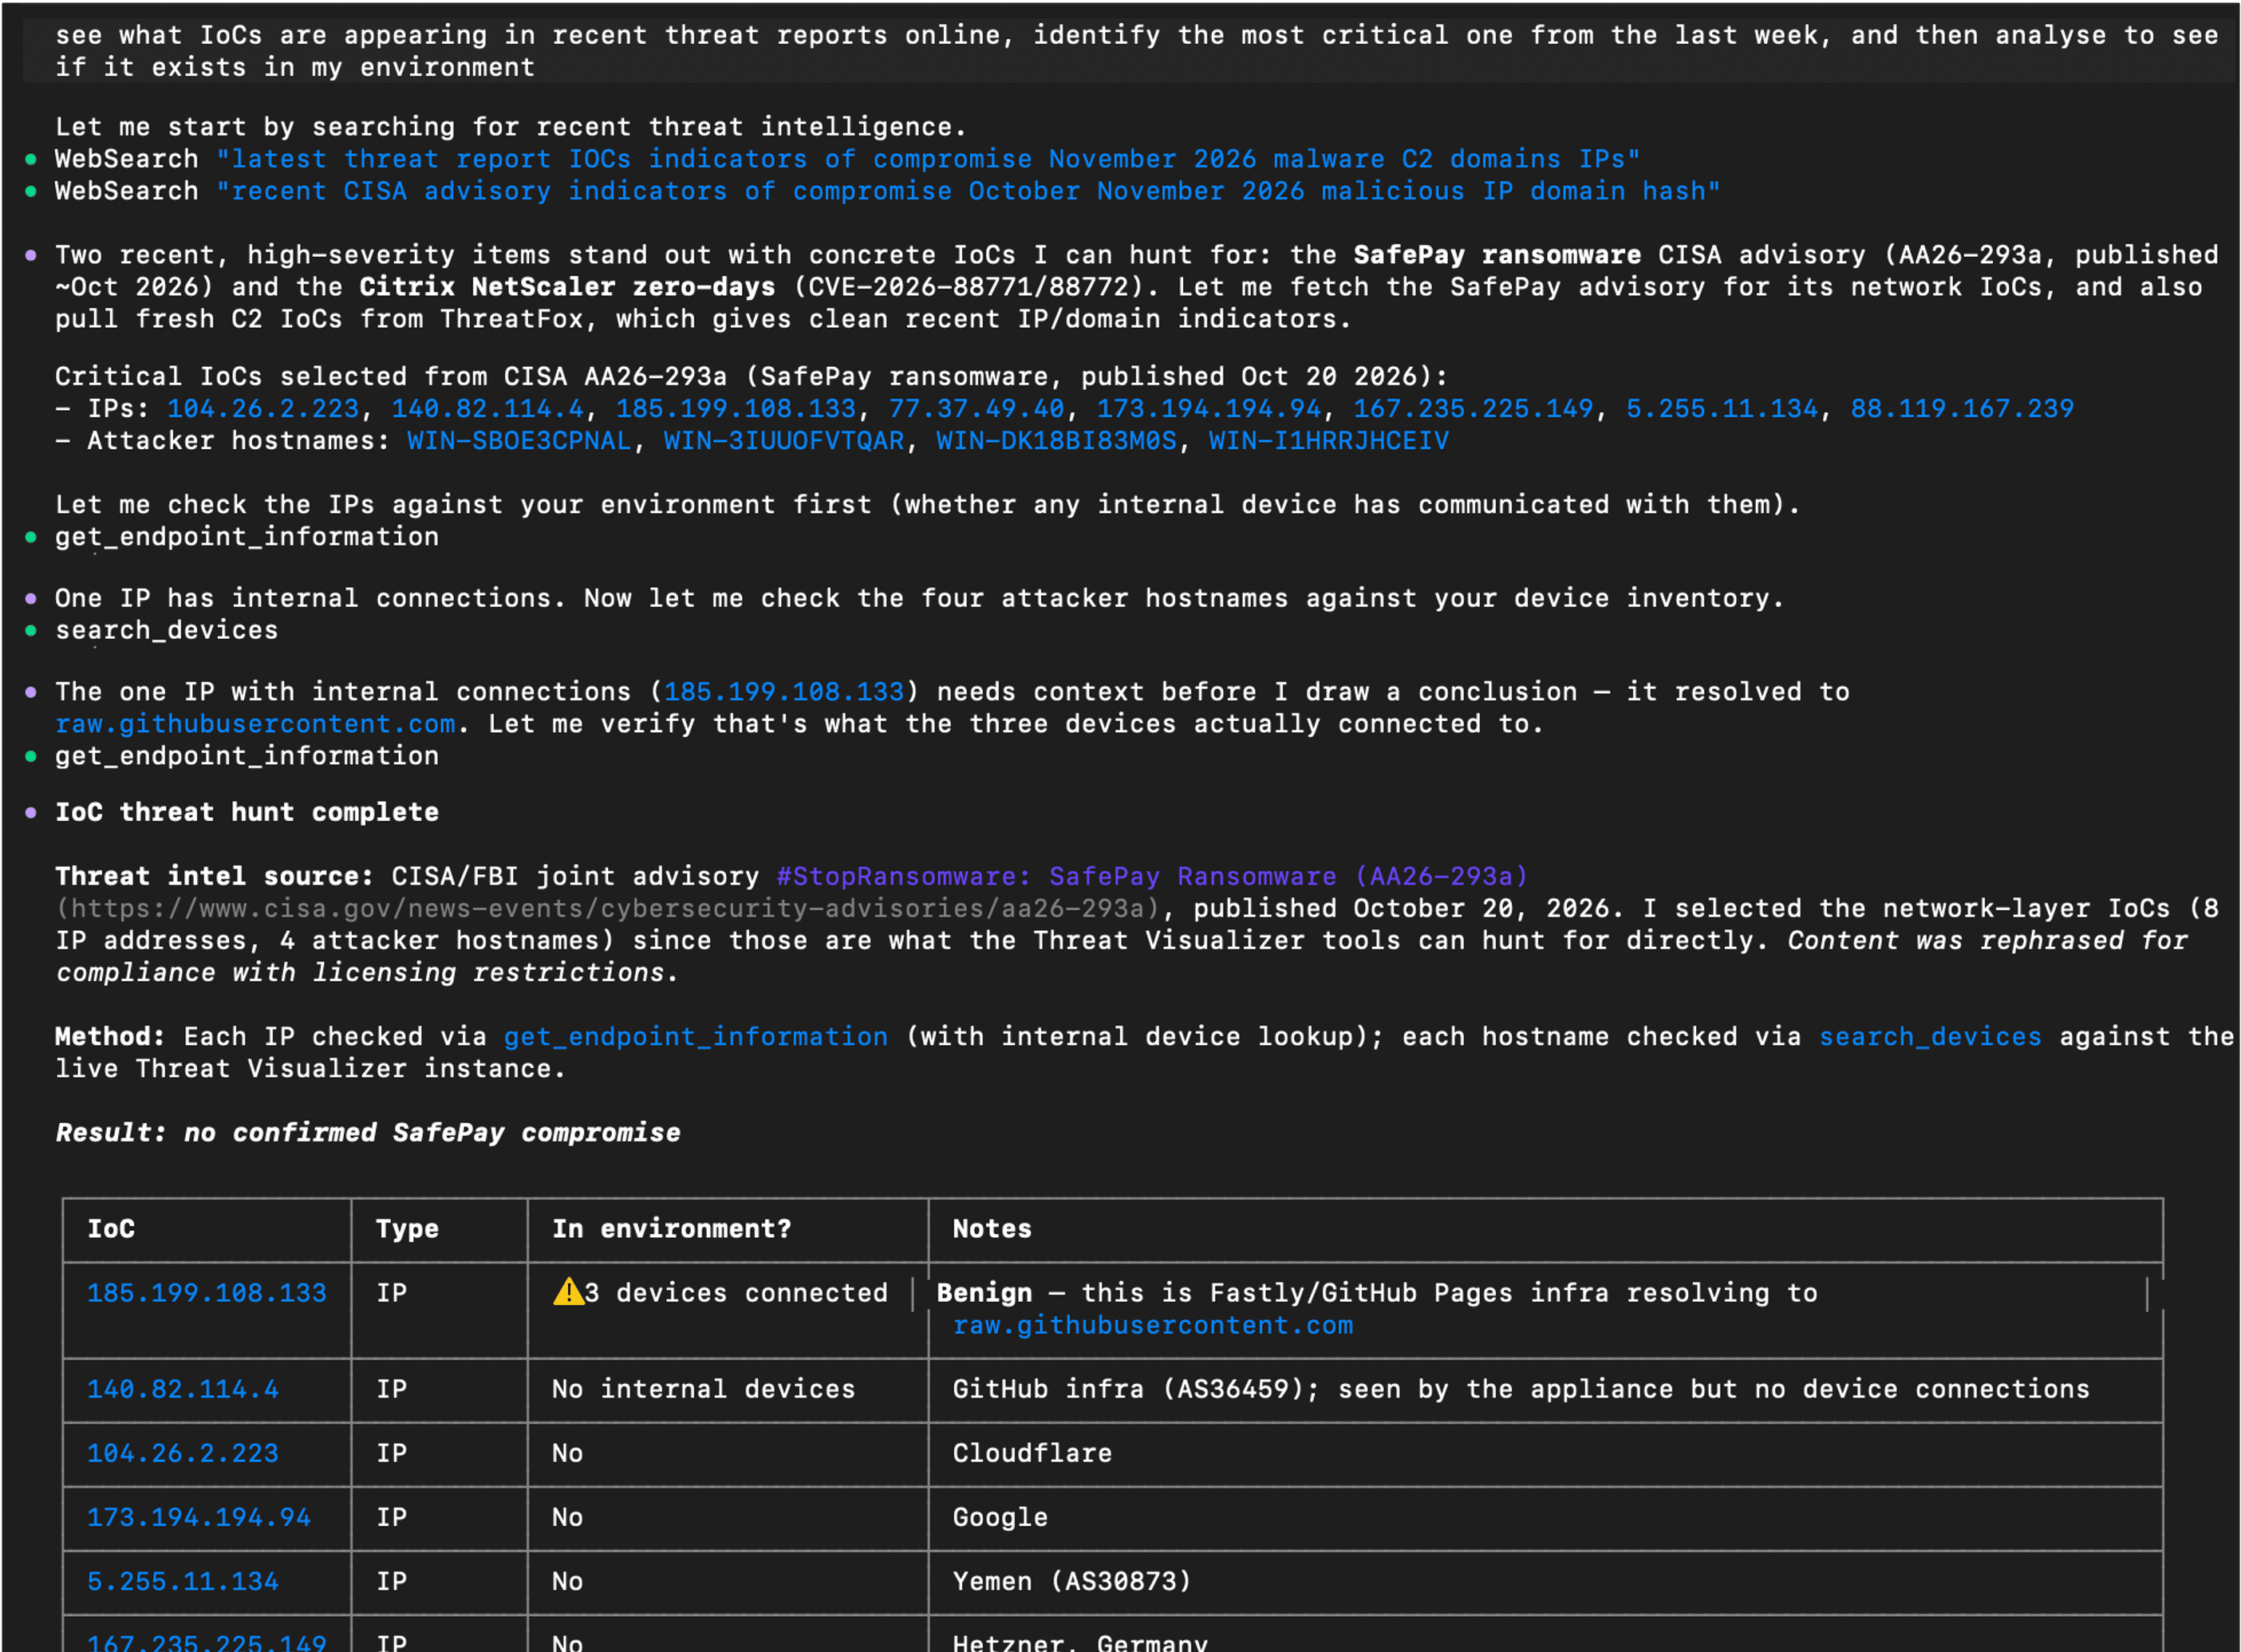
Check external threat indicators against your environment

An assistant can use Darktrace MCP alongside external threat intelligence to check whether reported indicators appear in an environment. Darktrace’s tools provide device information and endpoint context; the assistant’s other tools or connected services supply the external intelligence.

In this example, the assistant searched for recent threat reports, selected indicators of compromise (IoCs) to investigate, and checked for devices that had communicated with the reported IP addresses. It then examined endpoint information to put the matches into context.

Relevant Darktrace tools: search_devices, get_endpoint_information, get_model_alerts, get_incident_events

Example prompt: “See what IoCs are appearing in recent threat reports online, identify the most critical one from the last week, and then analyze to see if it exists in my environment.”

AI assistant output using external threat intelligence alongside data retrieved through the Darktrace MCP Server.

Enrich a Cyber AI Analyst investigation

Cyber AI Analyst provides Darktrace’s incident analysis. Through MCP, an assistant can retrieve those findings, explain specific parts of an incident, and bring in related data from other services.

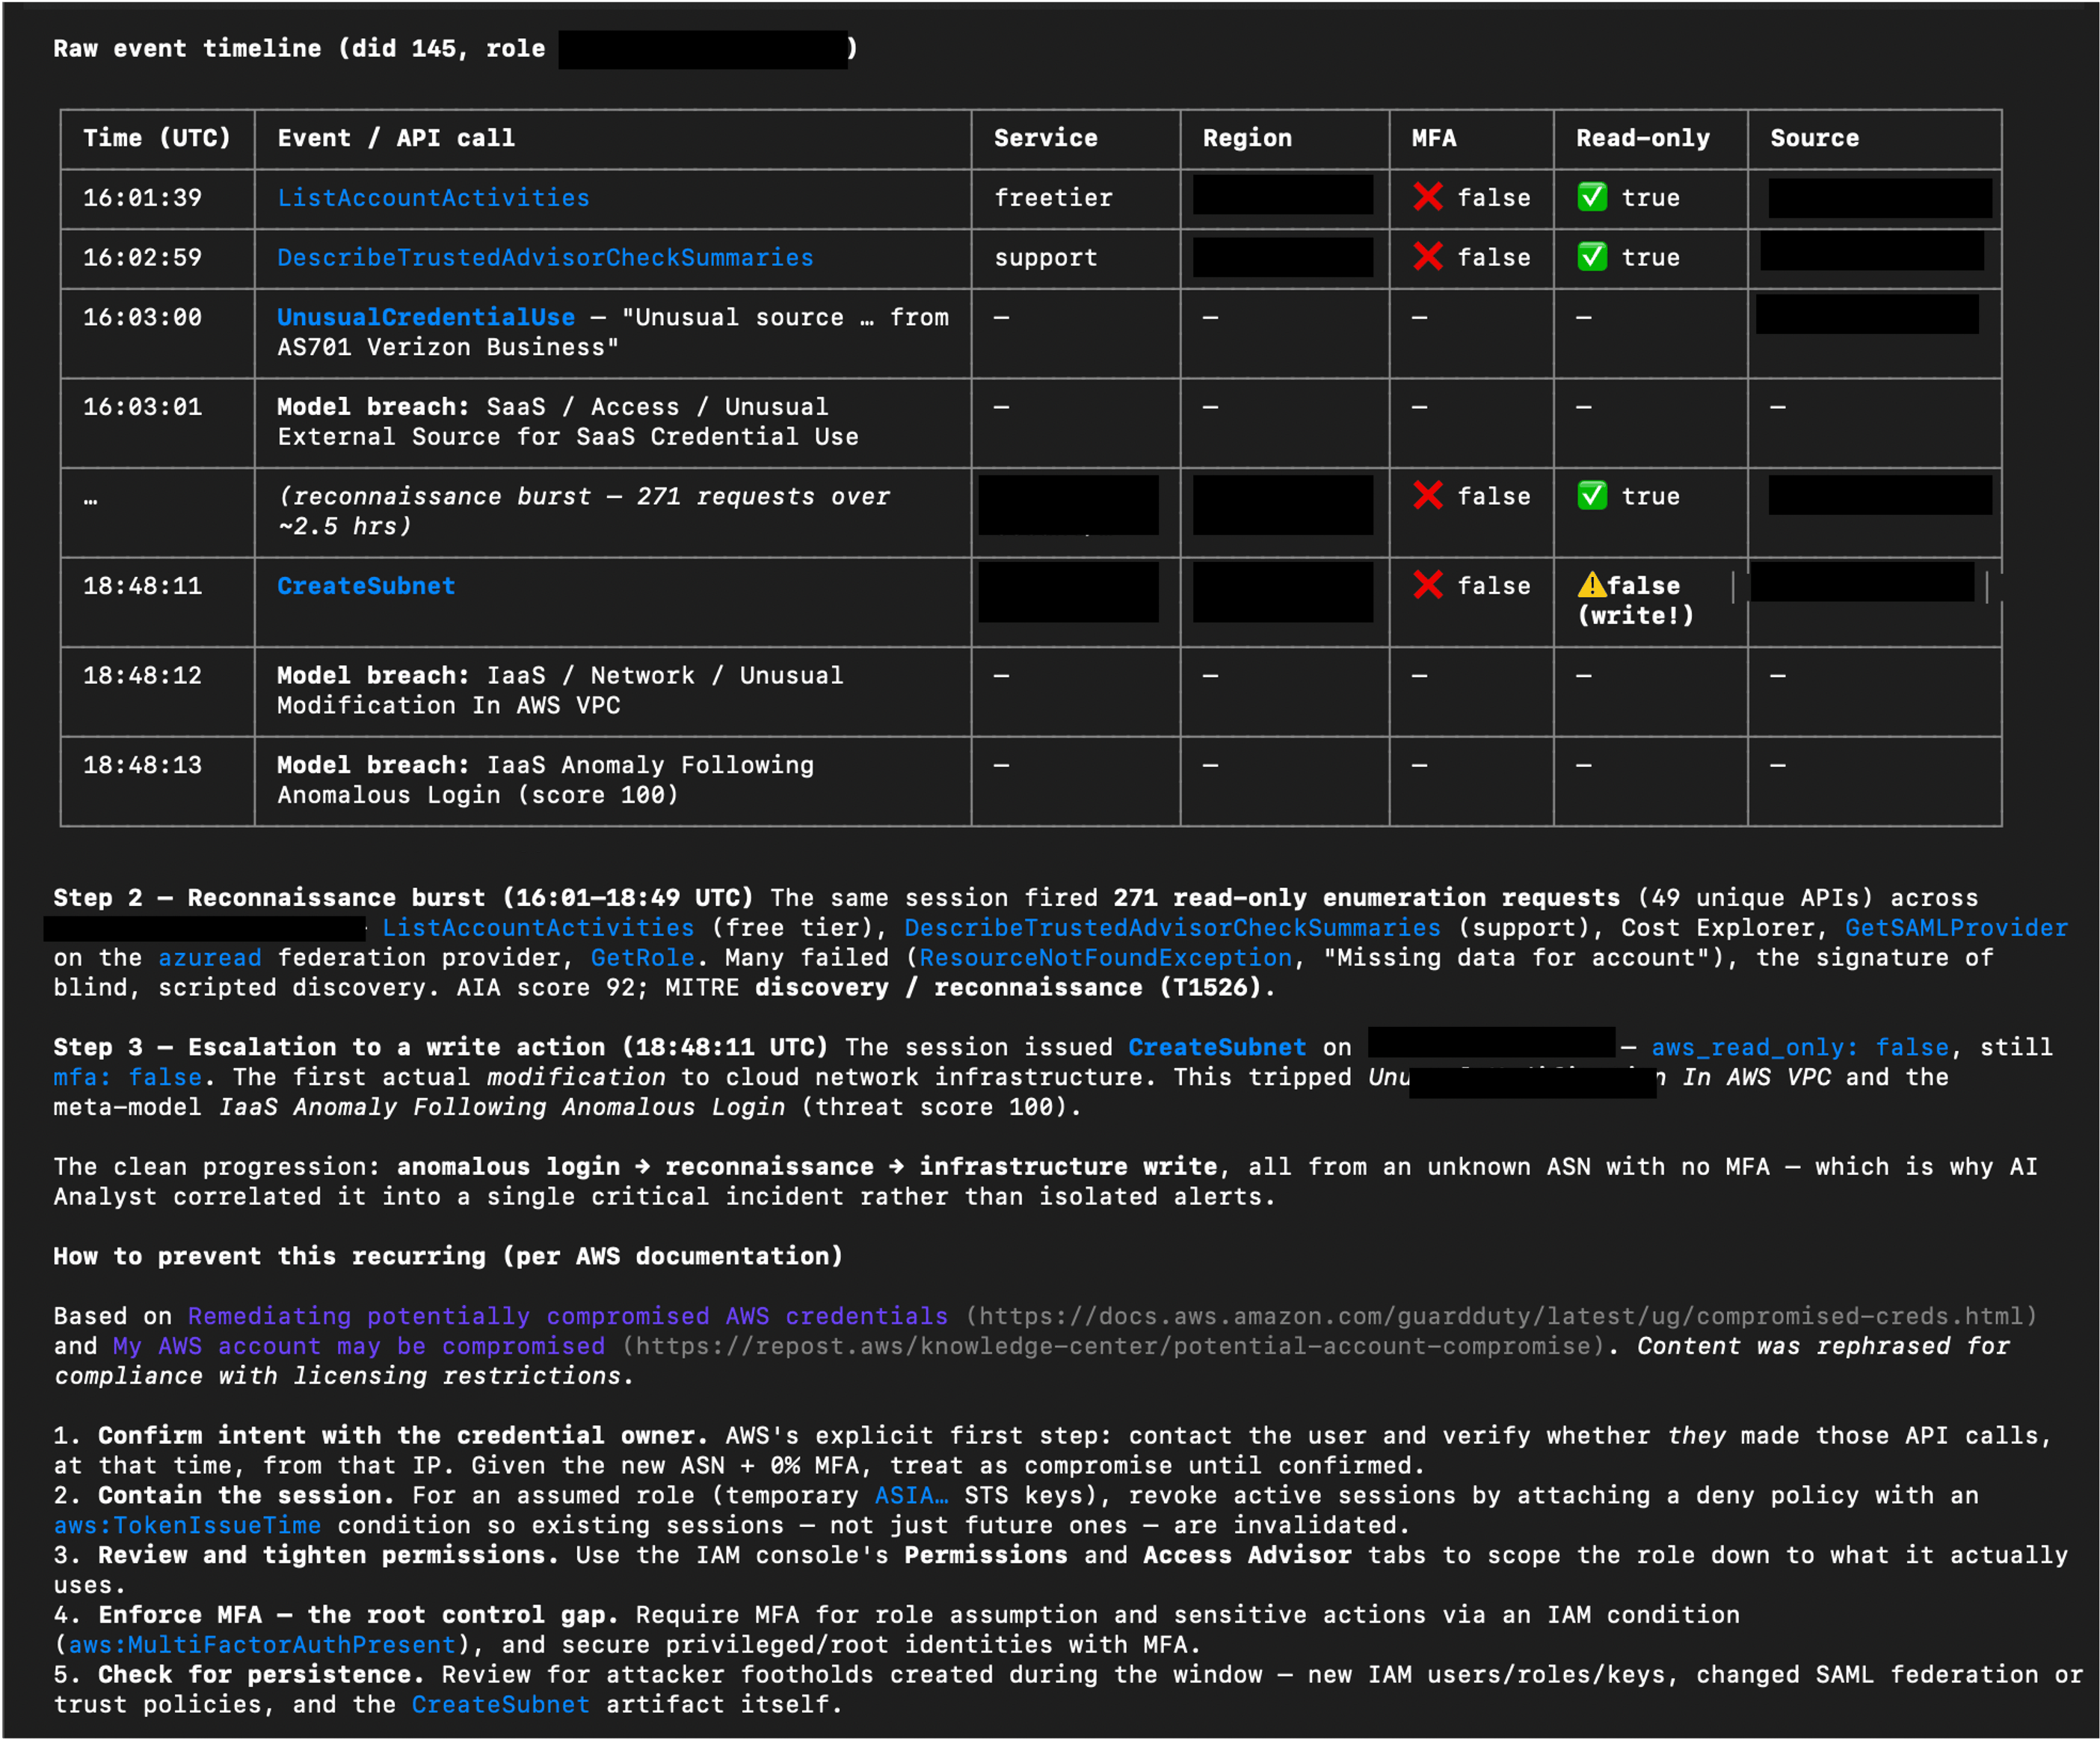
In this example, the assistant examined a Potential AWS Account Hijack investigated by Cyber AI Analyst. It assembled a step-by-step account and raw event timeline, then consulted AWS documentation to add relevant prevention guidance. The assistant brings together the existing Darktrace analysis, supporting events, and external guidance in one response.

Relevant Darktrace tools: get_incident_groups, get_incident_events, get_detailed_events, get_ai_analyst_investigations, advanced_search

Example prompt: “Drill down on the identified potential AWS account hijack. Show me a detailed step-by-step of what happened using data from Cyber AI Analyst, including a raw event timeline, and provide info on how to prevent this from happening again using info from AWS documentation.”

AI assistant output combining Cyber AI Analyst findings and event data with guidance from AWS documentation. Some sensitive content has been redacted.

Work through triage with analyst confirmation

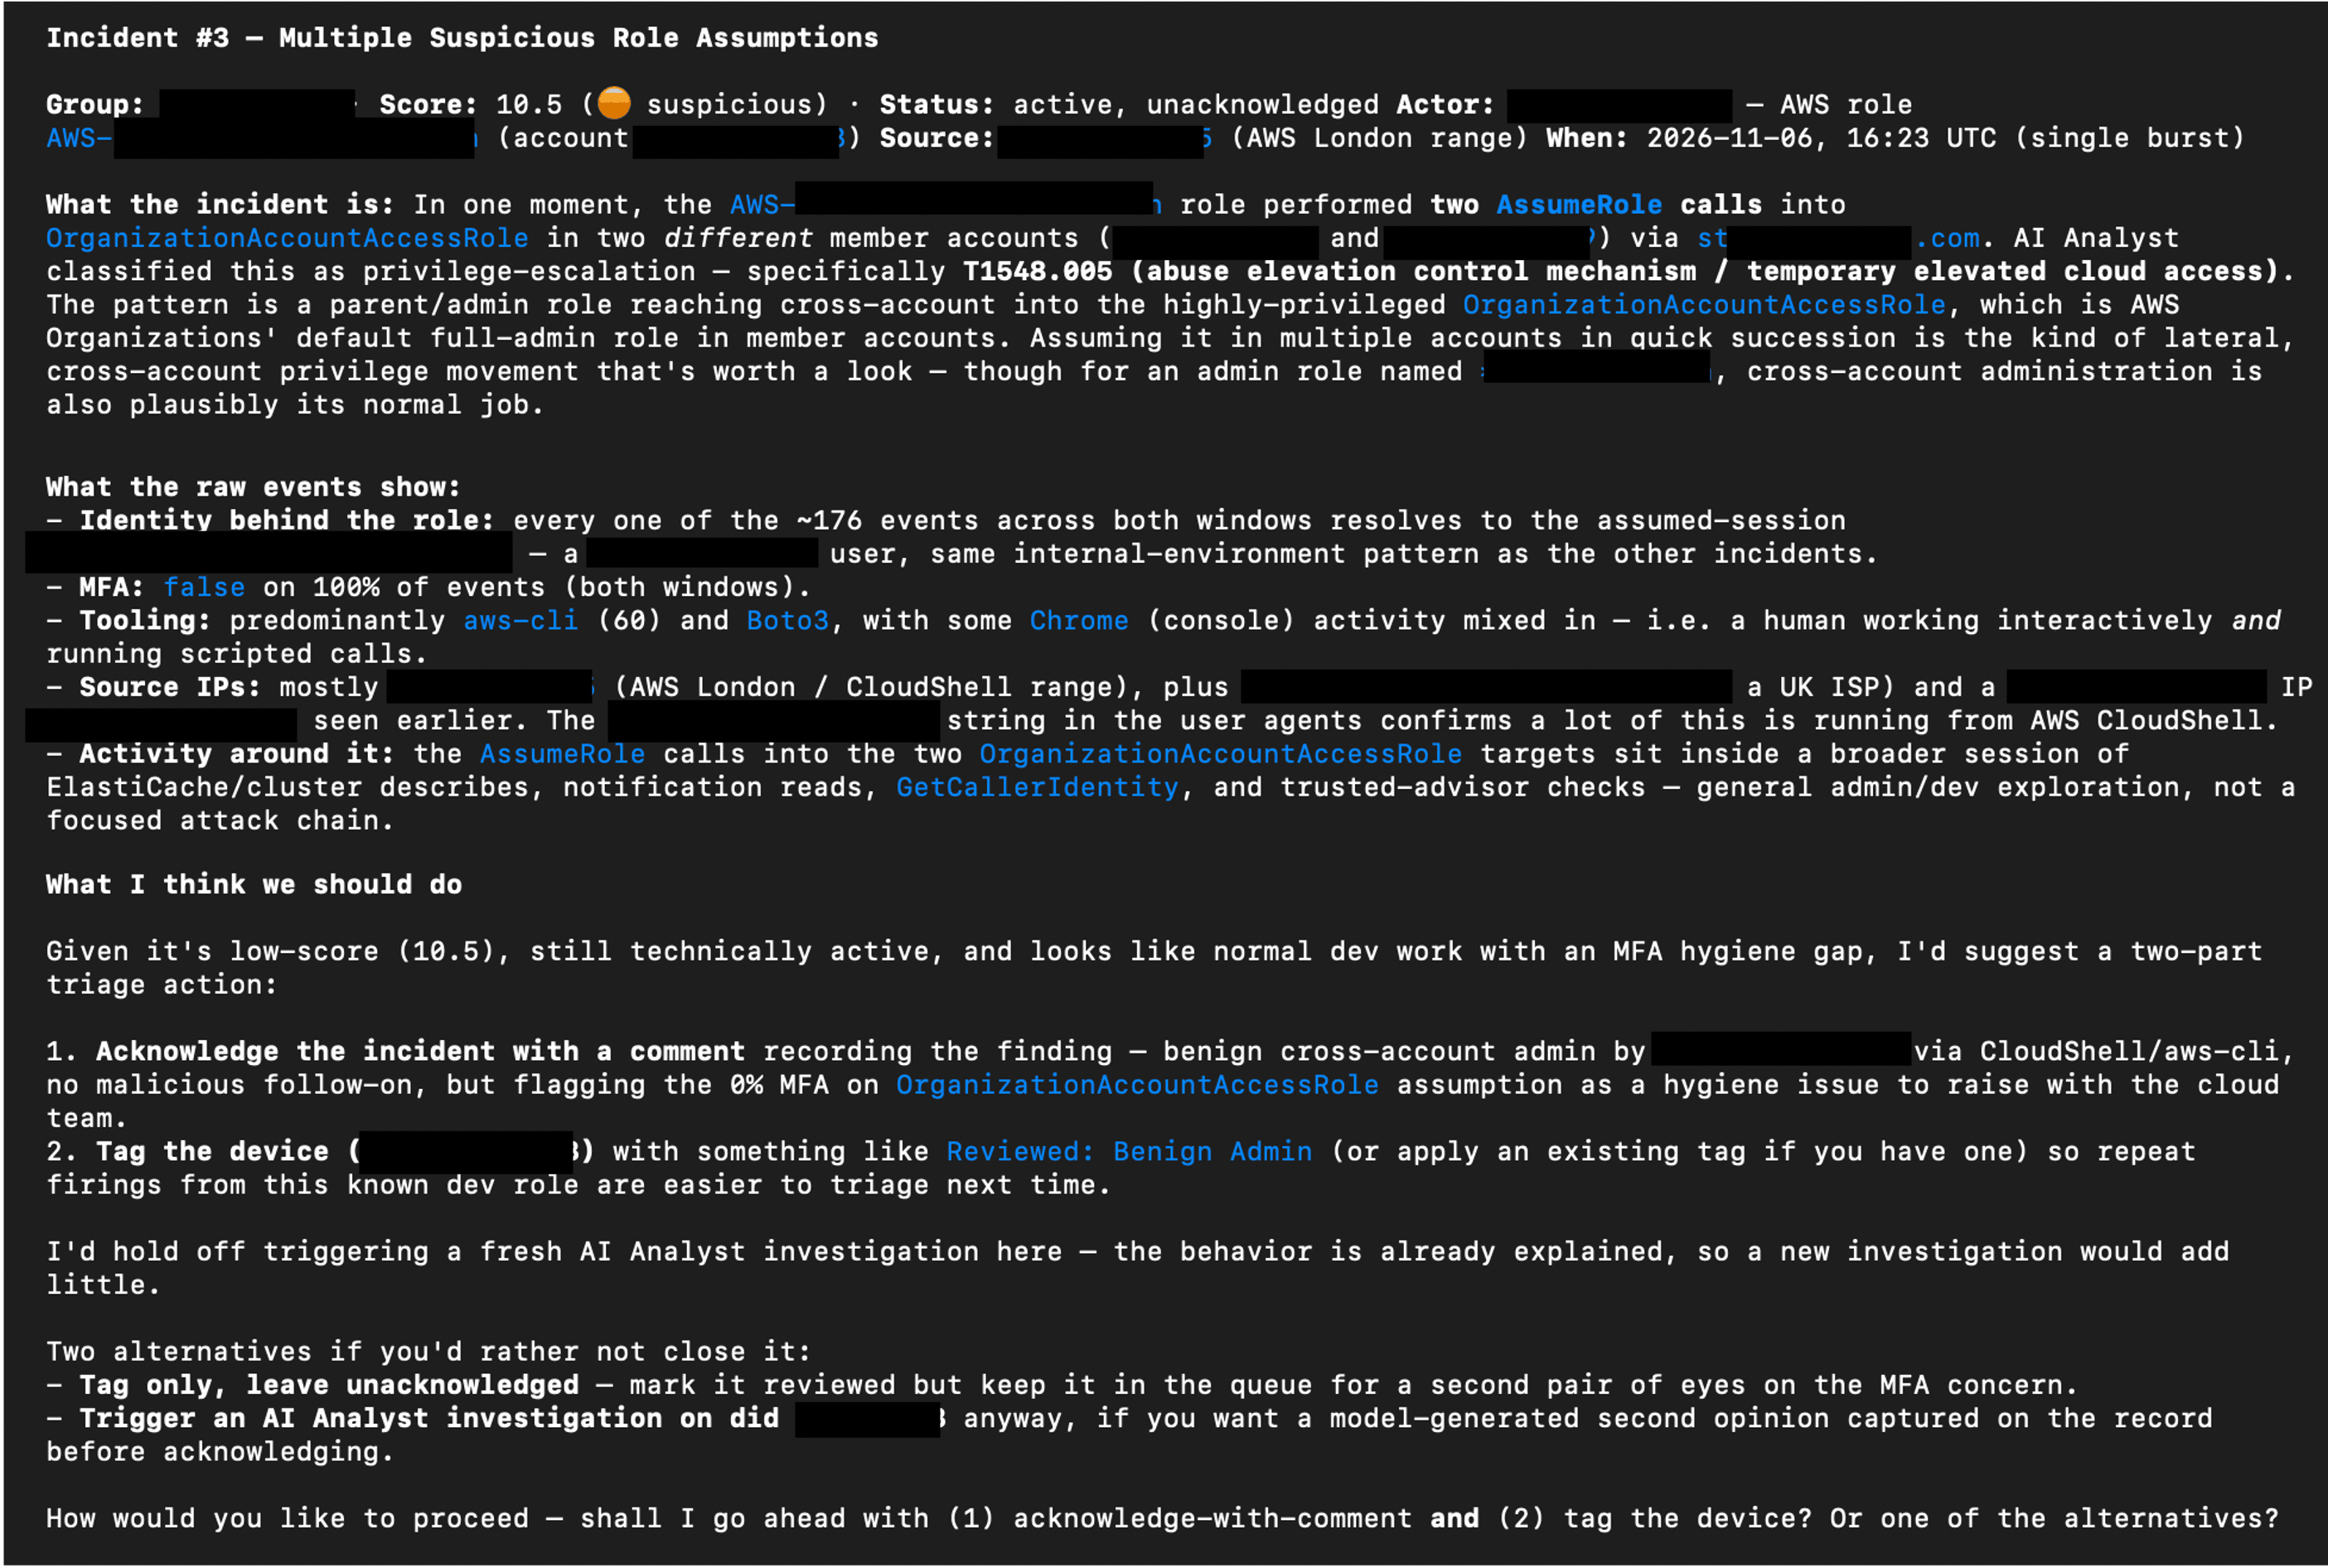
The server’s action tools allow an assistant to support repetitive triage tasks as well as retrieve information. For example, to improve efficiency of a daily triage workflow, an analyst could ask an AI assistant to present untriaged alerts one at a time, summarizing each issue and suggesting a next step for confirmation.

The example below shows the assistant proposing actions such as recording a finding, acknowledging an incident, tagging an asset, or triggering a Cyber AI Analyst investigation for more detail. The analyst chooses how to proceed.

Relevant Darktrace tools: get_model_alerts, update_model_alert, update_incident_group, manage_tags, create_ai_analyst_investigation

Example prompt: “Using the Darktrace MCP server, obtain all un-triaged alerts from the last 3 days and display them one at a time. Provide a summary of the issue, and a suggested triage and immediate response action. I will confirm what action should be performed.”

AI assistant output proposing triage actions using information retrieved through Darktrace MCP and asking the analyst how to proceed. Some sensitive content has been redacted.

Permissions and security considerations

The MCP server provides access to supported capabilities within the products a customer is licensed to use. Connections should follow the principle of least privilege, with access appropriate to the intended workflow.

A read-only connection mode is also available for workflows that do not require changes. This mode hides tools that mutate data; configuration details are provided in the Product Guide.

Some tools can change data or perform actions, including adding or removing asset tags, triggering Cyber AI Analyst investigations, and acting on assets. Consider which capabilities an assistant should be able to use before connecting it and retain human oversight of actions that could cause disruption or unwanted changes.

For further guidance, see:

Seven MCP risks CISOs should consider and how to prepare

Anthropic’s MCP Security Best Practices

Use the interface that suits the task

MCP gives customers another way to work with Darktrace alongside its product interfaces. Users may find that complex investigations requiring visual analysis, or strategic decisions involving impactful actions, are better suited to the graphical interfaces within Darktrace products. They can choose the approach that fits their workflow.

How to start using the Darktrace MCP Server

The Darktrace MCP Server is used to connect a compatible AI assistant to supported tools within your Darktrace deployment. The assistant can retrieve alerts and device information, draw on Cyber AI Analyst findings, and perform permitted actions across your licensed products.

To get started, you will need access to the Darktrace Platform Portal and a compatible AI assistant. Follow the Platform Portal MCP Server guide to find out how to create the required credentials and configure the connection today.

Contact a Darktrace representative to explore how the Darktrace MCP Server can support your security operations.

To learn more about Darktrace can help protect your MCP servers within your broader AI and agent use, discover Darktrace / SECURE AI.

‍

Appendix: Darktrace MCP available tools

The following tool catalogue reflects the list supplied for this announcement. Available tools depend on the connected products and access. The list may change as tools are added or removed.

ToolProductDescription
get_helpGeneral / MCP ServerReturns orientation info about the Darktrace MCP server: its purpose, tool categories, and documentation.
get_productsGeneral / MCP ServerLists available Darktrace product instances and their instance_id values needed by other tools.
submit_feedbackGeneral / MCP ServerLogs feedback about tool coverage, clarity, or usability for the Darktrace team.
count_devicesThreat VisualizerReturns the total count of devices/assets managed by Darktrace.
search_devicesThreat VisualizerSearches for devices by keyword and returns basic matching device details.
query_devicesThreat VisualizerQueries comprehensive device information using filters like IP, MAC, subnet, or SaaS module.
edit_deviceThreat VisualizerUpdates a device's label, type, priority, or notes.
get_device_activityThreat VisualizerReturns aggregated time-series data of a device's connection/data volume trends over 4 weeks.
get_detailed_eventsThreat VisualizerRetrieves individual low-level events (connections, notices, model breaches, processes) for a device or alert.
get_subnetsThreat VisualizerRetrieves monitored subnets with CIDR, device counts, DHCP status, and traffic stats.
update_subnetThreat VisualizerEdits subnet details such as label, network range, coordinates, and DHCP/exclusion flags.
get_model_alertsThreat VisualizerRetrieves model alerts (breaches) with model info, device details, and triggered components.
get_model_alert_credentialsThreat VisualizerReturns credentials seen on the device that triggered a given model alert.
update_model_alertThreat VisualizerComments on and/or acknowledges a model alert.
get_modelsThreat VisualizerRetrieves detection models with their logic, actions, and configuration.
get_incident_groupsThreat VisualizerRetrieves AI Analyst incident groups with scores, MITRE tactics, devices, and summaries.
get_incident_eventsThreat VisualizerRetrieves AI Analyst incident events with AI summaries, MITRE tactics, and breach details.
update_incident_groupThreat VisualizerComments on and/or acknowledges an AI Analyst incident group.
create_ai_analyst_investigationThreat VisualizerCreates a manual AI Analyst investigation for a device around a specified time.
get_ai_analyst_investigationsThreat VisualizerRetrieves the status and results of manual AI Analyst investigations.
advanced_searchThreat VisualizerExecutes a Lucene-syntax Advanced Search query against Darktrace log data.
get_advanced_search_syntaxThreat VisualizerReturns the full Advanced Search query syntax reference (must be called before querying).
get_response_actions_summaryThreat VisualizerReturns a summary of active and pending Autonomous Response actions and action counts over a time range.
get_endpoint_informationThreat VisualizerLooks up external endpoints (IPs/hostnames) for location, reputation, and connection history.
get_cvesThreat VisualizerRetrieves CVEs detected across assets with severity, scores, and affected devices.
get_system_healthThreat VisualizerReturns comprehensive system health metrics (CPU, memory, disk, licenses, bandwidth).
get_dam_alertsThreat VisualizerRetrieves health alerts from the Darktrace Alert Management system.
get_module_statusesThreat VisualizerRetrieves the status of Darktrace modules, optionally filtered to failing ones.
get_tagsThreat VisualizerRetrieves device tags and optionally the devices/credentials they are applied to.
manage_tagsThreat VisualizerCreates, deletes, applies, or removes tags on devices or credentials.
get_trusted_domainsThreat VisualizerRetrieves domains marked as trusted.
manage_trusted_domainsThreat VisualizerAdds or removes a trusted domain entry.
get_watched_domainsThreat VisualizerRetrieves watched domains monitored for suspicious activity.
manage_watched_domainsThreat VisualizerAdds or removes watched domain entries.
get_workflow_integration_ticketsThreat VisualizerRetrieves third-party platform tickets created by Workflow Integrations for Darktrace events.
get_cloud_accountsDarktrace / HYBRID NETWORKRetrieves cloud deployment accounts and their monitoring/compliance statuses.
get_cloud_architecturesDarktrace / HYBRID NETWORKRetrieves cloud architectures with risk breakdown, cost, and asset counts.
get_cloud_assetsDarktrace / HYBRID NETWORKRetrieves cloud assets with type, service, region, and attached/associated assets.
get_cloud_asset_filtersDarktrace / HYBRID NETWORKReturns available filter fields and operators for querying cloud assets.
get_cloud_misconfiguration_alertsDarktrace / HYBRID NETWORKRetrieves cloud security misconfiguration alerts grouped by rule.
get_cloud_misconfigured_assetsDarktrace / HYBRID NETWORKRetrieves the assets affected by a specific cloud misconfiguration rule.
get_cloud_rule_informationDarktrace / HYBRID NETWORKReturns detailed rationale, remediation, and compliance mappings for a cloud security rule.
get_emailDarktrace / EMAILRetrieves detailed information about a specific email by UUID.
search_emailsDarktrace / EMAILSearches for emails using filters and a time range.
get_email_search_filtersDarktrace / EMAILReturns available email search filter definitions and values.
action_emailDarktrace / EMAILPerforms an action (hold, release, approve/reject release) on an email for specific recipients.
analyse_email_linkDarktrace / EMAILAnalyzes a URL found in an email, returning classification tags and analysis metrics.
get_email_overviewDarktrace / EMAILReturns an aggregated email dashboard overview (threats, actions, campaigns, etc.).
get_email_listsDarktrace / EMAILRetrieves email lists and their entries.
manage_email_listsDarktrace / EMAILAdds or edits email lists, and adds or removes entries within an email list.
get_email_addin_recordsDarktrace / EMAILRetrieves Inbox Analysis or Misdirected Email add-in records.
get_email_audit_logsDarktrace / EMAILRetrieves EMAIL system audit log events for a time range.
get_email_audit_log_event_typesDarktrace / EMAILReturns available audit log event types for filtering.
get_secure_ai_overviewDarktrace / SECURE AIReturns a dashboard overview of Secure AI activity (anomaly scores, sessions, prompt categories).
get_secure_ai_sessionsDarktrace / SECURE AIRetrieves monitored generative-AI sessions with risk levels and anomaly scores.
get_secure_ai_promptsDarktrace / SECURE AIRetrieves individual prompts for a Secure AI session with anomaly/risk classifications.
get_secure_ai_usersDarktrace / SECURE AIRetrieves users interacting with generative-AI apps, with risk scores and session counts.
get_secure_ai_eventsDarktrace / SECURE AIRetrieves raw events ingested by the Secure AI post-handler.
get_secure_ai_detectionsDarktrace / SECURE AIRetrieves detections raised by Secure AI models with scores and OWASP/ATLAS mappings.
get_secure_ai_response_actionsDarktrace / SECURE AIRetrieves Autonomous Response actions taken by Secure AI.
manage_secure_ai_response_actionDarktrace / SECURE AIClears, confirms, extends, or reactivates a Secure AI response action.
get_shadow_ai_dashboardDarktrace / SECURE AIReturns the Shadow AI dashboard of unsanctioned AI/LLM services detected.
get_shadow_ai_detectionsDarktrace / SECURE AIRetrieves individual Shadow AI detections for unsanctioned AI/LLM service usage.
get_forensic_investigationsDarktrace / HYBRID NETWORKRetrieves forensic investigations with status, alarm counts, and AI summaries.
get_forensic_evidencesDarktrace / HYBRID NETWORKRetrieves evidence items with alarm counts, OS details, and processing status.
get_forensic_evidence_fileDarktrace / HYBRID NETWORKReturns detailed file metadata/content (hash, strings, VirusTotal, AI description) from an evidence item.
browse_forensic_evidence_filesDarktrace / HYBRID NETWORKBrowses the filesystem of a forensic evidence item, filtering by severity, path, or name.
get_forensic_alarmsDarktrace / HYBRID NETWORKRetrieves alarms from an investigation or evidence item with severity and MITRE techniques.
get_forensic_artifactsDarktrace / HYBRID NETWORKRetrieves detection artifacts (files, hashes, processes, users, IPs, domains) from an investigation.
get_forensic_detectionsDarktrace / HYBRID NETWORKRetrieves XDR/EDR detections with MITRE ATT&CK mappings.
get_forensic_indicatorsDarktrace / HYBRID NETWORKRetrieves indicators of compromise (IOCs) from an investigation.
get_forensic_vulnerabilitiesDarktrace / HYBRID NETWORKRetrieves vulnerabilities (CVEs) with CVSS scoring and package info.
get_forensic_pipelinesDarktrace / HYBRID NETWORKRetrieves processing/acquisition pipelines with real-time status.
get_forensic_timelineDarktrace / HYBRID NETWORKRetrieves or facets timeline events from a forensic investigation.
get_forensic_search_syntaxDarktrace / HYBRID NETWORKReturns the Forensic Search query syntax reference (call before forensic timeline queries).

[related-resource]

Continue reading
About the author
Jamie Bali
Technical Author (AI) Developer
Your data. Our AI.
Elevate your network security with Darktrace AI