Blog
/
/
August 25, 2020

Emotet Resurgence: Email & Network Defense Insights

Explore how Darktrace's defense in depth strategy combats Emotet's resurgence in email and network layers, ensuring robust cybersecurity.
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Max Heinemeyer
Global Field CISO
Written by
Dan Fein
VP, Product
Default blog image
25
Aug 2020

The Emotet banking malware first emerged in 2014, and has since undergone multiple iterations. Emotet seeks to financially profit from a range of organizations by spreading rapidly from device to device and stealing sensitive financial information.

Darktrace’s AI has detected the return of this botnet after a five month absence. The new Spamware campaign has hit multiple industries through highly sophisticated phishing emails, containing either URLs linking to the download of a macro-containing Microsoft Word document or an attachment of the document itself. This iteration uses new variants of infrastructure and malware that were unknown to threat intelligence lists – thus easily bypassing static, rule-based defenses.

In this blog post, we investigate the attack from two angles. The first documents a case where Emotet successfully infiltrated a company’s network, where it was promptly detected and alerted on by the Enterprise Immune System. We then explore two customers who had extended Darktrace’s Cyber AI coverage to the inbox. While these organizations were also targeted by this latest Emotet campaign, the malicious email containing the Emotet payload was identified and blocked by Antigena Email.

Case study one: Detecting Emotet in the network

Figure 1: A timeline of the attack

This first case study looks at a large European organization spanning multiple industries, including healthcare, pharmaceuticals, and manufacturing. Darktrace’s AI was monitoring over 2500 devices when the organization became a victim of this new wave of Emotet.

The attack entered the business via a phishing email that fell outside of Darktrace’s scope in this particular deployment, as the customer had not yet activated Antigena Email. Either a malicious link or a macro-embedded Word document in the email directed a device to the malicious payload.

Darktrace’s Enterprise Immune System witnessed SSL connections to a 100% rare external IP address, and detected a Kernel crash on the device shortly afterwards, indicating potential exploitation.

Following these actions, the desktop began to beacon to multiple external endpoints using self-signed or invalid SSL certificates. The observed endpoints had previously been associated with Trickbot C2 servers and the Emotet malware. The likely overall dwell time – that is the length of time an attacker has free reign in an environment before they are eradicated – was in this instance around 24 hours, with most of the activity taking place on July 23.

The device then made a large number of new and unusual internal connection attempts over SMB (port 445) to 97 internal devices during a one-hour period. The goal was likely lateral movement, possibly with the intention to infect other devices, download additional malware, and send out more spam emails.

Darktrace’s AI had promptly alerted the security team to the initial rare connections, but when the device attempted lateral movement it escalated the severity of the alert. The security team was able to remediate the situation before further damage was done, taking the desktop offline.

This overview of the infected device shows the extent of the anomalous behavior, with over a dozen Darktrace detections firing in quick succession.

Figure 2: A graph showing unusual activity in combination with the large number of model breaches on July 23

Figure 3: A list of all model breaches occurring over a small time on the compromised device

Case study two: Catching Emotet in the email environment

While Darktrace’s Enterprise Immune System allows us to visualize the attack within the network, Antigena Email has also identified the Emotet phishing campaign in many other customer environments and stopped the attack before the payload could be downloaded.

One European organization was hit by multiple phishing emails associated with Emotet. These emails use a number of tactics, including personalized subject lines, malicious attachments, and hidden malicious URLs. However, Darktrace’s AI recognized the emails as highly anomalous for the organization and prevented them from reaching employees’ inboxes.

Figure 4: A snapshot of Antigena Email’s user interface. The subject line reads ‘Notice of transfer.’

Despite claiming to be from CaixaBank, a Spanish financial services company, Antigena Email revealed that the email was actually sent from a Brazilian domain. The email also contained a link that was hidden behind text suggesting it would lead to a CaixaBank domain, but Darktrace recognized this as a deliberate attempt to mislead the recipient. Antigena Email is unique in its ability to gather insights from across the broader business, and it leveraged this ability to reveal that the link in fact led to a WordPress domain that Darktrace’s AI identified as 100% rare for the business. This would not have been possible without a unified security platform analyzing and comparing data across different parts of the organization.

Figure 5: The malicious links contained in the email

The three above links surfaced by Darktrace are all associated with the Emotet malware, and prompt the user to download a Word file. This document contains a macro with instructions for downloading the actual virus payload.

Another email targeting the same organization contained a header suggesting it was from Vietnam. The sender had never been in any previous correspondence across the business, and the single, isolated link within the email was also revealed to be a 100% rare domain. The website displayed when visiting the domain imitates a legitimate printing business, but appears hastily made and contained a similar malicious payload.

In both cases, Darktrace’s AI recognized these as phishing attempts due to its understanding of normal communication patterns and behavior for the business and held the emails back from the inbox, preventing Emotet from entering the next phase of the attack life cycle.

Case study three: A truly global campaign

Darktrace has seen Emotet in attacks targeting customers around the world, with one of the most recent campaigns aimed at a food production and distribution company in Japan. This customer received six Emotet emails across July 29 and July 30. The senders spoofed Japanese names and some existing Japanese companies, including Mitsubishi. Antigena Email successfully detected and actioned these emails, recognizing the spoofing indicators, ‘unspoofing’ the emails, and converting the attachments.

Figure 6: A second Emotet email targeting an organization in Japan

Revealing a phish

Both the subject line and the filename translate to “Regarding the invoice,” followed by a number and the date. The email imitated a well-known Japanese company (三菱食品(株)), with ‘藤沢 昭彦’ as a common Japanese name and the appended ‘様’ serving a similar function to ‘Sir’ or ‘Dr,’ in a clear attempt to mimic a legitimate business email.

A subsequent investigation revealed that the sender’s location was actually Portugal, and the hash values of Microsoft Word attachments were consistent with Emotet. Crucially, at the time of the attack, these file hashes were not publicly associated with any malicious behavior and so could not have been used for initial detection.

Figure 7: Antigena Email shows critical metrics revealing the true source of the email

Surfacing further key metrics behind the email, Antigena Email revealed that the true sender was using a GMO domain name. GMO is a Japanese cloud-hosting company that offers cheap web email services.

Figure 8: Antigena Email reveals the anomalous extensions and mimes

The details of the attachment show that both the extension and mime type is anomalous in comparison to documents this customer commonly exchanges by email.

Figure 9: Antigena Email detects the attempt at inducement

Antigena Email’s models are able to recognize topic anomalies and inducement attempts in emails, regardless of the language they are written in. Despite this email being written in Japanese, Darktrace’s AI was still able to reveal the attempt at inducement, giving the email a high score of 85.

Figure 10: The six successive Emotet emails

The close proximity in which these emails were sent and the fact they all contained URLs consistent with Emotet suggests that they are likely part of the same campaign. Different recipients received the emails from different senders in an attempt to bypass traditional security tools, which are trained to deny-list an individual sender once it is recognized as bad.

A defense in depth

This new campaign and the comeback of the Emotet malware has shown the need for defense in depth – or having multiple layers of security across the different areas of a business, including email, network, cloud and SaaS, and beyond.

Historically, defense in depth has led companies to adopt myriad point solutions, which can be both expensive and challenging to manage. Security leaders are increasingly abandoning point solutions in favor of a single security platform, which not only makes handling the security stack easier and more efficient, but creates synergies between different parts of the platform. Data can be analyzed across different sources and insights drawn from different areas of the organization, helping detect sophisticated attacks that might attempt to exploit a business’ siloed approach to security.

A single platform ultimately reduces the friction for security teams while allowing for effective, company-wide incident investigation. And when a platform approach leverages AI to understand normal behavior rather than looking for ‘known bad’, it can detect unknown and emerging threats – and help prevent damage from being done.

Thanks to Darktrace analyst Beverly McCann for her insights on the above threat find.

‍

Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Max Heinemeyer
Global Field CISO
Written by
Dan Fein
VP, Product

More in this series

No items found.

Blog

/

Network

/

November 17, 2026

GTA VI Cyber Threats: Fake downloads, ransomware and account hijacking

Default blog imageDefault blog image

Key findings

  • Darktrace detected GTA VI-themed suspicious activity across organizations in multiple sectors ahead of the game’s release, showing how malicious gaming content can reach corporate environments outside the gaming industry.
  • Twelve Darktrace customer environments connected to gta6demo[.]asia, a domain that public threat research has associated with a fake GTA VI demo used to distribute the Vidar infostealer. Seven of the twelve communicated with infrastructure associated with AS56322 ServerAstra Kft as part of this connectivity.

·       Darktrace investigated ransomware activity at two European games companies. One incident involved DireWolf ransomware alongside reported data exfiltration. A separate Qilin incident included Active Directory reconnaissance, new administrative credentials, possible lateral movement and substantial cloud-storage transfers before ransomware deployment.

  • Another incident on a gaming organization involved a SaaS account hijack in which a compromised account authenticated from unusual IP addresses, created a new privileged account and subsequently sent a high volume of suspected malicious email. An administrative account later authenticated from rare endpoints.

GTA VI gives criminals an audience

Grand Theft Auto VI arrives on November 19 with the kind of attention few entertainment releases command [1]. Before launch, that interest is already being exploited by sites offering supposed demos and downloads.

During September and October 2026, Darktrace detected devices across multiple customer environments connecting to GTA VI-themed sites associated with suspicious activity. The organizations involved were spread across EMEA and the Americas and included Manufacturing, Finance, and Public administration and defense sectors.

Darktrace has also investigated multiple incidents affecting gaming organizations including ransomware and a SaaS account hijack. Those investigations show a separate side of the threat: attackers operating inside corporate infrastructure and accounts, sometimes well before the eventual impact becomes apparent.

Following a fake GTA VI download

On October 7, 2026, Darktrace detected a device making suspicious DNS requests for gta6-play[.]ru, an unofficial Russian-language GTA VI site that had also been flagged as likely malicious in open-source intelligence (OSINT).

‍

Figure 1: A screenshot of the suspicious endpoint gta6-play[.]ru .

‍

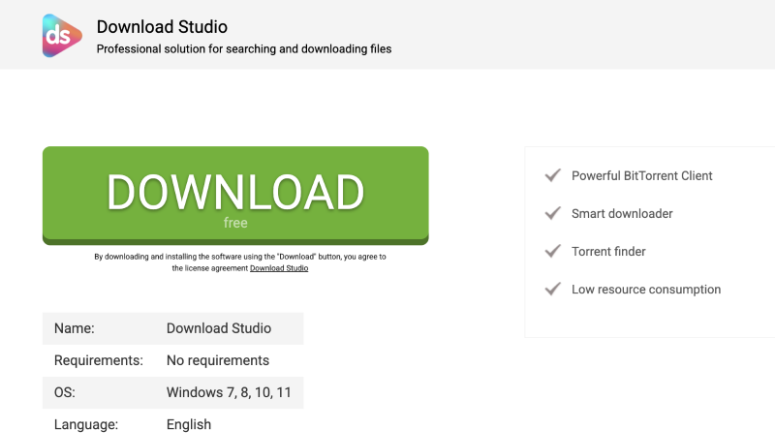
Figure 2: A screenshot of a “Download Studio” endpoint led to on gta6-play[.]ru.

‍

The site advertised a GTA VI download. The site led to a separate “Download Studio” page offering a Windows executable. Analysis found the file was packaged using InstallMate, a commercial installation framework, with an embedded .tsuarch section containing a compressed tiz3 archive.


Further examination identified functionality designed to inspect the environment in which the installer was running. This included checking registry entries for installed software and disk devices, enumerating network adapters, inspecting MAC addresses, and searching for running processes and window titles.


The installer also searched for processes associated with virtualization, debugging, and network analysis, including VMware and VirtualBox components, alongside debugging and monitoring utilities such as OllyDbg, WinDbg, Process Hacker, Process Monitor, Wireshark and Fiddler.

The presence of those checks did not prove that the executable was malicious. The installer contained functionality capable of extracting embedded files, but the investigation did not establish that it was being used to deploy a malicious payload. No definitive malicious payload or command-and-control infrastructure was identified. The software appeared to be InstallRex, which is classified by several security vendors as a potentially unwanted program.

That is still a useful finding; A user looking for GTA VI content could move from an unofficial gaming site to an executable that inspected the local environment, including checking for software commonly used by security researchers.

A second GTA VI lure appeared across twelve organizations

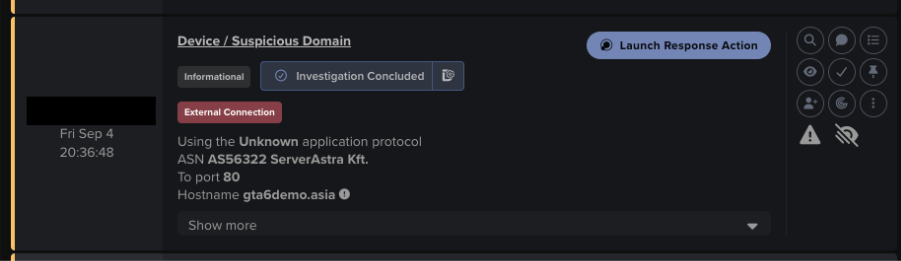
During September 2026, Darktrace alerted on HTTP connections to gta6demo[.]asia across twelve customer environments. Seven of the twelve communicated with infrastructure associated with AS56322 ServerAstra Kft as part of this connectivity.

‍

Figure 3: An example model alert generated due to a suspicious connection to gta6demo[.]asia.

‍

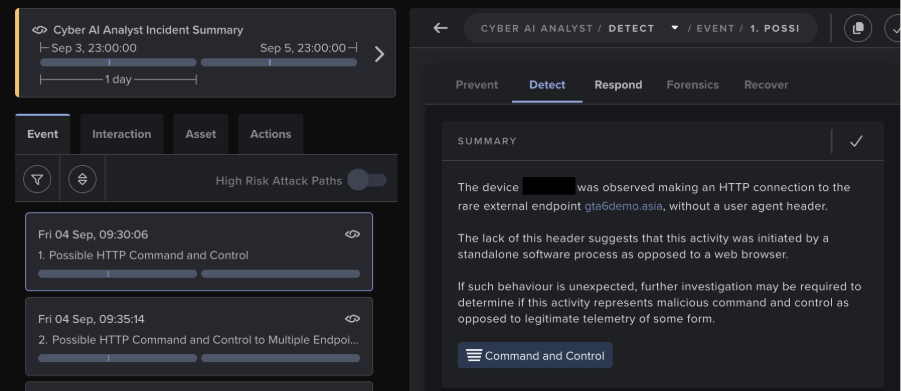
In a case affecting a UK-based customer, Darktrace’s Real-Time AI Analyst further investigated connections to gta6demo[.]asia and generated an incident due to the highly suspicious nature of the behavior.

‍

Figure 4: A Real-Time AI Analyst incident highlighting the suspicious activity for further investigation

‍

Public threat research has associated gta6demo[.]asia with a campaign advertising a fake GTA VI demo. Users clicking "Play Now" were reportedly directed towards an executable containing the Vidar infostealer [2].

There is a practical difference between this activity and an attack against a games company. The users encountering GTA VI-themed infrastructure can work anywhere. Darktrace saw the activity across several sectors outside Gaming, including Finance, Manufacturing, and Public administration and defense.

A major game release can therefore create security exposure well beyond its publisher. A search for a demo or unofficial download on a corporate device is enough to bring gaming-themed infrastructure into an enterprise environment.

Ransomware operators inside the gaming industry

The attacks Darktrace observed against Gaming companies themselves show different patterns.

In August 2026, Darktrace threat research identified possible malicious activity at a European game developer. Ransomware was ultimately deployed and data was exfiltrated, with the DireWolf ransomware group claiming responsibility.

Darktrace observed suspicious file downloads and beaconing from several devices to rare endpoints alongside Monero cryptocurrency mining, Active Directory and network reconnaissance, unusual administrative RDP connections, activity associated with data staging and HTTP-based exfiltration.

Much of the intrusion was therefore visible before ransomware appeared; the environment was already showing evidence of ingress tooling, external command-and-control communications (C2), reconnaissance, unusual administrative access and data movement.

A separate investigation in December 2025 provides a closer view of this pre-ransomware activity. A European games company was targeted by Qilin ransomware with Darktrace observing scanning and LDAP searches involving userAccountControl, which can expose information useful for identifying accounts and Service Principal Names within Active Directory.

New administrative credentials then appeared on a Domain Controller and the Domain Controller also generated scanning, anomalous RPC, SMB, and SSH activity, and NetShareEnum activity through srvsvc. Elsewhere in the environment, long Remote Desktop sessions and SMB enumeration appeared consistent with lateral movement.

Several devices also transferred data to cloud storage services including WebDrive and Amazon Web Services (AWS). In some cases, large downloads preceded subsequent uploads. Darktrace observed the transfer pattern, although the available telemetry does not establish that every transfer represented attacker-controlled exfiltration.

The activity preceding the Qilin deployment included Active Directory reconnaissance, privileged credential use, network and share enumeration, unusual remote access and significant data movement. Each appeared before ransomware became the defining feature of the incident.

SaaS hijacking shifts the attacker evidence

A separate investigation in May 2026 involved the hijacking of a SaaS account at a Gaming organization.

The compromised account authenticated from several IP addresses that were unusual for the organization. It then performed suspicious SaaS group administration, including creating a new privileged account. The account subsequently sent a high volume of emails assessed as likely malicious spam and potentially intended to compromise additional users.

The following day, an administrative SaaS account authenticated from rare endpoints, raising the possibility that further privileged access had been obtained.

The activity presented a different detection problem from the ransomware cases. Authentication from rare infrastructure, administrative changes, creation of a privileged account and subsequent email activity provided the strongest indications that a legitimate identity had been compromised.

For a Gaming company using hosted platforms for development, communication and business operations, a compromised account with the right permissions can provide considerable access without requiring the attacker to reproduce a conventional network intrusion.

Detecting the intrusion before impact

The ransomware investigations show why encryption should not be the first point at which an incident comes into focus. Darktrace observed LDAP and Active Directory-related reconnaissance, new privileged credentials, unusual Domain Controller activity, remote sessions, network enumeration and abnormal data movement before ransomware deployment.

The SaaS case produced different evidence: authentication from rare infrastructure, unexpected administrative changes and activity performed through a compromised account. GTA VI-themed activity required another approach again, following users through unofficial sites and redirects and examining the software offered for download.

GTA VI has put gaming back into the headlines ahead of its November release. The security activity around it is already visible beyond the games industry, while ransomware and account-compromise investigations show attackers operating inside gaming companies through very different routes.

For defenders, those routes leave evidence before the incident reaches its most damaging stage. The practical work is in recognizing those changes early enough to investigate them.

Credit to Gemma Stubberfield (Cyber Analyst), Ahmed Gardezi (Senior Cyber Analyst), Tara Gould (Malware Research Lead), Nathaniel Jones (SVP, Global Threat Intelligence)

References:

1.        https://www.rockstargames.com/VI

2.     https://www.malwarebytes.com/blog/threat-intel/2026/08/fake-gta-6-extended-look-and-demo-sites-deliver-an-infostealer

‍

Continue reading
About the author
Gemma Stubberfield
Cyber Analyst

Blog

/

AI

/

November 17, 2026

How Microsoft and Darktrace Secure the AI-Powered Enterprise

Default blog imageDefault blog image

When legitimate activity creates business risk

AI is making information more accessible and enabling autonomous agents to act across enterprise systems. But legitimate access can still result in sensitive-data exposure, unintended actions, or activity that deviates from business expectations.

Microsoft's evolving security strategy recognizes this shift, emphasizing continuous risk assessment, stronger identity protection, and security that adapts as AI systems operate. For enterprises, the challenge is increasingly about recognizing when trusted activity introduces risk, even when existing controls are functioning as intended.

Where global intelligence meets deep business context

Microsoft brings global threat intelligence and comprehensive security capabilities, helping organizations protect identities, data, applications, and infrastructure. Its integrated approach connects security signals, governance, detection, and response across increasingly complex environments.

Darktrace complements these strengths with deep, organization-specific behavioral understanding. Powered by Adaptive AI, Darktrace continuously learns the patterns and relationships unique to each business, developing a Unique Behavioral Profile for each organization that helps distinguish meaningful threats from legitimate activity. By connecting identity, activity, context, and intent, it adds another dimension to security intelligence.

Together, Microsoft and Darktrace combine global intelligence with deeper knowledge of how each customer operates. Through supported integrations, this behavioral context enriches existing Microsoft security workflows, enabling more informed investigations and precise response.

This complementary approach extends across three interconnected areas of enterprise security- AI, People and Infrastructure. From understanding how AI and agents operate to protecting trusted communications and the infrastructure businesses depend on, Darktrace strengthens Microsoft's security capabilities with behavioral insight specific to each organization.

Understanding AI beyond permissions and policies

As AI moves into business-critical operations, security teams need to understand more than which applications and agents are approved. They need visibility into how AI is used, what information it accesses, and whether its actions remain aligned with business intent.

Microsoft provides extensive AI development, governance, and security capabilities. Darktrace / SECURE AI complements these with behavioral analysis across Shadow AI, prompts, agent identities and actions, and development risk. Policy Manager helps evaluate activity against organizational AI policies, while the announced integration with Microsoft Agent 365 is designed to enrich agent risk assessments with organization-specific behavioral signals. Together, these capabilities help organizations scale AI adoption with greater confidence.

Recognizing risk within trusted relationships

Sophisticated threats increasingly exploit established business relationships, familiar communications, and legitimate accounts. A message from a trusted supplier or an action taken through an authorized identity may appear routine until considered against the organization's normal behavior.

Darktrace / EMAIL complements Microsoft's native email, identity, and data protection capabilities by understanding how people and organizations communicate. This enables more precise detection of targeted phishing, business email compromise, account takeover, and data loss, supported by proportionate response. Integrations such as Unified Quarantine within Microsoft Defender for Office 365 bring this additional protection into existing security workflows.

Seeing the bigger picture behind an attack across domains

Threats rarely unfold within a single security domain. Suspicious identity activity, unexpected cloud connections, and unusual network behavior may appear unrelated until the relationships between them reveal a developing attack.

Darktrace / HYBRID NETWORK complements Microsoft's security capabilities with organization-specific behavioral detection across network, cloud, identity, and operational technology. Real-Time AI Analyst, including Cyber AI Analyst, connects related activity into investigated incidents that can be delivered into Microsoft Sentinel, helping security teams accelerate investigations and support targeted containment across the hybrid enterprise.

Turning security intelligence into business confidence

As AI becomes more deeply integrated into business operations, organizations need security that understands not only what technology can access, but how it behaves within their unique environment.

Microsoft and Darktrace bring complementary strengths to that challenge. By connecting global threat intelligence and integrated security capabilities with deep behavioral understanding, the partnership helps organizations recognize emerging risks, respond with greater precision, and strengthen their existing security investments.

The opportunity is to turn security intelligence into meaningful business context, enabling organizations to innovate and operate AI with confidence.

Darktrace named a 2026 Microsoft Partner of the Year Finalist for ISV Innovation

Darktrace has been named a finalist for the 2026 Microsoft Partner of the Year Award in the ISV Innovation category.  

This recognition reflects our collaboration with Microsoft to bring business context to enterprise security. By connecting Microsoft's global threat intelligence and integrated security capabilities with Darktrace's deep behavioral understanding, we help organizations recognize emerging risks and respond with greater precision across AI, People and Infrastructure.

Thank you to Microsoft, our customers, and our teams for their continued collaboration.

Meet Darktrace at Microsoft Ignite and the Microsoft Frontier Tour

Explore how Darktrace and Microsoft are bringing behavioral security to AI, people, and infrastructure.

Join Darktrace at Microsoft Ignite in San Francisco, November 17–19, or connect with our experts as we join the Microsoft Frontier Tour across 21 cities worldwide.

Meet Darktrace at Microsoft Ignite

Connect with Darktrace at the Microsoft Frontier Tour

[related-resource]

Continue reading
About the author
Your data. Our AI.
Elevate your network security with Darktrace AI