ブログ
/
Network
/
September 13, 2023

How Darktrace Stopped Akira Ransomware

Learn how Darktrace is uniquely placed to identify and contain the novel Akira ransomware strain, first observed in March 2023.
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Manoel Kadja
Cyber Analyst
Default blog image
13
Sep 2023

Introduction to Akira Ransomware

In the face of a seemingly never-ending production line of novel ransomware strains, security teams across the threat landscape are continuing to see a myriad of new variants and groups targeting their networks. Naturally, new strains and threat groups present unique challenges to organizations. The use of previously unseen tactics, techniques, and procedures (TTPs) means that threat actors can often completely bypass traditional rule and signature-based security solutions, thus rendering an organization’s digital environment vulnerable to attack.

What is Akira Ransomware?

One such example of a novel ransomware family is Akira, which was first observed in the wild in March 2023. Much like many other strains, Akira is known to target corporate networks worldwide, encrypting sensitive files and demanding huge sums of money to retrieve the data and stop it from being posted online [1].

Key characteristics of Akira Ransomware

  • Targeted Attacks: Focuses on specific industries and organizations, often targeting those with valuable data.
  • Double Extortion Tactics: Employs double extortion by encrypting data and threatening to release it publicly if the ransom is not paid.
  • Advanced Encryption: Utilizes sophisticated encryption algorithms to ensure that data recovery is impossible without the decryption key.
  • Custom Ransom Notes: Delivers personalized ransom notes tailored to the victim, often containing detailed instructions and specific payment demands.
  • Stealth Techniques: Uses advanced evasion techniques to avoid detection by security tools and to remain undetected for extended periods.
  • Fast Encryption Process: Known for its rapid encryption process, minimizing the time window for detection and response by the victim.
  • Frequent Updates: Regularly updates its malware to bypass the latest security defenses and to improve its effectiveness.
  • Professional Communication: Maintains professional and often polite communication with victims to facilitate ransom payments and decryption.

Darktrace AI capabilities detect Akira Ransomware

In late May 2023, Darktrace observed multiple instances of Akira ransomware affecting networks across its customer base. Thanks to its anomaly-based approach to threat detection, Darktrace successfully identified the novel ransomware attacks and provided full visibility over the cyber kill chain, from the initial compromise to the eventual file encryptions and ransom notes. In cases where Darktrace was enabled in autonomous response mode, these attacks were mitigated the early stages of the attack, thus minimizing any disruption or damage to customer networks.

Initial access and privileged escalation

Methods used by Akira ransomware for privileged escalation

The Akira ransomware group typically uses spear-phishing campaigns containing malicious downloads or links as their primary initial access vector; however, they have also been known to use Remote Desktop Protocol (RDP) brute-force attacks to access target networks [2].

While Darktrace did observe the early access activities that are detailed below, it is very likely that the actual initial intrusion happened prior to this, through targeted phishing attacks that fell outside of Darktrace’s purview. The first indicators of compromise (IoCs) that Darktrace observed on customer networks affected by Darktrace were typically unusual RDP sessions, and the use of compromised administrative credentials.

Darktrace detection of initial access and priviledged escalation

On one Darktrace customer’s network (customer A), Darktrace identified a highly privileged credential being used for the first time on an internal server on May 21, 2023. Around a week later, this server was observed establishing RDP connections with multiple internal destination devices via port 3389. Further investigation carried out by the customer revealed that this credential had indeed been compromised. On May 30, Darktrace detected another device scanning internal devices and repeatedly failing to authenticate via Kerberos.

As the customer had integrated Darktrace with Microsoft Defender, their security team received additional cyber threat intelligence from Microsoft which, coupled with the anomaly alerts provided by Darktrace, helped to further contextualize these anomalous events. One specific detail gleaned from this integration was that the anomalous scanning activity and failed authentication attempts were carried out using the compromised administrative credentials mentioned earlier.

By integrating Microsoft Defender with Darktrace, customers can efficiently close security gaps across their digital infrastructure. While Darktrace understands customer environments and provides valuable network-level insights, by integrating with Microsoft Defender, customers can further enrich these insights with endpoint-specific information and activity.

In another customer’s network (customer B), Darktrace detected a device, later observed writing a ransom note, receiving an unusual RDP connection from another internal device. The RDP cookie used during this activity was an administrative RDP cookie that appeared to have been compromised. This device was also observed making multiple connections to the domain, api.playanext[.]com, and using the user agent , AnyDesk/7.1.11, indicating the use of the AnyDesk remote desktop service.

Although this external domain does not appear directly related to Akira ransomware, open-source intelligence (OSINT) found associations with multiple malicious files, and it appeared to be associated with the AnyDesk user agent, AnyDesk/6.0.1 [3]. The connections to this endpoint likely represented the malicious use of AnyDesk to remotely control the customer’s device, rather than Akira command-and-control (C2) infrastructure or payloads. Alternatively, it could be indicative of a spoofing attempt in which the threat actor is attempting to masquerade as legitimate remote desktop service to remain undetected by security tools.

Around the same time, Darktrace observed many devices on customer B’s network making anomalous internal RDP connections and authenticating via Kerberos, NTLM, or SMB using the same administrative credential. These devices were later confirmed to be affected by Akira Ransomware.

Figure 1 shows how Darktrace detected one of those internal devices failing to login via SMB multiple times with a certain credential (indication of a possible SMB/NTLM brute force), before successfully accessing other internal devices via SMB, NTLM and RDP using the likely compromised administrative credential mentioned earlier.

Figure 1: Model Breach Event Log indicating unusual SMB, NTLM and RDP activity with different credentials detected which led to the Darktrace model breaches, "Unusual Admin RDP Session” and “Successful Admin Brute-Force Activity”.

Darktrace models observed for initial access and privilege escalation:

  • Device / Anomalous RDP Followed By Multiple Model Breaches
  • Anomalous Connection / Unusual Admin RDP Session
  • New Admin Credentials on Server
  • Possible SMB/NTLM Brute Force Indicator
  • Unusual Activity / Successful Admin Brute-Force Activity

Internal Reconnaissance and Lateral Movement

The next step Darktrace observed during Akira Ransomware attacks across the customer was internal reconnaissance and lateral movement.

How Akira Ransomware conducts internal reconnaissance

In another customer’s environment (customer C), after authenticating via NTLM using a compromised credential, a domain controller was observed accessing a large amount of SMB shares it had never previously accessed. Darktrace understood that this SMB activity represented a deviation in the device’s expected behavior and recognized that it could be indicative of SMB enumeration. Darktrace observed the device making at least 196 connections to 34 unique internal IPs via port 445. SMB actions read, write, and delete were observed during those connections. This domain controller was also one of many devices on the customer’s network that was received incoming connections from an external endpoint over port 3389 using the RDP protocol, indicating that the devices were likely being remotely controlled from outside the network. While there were no direct OSINT links with this endpoint and Akira ransomware, the domain controller in question was later confirmed to be compromised and played a key role in this phase of the attack.

Moreover, this represents the second IoC that Darktrace observed that had no obvious connection to Akira, likely indicating that Akira actors are establishing entirely new infrastructure to carry out their attacks, or even utilizing newly compromised legitimate infrastructure. As Darktrace adopts an anomaly-based approach to threat detection, it can recognize suspicious activity indicative of an emerging ransomware attack based on its unusualness, rather than having to rely on previously observed IoCs and lists of ‘known-bads’.

Darktrace further observed a flurry of activity related to lateral movement around this time, primarily via SMB writes of suspicious files to other internal destinations. One particular device on customer C’s network was detected transferring multiple executable (.exe) and script files to other internal devices via SMB.

Darktrace recognized that these transfers represented a deviation from the device’s normal SMB activity and may have indicated threat actors were attempting to compromise additional devices via the transfer of malicious software.

Figure 2: Advanced Search results showing 20 files associated with suspicious SMB write activity, amongst them executable files and dynamic link libraries (DLLs).

Darktrace DETECT models observed for internal reconnaissance and lateral movement:

  • Device / RDP Scan
  • Anomalous Connection / SMB Enumeration
  • Anomalous Connection / Possible Share Enumeration Activity
  • Scanning of Multiple Devices (Cyber AI Analyst Incident)
  • Device / Possible SMB/NTLM Reconnaissance
  • Compliance / Incoming Remote Desktop
  • Compliance / Outgoing NTLM Request from DC
  • Unusual Activity / Internal Data Transfer
  • Security Integration / Lateral Movement and Integration Detection
  • Device / Anomalous SMB Followed By Multiple Model Breaches

Ransomware deployment

In the final phase of Akira ransomware attacks detected on Darktrace customer networks, Darktrace identified the file extension “.akira” being added after encryption to a variety of files on the affected network shares, as well as a ransom note titled “akira_readme.txt” being dropped on affected devices.

On customer A’s network, after nearly 9,000 login failures and 2,000 internal connection attempts indicative of scanning activity, one device was detected transferring suspicious files over SMB to other internal devices. The device was then observed connecting to another internal device via SMB and continuing suspicious file activity, such as appending files on network shares with the “.akira” extension, and performing suspicious writes to SMB shares on other internal devices.

Darktrace’s autonomous threat investigator, Cyber AI Analyst™, was able to analyze the multiple events related to this encryption activity and collate them into one AI Analyst incident, presenting a detailed and comprehensive summary of the entire incident within 10 minutes of Darktrace’s initial detection. Rather than simply viewing individual breaches as standalone activity, AI Analyst can identify the individual steps of an ongoing attack to provide complete visibility over emerging compromises and their kill chains. Not only does this bolster the network’s defenses, but the autonomous investigations carried out by AI Analyst also help to save the security team’s time and resources in triaging and monitoring ongoing incidents.

Figure 3: Darktrace Cyber AI Analyst incident correlated multiple model breaches together to show Akira ransomware encryption activity.

In addition to analyzing and compiling Darktrace model breaches, AI Analyst also leveraged the host-level insights provided by Microsoft Defender to enrich its investigation into the encryption event. By using the Security Integration model breaches, AI Analyst can retrieve timestamp and device details from a Defender alert and further investigate any unusual activity surrounding the alert to present a full picture of the suspicious activity.

In customer B’s environment, following the unusual RDP sessions and rare external connections using the AnyDesk user agent, an affected device was later observed writing around 2,000 files named "akira_readme.txt" to multiple internal SMB shares. This represented the malicious actor dropping ransom notes, containing the demands and extortion attempts of the actors.

Figure 4: Model Breach Event Log indicating the ransom note detected on May 12, 2023, which led to the Darktrace DETECT model breach, Anomalous Server Activity / Write to Network Accessible WebRoot.
Figure 5: Packet Capture (PCAP) demonstrating the Akira ransom note captured from the connection details seen in Figure 4.

As a result of this ongoing activity, an Enhanced Monitoring model breach, a high-fidelity detection model type that detects activities that are more likely to be indicative of compromise, was escalated to Darktrace’s Security Operations Center (SOC) who, in turn were able to further investigate and triage this ransomware activity. Customers who have subscribed to Darktrace’s Proactive Threat Notification (PTN) service would receive an alert from the SOC team, advising urgent follow up action.

Darktrace detection models observed during ransomware deployment:

  • Security Integration / Integration Ransomware Incident
  • Security Integration / High Severity Integration Detection
  • Security Integration / Integration Ransomware Detected
  • Device / Suspicious File Writes to Multiple Hidden SMB Shares
  • Compliance / SMB Drive Write
  • Compromise / Ransomware / Suspicious SMB Activity (Proactive Threat Notification Alerted by the Darktrace SOC)
  • Anomalous File / Internal / Additional Extension Appended to SMB File
  • Anomalous File / Internal / Unusual SMB Script Write
  • Compromise / Ransomware / Ransom or Offensive Words Written to SMB
  • Anomalous Server Activity /Write to Network Accessible WebRoot
  • Anomalous Server Activity /Write to Network Accessible WebRoot

Darktrace autonomous response neutralizes Akira Ransomware

When Darktrace is configured in autonomous response mode, it is able to follow up successful threat identifications with instant autonomous actions that stop malicious actors in their tracks and prevent them from achieving their end goals.

In the examples of Darktrace customers affected by Akira Ransomware outlined above, only customer A had autonomous response mode enabled during their ransomware attack. The autonomous response capability of Darktrace helped the customer to minimize disruption to the business through multiple targeted actions on devices affected by ransomware.

One action carried out by Darktrace's Autonomous Respose was to block all on-going traffic from affected devices. In doing so, Darktrace effectively shuts down communications between devices affected by Akira and the malicious infrastructure used by threat actors, preventing the spread of data on the client network or threat actor payloads.

Another crucial response action applied on this customer’s network was combat Akira was to “Enforce a Pattern of Life” on affected devices. This action is designed to prevent devices from performing any activity that would constitute a deviation from their expected behavior, while allowing them to continue their ‘usual’ business operations without causing any disruption.

While the initial intrusion of the attack on customer A’s network likely fell outside of the scope of Darktrace’s visibility, Darktrace was able to minimize the disruption caused by Akira, containing the ransomware and allowing the customer to further investigate and remediate.

Darktrace Autonomous Response model breaches:

  • Antigena / Network / External Threat / Antigena Ransomware Block
  • Antigena / Network / External Threat / Antigena Suspicious Activity Block
  • Antigena / Network / Significant Anomaly / Antigena Enhanced Monitoring from Server Block
  • Antigena / Network / External Threat / Antigena Suspicious Activity Block
  • Antigena / Network / External Threat / Antigena File then New Outbound Block
  • Antigena / Network / Insider Threat / Antigena Unusual Privileged User Activities Block
  • Antigena / Network / Significant Anomaly / Antigena Breaches Over Time Block
  • Antigena / Network / Significant Anomaly / Antigena Significant Anomaly from Client Block
  • Antigena / Network /Insider Threat /Antigena SMB Enumeration Block

Conclusion

The impact of cyber attacks

Novel ransomware strains like Akira Ransomware present a significant challenge to security teams across the globe due to the constant evolution of attack methods and tactics, making it huge a challenge for security teams to stay up to date with the most current threat intelligence.  

Therefore, it is paramount for organizations to adopt a technology designed around an intelligent decision maker able to identify unusual activity that could be indicative of a ransomware attack without depending solely on rules, signatures, or statistic lists of malicious IoCs.

Importance of AI-powered cybersecurity solutions

Darktrace identified Akira ransomware at every stage of the attack’s kill chain on multiple customer networks, even when threat actors were utilizing seemingly legitimate services (or spoofed versions of them) to carry out malicious activity. While this may have gone unnoticed by traditional security tools, Darktrace’s anomaly-based detection enabled it to recognize malicious activity for what it was. When enabled in autonomous response mode, Darktrace is able to follow up initial detections with machine-speed preventative actions to stop the spread of ransomware and minimize the damage caused to customer networks.  

There is no silver bullet to defend against novel cyber-attacks, however Darktrace’s anomaly-based approach to threat detection and autonomous response capabilities are uniquely placed to detect and respond to cyber disruption without latency.

Credit to: Manoel Kadja, Cyber Analyst, Nahisha Nobregas, SOC Analyst.

Appendices

IOC - Type - Description/Confidence

202.175.136[.]197 - External destination IP -Incoming RDP Connection

api.playanext[.]com - External hostname - Possible RDP Host

.akira - File Extension - Akira Ransomware Extension

akira_readme.txt - Text File - Akira Ransom Note

AnyDesk/7.1.11 - User Agent -AnyDesk User Agent

MITRE ATT&CK Mapping

Tactic & Technique

DISCOVERY

T1083 - File and Directory Discovery

T1046 - Network Service Scanning

T1135 - Network Share Discovery

‍

RECONNAISSANCE

T1595.002 - Vulnerability Scanning

‍

CREDENTIAL ACCESS, COLLECTION

T1557.001 - LLMNR/NBT-NS Poisoning and SMB Relay

‍

DEFENSE EVASION, LATERAL MOVEMENT

T1550.002 - Pass the Hash

‍

DEFENSE EVASION, PERSISTENCE, PRIVILEGE ESCALATION, INITIAL ACCESS

T1078 - Valid Accounts

‍

DEFENSE EVASION

T1006 - Direct Volume Access

‍

LATERAL MOVEMENT

T1563.002 - RDP Hijacking

T1021.001 - Remote Desktop Protocol

T1080 - Taint Shared Content

T1021.002 - SMB/Windows Admin Shares

‍

INITIAL ACCESS

T1190 - Exploit Public-Facing Application

T1199 - Trusted Relationship

‍

PERSISTENCE, INITIAL ACCESS

T1133 - External Remote Services

‍

PERSISTENCE

T1505.003 - Web Shell

‍

IMPACT

T1486 - Data Encrypted for Impact

References

[1] https://www.bleepingcomputer.com/news/security/meet-akira-a-new-ransomware-operation-targeting-the-enterprise/

[2] https://www.civilsdaily.com/news/cert-in-warns-against-akira-ransomware/#:~:text=Spread%20Methods%3A%20Akira%20ransomware%20is,Desktop%20connections%20to%20infiltrate%20systems

[3] https://hybrid-analysis.com/sample/0ee9baef94c80647eed30fa463447f000ec1f50a49eecfb71df277a2ca1fe4db?environmentId=100

Get the latest insights on emerging cyber threats

This report explores the latest trends shaping the cybersecurity landscape and what defenders need to know in 2026.
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Manoel Kadja
Cyber Analyst

More in this series

No items found.

Blog

/

AI

/

October 22, 2026

Vulnerability Discovery to Active Attacks: AI in Cyber Operations

Default blog imageDefault blog image

The disclosure of CVE-2026-109618 and CVE-2026-109619 placed immediate pressure on organizations running PHP. Both vulnerabilities can allow unauthenticated remote code execution, including in products and appliances where PHP is embedded, and updates depend on third-party vendors [1].

Early guidance focused on patching internet-facing systems and monitoring for behavior associated with successful exploitation, including unexpected command execution, Webroot changes and outbound connections from PHP servers.

Darktrace observed widespread scanning across monitored environments involving hundreds of distinct source IP addresses that public reporting has associated with activity targeting the PHP vulnerabilities. The volume of scanning was significantly greater than the evidence available for successful exploitation. For analysts, that distinction is important. Scanning demonstrates interest in exposed infrastructure; establishing compromise requires evidence of subsequent behavior on the targeted system, including command execution, file modification or unexpected outbound communication.

While Darktrace has not observed direct evidence of CVE-2026-109618 or CVE-2026-109619 exploitation, on October 21st we observed a six-month high in detections consistent with zero-day exploitation activity, representing a 64% increase compared to historic data. This increase has not been confirmed as related to the PHP vulnerabilities. Darktrace’s behavioral approach is designed to detect anomalous activity without relying solely on rules written for a specific exploit. Comparable increases were observed around the Log4j disclosure and other globally significant vulnerability disclosures.

AI-assisted vulnerability research

The PHP disclosure arrives as AI systems have become more capable at vulnerability research [2]. OpenAI launched Daybreak in June 2026, combining GPT-5.5-Cyber, Codex Security and partnerships with security researchers and software maintainers. OpenAI says its models have been applied to discovering and generating patches for vulnerabilities in browsers, network infrastructure, FreeBSD and the Linux kernel. Darktrace joined the OpenAI Daybreak Cyber Partner Program in June to explore how OpenAI's cyber capabilities could be integrated within Darktrace products and services [3][9].

OpenAI reported in August that Codex Security Cloud had analyzed more than 30 million commits across more than 30,000 codebases. According to OpenAI, Cloudflare uses models accessed through Daybreak to investigate customer-authorized code and combines findings with live traffic and security signals to assess whether affected routes are active or receiving suspicious traffic, with proposed mitigations and patches remaining subject to customer review [4][5].

Faster discovery still leaves defenders with the work of locating affected software, testing fixes and completing remediation. The PHP case shows that gap clearly, particularly when vulnerable runtimes are embedded inside other products.

Enterprise agents as an attack surface

Darktrace Signal Labs has also examined how a trusted enterprise agent could be abused after an attacker has already obtained access to an environment. In a controlled simulation, researchers demonstrated that, in that post-compromise scenario, the Claude platform’s memory stores feature could be abused to establish a live C2 channel between an external operator and internal Claude Code agents. The external operator was able to dynamically assign network discovery, credential access, and data exfiltration tasks to the agents via this C2 channel. Detection of the agents’ activities relied on the correlation of process creation and network traffic activity from agent harness processes, alongside behavioral analysis to identify deviations from expected behavior. Darktrace has not claimed it observed this memory-store command-and-control technique in operational attacks [6].

AI-assisted attacks in Japan

Evidence from Japan indicates AI being used for vulnerability scanning and attacks outside controlled research. On 21 October, JPCERT/CC published findings from an investigation into recent unauthorized access incidents affecting organizations in Japan. JPCERT/CC states that it confirmed attackers had used AI to scan for known vulnerabilities and conduct attacks through APIs. According to JPCERT/CC, its examination of attack infrastructure found evidence of Android application analysis, API discovery and testing for weaknesses including server-side request forgery, and the infrastructure also targeted services intended for users outside Japan [7].

JPCERT/CC does not identify ARTEX by name in that publication. The named ARTEX attribution comes from separate investigations, including Microsoft's analysis of Storm-0940.

AI in Offensive Operations

Microsoft describes ARTEX as an open-source, multi-agent penetration-testing system capable of automating activity with limited human interaction. Microsoft reported that Storm-0940, which it assesses to be a China state-aligned actor active since 2021, used ARTEX against hundreds of organizations, and Microsoft attributed the ConnectWise supply-chain compromise [8].

Microsoft observed ARTEX accelerating scanning, reconnaissance, password spraying and OAuth application abuse. Several ARTEX-driven operations reached privileged cloud access less than three hours after initial targeting. Following the ConnectWise compromise, Storm-0940 attempted to authenticate to more than 2,250 tenants at rates of up to 2,900 attempts per minute [8].

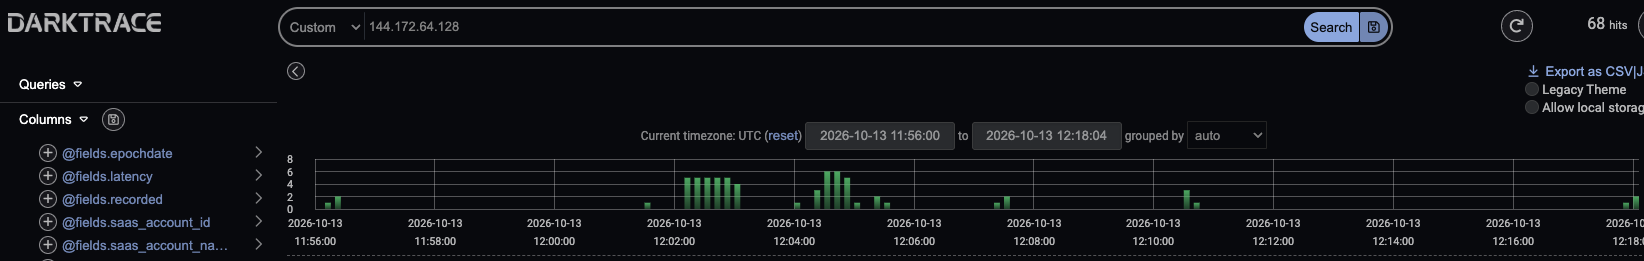
Darktrace Threat Research found activity in its own telemetry involving infrastructure later associated with the campaign. On 13 October, Darktrace recorded failed authentication activity involving 144.172.64[.]128, one of the addresses Microsoft later identified as performing sign-ins and Microsoft Graph activity in ConnectWise customer environments. Darktrace analysis identified 65 failed authentication attempts in around 20 minutes.

Figure 1: Darktrace Advanced Search showing failed authentication events involving 144.172.64[.]128 on 13 October 2026, (customer-identifying information redacted).

The telemetry establishes repeated failed authentication from infrastructure later associated with the campaign. It does not establish ARTEX execution or successful compromise. At the time of observation, Microsoft's later attribution was unavailable. Analysts therefore had the behavior itself: repeated failed authentication from the same source over a short period, together with any related identity, application or network activity inside the environment.

Microsoft documented a wider password-spray campaign against 327 accounts across eight organizations between 10 and 14 October. It recorded more than 151,000 failed logons, including more than 111,000 on 11 October, but no successful authentication, token issuance, Graph call or directory change from that campaign. Microsoft also reported that most Storm-0940 targeting was unsuccessful [8].

Where the actor progressed beyond authentication, Microsoft observed service-principal sign-ins followed by Graph and directory operations. Activity included reconnaissance, application credential changes and attempts to modify privileges. Microsoft recommends correlating service-principal sign-ins with Graph activity, directory changes and resource access [8].

Behavior before Attribution

The PHP and ARTEX cases begin with different information. PHP defenders knew which software required urgent remediation but initially had limited information about exploitation. Process execution, file modification and outbound communication could still provide evidence of compromise.

The PHP and ARTEX observations also illustrate the difference between volume and impact. Darktrace observed broad scanning around the PHP disclosure, while the ARTEX-associated infrastructure produced concentrated authentication activity. Neither observation independently demonstrates compromise and in each case examining the behavior that follows the initial interaction is the investigative clue.

The Darktrace ARTEX-related observation began with authentication behavior. Microsoft publicly attributed the source infrastructure eight days later. That attribution added context, but it did not change what had originally been recorded in the environment.

AI is now present at several points in this cycle. Daybreak applies models to vulnerability discovery and remediation. Darktrace Signal Labs demonstrated how a trusted enterprise agent could be co-opted in a controlled environment. JPCERT/CC confirmed AI-assisted vulnerability scanning and API attacks in recent incidents. Microsoft documented ARTEX being used by Storm-0940 in active operations [3][6][7][8].

Microsoft's findings also show why scale and impact must be assessed separately. One ARTEX-associated campaign produced more than 151,000 failed logons without successful access, while other operations reached privileged cloud access in less than three hours. Security teams have to distinguish high-volume attempts from activity that progresses through authentication, privilege changes and resource access.

The evidence required to assess these cases remains familiar: authentication records, process execution, application and directory changes, file activity and network communication. AI can increase the rate at which those behaviors occur. Defenders still need to establish their sequence and impact.

Credit to Emma Foulger, Sam Lister, Dylan Evans, Moishe Tajtelbaum

References

[1] NCSC-NL, php2shell vulnerabilities (CVE-2026-109618, CVE-2026-109619), 21 October 2026. https://github.com/NCSC-NL/php2shell

[2] Cyber Security Agency of Singapore, https://www.csa.gov.sg/alerts-and-advisories/alerts/al-2026-151/

[3] OpenAI, Daybreak: Tools for securing every organization in the world, 22 June 2026. https://openai.com/index/daybreak-securing-the-world/

[4] OpenAI Developers, Scaling cyber defenders with Daybreak, 21 August 2026. https://developers.openai.com/blog/scaling-cyber-defenders-with-daybreak

[5] OpenAI, Cloudflare links vulnerability discovery to defense with OpenAI, 21 October 2026. https://openai.com/index/cloudflare-cyber/

[6] Darktrace Signal Labs, Shared Memories as a Covert C2 Channel, draft research supplied for review.

[7] JPCERT/CC, Recent AI-Assisted Cyber Attacks in Japan: Investigating Attack Infrastructure and Techniques, 21 October 2026. https://blogs.jpcert.or.jp/en/2026/10/web_api_attacks.html

[8] Microsoft Security Research and Microsoft Threat Intelligence, AI-driven, large-scale nation-state campaign using ARTEX enables supply chain compromise, 21 October 2026. https://www.microsoft.com/en-us/security/blog/2026/10/21/storm-0940-uses-artex-agentic-ai-connectwise-supply-chain-compromise/

[9] Darktrace, Advancing the Use of Frontier AI in Cybersecurity: Darktrace Joins the OpenAI Daybreak Cyber Partner Program to Explore Defensive AI Integrations, 22 June 2026. https://www.darktrace.com/blog/advancing-the-use-of-frontier-ai-in-cybersecurity-darktrace-joins-the-openai-daybreak-cyber-partner-program-to-explore-defensive-ai-integrations

Continue reading
About the author

Blog

/

OT

/

October 21, 2026

Beyond the Fridge: Exposed Industrial Control Systems

Default blog imageDefault blog image

Introduction

In October 2026, hundreds of supermarkets across France were reportedly affected by a cyberattack targeting their refrigeration systems. According to public reports, the attackers gained access to internet-connected controllers and modified their settings, forcing refrigeration units into high and extremely low temperatures and causing significant disruption. Total losses have been reported to reach several million euros.

The incident drew attention to the security of industrial refrigeration systems, particularly older devices with exposed management interfaces and known vulnerabilities.

The exact details of how the attackers gained access have not been confirmed, however it is speculated that the public-facing web server could be accessed with the username “admin” and password being the current date. Researchers from Claroty’s Team82 identified a vulnerability in Danfoss AK-SM 8xxA Series in 2025, “CVE-2025-41450", allowing for administrative access using a time-based “code-of-the-day" for authentication [1].

Default credentials, outdated firmware and publicly accessible administrative interfaces have been an issue for years. And yet these systems continue to appear in internet scans and require little sophistication to gain admin access. A simple search of internet-connected devices shows a range of exposed devices from Programmable Logic Controllers (PLCs) and remote gateways, to, yes, more fridges.

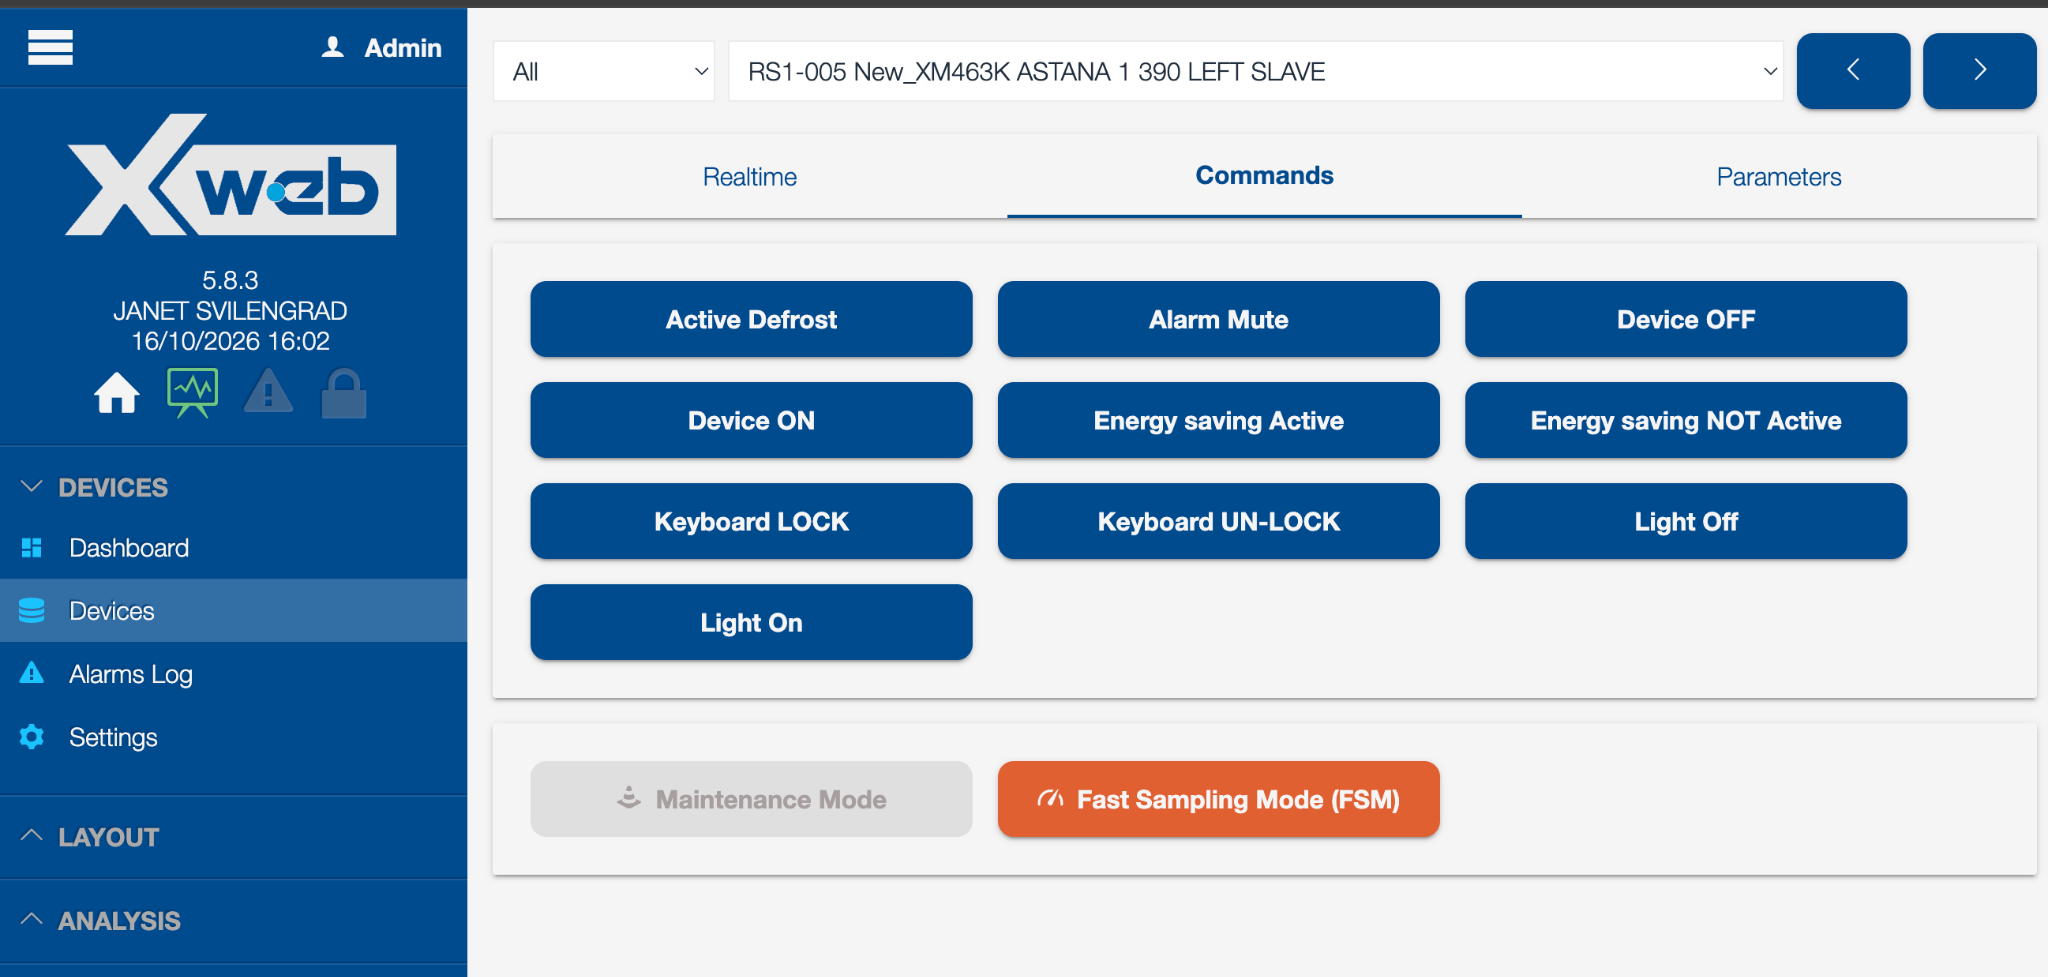
Darktrace malware researchers identified hundreds of IoT and OT devices publicly exposed on the internet, many of which are configured with no authentication, weak credentials, or default credentials. As shown in Figure 1, an exposed Copeland XWEB web interface, used to manage Dixell equipment, including refrigerators, can provide the ability to remotely control connected devices.

‍

Figure 1: Copeland XWEB interface used to control systems including refrigerators and air conditioning.

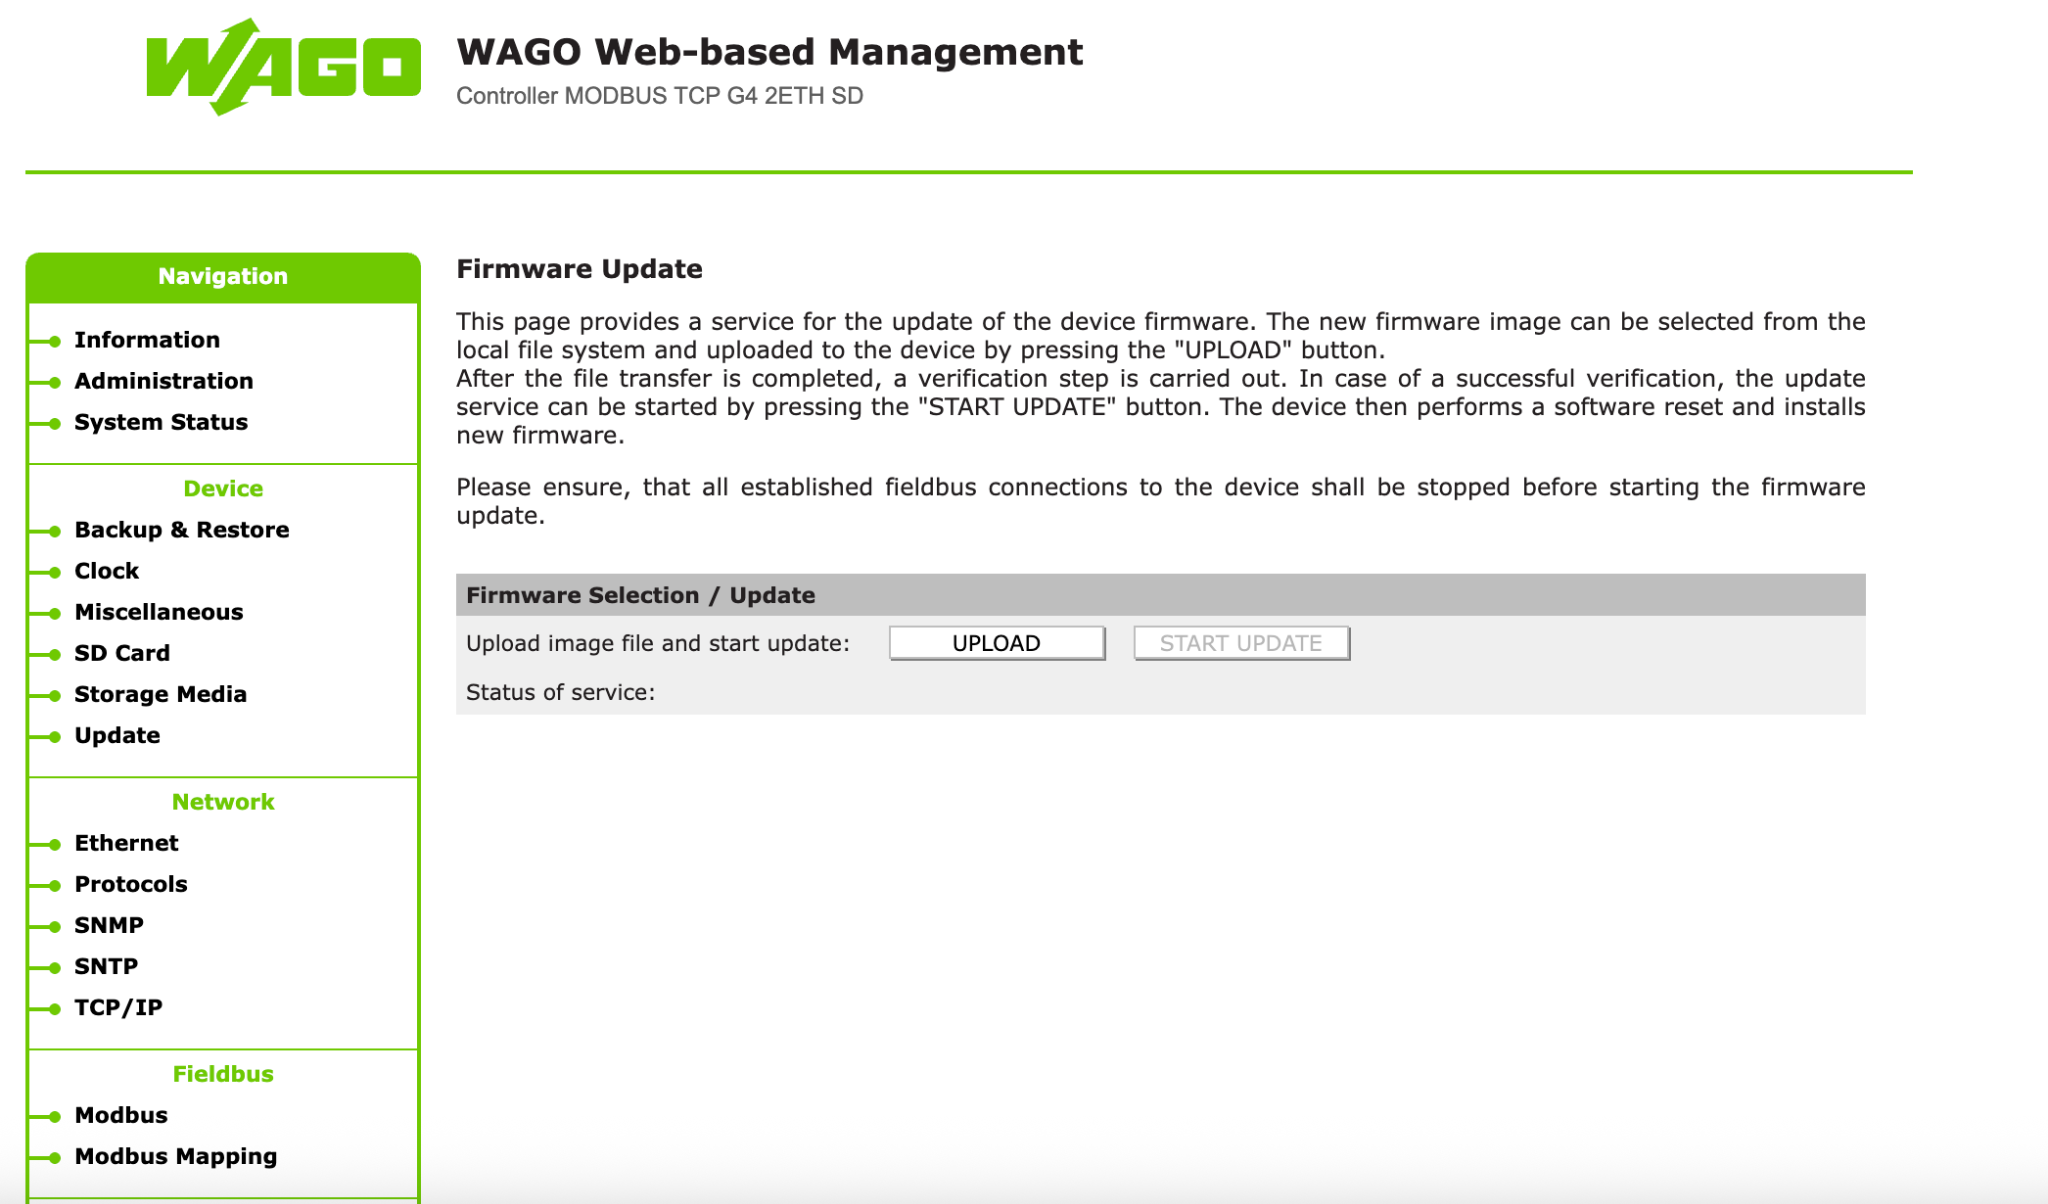
However, it’s not only fridges; web management interfaces for industrial controls are also publicly accessible, often protected only by weak credentials. Figure 2 shows an example of a publicly exposed WAGO interface. The WAGO management interface is a configuration and administration panel for controllers. Through it, a logged-in user can view device details and diagnostics, manage user accounts and passwords, update firmware, back up or restore the full configuration, set the clock, and manage SD card storage. While it typically doesn’t manage switch outputs or read live process values, someone with access could still disrupt operation by changing network or Modbus settings, loading bad firmware or configurations, or by resetting passwords and enabling insecure services.

‍

Figure 2: WAGO Management interface.

‍

The issue extends beyond management interfaces. During our research, we identified publicly accessible web interfaces belonging to PLCs, including Rockwell Automation Allen-Bradley devices. In each case, the risk arises from how the devices have been deployed and configured, not from a flaw in the vendors’ products.

‍

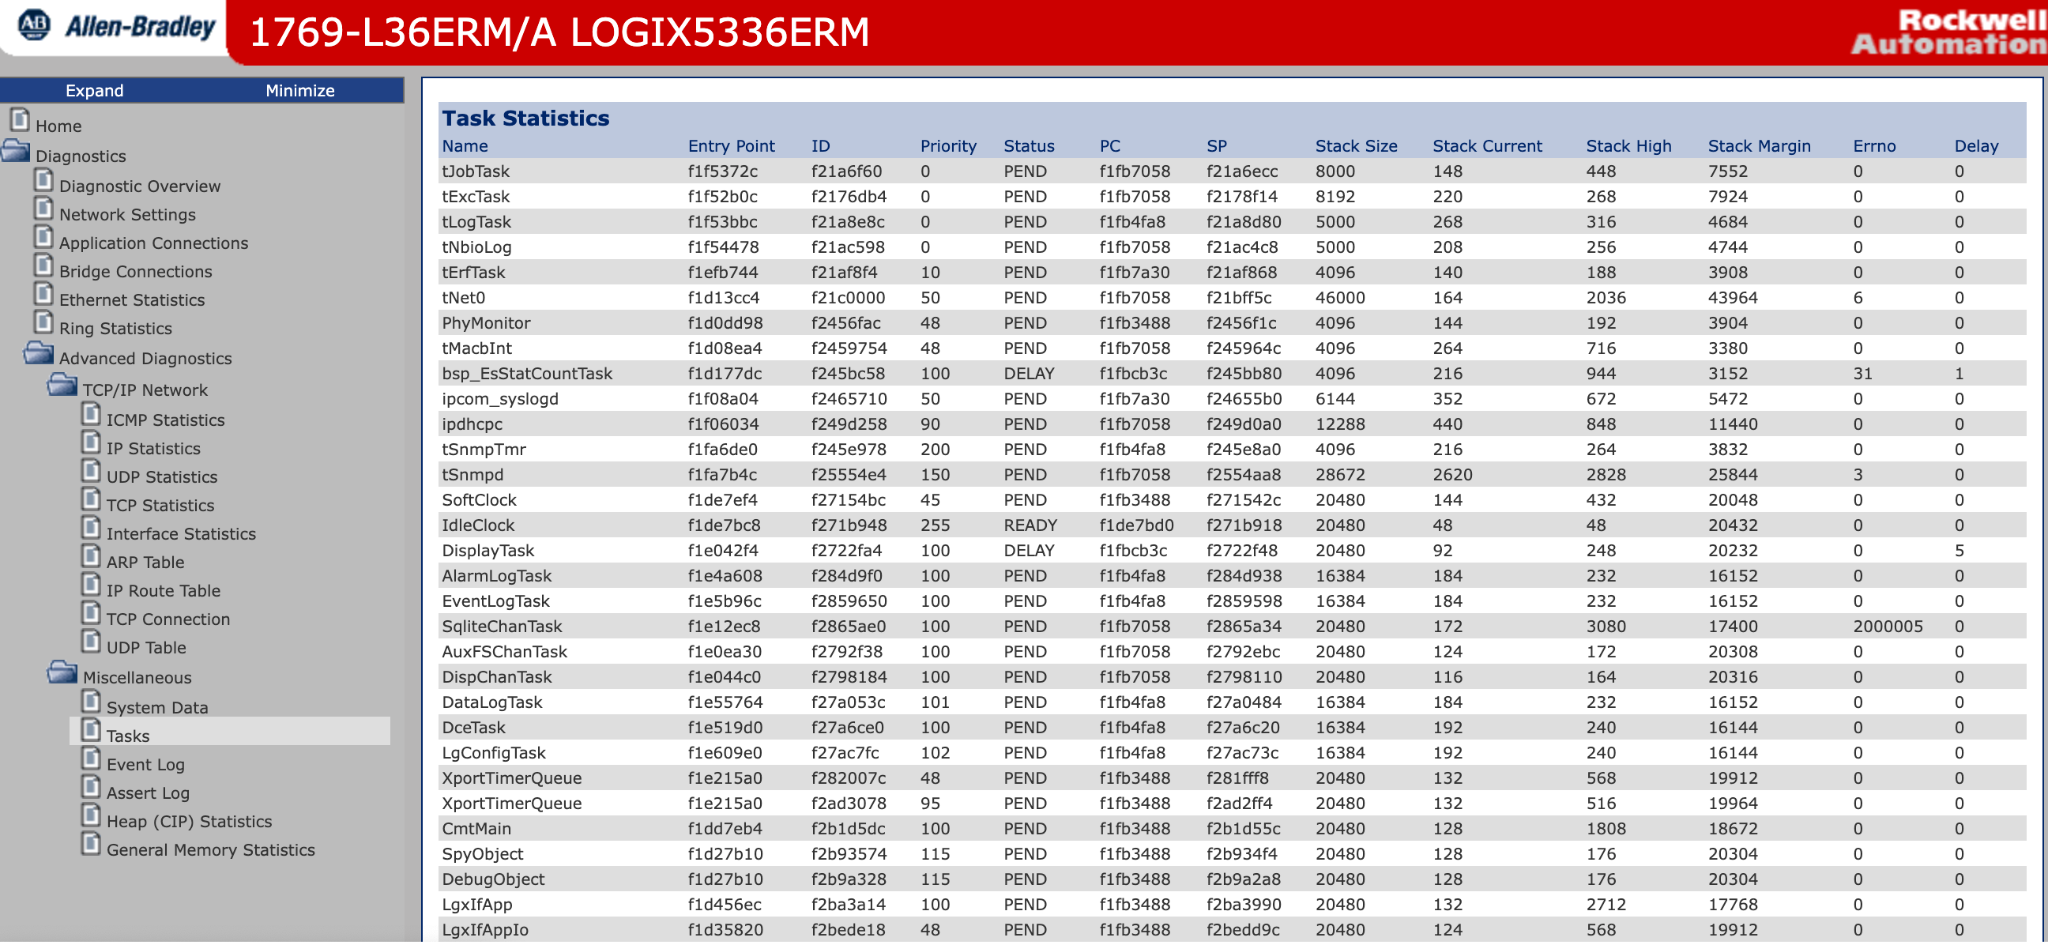
Figure 3: Web interface for Allen-Bradley CompactLogix controller.

‍

Figure 3 shows the web interface of an Allen-Bradley CompactLogix controller. Unlike the previous examples, this interface provides a view into the controller's operation, including running tasks, network connections, memory usage and diagnostic information. Rockwell Automation's CompactLogix controllers are commonly used to automate industrial processes, from manufacturing and packaging lines to water treatment and material handling systems. Depending on their configuration, these controllers can operate motors, pumps, valves and other physical equipment.

Although in this example the interface shown does not provide direct control over the PLC's logic, it exposes information about the model, firmware, network layout, and connections, which is useful reconnaissance for a bigger attack.

The concern is not necessarily that every exposed interface allows an attacker to immediately manipulate industrial processes. However, these devices are accessible from the public internet in the first place, providing information about systems that may be responsible for controlling physical equipment.

The attacks on refrigeration systems in France highlight the consequences of poorly secured industrial devices. As demonstrated throughout this research, publicly accessible management interfaces are not limited to refrigeration controllers but extend to PLCs and other systems used to manage industrial equipment.

Finding these devices requires little effort. Internet scanners make it possible to identify publicly exposed interfaces quickly, and in some cases these interfaces rely on publicly documented default credentials or have no authentication at all. As attackers increasingly use AI tools, such attacks may be identified and carried out faster and at a greater scale.

The consequences of this access depend on the device and the functionality exposed. While some interfaces provide little more than diagnostic information, others allow users to modify configurations, disrupt communications, or change settings that affect physical equipment. In industrial environments, this can result in operational downtime, damaged equipment and financial losses.

Weak passwords, default credentials and exposed administrative interfaces are not new security issues. Yet their continued presence on internet-connected industrial systems demonstrates how easily preventable weaknesses can leave physical operations vulnerable to attack.

Exposed devices often come from third-party suppliers and contractors, who frequently install refrigeration controllers, gateways and PLCs without the organization ever being aware they are connected to the internet. Asset visibility remains an important foundation, but organizations should assume that some unknown assets and services will exist. Effective security therefore also depends on continuous monitoring, anomaly detection, network segmentation and rapid response, so that risky exposure and unusual activity can be identified and addressed before it becomes disruptive.

Darktrace helps security teams gain visibility across IT and OT and respond to risks: https://www.darktrace.com/products/operational-technology.

Copeland, Dixell, WAGO, Rockwell Automation, Allen-Bradley and CompactLogix are trademarks of their respective owners. Their use here is for identification only and does not imply any affiliation with or endorsement by those owners.

References

1.        https://claroty.com/team82/research/freeze-the-controller-defrost-the-food-uncovering-vulnerabilities-in-danfoss-refrigeration-controllers

‍

Continue reading
About the author
Tara Gould
Malware Research Lead
あなたのデータ × DarktraceのAI
唯一無二のDarktrace AIで、ネットワークセキュリティを次の次元へ