ブログ
/
Network
/
June 3, 2024

The Price of Admission: Countering Stolen Credentials with Darktrace

This blog examines a network compromise that stemmed from the purchase of leaked credentials from the dark web. Credentials purchased from dark web marketplaces allow unauthorized access to internal systems. Such access can be used to exfiltrate data, disrupt operations, or deploy malware.
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Charlotte Thompson
Cyber Analyst
Default blog image
03
Jun 2024

Using leaked credentials to gain unauthorized access

Dark web marketplaces selling sensitive data have increased accessibility for malicious actors, similar to Ransomware-as-a-Service (RaaS), lowering the barrier to entry usually associated with malicious activity. By utilizing leaked credentials, malicious actors can easily gain unauthorized access to accounts and systems which they can leverage to carry out malicious activities like data exfiltration or malware deployment.

Usage of leaked credentials by malicious actors is a persistent concern for both organizations and security providers. Google Cloud’s ‘H1 2024 Threat Horizons Report’ details that initial access seen in 2.9% of cloud compromises observed on Google Cloud resulted from leaked credential usage [1], with the ‘IBM X-Force Threat Intelligence Index 2024’ reporting 71% year-on-year increase in cyber-attacks which utilize stolen or compromised credentials [2].

Darktrace coverage of leaked credentials

In early 2024, one Darktrace customer was compromised by a malicious actor after their internal credentials had been leaked on the dark web. Subsequent attack phases were detected by Darktrace/Network and the customer was alerted to the suspicious activity via the Proactive Threat Notification (PTN) service, following an investigation by Darktrace’s Security Operation Center (SOC).

Darktrace detected a device on the network of a customer in the US carrying out a string of anomalous activity indicative of network compromise. The device was observed using a new service account to authenticate to a Virtual Private Network (VPN) server, before proceeding to perform a range of suspicious activity including internal reconnaissance and lateral movement.

Malicious actors seemingly gained access to a previously unused service account for which they were able to set up multi-factor authentication (MFA) to access the VPN. As this MFA setup was made possible by the configuration of the customer’s managed service provider (MSP), the initial access phase of the attack fell outside of Darktrace’s purview.

Unfortunately for the customer in this case, Darktrace RESPOND™ was not enabled on the network at the time of the attack. Had RESPOND been active, it would have been able to autonomously act against the malicious activity by disabling users, strategically blocking suspicious connections and limiting devices to their expected patterns of activity.

Attack timeline of leaked credentials spotted by darktrace

Network Scanning Activity

On February 22, 2024, Darktrace detected the affected device performing activity indicative of network scanning, namely initiating connections on multiple ports, including ports 80, 161 389 and 445, to other internal devices. While many of these internal connection attempts were unsuccessful, some successful connections were observed.

Devices on a network can gather information about other internal devices by performing network scanning activity. Defensive scanning can be used to support network security, allowing internal security teams to discover vulnerabilities and potential entry points that require their attention, however attackers are also able to take advantage of such information, such as open ports and services available on internal devices, with offensive scanning.

Brute Force Login Attempts

Darktrace proceeded to identify the malicious actor attempting to access a previously unused service account for which they were able to successfully establish MFA to access the organization’s VPN. As the customer’s third-party MSP had been configured to allow all users to login to the organization’s VPN using MFA, this login was successful. Moreover, the service account had never previously been used and MFA and never been established, allowing the attacker to leverage it for their own nefarious means.

Darktrace/Network identified the attacker attempting to authenticate over the Kerberos protocol using a total of 30 different usernames, of which two were observed successfully authenticating. There was a total of 6 successful Kerberos logins identified from two different credentials.  Darktrace also observed over 100 successful NTLM attempts from the same device for multiple usernames including “Administrator” and “mail”. These credentials were later confirmed by the customer to have been stolen and leaked on the dark web.

Advanced Search query results showing the usernames that successfully authenticated via NTLM.
Figure 1: Advanced Search query results showing the usernames that successfully authenticated via NTLM.

Even though MFA requirements had been satisfied when the threat actor accessed the organization’s VPN, Darktrace recognized that this activity represented a deviation from its previously learned behavior.

Malicious actors frequently attempt to gain unauthorized access to accounts and internal systems by performing login attempts using multiple possible usernames and passwords. This type of brute-force activity is typically accomplished using computational power via the use of software or scripts to attempt different username/password combinations until one is successful.

By purchasing stolen credentials from dark web marketplaces, attackers are able to significantly increase the success rate of brute-force attacks and, if they do gain access, they can easily act on their objectives, be that exfiltrating sensitive data or moving through their target networks to further the compromise.

Share Enumeration

Around 30 minutes after the initial network scanning activity, the compromised device was observed performing SMB enumeration using one of the aforementioned accounts. Darktrace understood that this activity was suspicious as the device had never previously been used to perform SMB activity and had not been tagged as a security device.

Darktrace/Network identifying the suspicious SMB enumeration performed by the compromised device.
Figure 2: Darktrace/Network identifying the suspicious SMB enumeration performed by the compromised device.

Such enumeration can be used by malicious actors to gain insights into the structures and configurations of a target device, view permissions associated with shared resources, and also view general identifying information about the system.

Darktrace further identified that the device connected to the named pipe “srvsvc”. By enumerating over srvsvc, a threat actor is able to request a list of all available SMB shares on a destination device, enabling further data gathering as part of network reconnaissance. Srvsvc also provides access to remote procedure call (RPC) for various services on a destination device.

At this stage, a Darktrace/Network Enhanced Monitoring model was triggered for lateral movement activity taking place on the customer’s network. As this particular customer was subscribed to the PTN service, the Enhanced Monitoring model alert was promptly triaged and investigated by the Darktrace SOC. The customer was alerted to the emerging activity and given full details of the incident and the SOC team’s investigation.

Attack and Reconnaissance Tool Usage

A few minutes later, Darktrace observed the device making a connection with a user agent associated with the Nmap network scanning tool, “Mozilla/5.0 (compatible; Nmap Scripting Engine; https://nmap.org/book/nse[.]html)”. While these tools are often used legitimately by an organization’s security team, they can also be used maliciously by attackers to exploit vulnerabilities that attackers may have unearthed during earlier reconnaissance activity.

As such services are often seen as normal network traffic, attackers can often use them to bypass traditional security measures. Darktrace’s Self-Learning AI, however, was able to recognize that the affected device was not a security device and therefore not expected to carry out such activity, even if it was using a legitimate Nmap service.

Darktrace/Network identifying the compromised device using the Nmap scanning tool.
Figure 3: Darktrace/Network identifying the compromised device using the Nmap scanning tool.

Further Lateral Movement

Following this suspicious Nmap usage, Darktrace observed a range of additional anomalous SMB activity from the aforementioned compromised account. The affected device attempted to establish almost 900 SMB sessions, as well as performing 65 unusual file reads from 29 different internal devices and over 300 file deletes for the file “delete.me” from over 100 devices using multiple paths, including ADMIN$, C$, print$.

Darktrace also observed the device making several DCE-RPC connections associated with Active Directory Domain enumeration, including DRSCrackNames and DRSGetNCChanges; a total of more than 1000 successful DCE-RPC connection were observed to a domain controller.

As this customer did not have Darktrace/Network's autonomous response deployed on their network, the above detailed lateral movement and network reconnaissance activity was allowed to progress unfettered, until Darktrace’s SOC alerted the customer’s security team to take urgent action. The customer also received follow-up support through Darktrace’s Ask the Expert (ATE) service, allowing them to contact the analyst team directly for further details and support on the incident.

Thanks to this early detection, the customer was able to quickly identify and disable affected user accounts, effectively halting the attack and preventing further escalation.

Conclusions

Given the increasing trend of ransomware attackers exfiltrating sensitive data for double extortion and the rise of information stealers, stolen credentials are commonplace across dark web marketplaces. Malicious actors can exploit these leaked credentials to drastically lower the barrier to entry associated with brute-forcing access to their target networks.

While implementing well-configured MFA and enforcing regular password changes can help protect organizations, these measures alone may not be enough to fully negate the advantage attackers gain with stolen credentials.

In this instance, an attacker used leaked credentials to compromise an unused service account, allowing them to establish MFA and access the customer’s VPN. While this tactic may have allowed the attacker to evade human security teams and traditional security tools, Darktrace’s AI detected the unusual use of the account, indicating a potential compromise despite the organization’s MFA requirements being met. This underscores the importance of adopting an intelligent decision maker, like Darktrace, that is able to identify and respond to anomalies beyond standard protective measures.

Credit to Charlotte Thompson, Cyber Security Analyst, Ryan Traill, Threat Content Lead

Appendices

Darktrace DETECT Model Coverage

-       Device / Suspicious SMB Scanning Activity (Model Alert)

-       Device / ICMP Address Scan (Model Alert)

-       Device / Network Scan (Model Alert)

-       Device / Suspicious LDAP Search Operation (Model Alert)

-       User / Kerberos Username Brute Force (Model Alert)

-       Device / Large Number of Model Breaches (Model Alert)

-       Anomalous Connection / SMB Enumeration (Model Alert)

-       Device / Multiple Lateral Movement Model Breaches (Enhanced Monitoring Model Alert)

-       Device / Possible SMB/NTLM Reconnaissance (Model Alert)

-       Anomalous Connection / Possible Share Enumeration Activity (Model Alert)

-       Device / Attack and Recon Tools (Model Alert)

MITRE ATT&CK Mapping

Tactic – Technique - Code

INITIAL ACCESS - Hardware Additions     -T1200

DISCOVERY - Network Service Scanning -T1046

DISCOVERY - Remote System Discovery - T1018

DISCOVERY - Domain Trust Discovery      - T1482

DISCOVERY - File and Directory Discovery - T1083

DISCOVERY - Network Share Discovery - T1135

RECONNAISSANCE - Scanning IP Blocks - T1595.001

RECONNAISSANCE - Vulnerability Scanning - T1595.002

RECONNAISSANCE - Client Configurations - T1592.004

RECONNAISSANCE - IP Addresses - T1590.005

CREDENTIAL ACCESS - Brute Force - T1110

LATERAL MOVEMENT - Exploitation of Remote Services -T1210

References

  1. 2024 Google Cloud Threat Horizons Report
    https://services.google.com/fh/files/misc/threat_horizons_report_h12024.pdf
  2. IBM X-Force Threat Intelligence Index 2024
    https://www.ibm.com/reports/threat-intelligence
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Charlotte Thompson
Cyber Analyst

More in this series

No items found.

Blog

/

AI

/

November 18, 2026

Agentic attacks in the wild: Inside three ARTEX investigations

Default blog imageDefault blog image

Key insights

·       Darktrace observed activity in several customer environments involving infrastructure and behaviors associated with reported ARTEX-enabled campaigns, including activity linked to China-nexus espionage and financially motivated attacks.

·       In the higher-confidence cases, known infrastructure appeared alongside beaconing, unusual TLS, reconnaissance, tunneling, script retrieval, SMB activity and external data transfer. One Azure case had no observed network command and control at all, only key listing and application identity activity.

·       ARTEX is now used by actors with different objectives. Identifying the framework can help locate relevant activity, while the behavior around the affected system provides the stronger evidence for understanding compromise and attribution.

‍

Introduction

Attackers have moved beyond using AI for phishing and are running agentic frameworks; open-source tools like ARTEX, CAIRN, PentAGI and Hexstrike that let AI agents scan, exploit and move through an environment with little human input [1]. ARTEX has moved quickly from an offensive security project into live intrusion activity. Since at least August 2026, the framework has been associated with espionage, financially motivated attacks and opportunistic campaigns across government, financial services, technology, defense, telecommunications and other sectors. The FBI has documented ARTEX activity spanning reconnaissance, exploitation, credential abuse, lateral movement, collection, command and control, and exfiltration [2].

Darktrace has observed activity in customer environments that overlaps with infrastructure, tooling and behaviors reported in several of these campaigns. The cases below highlight how those intrusions appeared on the network, including the activity visible before an analyst can determine which actor or framework may be responsible.

ARTEX as part of the attacker workflow

ARTEX is an open-source, multi-agent offensive security platform that converts high-level objectives into actions carried out by specialized agents [2]. Operators have used it to automate activity across the attack lifecycle, including scanning, exploitation, credential activity and post-compromise operations. Some reported intrusions moved from initial targeting to privileged access in under three hours [2].

The framework is now associated with actors pursuing different objectives and using different post-exploitation tooling. The original public repository was removed in October 2026, but archived copies and localized versions remain available. For defenders, ARTEX is more useful as context for an investigation than as an attribution shortcut.

Darktrace observations show the same point at network level. Infrastructure linked to reported ARTEX campaigns appeared alongside beaconing, tunneling, unusual TLS, reconnaissance, file retrieval and lateral activity.

Case 1: Espionage-linked activity

Darktrace observed activity associated with BLOODALCHEMY command-and-control (C2) infrastructure in two customer environments. In one environment, five devices communicated with nginxmysql[.]com and 45.153.126[.]223 between October 23 and November 2. Both indicators had previously been linked to China-nexus espionage activity involving ARTEX [4].

The connections were accompanied by suspicious beaconing, repeated successful connections and unusual self-signed TLS. One system began making suspicious TLS connections to nginxmysql[.]com on October 23. Beaconing followed on October 24, and SMB scanning appeared later in the sequence. Other affected systems subsequently communicated with previously unseen external endpoints.

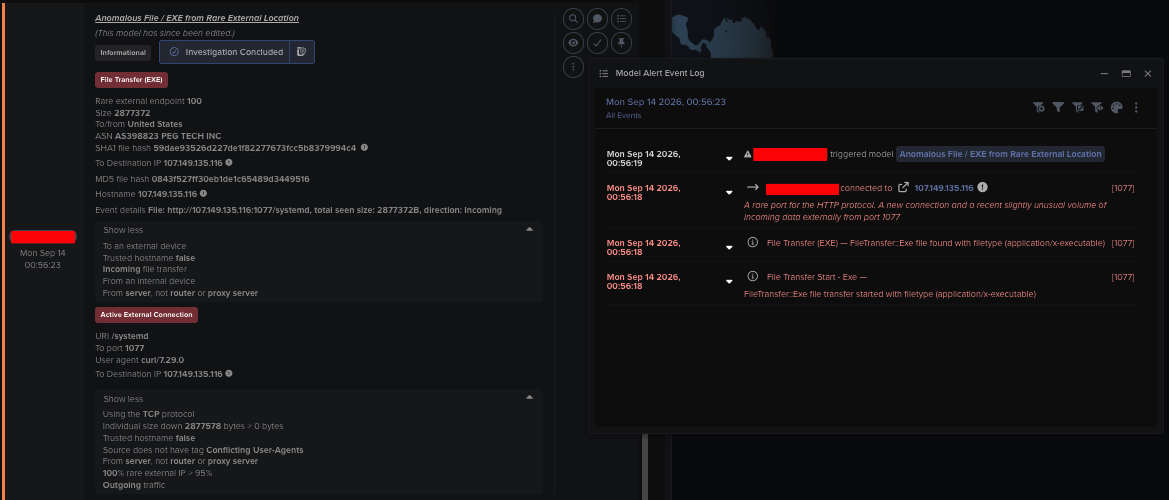
Prior to the observed C2, Darktrace detected curl requests retrieving executable and script content including /systemd, /wazuh, linux_amd64, u.sh and q.sh. Related telemetry included DRSGetNCChanges activity consistent with DCSync, LDAP enumeration, DNS zone transfers, network scanning, certificate downloads and SMB writes involving start.bat.

‍

Figure 1: Darktrace investigation showing suspicious network activity associated with infrastructure linked to reported ARTEX activity.

‍

Figure 2: Darktrace detection showing anomalous self-signed TLS activity during the espionage-linked investigation.

‍

BLOODALCHEMY has been reported in more than one China-nexus cluster [5]. SoftEther infrastructure observed in one environment provided another point of correlation with reported VAPOR PANDA tradecraft. The moderate-confidence assessment tying this to a Chinese nexus threat actor is based on infrastructure, victim context, tradecraft behavior that followed the initial connection, and public reporting.

Case 2: Financial-sector activity

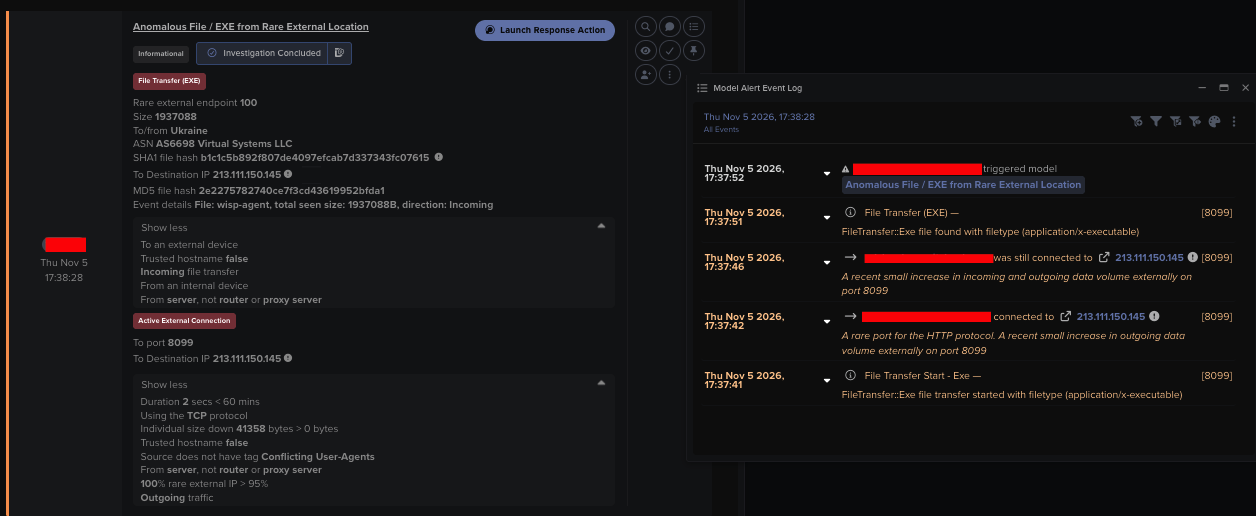
In early November, Darktrace observed activity in two financial-sector environments that overlap with reported ARTEX infrastructure. On November 5, a server connected to 213.111.150[.]145:8099 and downloaded wisp-agent, associated with WISP C2 activity.

In a second environment, a device attempted connections to 85.11.167[.]52 on November 1 and 2. The connections occurred alongside beaconing to new and rare destinations, anomalous TLS, possible tunneling and unusual package downloads.

The device also communicated with temp[.]sh, ssh.localhost[.]run, localhost[.]run, termbin[.]com, pastebin[.]com and GitHub-hosted release infrastructure. The sequence showed potential tooling retrieval, C2, tunneling and use of external services capable of staging or moving data.

Figure 3: Darktrace investigation showing connections to new and rare external destinations during the financial-sector activity.

‍

Case 3: Credential collection in Azure

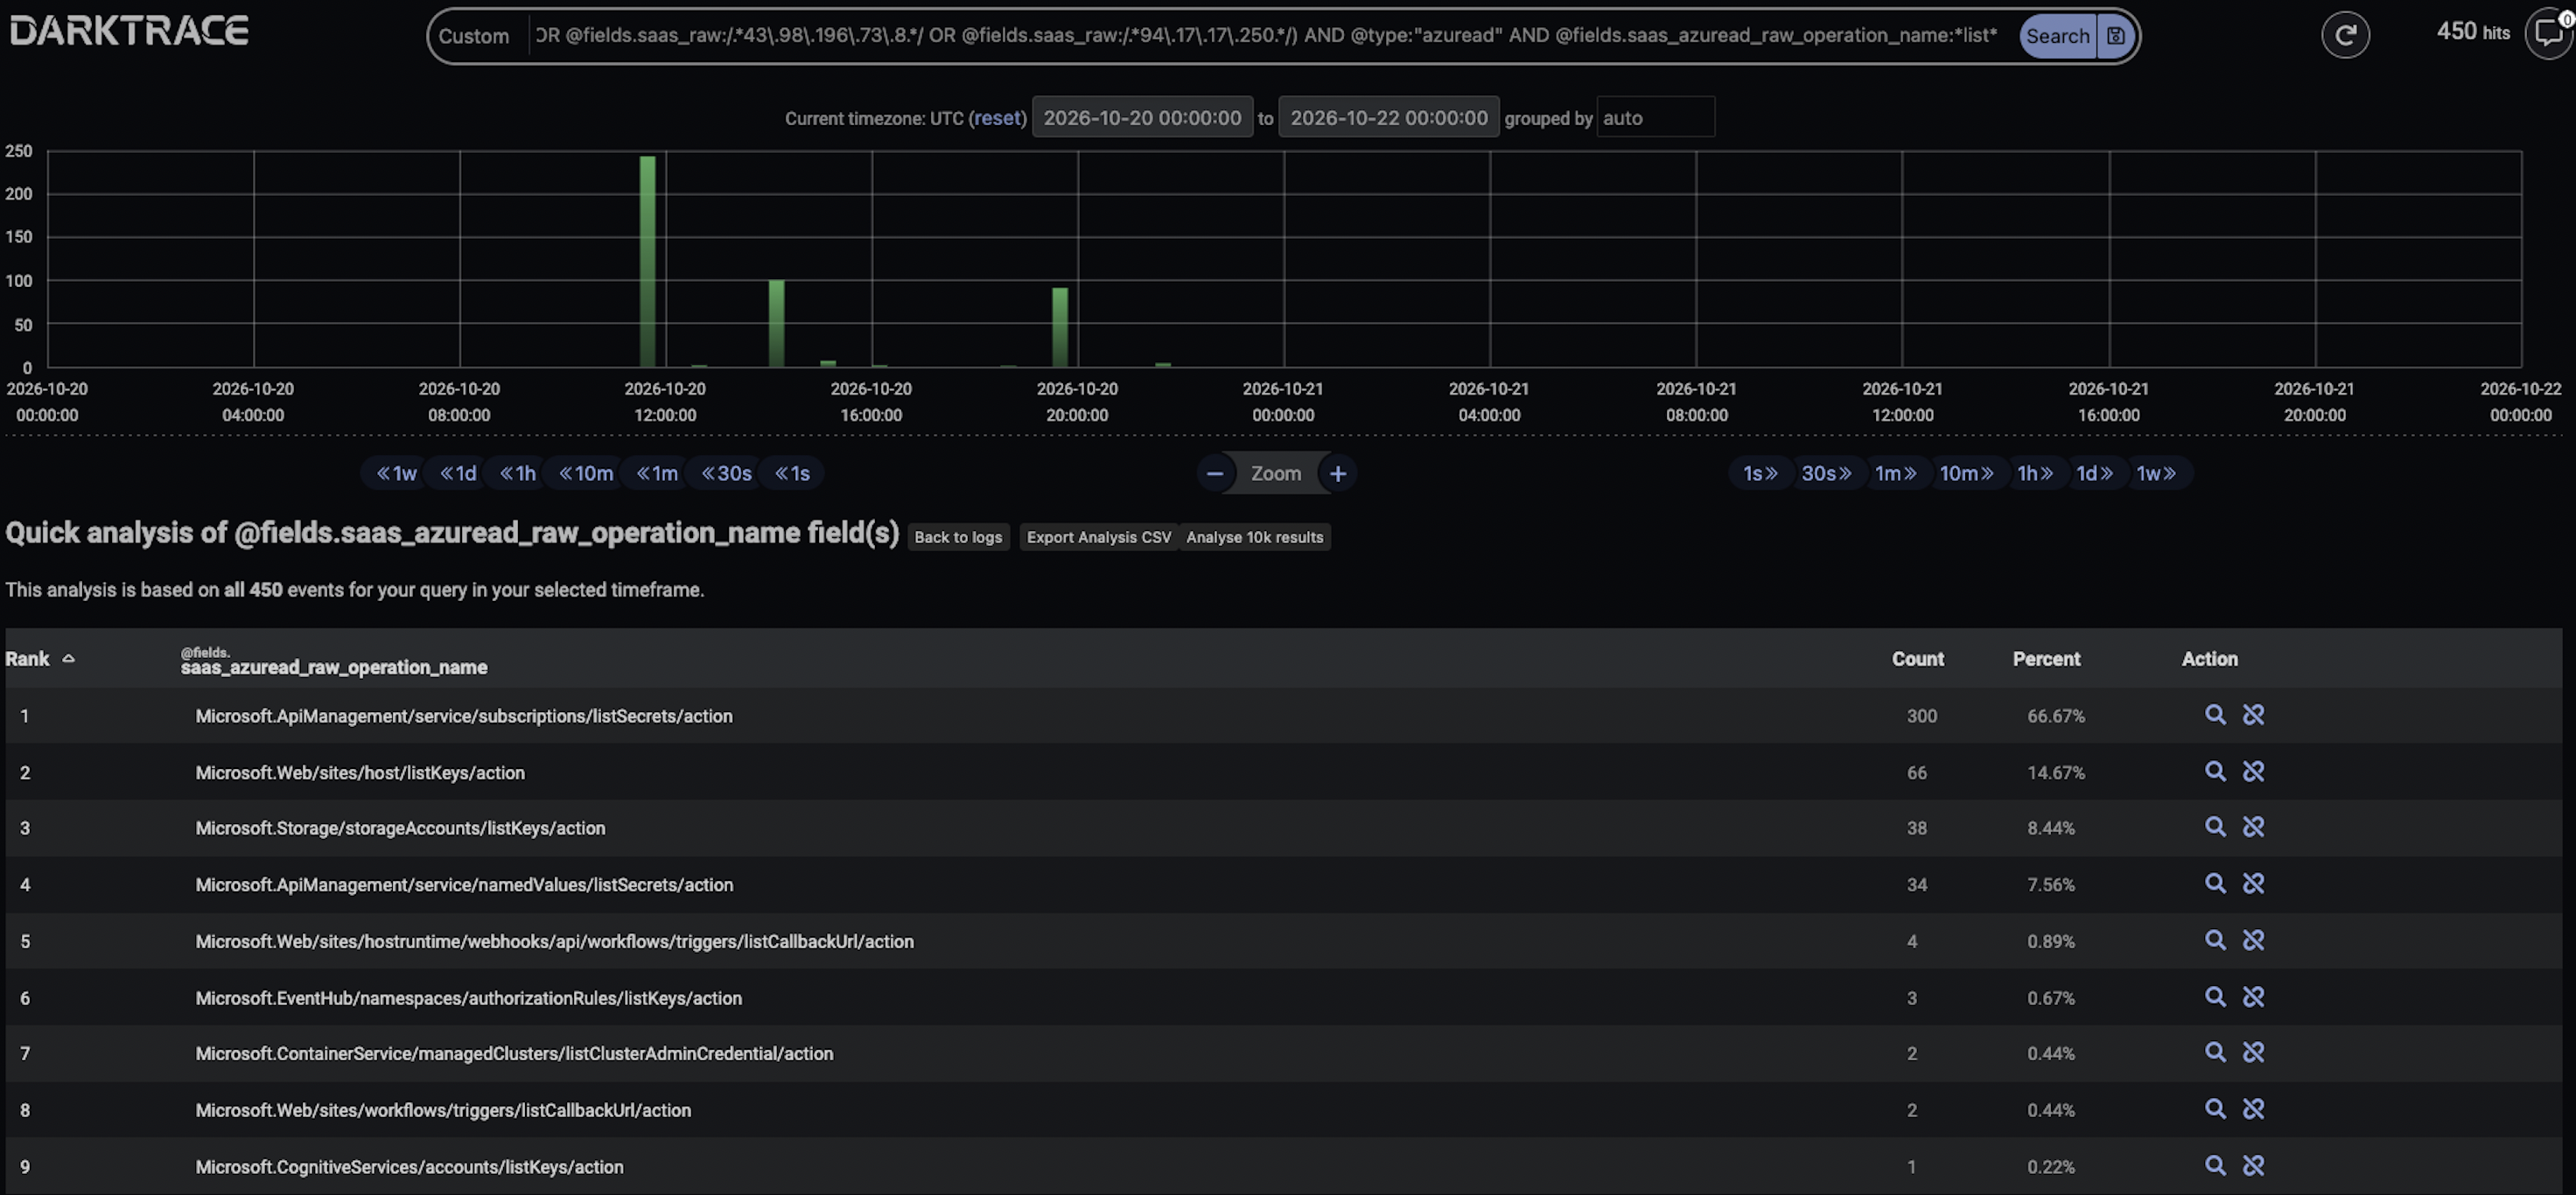
On October 20, Darktrace observed a sweep of credential collection in a customer’s Azure environment that is consistent with ARTEX use. The intrusion began with connections to the virtual network from 43.98.196[.]73 (Alibaba Cloud). Open-source scanning data associates the address with ARTEX.

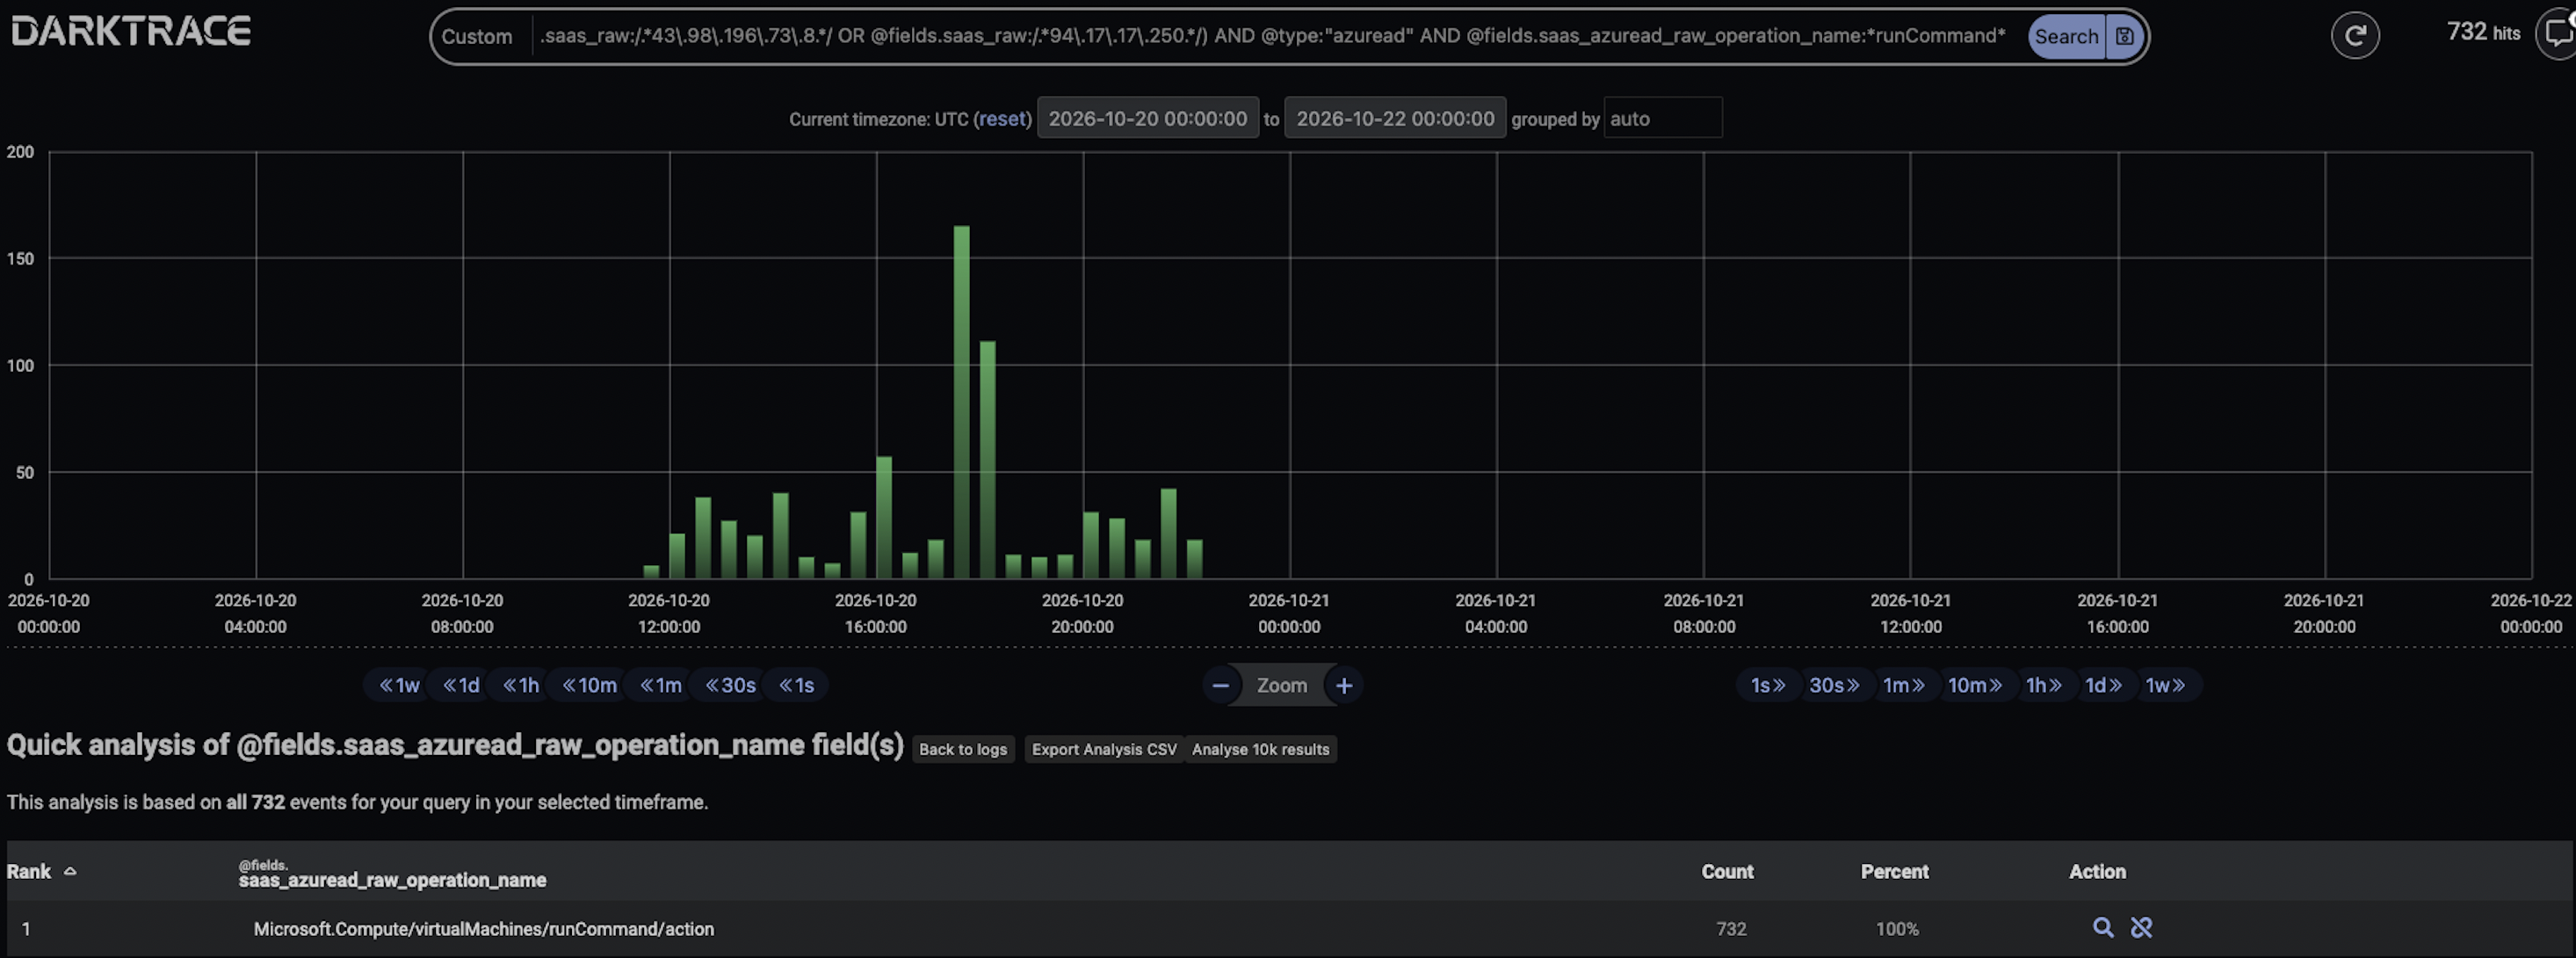
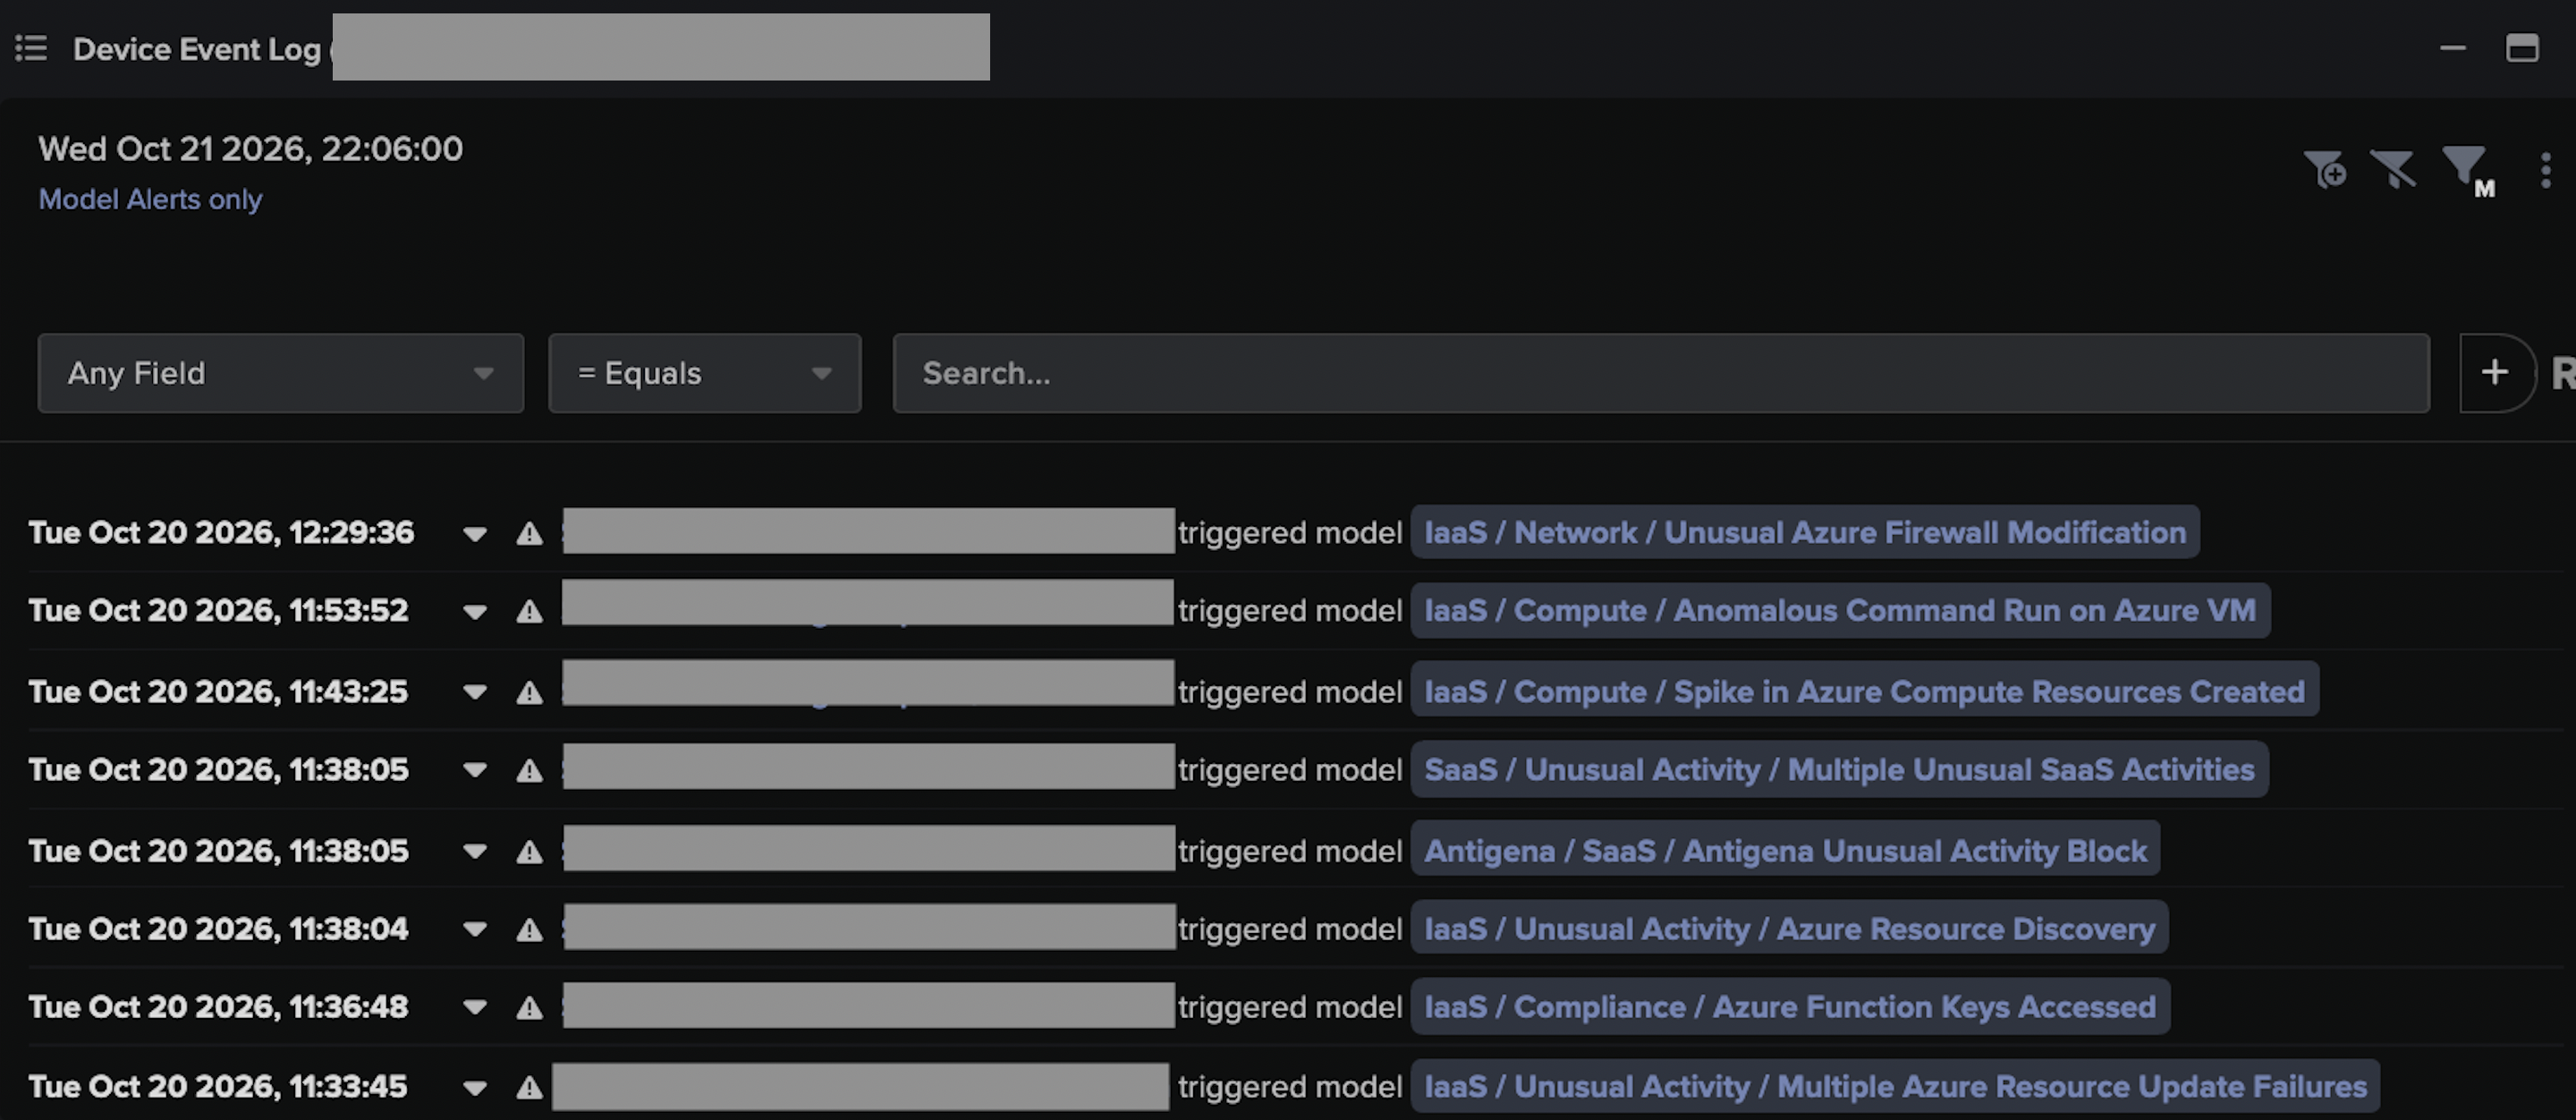
A compromised user identity made requests to the Azure Resource Manager API, though how it was compromised is unknown. The requests listed keys and secrets across API Management, web and function apps, Cognitive Services, Event Hubs, storage accounts and a managed Kubernetes cluster. With those credentials the attacker compromised multiple application identities. The attacker then used the application identities and the user identity to retrieve more credentials, change firewall and security rules and run scripts on virtual machines. Microsoft Defender alerts showed attempted execution of scripts related to Mimikatz and Impacket.

In a cloud environment, such privileged and enumerative operations are potentially indistinguishable from legitimate administrative actions. Consequently, the sequence and context of such operations signified more than any specific API call. There was no C2 traffic to match, and listing keys and using application identities are also what administrators and automation do. A compromised user, credential retrieval across several Azure services, new application identities, more credential collection and changes to security controls only made sense together, and by then access was spreading through the cloud environment.

‍

Figure 4: Darktrace Advanced Search showing Azure AD operation names associated with the activity.

‍

Figure 5: Darktrace Advanced Search showing the Azure Resource Manager action used to execute scripts.
Figure 6: Darktrace Device Event log window showing the triggered models related to the suspicious Azure activity.

‍

Shared tooling weakens attribution signals

The three cases looked different on the network: BLOODALCHEMY infrastructure and espionage-consistent tradecraft, WISP infrastructure in financial-sector systems, and Azure identity and control-plane activity with no C2 at all.

Shared tooling has complicated attribution for years, and ARTEX adds to it because the framework carries out more of the attack, so reconnaissance, exploitation attempts and some post-compromise activity can look the same whoever set the objective. Attribution still needs infrastructure, malware, victimology, timing and the sequence of behavior inside the environment, and an ARTEX link is one input to that. Moreover, the behavior and the agent will still be shaped by the biases, preferences, and tradecraft of its operators.

At its core, ARTEX’s planner and worker agents identify and record facts, while exploring intents. However, the way the Large Language Model (LLM) chooses its next steps toward an objective is shaped fundamentally by the skills and tools available in its context. This includes its starting context, as well as various possible Model Context Protocol (MCP) plugins and user-injected context (e.g. user input mid-operation). Operators still have preferred tradecraft, and this preference shapes the pathways the harness will provide to the LLM in context prompts. Even on the same platform, customization based on operator preferences and goals will remain a key facet of campaign and actor identification.

Detection and response

Across the Darktrace cases, the stronger signals came from behavior after the connection: beaconing, abnormal TLS, reconnaissance, unusual authentication, tunneling, script retrieval, SMB activity and outbound transfer. Automated activity also produced compressed bursts of requests, sequential enumeration and repeated attempts with small changes.

With agentic tools reaching privileged access in under three hours, analysts may have only a short window to connect scanning or authentication activity to credential changes, new administrative access, tooling retrieval or lateral movement. Keeping network, identity and cloud telemetry together shows what happened before and after the first match, and whether a connection was noise or an intrusion moving toward privileged access.

ARTEX won’t be the last of these frameworks. The next ones will come with new capabilities and defaults, but an intrusion still must interact with the target environment, and that shows up in how systems, identities and applications behave even after the indicator has aged out. The harder intrusions to catch will have no infrastructure to match, just ordinary API calls and legitimate identities. Detecting those depends on knowing what normal looks like for each identity and device.

‍

Credit to Nathaniel Jones (SVP, Global Threat Intelligence), Eugene Chua (Principal Analyst), Sam Lister (Senior Security Researcher), Adam Potter (Associate Principal Cyber Analyst)

Appendices

Darktrace model detections

·       Anomalous Connection / Multiple HTTP POSTs to Rare Hostname

·       Anomalous Connection / Rare External SSL Self-Signed

·       Anomalous Connection / Suspicious Self-Signed SSL

·       Compromise / Large Number of Suspicious Successful Connections

·       Compromise / Suspicious Beaconing Behaviour

·       Compromise / Agent Beacon to New Endpoint

·       Compromise / Beacon to Young Endpoint

·       Compromise / SSL Beaconing to Rare Destination

·       Compromise / Suspicious TLS Beaconing To Rare External

·       Compromise / Possible Tunnelling to Bin Services

·       Device / Anomalous Github Download

·       Device / Anomalous Package Download

·       Device / Initial Attack Chain Activity

Indicators of compromise (IoCs)

nginxmysql[.]com

45.153.126[.]223

213.111.150[.]145

wisp-agent

85.11.167[.]52

43.98.196[.]73

192.121.47[.]20

www[.]ddduuuppp[.]com

89.46.234[.]50

sqlserver-sqlite[.]com

199.19.95[.]66

graphics-hook-filter64.dll

graphics-hook_config.bin

References

1.      Google. GTIG AI Threat Tracker - https://cloud.google.com/blog/topics/threat-intelligence/agentic-threat-activity-crosses-a-significant-threshold

2.      Federal Bureau of Investigation, Threat Overview of ARTEX Autonomous Penetration Testing Framework, FLASH-20261113-001, 13 November 2026: https://www.ic3.gov/CSA/2026/261113.pdf

3.      Microsoft Security Blog, Storm-0940 Uses ARTEX Agentic AI in ConnectWise Supply Chain Compromise: https://www.microsoft.com/en-us/security/blog/2026/10/21/storm-0940-uses-artex-agentic-ai-connectwise-supply-chain-compromise/

4.      CrowdStrike, VAPOR PANDA Uses ARTEX to Scale Global Campaign: https://www.crowdstrike.com/en-us/blog/vapor-panda-uses-artex-to-scale-global-campaign/

5.      Bitdefender, SilkParasite: Tracking a China-Nexus APT Across Central Asia: https://www.bitdefender.com/en-us/blog/businessinsights/silkparasite-tracking-china-nexus-apt-across-central-asia

‍

‍

Continue reading
About the author
Nathaniel Jones
SVP, Global Threat Intelligence

Blog

/

AI

/

November 18, 2026

Darktrace qualifies for NATO’s Cybersecurity Dynamic Marketplace

Default blog imageDefault blog image

Darktrace has been selected to join NATO’s Cybersecurity Dynamic Marketplace (CSDM), an initiative designed to give NATO faster, more flexible access to cybersecurity technology and services in support of its missions.  

Established by the NATO Communications and Information Agency (NCIA), the marketplace brings together qualified suppliers whose technical capabilities have been reviewed, helping NATO match specialist expertise to project needs and respond more quickly to changing operational priorities.

Qualified across all eight cybersecurity categories

The program’s first phase, known as Lot 1, covers eight cybersecurity categories. Suppliers can qualify in individual categories; Darktrace has qualified to compete for future work across all eight:

  • Identity, Credential and Access Management
  • Endpoint Protection and Platforms
  • Network and Perimeter Security
  • Cloud Security
  • Threat Detection and Analytics Platforms
  • Vulnerability and Exposure Management
  • Digital Forensics and Evidence Platforms
  • Professional Services

Darktrace’s qualification across all eight categories reflects the breadth of our technology and services.

Supporting government and defense organizations

Nation-state attacks, compromised suppliers, the rapid exploitation of security weaknesses and attackers’ growing use of AI are increasing pressure on public-sector organizations. At the same time, agencies are adopting cloud services, connecting the technology that runs physical operations, and introducing automation and AI. Security teams must manage these changes while keeping essential operations running and sensitive information secure.

Protecting these environments requires an understanding of how people, AI and connected systems interact, and the ability to recognize when their activity creates risk. Threats can span several systems, making it essential for security teams to connect related activity and respond quickly.

The Darktrace Behavioral Defense Platform™ supports this approach through unified visibility, continuous behavioral monitoring and autonomous response across AI, people and infrastructure.

At its core, Darktrace’s Adaptive AI™ continuously learns how each organization behaves, building a unique understanding of its people, AI agents and connected systems. This enables the platform to help identify activity that does not belong, connect related behavior across the organization, and investigate and respond to threats autonomously in real time, helping prevent disruption to essential operations.

Our selection builds on work to meet government security requirements internationally. Darktrace recently completed an independent assessment under Australia’s InfoSec Registered Assessors Program (IRAP) for Darktrace / NETWORK™ and Darktrace / OT™ against the Australian Government’s Information Security Manual PROTECTED-level controls. In the United States, Darktrace Federal continues to deliver the Darktrace technology to Department of War, Department of State, and Federal civilian organizations via its on-premises and FedRAMP CLASS D (High) Authorization platforms.

Together, these achievements demonstrate Darktrace’s ability to meet rigorous public-sector security requirements and reinforce its position as a trusted provider of mission-critical cybersecurity technology for government environments.

Meet us at NATO Edge 2026

Darktrace representatives will attend NATO Edge 2026, NCIA’s flagship technology event, in İzmir, Türkiye, from 17 to 19 November. We look forward to meeting government, military, and industry partners to discuss their cybersecurity priorities and how we can support them.

To learn more about the Darktrace Behavioral Defense Platform, visit the platform hub.

Continue reading
About the author
The Darktrace Community
あなたのデータ × DarktraceのAI
唯一無二のDarktrace AIで、ネットワークセキュリティを次の次元へ