Blog
/
Network
/
November 13, 2024

Tactics Behind the Royal and Blacksuit Ransomware

Delve into the complexities of the Royal and Blacksuit ransomware strains and their implications for cybersecurity in today’s digital landscape.
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Signe Zaharka
Principal Cyber Analyst
Default blog image
13
Nov 2024

What is BlackSuit Ransomware?

Since late 2023, Darktrace has detected BlackSuit ransomware infiltrating multiple customer networks in the US. This ransomware has targeted a wide range of industries, including arts, entertainment, real estate, public administration, defense, and social security.

Emerging in May 2023, BlackSuit is believed to be a spinoff of Royal ransomware due to similarities in code and Conti, and most likely consists of Russian and Eastern European hackers [1]. Recorded Future reported that the ransomware had affected 95 organizations worldwide, though the actual number is likely much higher [2]. While BlackSuit does not appear to focus on any particular sector, it has targeted multiple organizations in the healthcare, education, IT, government, retail and manufacturing industries [3]. Employing double extortion tactics, BlackSuit not only encrypts files but also steals sensitive data to leverage ransom payments.

BlackSuit has demanded over USD 500 million in ransoms, with the highest individual demand reaching USD 60 million [4]. Notable targets include CDK Global, Japanese media conglomerate Kadokawa, multiple educational institutions, Octapharma Plasma, and the government of Brazil [5][6][7][8].

Darktrace’s Coverage of BlackSuit Ransomware Attack

Case 1, November 2023

The earliest attack on a Darktrace customer by BlackSuit was detected at the start of November 2023. The unusual network activity began on a weekend—a time commonly chosen by ransomware groups to increase their chances of success, as many security teams operate with reduced staff. Darktrace identified indicators of the attackers’ presence on the network for almost two weeks, during which a total of 15 devices exhibited suspicious behavior.

The attack commenced with unusual internal SMB (Server Message Block) connections using a compromised service account. An internal device uploaded an executable (zzza.exe) to a domain controller (DC) and shortly after, wrote a script (socks5.ps1) to another device. According to a Cybersecurity Advisory from the CISA (Cybersecurity and Infrastructure Security Agency, US), the script file was a PowerShell reverse proxy [9].

Approximately an hour and a half later, the device to which the script was written exhibited uncommon WMI (Windows Management Instrumentation) activity. Two hours after receiving the executable file, the DC was observed making an outgoing NTLM request, using PowerShell to remotely execute commands, distributing differently named executable files (<PART OF THE CUSTOMER’S NAME>.exe), and controlling services on other devices.

Eighteen hours after the start of the unusual activity, Darktrace detected another device making repeated connections to “mystuff.bublup[.]com”, which the aforementioned CISA Advisory identifies as a domain used by BlackSuit for data exfiltration [9].

About ten minutes after the suspicious executables were distributed across the network, and less than 24 hours after the start of the unusual activity, file encryption began. A total of ten devices were seen appending the “.blacksuit” extension to files saved on other devices using SMB, as well as writing ransom notes (readme.blacksuit.txt). The file encryption lasted less than 20 minutes.

 An example of the contents of a BlackSuit ransom note being written over SMB.
Figure 1: An example of the contents of a BlackSuit ransom note being written over SMB.

During this compromise, external connections to endpoints related to ConnectWise’s ScreenConnect remote management tool were also seen from multiple servers, suggesting that the tool was likely being abused for command-and-control (C2) activity. Darktrace identified anomalous connectivity associated with ScreenConnect was seen up to 11 days after the start of the attack.

10 days after the start of the compromise, an account belonging to a manager was detected adding “.blacksuit” extensions to the customer’s Software-a-Service (SaaS) resources while connecting from 173.251.109[.]106. Six minutes after file encryption began, Darktrace flagged the unusual activity and recommended a block. However, since Autonomous Response mode was not enabled, the customer’s security team needed to manually confirm the action. Consequently, suspicious activity continued for about a week after the initial encryption. This included disabling authentication on the account and an unusual Teams session initiated from the suspicious external endpoint 216.151.180[.]147.

Case 2, February 2024

Another BlackSuit compromise occurred at the start of February 2024, when Darktrace identified approximately 50 devices exhibiting ransomware-related activity in another US customer’s environment. Further investigation revealed that a significant number of additional devices had also been compromised. These devices were outside Darktrace’s purview to the customer’s specific deployment configuration. The threat actors managed to exfiltrate around 4 TB of data.

Initial access to the network was gained via a virtual private network (VPN) compromise in January 2024, when suspicious connections from a Romanian IP address were detected. According to CISA, the BlackSuit group often utilizes the services of initial access brokers (IAB)—actors who specialize in infiltrating networks, such as through VPNs, and then selling that unauthorized access to other threat actors [9]. Other initial access vectors include phishing emails, RDP (Remote Desktop Protocol) compromise, and exploitation of vulnerable public-facing applications.

Similar to the first case, the file encryption began at the end of the working week. During this phase of the attack, affected devices were observed encrypting files on other internal devices using two compromised administrator accounts. The encryption activity lasted for approximately six and a half hours. Multiple alerts were sent to the customer from Darktrace’s Security Operations Centre (SOC) team, who began reviewing the activity within four minutes of the start of the file encryption.

Darktrace’s Cyber AI Analyst clustering together multiple events related to unusual activity on the network, including file encryption over SMB by BlackSuit.
Figure 2: Darktrace’s Cyber AI Analyst clustering together multiple events related to unusual activity on the network, including file encryption over SMB by BlackSuit.
Figure 3: A spike in model alerts on the day when file encryption by BlackSuit was observed in the network.

In this case, the threat actor utilized SystemBC proxy malware for command and control (C2). A domain controller (DC) was seen connecting to 137.220.61[.]94 on the same day the file encryption took place. The DC was also observed connecting to a ProxyScrape domain around the same time, which is related to the SOCKS5 protocol used by SystemBC. During this compromise, RDP, SSH, and SMB were used for lateral movement within the network.

Figure 4: A Cyber AI Analyst investigation alerting to a device on the VPN subnet making suspicious internal SSH connections due to malicious actors moving laterally within the network.

Signs of threat actors potentially being on the network were observed as early as two days prior to the file encryption. This included unusual internal network scanning via multiple protocols (ICMP, SMB, RDP, etc.), credential brute-forcing, SMB access failures, and anonymous SMBv1 sessions. These activities were traced to IP addresses belonging to two desktop devices in the VPN subnet associated with two regular employee user accounts. Threat actors were seemingly able to exploit at least one of these accounts due to LDAP legacy policies being in place on the customer’s environment.

A Cyber AI Analyst incident summary alerting to a device on the VPN subnet conducting internal reconnaissance.
Figure 5: A Cyber AI Analyst incident summary alerting to a device on the VPN subnet conducting internal reconnaissance.
Examples of the proposed Darktrace Autonomous Response actions on the day BlackSuit initiated file encryption.
Figure 6: Examples of the proposed Darktrace Autonomous Response actions on the day BlackSuit initiated file encryption.

Case 3, August 2024

The most recently observed BlackSuit compromise occurred in August 2024, when a device was observed attempting to brute-force the credentials of an IT administrator. This activity continued for 11 days.

Once the admin’s account was successfully compromised, network scanning, unusual WMI, and SAMR (Security Account Manager Remote protocol) activity followed. A spike in the use of this account was detected on a Sunday—once again, the attackers seemingly targeting the weekend—when the account was used by nearly 50 different devices.

The compromised admin’s account was exploited for data gathering via SMB, resulting in the movement of 200 GB of data between internal devices in preparation for exfiltration. The files were then archived using the naming convention “*.part<number>.rar”.

Around the same time, Darktrace observed data transfers from 19 internal devices to “bublup-media-production.s3.amazonaws[.]com,” totaling just over 200 GB—the same volume of data gathered internally. Connections to other Bublup domains were also detected. The internal data download and external data transfer activity took approximately 8-9 hours.

Unfortunately, Darktrace was not configured in Autonomous Response mode at the time of the attack, meaning any mitigative actions to stop the data gathering or exfiltration required human confirmation.  

One of the compromised devices was seen sending 80 GB of data to bublup-media-production.s3.amazonaws[.]com within a span of 4 hours.
Figure 7: One of the compromised devices was seen sending 80 GB of data to bublup-media-production.s3.amazonaws[.]com within a span of 4 hours.

Once the information was stolen, the threat actor moved on to the final stage of the attack—file encryption. Five internal devices, using either the compromised admin account or connecting via anonymous SMBv1 sessions, were seen encrypting files and writing ransom notes to five other devices on the network. The attempts at file encryption continued for around two hours, but Darktrace’s Autonomous Response capability was able to block the activity and prevent the attack from escalating.

Conclusion

The persistent and evolving threat posed by ransomware like BlackSuit underscores the critical importance of robust cybersecurity measures across all sectors. Since its emergence in 2023, BlackSuit has demonstrated a sophisticated approach to infiltrating networks, leveraging double extortion tactics, and demanding substantial ransoms. The cases highlighted above illustrate the varied methods and persistence of BlackSuit attackers, from exploiting VPN vulnerabilities to abusing remote management tools and targeting off-hours to maximize impact.

Although many similar connection patterns, such as the abuse of Bublup services for data exfiltration or the use of SOCKS5 proxies for C2, were observed during cases investigated by Darktrace, BlackSuit actors are highly sophisticated and tailors their attacks to each target organization. The consequences of a successful attack can be highly disruptive, and remediation efforts can be time-consuming and costly. This includes taking the entire network offline while responding to the incident, restoring encrypted files from backups (if available), dealing with damage to the organization’s reputation, and potential lawsuits.

These BlackSuit ransomware incidents emphasize the need for continuous vigilance, timely updates to security protocols, and the adoption of autonomous response technologies to swiftly counteract such attacks. As ransomware tactics continue to evolve, organizations must remain agile and informed to protect their critical assets and data. By learning from these incidents and enhancing their cybersecurity frameworks, organizations can better defend against the relentless threat of ransomware and ensure the resilience of their operations in an increasingly digital world.

Credit to Signe Zaharka (Principal Cyber Analyst) and Adam Potter (Senior Cyber Analyst)

Insights from Darktrace’s First 6: Half-year threat report for 2024

First 6: half year threat report darktrace screenshot

Darktrace’s First 6: Half-Year Threat Report 2024 highlights the latest attack trends and key threats observed by the Darktrace Threat Research team in the first six months of 2024.

  • Focuses on anomaly detection and behavioral analysis to identify threats
  • Maps mitigated cases to known, publicly attributed threats for deeper context
  • Offers guidance on improving security posture to defend against persistent threats

‍

‍

Appendices

Darktrace Model Detections

Anomalous Connection / Data Sent to Rare Domain

Anomalous Connection / High Volume of New or Uncommon Service Control

Anomalous Connection / New or Uncommon Service Control

Anomalous Connection / Rare WinRM Outgoing

Anomalous Connection / SMB Enumeration

Anomalous Connection / Suspicious Activity On High Risk Device

Anomalous Connection / Suspicious Read Write Ratio

Anomalous Connection / Suspicious Read Write Ratio and Unusual SMB

Anomalous Connection / Sustained MIME Type Conversion

Anomalous Connection / Uncommon 1 GiB Outbound

Anomalous Connection / Unusual Admin SMB Session

Anomalous File / Internal / Additional Extension Appended to SMB File

Anomalous File / Internal / Executable Uploaded to DC

Anomalous File / Internal / Unusual SMB Script Write

Anomalous Server Activity / Anomalous External Activity from Critical Network Device

Anomalous Server Activity / Outgoing from Server

Anomalous Server Activity / Rare External from Server

Anomalous Server Activity / Write to Network Accessible WebRoot

Compliance / Outgoing NTLM Request from DC

Compliance / Remote Management Tool On Server

Compliance / SMB Drive Write

Compromise / Beacon to Young Endpoint

Compromise / Beaconing Activity To External Rare

Compromise / Ransomware / Possible Ransom Note Read

Compromise / Ransomware / Possible Ransom Note Write

Compromise / Ransomware / SMB Reads then Writes with Additional Extensions

Compromise / Ransomware / Suspicious SMB Activity

Device / Anomalous RDP Followed By Multiple Model Breaches

Device / EXE Files Distributed to Multiple Devices

Device / Internet Facing Device with High Priority Alert

Device / Large Number of Model Breaches

Device / Large Number of Model Breaches from Critical Network Device

Device / Multiple Lateral Movement Model Breaches

Device / Network Scan

Device / New or Uncommon WMI Activity

Device / New or Unusual Remote Command Execution

Device / New User Agent To Internal Server

Device / SMB Lateral Movement

Device / SMB Session Brute Force (Admin)

Device / Suspicious SMB Scanning Activity

Device / Unusual LDAP Query For Domain Admins

SaaS / Access / Teams Activity from Rare Endpoint

SaaS / Resource / SaaS Resources With Additional Extensions

SaaS / Unusual Activity / Disabled Strong Authentication

SaaS / Unusual Activity / Multiple Unusual SaaS Activity Scores

SaaS / Unusual Activity / Unusual SaaS Activity Score

SaaS / Unusual Activity / Unusual Volume of SaaS Modifications

Unusual Activity / Anomalous SMB Delete Volume

Unusual Activity / Anomalous SMB Move & Write

Unusual Activity / High Volume Client Data Transfer

Unusual Activity / High Volume Server Data Transfer

Unusual Activity / Internal Data Transfer

Unusual Activity / SMB Access Failures

Unusual Activity / Sustained Anomalous SMB Activity

Unusual Activity / Unusual External Data to New Endpoint

User / New Admin Credentials on Client

User / New Admin Credentials on Server

User/ Kerberos Password Bruteforce

Autonomous Response Models

Antigena / Network / External Threat / Antigena File then New Outbound Block

Antigena / Network / External Threat / Antigena Ransomware Block

Antigena / Network / External Threat / Antigena Suspicious Activity Block

Antigena / Network / External Threat / SMB Ratio Antigena Block

Antigena / Network / Insider Threat / Antigena Internal Anomalous File Activity

Antigena / Network / Insider Threat / Antigena Internal Data Transfer Block

Antigena / Network / Insider Threat / Antigena Large Data Volume Outbound Block

Antigena / Network / Insider Threat / Antigena Network Scan Block

Antigena / Network / Insider Threat / Antigena Unusual Privileged User Activities Block

Antigena / Network / Insider Threat / Antigena Unusual Privileged User Activities Pattern of Life Block

Antigena / Network / Significant Anomaly / Antigena Breaches Over Time Block

Antigena / Network / Significant Anomaly / Antigena Controlled and Model Breach

Antigena / Network / Significant Anomaly / Antigena Enhanced Monitoring from Client Block

Antigena / Network / Significant Anomaly / Antigena Enhanced Monitoring from Server Block

Antigena / Network / Significant Anomaly / Antigena Significant Anomaly from Client Block

Antigena / Network / Significant Anomaly / Antigena Significant Server Anomaly Block

Antigena / Network / Significant Anomaly / Repeated Antigena Breaches

Antigena / SaaS / Antigena Unusual Activity Block

List of Indicators of Compromise (IoCs)

IoC - Type - Description + Confidence

.blacksuit - File extension – When encrypting the files, this extension is appended to the filename – High

readme.blacksuit.txt – ransom note - A file demanding cryptocurrency payment in exchange for decrypting the victim's files and not leaking the stolen data – High

mystuff.bublup[.]com, bublup-media-production.s3.amazonaws[.]com – data exfiltration domains related to an organization and project management app that has document sharing functionality – High

137.220.61[.]94:4001 – SystemBC C2 related IP address (this tool is often used by other ransomware groups as well) - Medium

173.251.109[.]106 – IP address seen during a SaaS BlackSuit compromise (during file encryption) – Medium

216.151.180[.]147 – IP address seen during a SaaS BlackSuit compromise (during an unusual Teams session) - Medium

MITRE ATT&CK Mapping

Tactic - Technqiue

Account Manipulation - PERSISTENCE - T1098

Alarm Suppression - INHIBIT RESPONSE FUNCTION - T0878

Application Layer Protocol - COMMAND AND CONTROL - T1071

Automated Collection - COLLECTION - T1119

Block Command Message - INHIBIT RESPONSE FUNCTION - T0803

Block Reporting Message - INHIBIT RESPONSE FUNCTION - T0804

Browser Extensions - PERSISTENCE - T1176

Brute Force I/O - IMPAIR PROCESS CONTROL - T0806

Brute Force - CREDENTIAL ACCESS - T1110

Client Configurations - RECONNAISSANCE - T1592.004 - T1592

Cloud Accounts - DEFENSE EVASION, PERSISTENCE, PRIVILEGE ESCALATION, INITIAL ACCESS - T1078.004 - T1078

Data Destruction - IMPACT - T1485

Data Destruction - INHIBIT RESPONSE FUNCTION - T0809

Data Encrypted for Impact - IMPACT - T1486

Data from Cloud Storage Object - COLLECTION - T1530

Data Staged - COLLECTION - T1074

Domain Groups - DISCOVERY - T1069.002 - T1069

Email Collection - COLLECTION - T1114

Exfiltration Over C2 Channel - EXFILTRATION - T1041

Exfiltration to Cloud Storage - EXFILTRATION - T1567.002 - T1567

Exploit Public - Facing Application - INITIAL ACCESS - T1190

Exploitation for Privilege Escalation - PRIVILEGE ESCALATION - T0890

Exploitation of Remote Services - LATERAL MOVEMENT - T1210

File and Directory Discovery - DISCOVERY - T1083

File Deletion - DEFENSE EVASION - T1070.004 - T1070

IP Addresses - RECONNAISSANCE - T1590.005 - T1590

Lateral Tool Transfer - LATERAL MOVEMENT - T1570

LLMNR/NBT - NS Poisoning and SMB Relay - CREDENTIAL ACCESS, COLLECTION - T1557.001 - T1557

Modify Alarm Settings - INHIBIT RESPONSE FUNCTION - T0838

Modify Control Logic - IMPAIR PROCESS CONTROL, INHIBIT RESPONSE FUNCTION - T0833

Modify Parameter - IMPAIR PROCESS CONTROL - T0836

Network Service Scanning - DISCOVERY - T1046

Network Share Discovery - DISCOVERY - T1135

Pass the Hash - DEFENSE EVASION, LATERAL MOVEMENT - T1550.002 - T1550

RDP Hijacking - LATERAL MOVEMENT - T1563.002 - T1563

Remote Access Software - COMMAND AND CONTROL - T1219

Remote Desktop Protocol - LATERAL MOVEMENT - T1021.001 - T1021

Remote System Discovery - DISCOVERY - T1018

Rename System Utilities - DEFENSE EVASION - T1036.003 - T1036

Scanning IP Blocks - RECONNAISSANCE - T1595.001 - T1595

Scheduled Transfer - EXFILTRATION - T1029

Service Execution - EXECUTION - T1569.002 - T1569

Service Stop - IMPACT - T1489

SMB/Windows Admin Shares - LATERAL MOVEMENT - T1021.002 - T1021

Stored Data Manipulation - IMPACT - T1565.001 - T1565

Taint Shared Content - LATERAL MOVEMENT - T1080

Valid Accounts - DEFENSE EVASION, PERSISTENCE, PRIVILEGE ESCALATION, INITIAL ACCESS - T1078

Vulnerability Scanning - RECONNAISSANCE - T1595.002 - T1595

Web Protocols - COMMAND AND CONTROL - T1071.001 - T1071

Web Services - RESOURCE DEVELOPMENT - T1583.006 - T1583

Web Shell - PERSISTENCE - T1505.003 - T1505

Windows Management Instrumentation - EXECUTION - T1047

Windows Remote Management - LATERAL MOVEMENT - T1021.006 - T1021

References

1.     https://www.trendmicro.com/en_us/research/23/e/investigating-blacksuit-ransomwares-similarities-to-royal.html

2.     https://www.reuters.com/technology/cybersecurity/blacksuit-hacker-behind-cdk-global-attack-hitting-us-car-dealers-2024-06-27/

3.     https://www.sentinelone.com/anthology/blacksuit/

4.     https://thehackernews.com/2024/08/fbi-and-cisa-warn-of-blacksuit.html

5.     https://www.techtarget.com/whatis/feature/The-CDK-Global-outage-Explaining-how-it-happened

6.     https://therecord.media/japanese-media-kadokawa-investigating-cyber

7.     https://therecord.media/plasma-donation-company-cyberattack-blacksuit

8.     https://thecyberexpress.com/government-of-brazil-cyberattack-by-blacksuit/

9.     https://www.cisa.gov/news-events/cybersecurity-advisories/aa23-061a

Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Signe Zaharka
Principal Cyber Analyst

More in this series

No items found.

Blog

/

AI

/

November 17, 2026

How Microsoft and Darktrace Secure the AI-Powered Enterprise

Default blog imageDefault blog image

When legitimate activity creates business risk

AI is making information more accessible and enabling autonomous agents to act across enterprise systems. But legitimate access can still result in sensitive-data exposure, unintended actions, or activity that deviates from business expectations.

Microsoft's evolving security strategy recognizes this shift, emphasizing continuous risk assessment, stronger identity protection, and security that adapts as AI systems operate. For enterprises, the challenge is increasingly about recognizing when trusted activity introduces risk, even when existing controls are functioning as intended.

Where global intelligence meets deep business context

Microsoft brings global threat intelligence and comprehensive security capabilities, helping organizations protect identities, data, applications, and infrastructure. Its integrated approach connects security signals, governance, detection, and response across increasingly complex environments.

Darktrace complements these strengths with deep, organization-specific behavioral understanding. Powered by Adaptive AI, Darktrace continuously learns the patterns and relationships unique to each business, developing a Unique Behavioral Profile for each organization that helps distinguish meaningful threats from legitimate activity. By connecting identity, activity, context, and intent, it adds another dimension to security intelligence.

Together, Microsoft and Darktrace combine global intelligence with deeper knowledge of how each customer operates. Through supported integrations, this behavioral context enriches existing Microsoft security workflows, enabling more informed investigations and precise response.

This complementary approach extends across three interconnected areas of enterprise security- AI, People and Infrastructure. From understanding how AI and agents operate to protecting trusted communications and the infrastructure businesses depend on, Darktrace strengthens Microsoft's security capabilities with behavioral insight specific to each organization.

Understanding AI beyond permissions and policies

As AI moves into business-critical operations, security teams need to understand more than which applications and agents are approved. They need visibility into how AI is used, what information it accesses, and whether its actions remain aligned with business intent.

Microsoft provides extensive AI development, governance, and security capabilities. Darktrace / SECURE AI complements these with behavioral analysis across Shadow AI, prompts, agent identities and actions, and development risk. Policy Manager helps evaluate activity against organizational AI policies, while the announced integration with Microsoft Agent 365 is designed to enrich agent risk assessments with organization-specific behavioral signals. Together, these capabilities help organizations scale AI adoption with greater confidence.

Recognizing risk within trusted relationships

Sophisticated threats increasingly exploit established business relationships, familiar communications, and legitimate accounts. A message from a trusted supplier or an action taken through an authorized identity may appear routine until considered against the organization's normal behavior.

Darktrace / EMAIL complements Microsoft's native email, identity, and data protection capabilities by understanding how people and organizations communicate. This enables more precise detection of targeted phishing, business email compromise, account takeover, and data loss, supported by proportionate response. Integrations such as Unified Quarantine within Microsoft Defender for Office 365 bring this additional protection into existing security workflows.

Seeing the bigger picture behind an attack across domains

Threats rarely unfold within a single security domain. Suspicious identity activity, unexpected cloud connections, and unusual network behavior may appear unrelated until the relationships between them reveal a developing attack.

Darktrace / HYBRID NETWORK complements Microsoft's security capabilities with organization-specific behavioral detection across network, cloud, identity, and operational technology. Real-Time AI Analyst, including Cyber AI Analyst, connects related activity into investigated incidents that can be delivered into Microsoft Sentinel, helping security teams accelerate investigations and support targeted containment across the hybrid enterprise.

Turning security intelligence into business confidence

As AI becomes more deeply integrated into business operations, organizations need security that understands not only what technology can access, but how it behaves within their unique environment.

Microsoft and Darktrace bring complementary strengths to that challenge. By connecting global threat intelligence and integrated security capabilities with deep behavioral understanding, the partnership helps organizations recognize emerging risks, respond with greater precision, and strengthen their existing security investments.

The opportunity is to turn security intelligence into meaningful business context, enabling organizations to innovate and operate AI with confidence.

Darktrace named a 2026 Microsoft Partner of the Year Finalist for ISV Innovation

Darktrace has been named a finalist for the 2026 Microsoft Partner of the Year Award in the ISV Innovation category.  

This recognition reflects our collaboration with Microsoft to bring business context to enterprise security. By connecting Microsoft's global threat intelligence and integrated security capabilities with Darktrace's deep behavioral understanding, we help organizations recognize emerging risks and respond with greater precision across AI, People and Infrastructure.

Thank you to Microsoft, our customers, and our teams for their continued collaboration.

Meet Darktrace at Microsoft Ignite and the Microsoft Frontier Tour

Explore how Darktrace and Microsoft are bringing behavioral security to AI, people, and infrastructure.

Join Darktrace at Microsoft Ignite in San Francisco, November 17–19, or connect with our experts as we join the Microsoft Frontier Tour across 21 cities worldwide.

Meet Darktrace at Microsoft Ignite

Connect with Darktrace at the Microsoft Frontier Tour

[related-resource]

Continue reading
About the author

Blog

/

AI

/

November 13, 2026

Introducing Darktrace MCP: Connect your AI assistants to the Darktrace Behavioral Defense Platform

Default blog imageDefault blog image

The Darktrace MCP Server is now generally available to users of the Darktrace Platform Portal. It enables compatible AI assistants to query security data, retrieve Cyber AI Analyst findings, and execute supported actions across actively licensed Darktrace products. Customers can now use these capabilities in their own AI workflows to gather incident context, search telemetry, enrich investigations with information from other services, and carry out triage tasks.

What is MCP?
MCP is an open standard developed by Anthropic that lets AI systems connect to and use enterprise tools and data. Adoption of MCP servers creates an opportunity for SOC teams to move beyond isolated AI experiences toward truly operational AI workflows.

Available capabilities

The server exposes tools for three areas of security work:

  • Incident discovery and threat hunting. Retrieve model alerts and incident groups, search for relevant devices and investigate indicators of compromise. Assistants with access to other services can combine these results with external threat intelligence.
  • Investigation and analysis. Retrieve Cyber AI Analyst incident findings, examine related event data, and enrich the investigation with information from other platforms or external documentation.
  • Triage and workflow actions. Add comments, tags and statuses to alerts and assets, modify supported settings such as trusted domains and subnet details, or trigger a Cyber AI Analyst investigation.

Available capabilities depend on the licensed products connected to the server. The toolset also includes access to Secure AI prompt and shadow AI information, cloud misconfigurations and external exposure information, and Email threat trends and supported management functions.

The following examples show how the server’s discovery, investigation, and action capabilities can be combined within an AI assistant.

Check external threat indicators against your environment

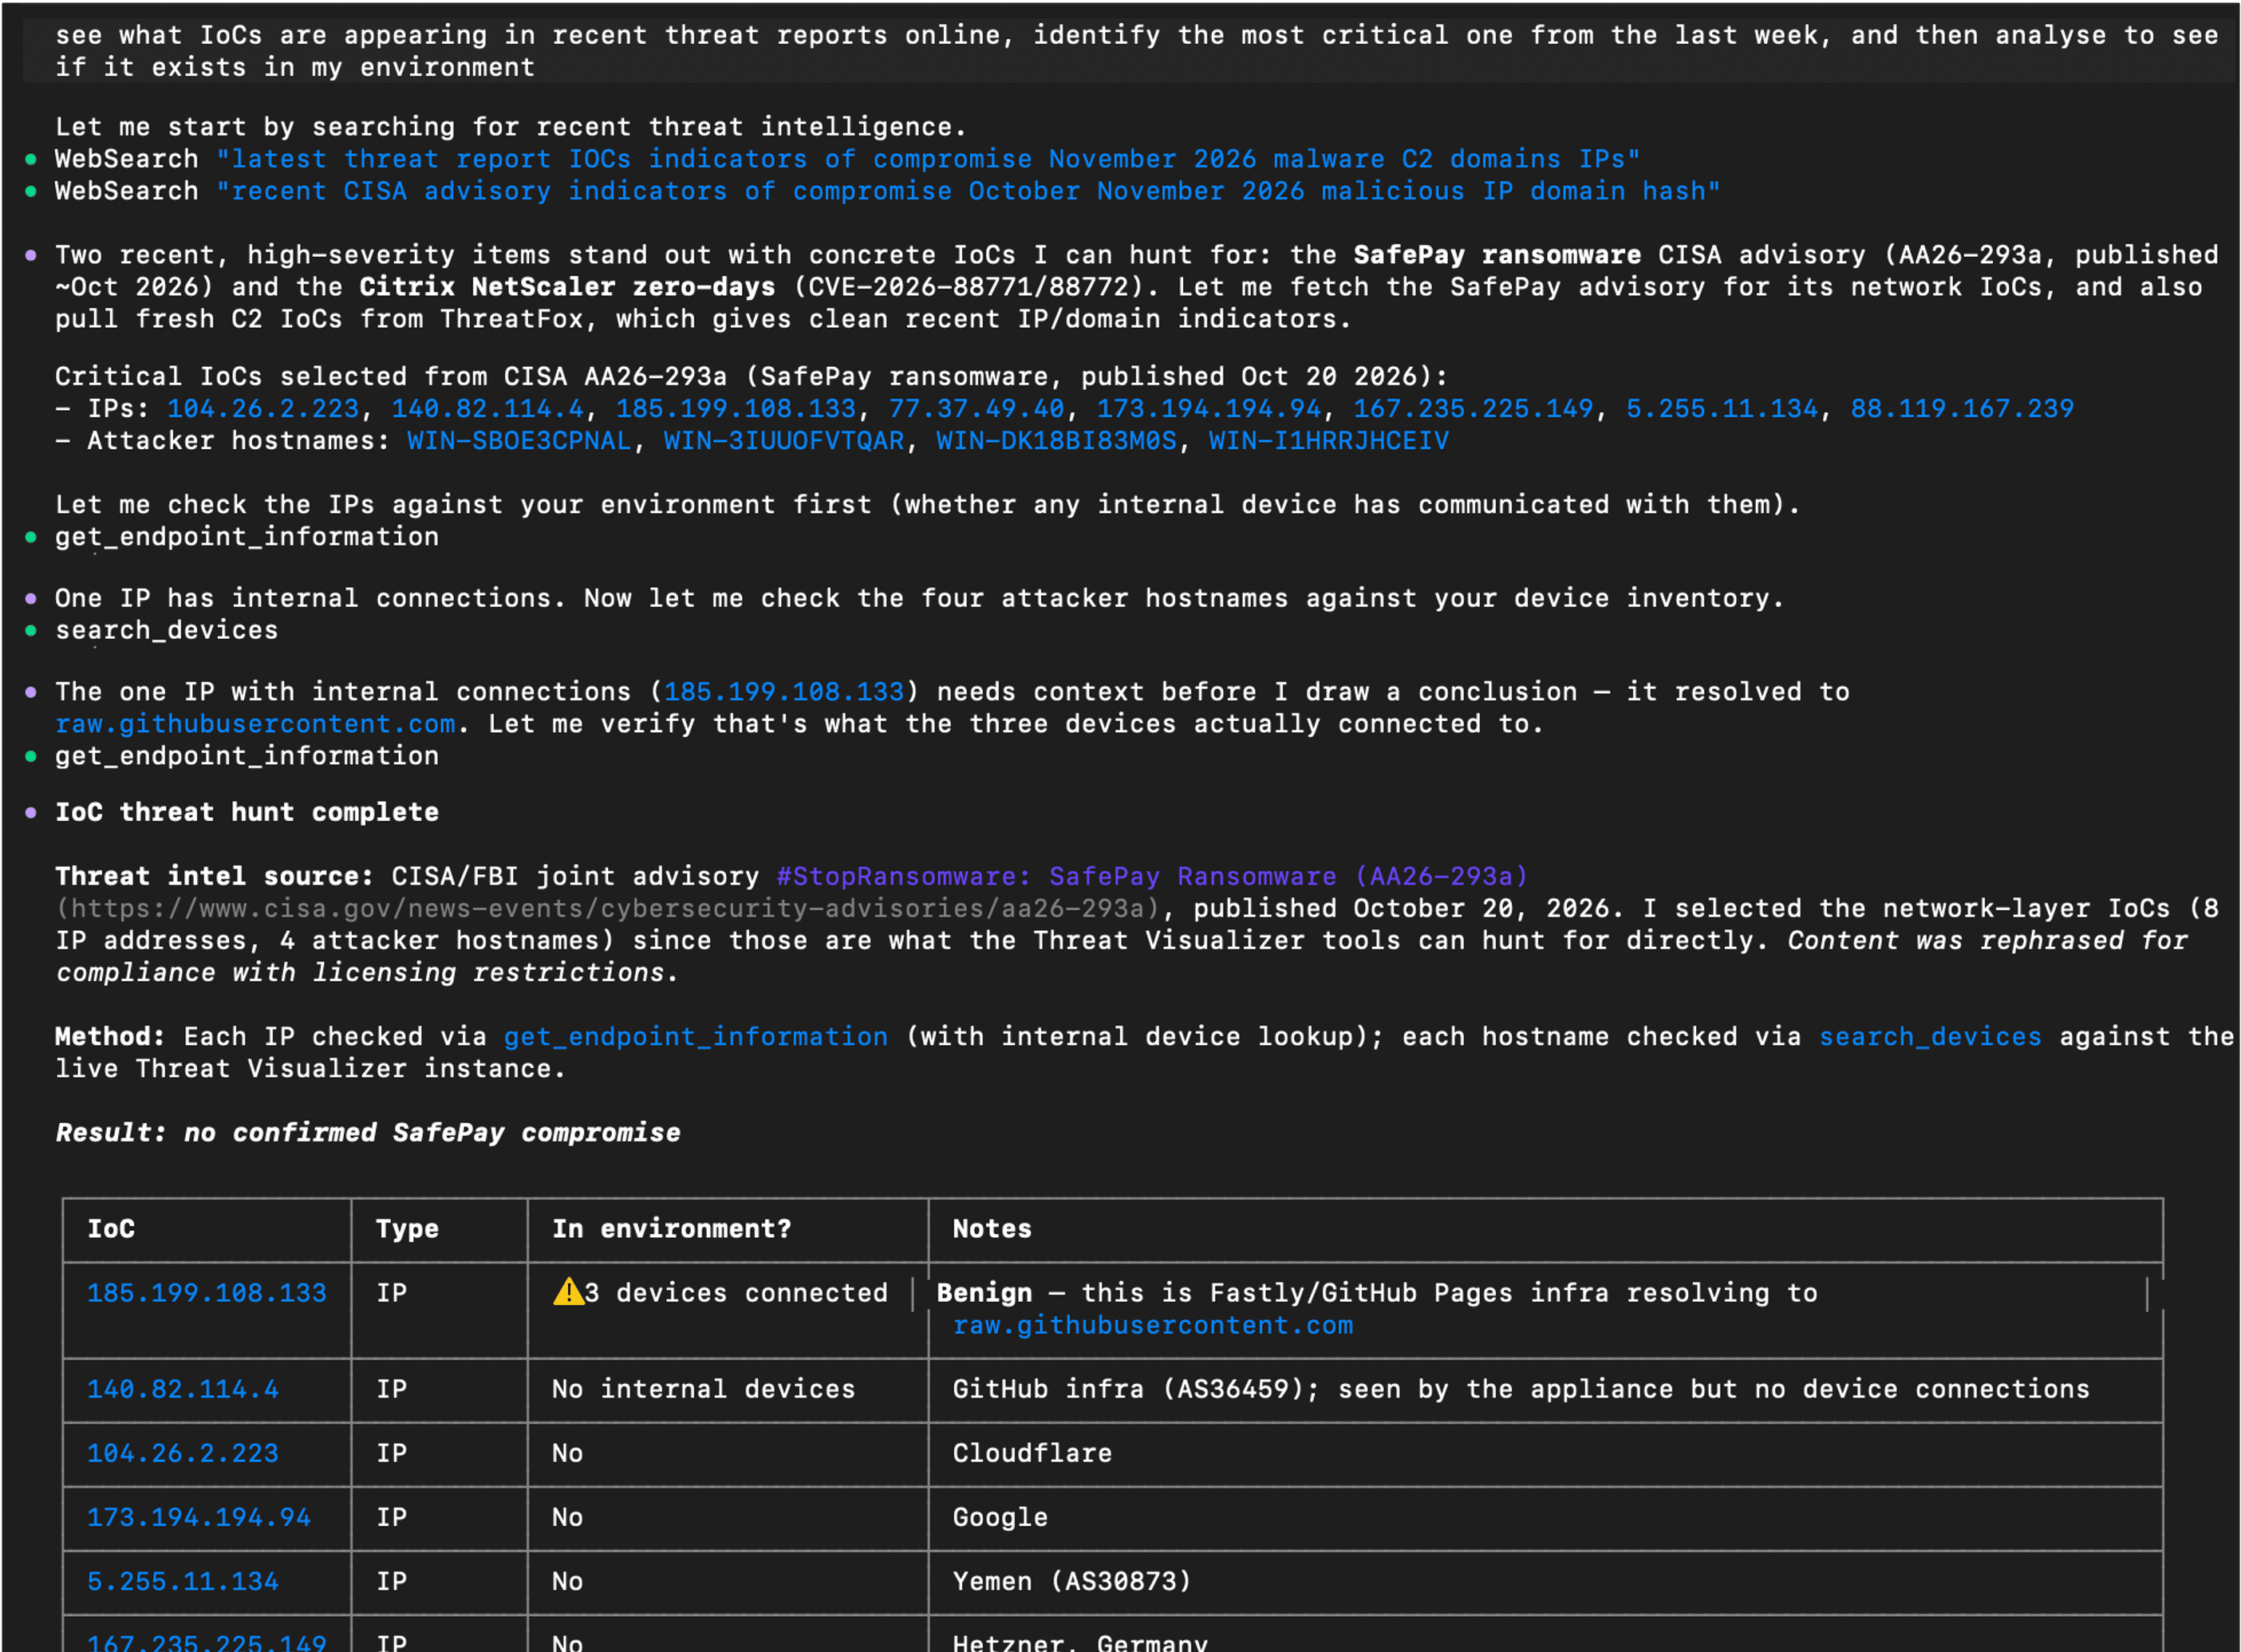
An assistant can use Darktrace MCP alongside external threat intelligence to check whether reported indicators appear in an environment. Darktrace’s tools provide device information and endpoint context; the assistant’s other tools or connected services supply the external intelligence.

In this example, the assistant searched for recent threat reports, selected indicators of compromise (IoCs) to investigate, and checked for devices that had communicated with the reported IP addresses. It then examined endpoint information to put the matches into context.

Relevant Darktrace tools: search_devices, get_endpoint_information, get_model_alerts, get_incident_events

Example prompt: “See what IoCs are appearing in recent threat reports online, identify the most critical one from the last week, and then analyze to see if it exists in my environment.”

AI assistant output using external threat intelligence alongside data retrieved through the Darktrace MCP Server.

Enrich a Cyber AI Analyst investigation

Cyber AI Analyst provides Darktrace’s incident analysis. Through MCP, an assistant can retrieve those findings, explain specific parts of an incident, and bring in related data from other services.

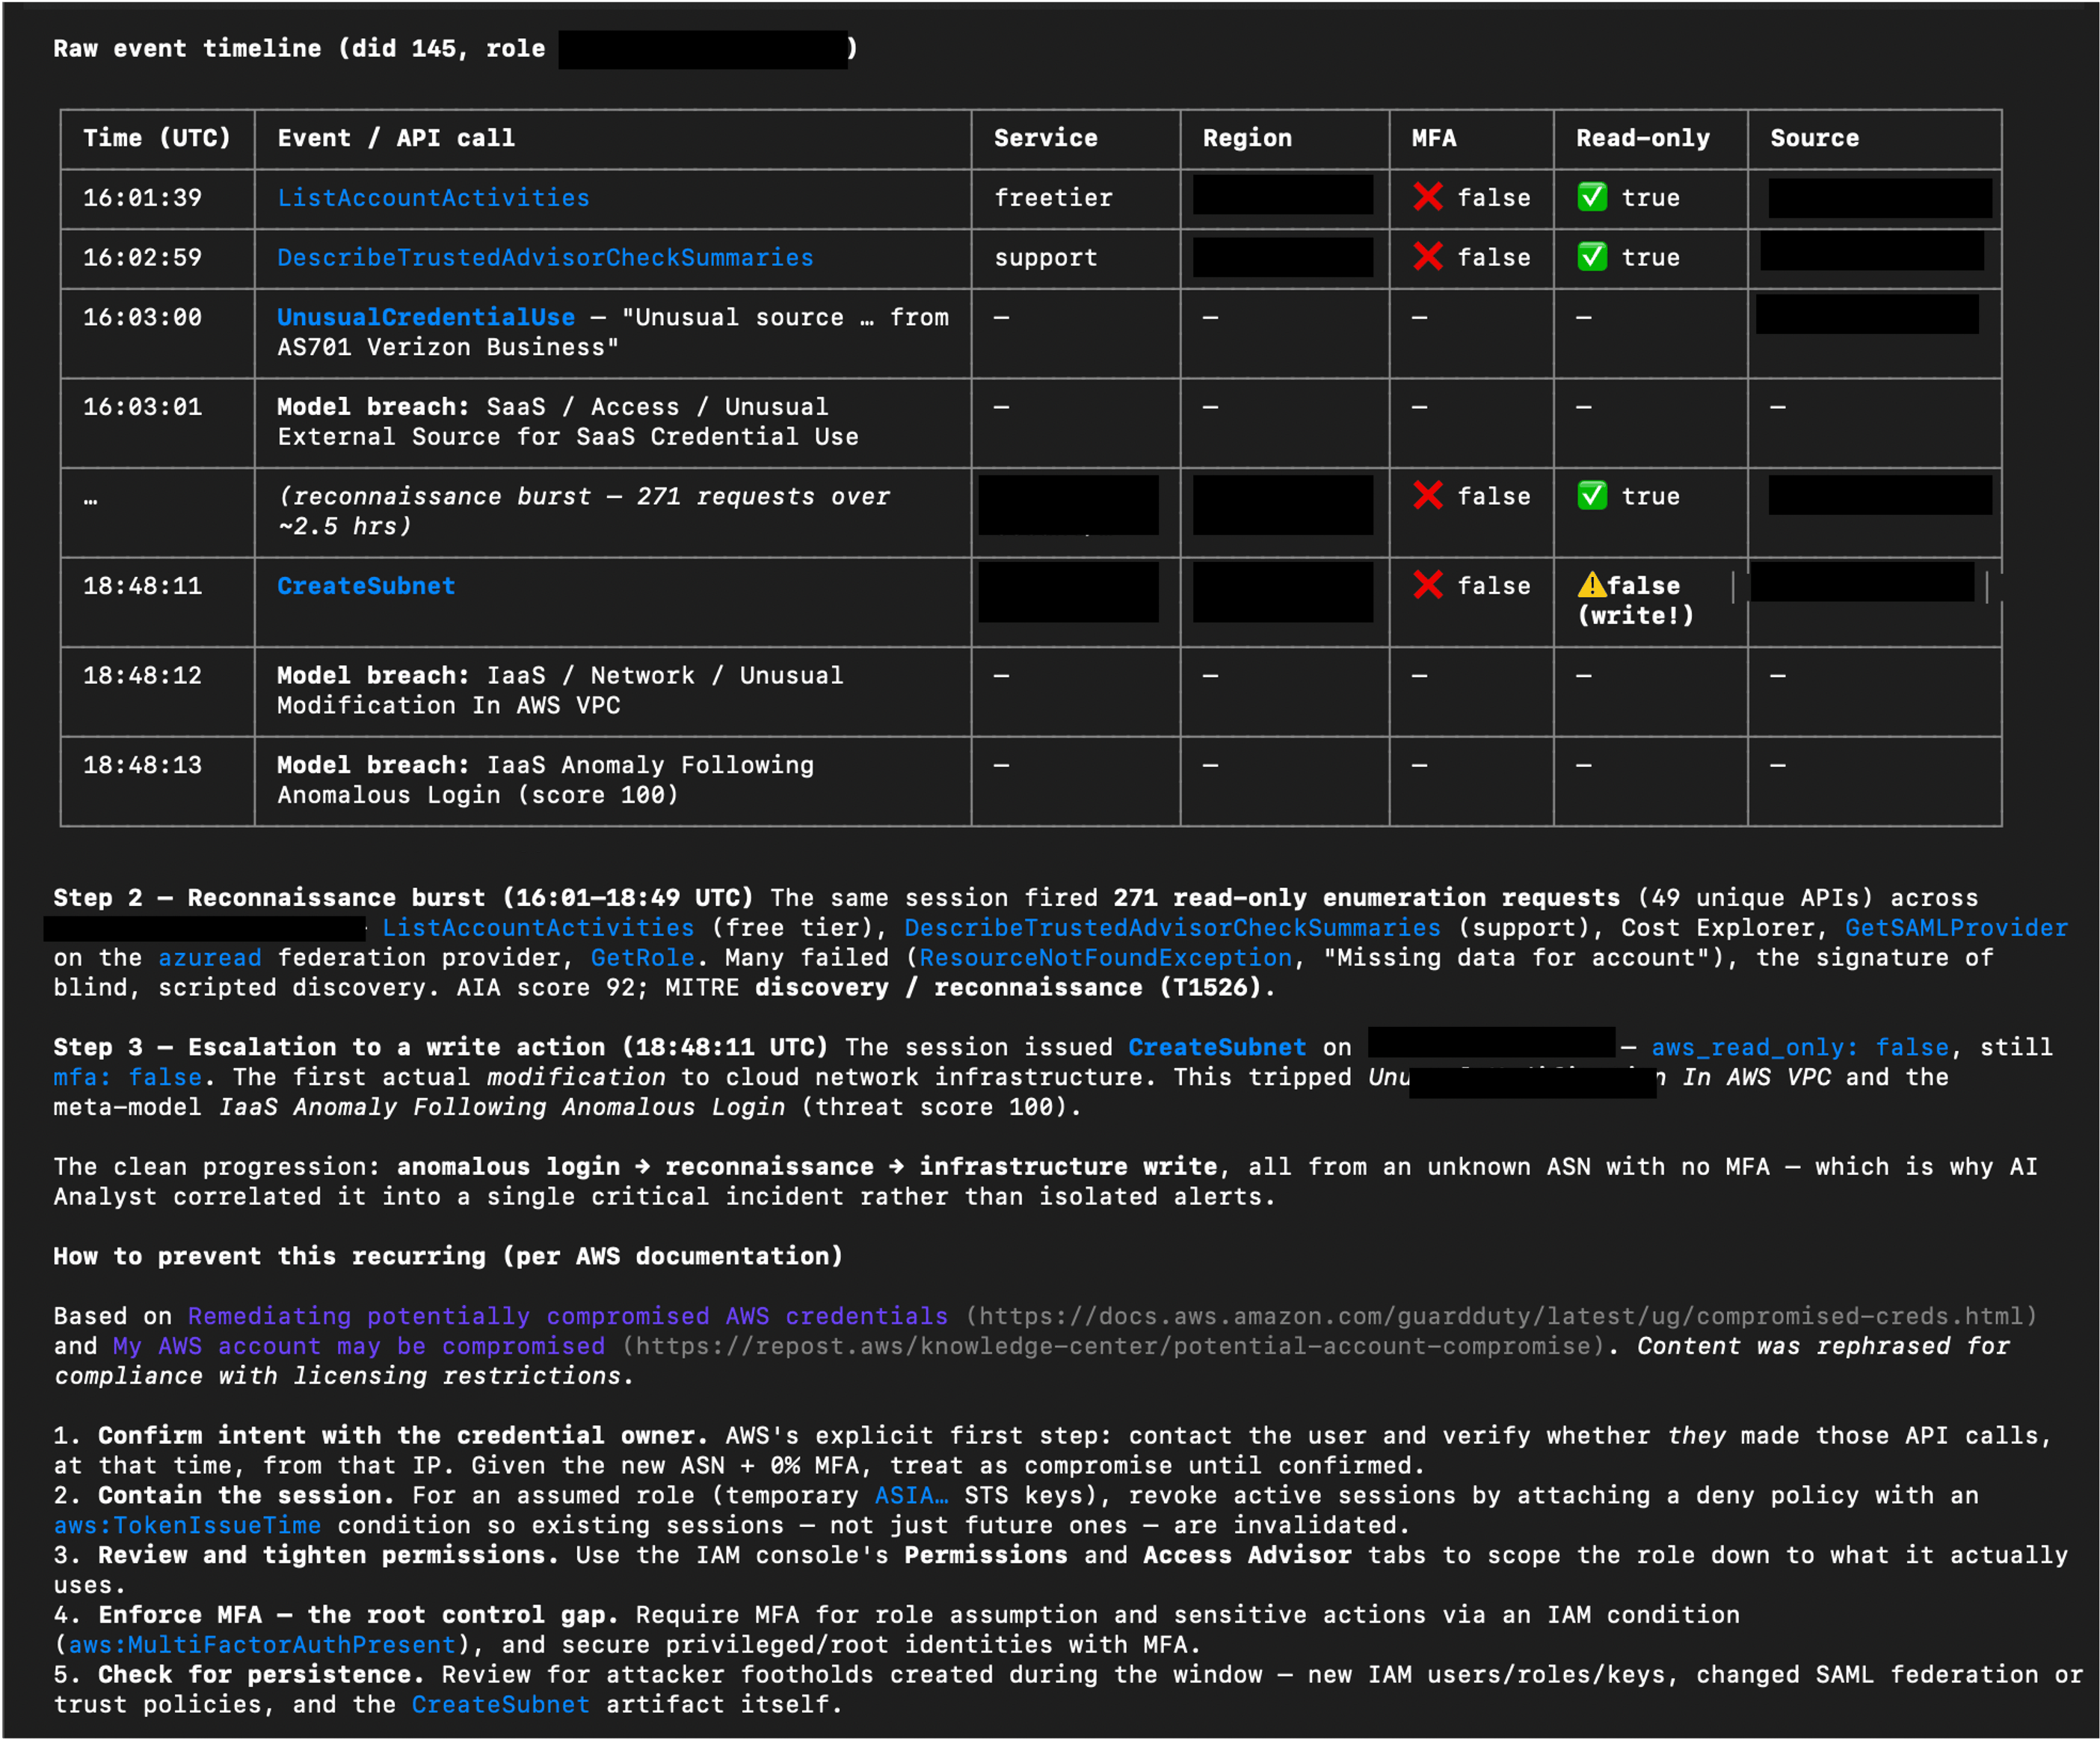
In this example, the assistant examined a Potential AWS Account Hijack investigated by Cyber AI Analyst. It assembled a step-by-step account and raw event timeline, then consulted AWS documentation to add relevant prevention guidance. The assistant brings together the existing Darktrace analysis, supporting events, and external guidance in one response.

Relevant Darktrace tools: get_incident_groups, get_incident_events, get_detailed_events, get_ai_analyst_investigations, advanced_search

Example prompt: “Drill down on the identified potential AWS account hijack. Show me a detailed step-by-step of what happened using data from Cyber AI Analyst, including a raw event timeline, and provide info on how to prevent this from happening again using info from AWS documentation.”

AI assistant output combining Cyber AI Analyst findings and event data with guidance from AWS documentation. Some sensitive content has been redacted.

Work through triage with analyst confirmation

The server’s action tools allow an assistant to support repetitive triage tasks as well as retrieve information. For example, to improve efficiency of a daily triage workflow, an analyst could ask an AI assistant to present untriaged alerts one at a time, summarizing each issue and suggesting a next step for confirmation.

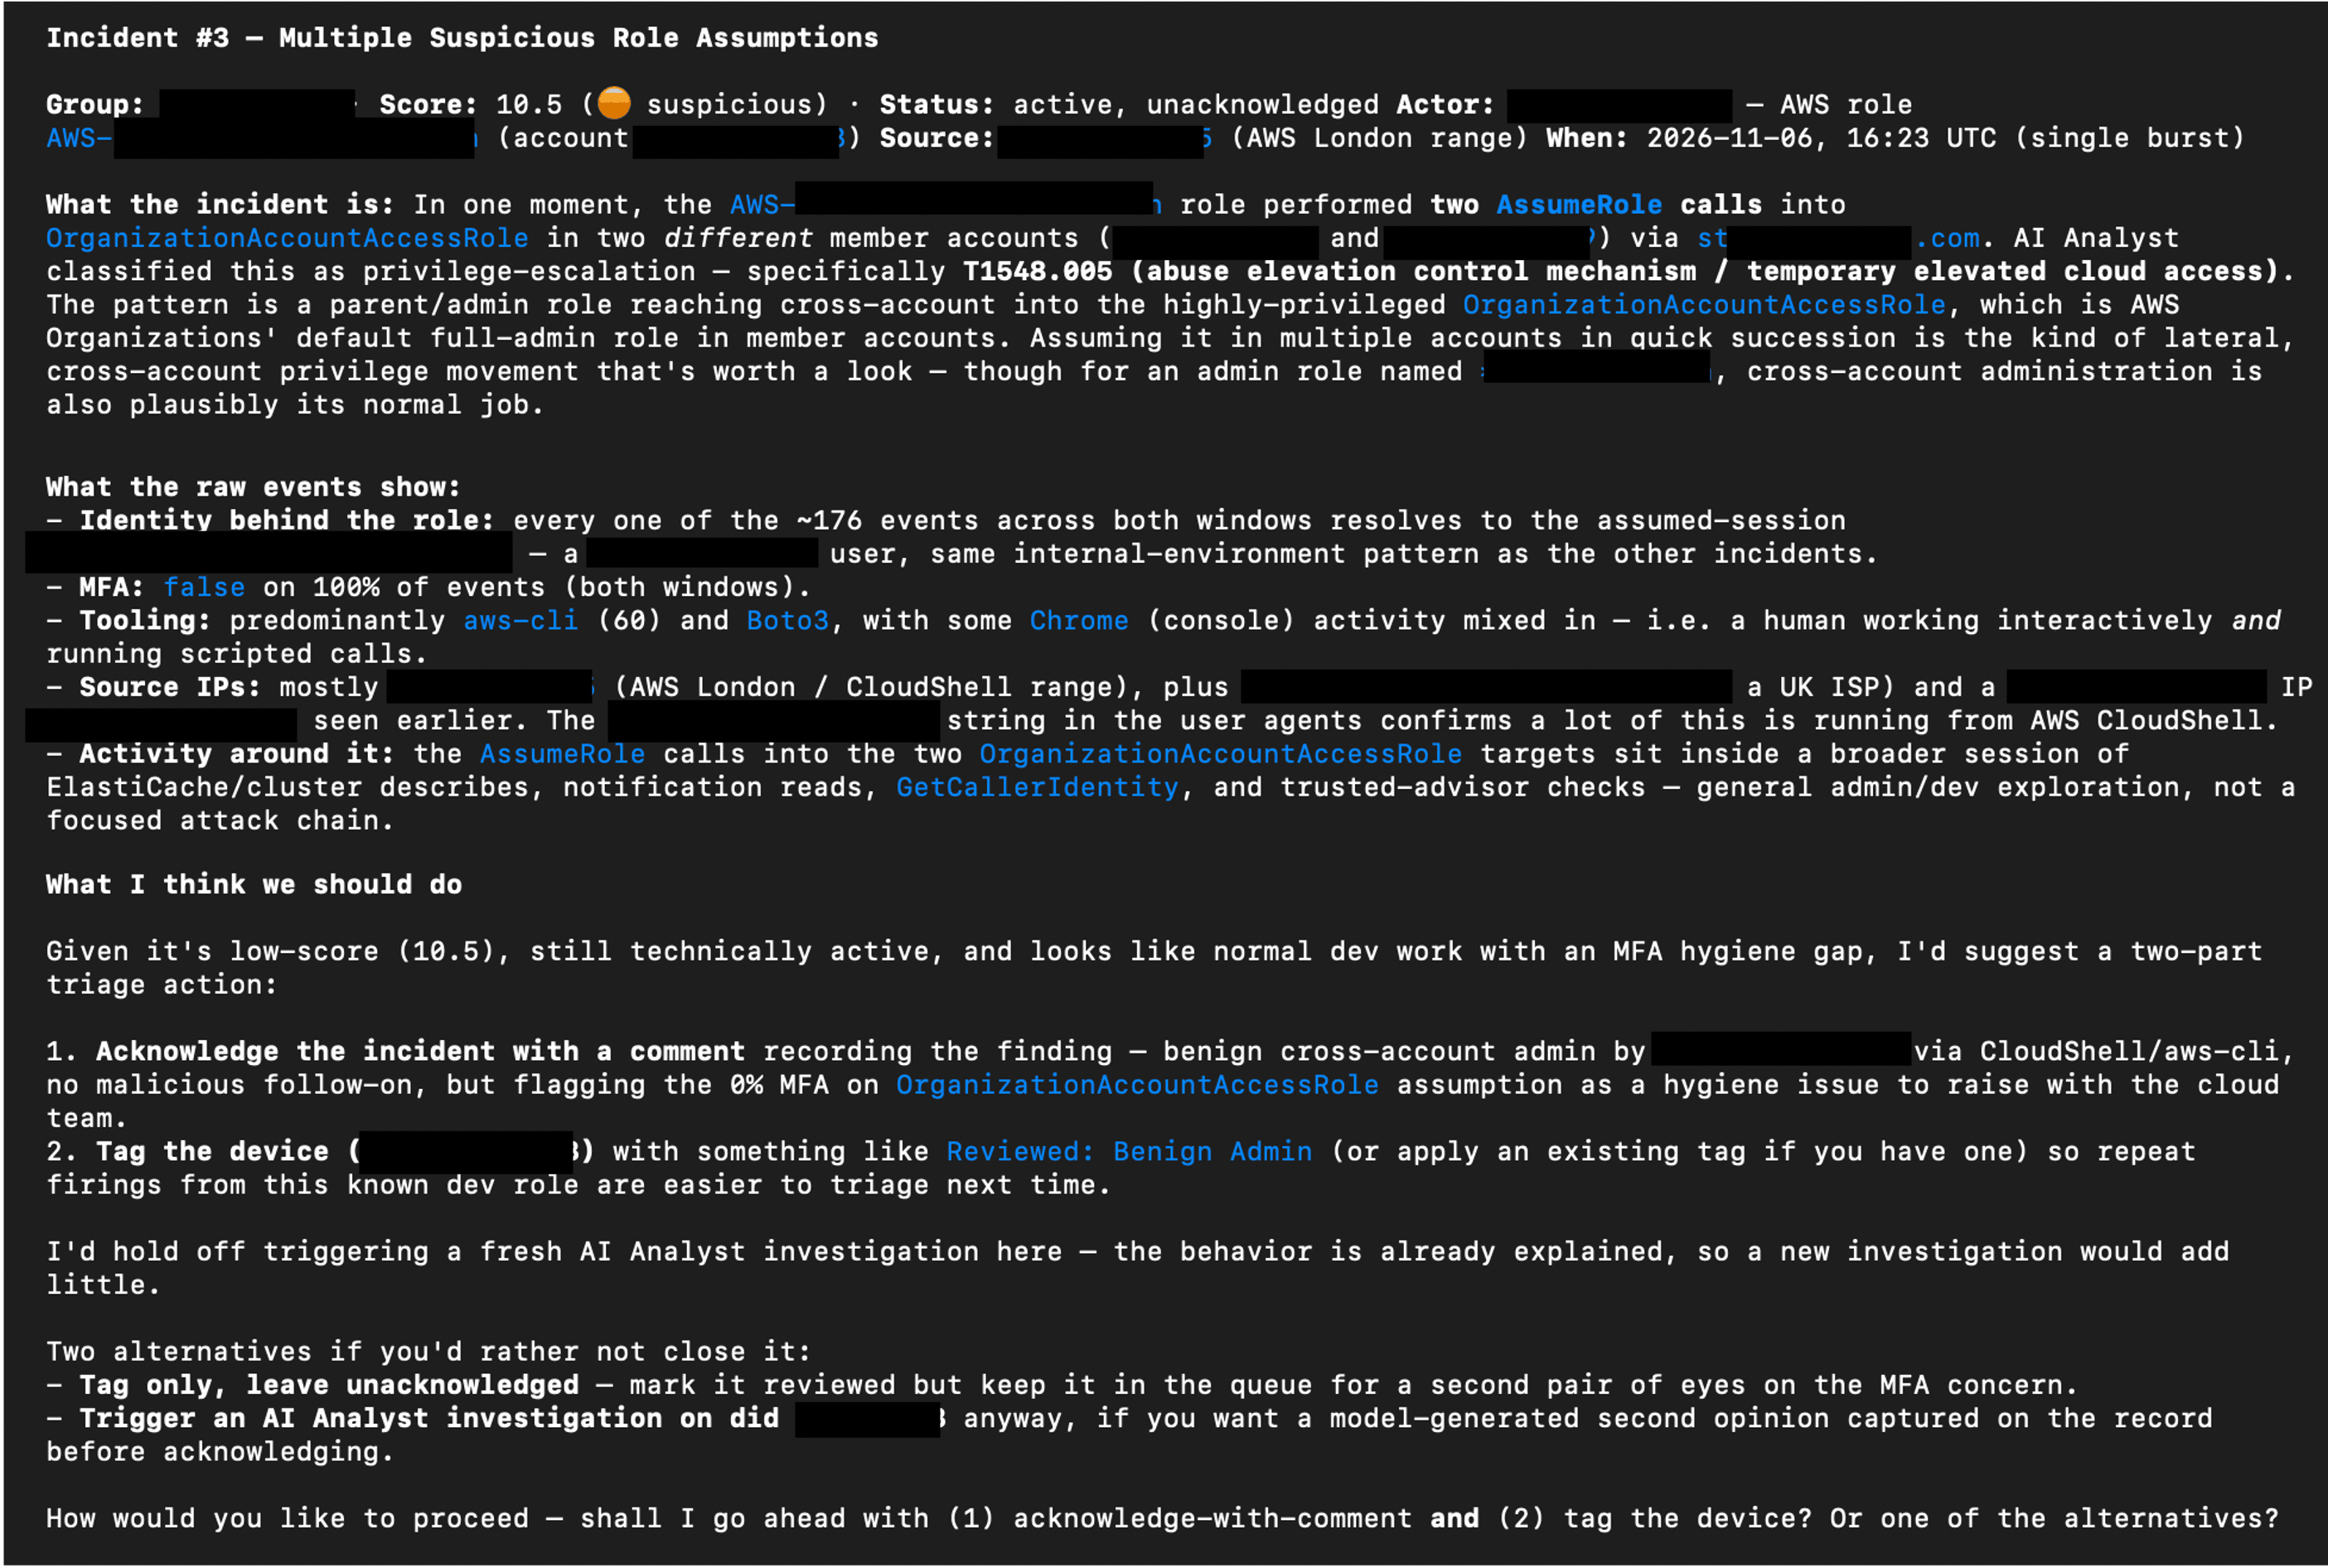
The example below shows the assistant proposing actions such as recording a finding, acknowledging an incident, tagging an asset, or triggering a Cyber AI Analyst investigation for more detail. The analyst chooses how to proceed.

Relevant Darktrace tools: get_model_alerts, update_model_alert, update_incident_group, manage_tags, create_ai_analyst_investigation

Example prompt: “Using the Darktrace MCP server, obtain all un-triaged alerts from the last 3 days and display them one at a time. Provide a summary of the issue, and a suggested triage and immediate response action. I will confirm what action should be performed.”

AI assistant output proposing triage actions using information retrieved through Darktrace MCP and asking the analyst how to proceed. Some sensitive content has been redacted.

Permissions and security considerations

The MCP server provides access to supported capabilities within the products a customer is licensed to use. Connections should follow the principle of least privilege, with access appropriate to the intended workflow.

A read-only connection mode is also available for workflows that do not require changes. This mode hides tools that mutate data; configuration details are provided in the Product Guide.

Some tools can change data or perform actions, including adding or removing asset tags, triggering Cyber AI Analyst investigations, and acting on assets. Consider which capabilities an assistant should be able to use before connecting it and retain human oversight of actions that could cause disruption or unwanted changes.

For further guidance, see:

Seven MCP risks CISOs should consider and how to prepare

Anthropic’s MCP Security Best Practices

Use the interface that suits the task

MCP gives customers another way to work with Darktrace alongside its product interfaces. Users may find that complex investigations requiring visual analysis, or strategic decisions involving impactful actions, are better suited to the graphical interfaces within Darktrace products. They can choose the approach that fits their workflow.

How to start using the Darktrace MCP Server

The Darktrace MCP Server is used to connect a compatible AI assistant to supported tools within your Darktrace deployment. The assistant can retrieve alerts and device information, draw on Cyber AI Analyst findings, and perform permitted actions across your licensed products.

To get started, you will need access to the Darktrace Platform Portal and a compatible AI assistant. Follow the Platform Portal MCP Server guide to find out how to create the required credentials and configure the connection today.

Contact a Darktrace representative to explore how the Darktrace MCP Server can support your security operations.

To learn more about Darktrace can help protect your MCP servers within your broader AI and agent use, discover Darktrace / SECURE AI.

‍

Appendix: Darktrace MCP available tools

The following tool catalogue reflects the list supplied for this announcement. Available tools depend on the connected products and access. The list may change as tools are added or removed.

ToolProductDescription
get_helpGeneral / MCP ServerReturns orientation info about the Darktrace MCP server: its purpose, tool categories, and documentation.
get_productsGeneral / MCP ServerLists available Darktrace product instances and their instance_id values needed by other tools.
submit_feedbackGeneral / MCP ServerLogs feedback about tool coverage, clarity, or usability for the Darktrace team.
count_devicesThreat VisualizerReturns the total count of devices/assets managed by Darktrace.
search_devicesThreat VisualizerSearches for devices by keyword and returns basic matching device details.
query_devicesThreat VisualizerQueries comprehensive device information using filters like IP, MAC, subnet, or SaaS module.
edit_deviceThreat VisualizerUpdates a device's label, type, priority, or notes.
get_device_activityThreat VisualizerReturns aggregated time-series data of a device's connection/data volume trends over 4 weeks.
get_detailed_eventsThreat VisualizerRetrieves individual low-level events (connections, notices, model breaches, processes) for a device or alert.
get_subnetsThreat VisualizerRetrieves monitored subnets with CIDR, device counts, DHCP status, and traffic stats.
update_subnetThreat VisualizerEdits subnet details such as label, network range, coordinates, and DHCP/exclusion flags.
get_model_alertsThreat VisualizerRetrieves model alerts (breaches) with model info, device details, and triggered components.
get_model_alert_credentialsThreat VisualizerReturns credentials seen on the device that triggered a given model alert.
update_model_alertThreat VisualizerComments on and/or acknowledges a model alert.
get_modelsThreat VisualizerRetrieves detection models with their logic, actions, and configuration.
get_incident_groupsThreat VisualizerRetrieves AI Analyst incident groups with scores, MITRE tactics, devices, and summaries.
get_incident_eventsThreat VisualizerRetrieves AI Analyst incident events with AI summaries, MITRE tactics, and breach details.
update_incident_groupThreat VisualizerComments on and/or acknowledges an AI Analyst incident group.
create_ai_analyst_investigationThreat VisualizerCreates a manual AI Analyst investigation for a device around a specified time.
get_ai_analyst_investigationsThreat VisualizerRetrieves the status and results of manual AI Analyst investigations.
advanced_searchThreat VisualizerExecutes a Lucene-syntax Advanced Search query against Darktrace log data.
get_advanced_search_syntaxThreat VisualizerReturns the full Advanced Search query syntax reference (must be called before querying).
get_response_actions_summaryThreat VisualizerReturns a summary of active and pending Autonomous Response actions and action counts over a time range.
get_endpoint_informationThreat VisualizerLooks up external endpoints (IPs/hostnames) for location, reputation, and connection history.
get_cvesThreat VisualizerRetrieves CVEs detected across assets with severity, scores, and affected devices.
get_system_healthThreat VisualizerReturns comprehensive system health metrics (CPU, memory, disk, licenses, bandwidth).
get_dam_alertsThreat VisualizerRetrieves health alerts from the Darktrace Alert Management system.
get_module_statusesThreat VisualizerRetrieves the status of Darktrace modules, optionally filtered to failing ones.
get_tagsThreat VisualizerRetrieves device tags and optionally the devices/credentials they are applied to.
manage_tagsThreat VisualizerCreates, deletes, applies, or removes tags on devices or credentials.
get_trusted_domainsThreat VisualizerRetrieves domains marked as trusted.
manage_trusted_domainsThreat VisualizerAdds or removes a trusted domain entry.
get_watched_domainsThreat VisualizerRetrieves watched domains monitored for suspicious activity.
manage_watched_domainsThreat VisualizerAdds or removes watched domain entries.
get_workflow_integration_ticketsThreat VisualizerRetrieves third-party platform tickets created by Workflow Integrations for Darktrace events.
get_cloud_accountsDarktrace / HYBRID NETWORKRetrieves cloud deployment accounts and their monitoring/compliance statuses.
get_cloud_architecturesDarktrace / HYBRID NETWORKRetrieves cloud architectures with risk breakdown, cost, and asset counts.
get_cloud_assetsDarktrace / HYBRID NETWORKRetrieves cloud assets with type, service, region, and attached/associated assets.
get_cloud_asset_filtersDarktrace / HYBRID NETWORKReturns available filter fields and operators for querying cloud assets.
get_cloud_misconfiguration_alertsDarktrace / HYBRID NETWORKRetrieves cloud security misconfiguration alerts grouped by rule.
get_cloud_misconfigured_assetsDarktrace / HYBRID NETWORKRetrieves the assets affected by a specific cloud misconfiguration rule.
get_cloud_rule_informationDarktrace / HYBRID NETWORKReturns detailed rationale, remediation, and compliance mappings for a cloud security rule.
get_emailDarktrace / EMAILRetrieves detailed information about a specific email by UUID.
search_emailsDarktrace / EMAILSearches for emails using filters and a time range.
get_email_search_filtersDarktrace / EMAILReturns available email search filter definitions and values.
action_emailDarktrace / EMAILPerforms an action (hold, release, approve/reject release) on an email for specific recipients.
analyse_email_linkDarktrace / EMAILAnalyzes a URL found in an email, returning classification tags and analysis metrics.
get_email_overviewDarktrace / EMAILReturns an aggregated email dashboard overview (threats, actions, campaigns, etc.).
get_email_listsDarktrace / EMAILRetrieves email lists and their entries.
manage_email_listsDarktrace / EMAILAdds or edits email lists, and adds or removes entries within an email list.
get_email_addin_recordsDarktrace / EMAILRetrieves Inbox Analysis or Misdirected Email add-in records.
get_email_audit_logsDarktrace / EMAILRetrieves EMAIL system audit log events for a time range.
get_email_audit_log_event_typesDarktrace / EMAILReturns available audit log event types for filtering.
get_secure_ai_overviewDarktrace / SECURE AIReturns a dashboard overview of Secure AI activity (anomaly scores, sessions, prompt categories).
get_secure_ai_sessionsDarktrace / SECURE AIRetrieves monitored generative-AI sessions with risk levels and anomaly scores.
get_secure_ai_promptsDarktrace / SECURE AIRetrieves individual prompts for a Secure AI session with anomaly/risk classifications.
get_secure_ai_usersDarktrace / SECURE AIRetrieves users interacting with generative-AI apps, with risk scores and session counts.
get_secure_ai_eventsDarktrace / SECURE AIRetrieves raw events ingested by the Secure AI post-handler.
get_secure_ai_detectionsDarktrace / SECURE AIRetrieves detections raised by Secure AI models with scores and OWASP/ATLAS mappings.
get_secure_ai_response_actionsDarktrace / SECURE AIRetrieves Autonomous Response actions taken by Secure AI.
manage_secure_ai_response_actionDarktrace / SECURE AIClears, confirms, extends, or reactivates a Secure AI response action.
get_shadow_ai_dashboardDarktrace / SECURE AIReturns the Shadow AI dashboard of unsanctioned AI/LLM services detected.
get_shadow_ai_detectionsDarktrace / SECURE AIRetrieves individual Shadow AI detections for unsanctioned AI/LLM service usage.
get_forensic_investigationsDarktrace / HYBRID NETWORKRetrieves forensic investigations with status, alarm counts, and AI summaries.
get_forensic_evidencesDarktrace / HYBRID NETWORKRetrieves evidence items with alarm counts, OS details, and processing status.
get_forensic_evidence_fileDarktrace / HYBRID NETWORKReturns detailed file metadata/content (hash, strings, VirusTotal, AI description) from an evidence item.
browse_forensic_evidence_filesDarktrace / HYBRID NETWORKBrowses the filesystem of a forensic evidence item, filtering by severity, path, or name.
get_forensic_alarmsDarktrace / HYBRID NETWORKRetrieves alarms from an investigation or evidence item with severity and MITRE techniques.
get_forensic_artifactsDarktrace / HYBRID NETWORKRetrieves detection artifacts (files, hashes, processes, users, IPs, domains) from an investigation.
get_forensic_detectionsDarktrace / HYBRID NETWORKRetrieves XDR/EDR detections with MITRE ATT&CK mappings.
get_forensic_indicatorsDarktrace / HYBRID NETWORKRetrieves indicators of compromise (IOCs) from an investigation.
get_forensic_vulnerabilitiesDarktrace / HYBRID NETWORKRetrieves vulnerabilities (CVEs) with CVSS scoring and package info.
get_forensic_pipelinesDarktrace / HYBRID NETWORKRetrieves processing/acquisition pipelines with real-time status.
get_forensic_timelineDarktrace / HYBRID NETWORKRetrieves or facets timeline events from a forensic investigation.
get_forensic_search_syntaxDarktrace / HYBRID NETWORKReturns the Forensic Search query syntax reference (call before forensic timeline queries).

[related-resource]

Continue reading
About the author
Jamie Bali
Technical Author (AI) Developer
Your data. Our AI.
Elevate your network security with Darktrace AI