Blog
/
/
December 7, 2017

Darktrace: Investigating Widespread Trojan Infections

Discover how Darktrace expedites the investigation of widespread Trojan infections, enhancing cybersecurity and response times.
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Max Heinemeyer
Global Field CISO
Default blog image
07
Dec 2017

This blog post outlines how Darktrace helps security operations centre (SOC) teams become more efficient by drastically cutting down the time needed to investigate incidents. This is illustrated by an example encountered in a recent Proof of Value where over 350 client devices had been infected by a stealthy banking trojan.

Identifying and investigating a compromise of this size would usually take a SOC team several hours if not days using disparate traditional security tools. Employing Darktrace, the most important questions were answered within 90 minutes. The main reason for this is that Darktrace provides full visibility and context into network activity for all devices monitored on a single, unified platform.

Alert fatigue & the cyber security skill gap

Getting cyber security right is difficult and time-consuming. Complexity is one of the main challenges the cyber security community is facing. These days, networks are only vaguely defined with digital supply chains, outsourcing, the push into the cloud and the advent of micro-virtualisation like Docker. The amount of data stored, devices connected to internal networks, connections made by devices and the heterogeneity in IT adds to this complexity. Managing it is difficult at best and securing it with traditional tools can be a daunting task.

Our industry is struggling with what has been labelled the ‘cyber security skill gap’. The demand for skilled, experienced security practitioners consistently outstrips supply. SOC teams struggle to find the right people for the job and to keep their analysts motivated in the face of a rapidly evolving threat landscape. Alert fatigue and burnout are common symptoms for SOC analysts working long hours and graveyard shifts.

Investigation methodology

Any incident responder will always begin by asking some high-level questions concerning the incident under investigation – regardless of it being an adware infection, a banking trojan, ransomware, an active intrusion or any other form of cyber security incident.

The most important questions usually are:

  • How did the infection occur? (To prevent the same initial infection vector in the future)
  • What behavior is the infected device exhibiting? (To understand the threat and the risk of the infection)
  • What Indicators of Compromise (IoC) are seen? (To update other security tools and to use for further investigation)
  • Are other devices infected as well? (To assess the extent of the infection)

We did a recent Proof of Value with an IT service provider in EMEA. Darktrace entered an environment which had already succumbed to a widespread compromise – over 350 client devices had been infected with banking trojans. Let’s walk through how we identified, triaged and investigated this infection using Darktrace.

Identifying the incident

Darktrace came into the environment after the initial infection had taken place already. Darktrace instantly identified several devices exhibiting unexpected HTTP beaconing to unusual, rare external IP addresses. The devices made HTTP POST requests without prior GET requests along other suspicious behavior. Darktrace created several high-severity alerts for this, e.g. ‘Compromise / Suspicious HTTP Beacons to Dotted Quad’ and ‘Compromise / Possible Malware HTTP Comms’:
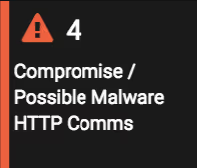
Figure 1: Example Darktrace alert.

Triaging the incident

Darktrace then provides context around this alert - e.g. the external IP the beaconing was made to, the internal device including the associated user, and the suspicious behavior:
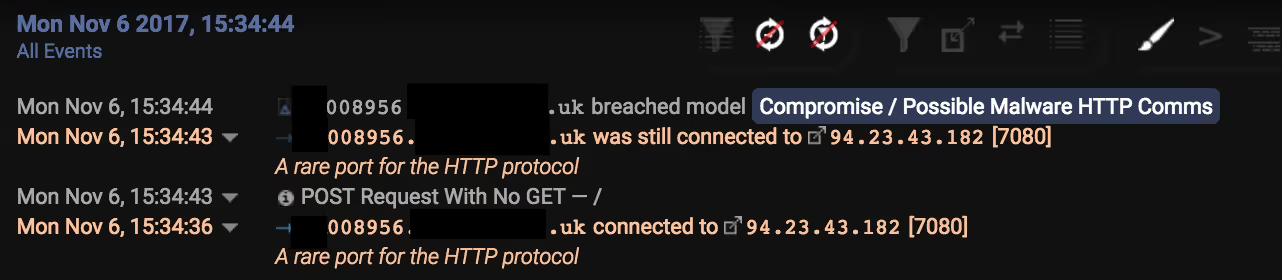
Figure 2: Detection context and C2 IP.

A quick investigation of the external IP reveals that it is a recently discovered command and control (C2) IP address for the Dridex banking trojan.

Drilling deeper into this, Darktrace provides PCAPs for every connection seen. A PCAP for the C2 connection above confirms this incident as active, successful, encoded beaconing to a malicious C2 IP:
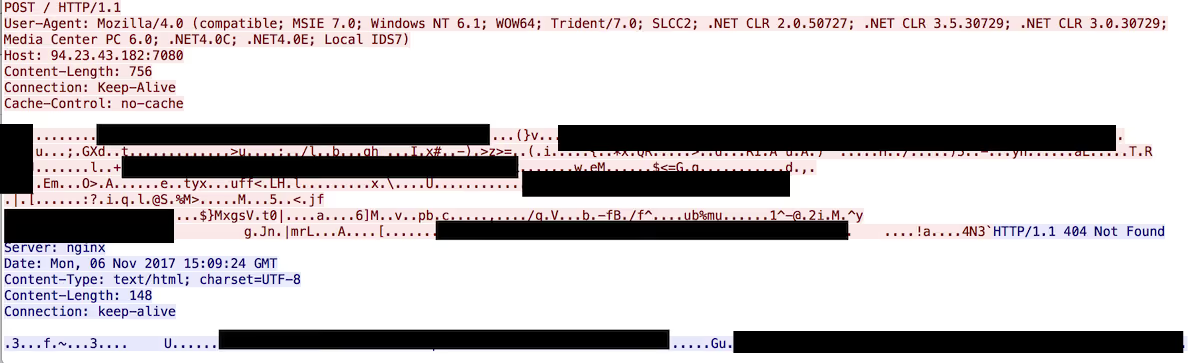
Figure 3: PCAP and encoded HTTP POSTs.

Investigating the incident

At this stage, we want to further examine the behavior of the infected device around the time of the incident. Darktrace provides full visibility into past activity, including all network connection made by any device - regardless of whether the incident occurred on the device or not.

We attend to all external connections made by the infected device around the time of the incident and immediately identify more suspicious C2 communication:
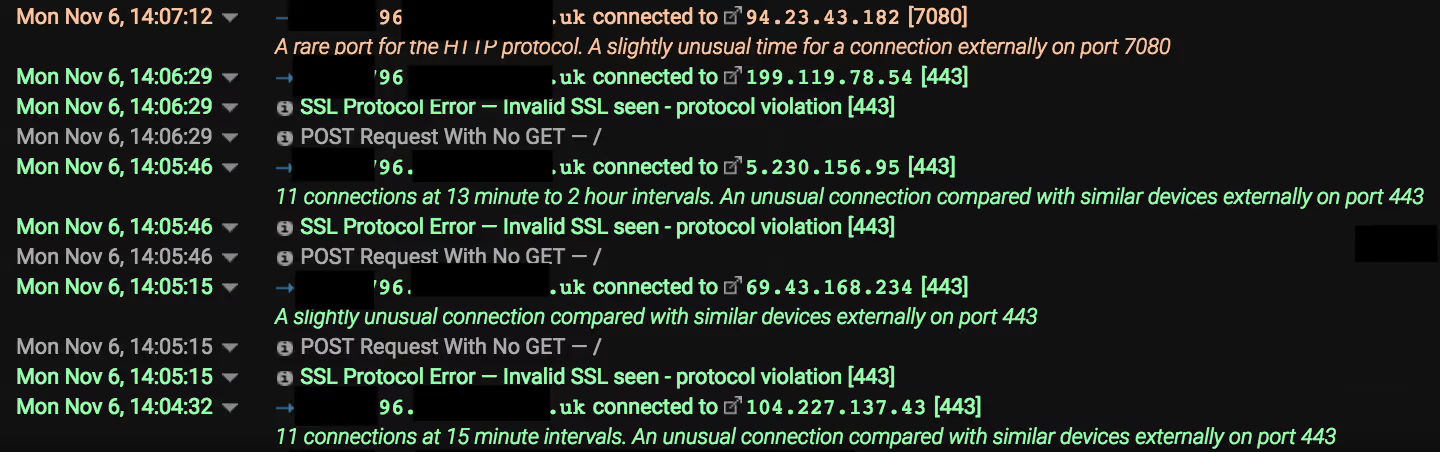
Figure 4: More device behavior; further C2 IPs.

By now we have identified 6 different C2 IP addresses.

We can use Darktrace’s ‘External Sites Summary’ to view all devices that have connected to a specific IP or domain in the recent past. Doing this for the initial C2 IP yields the following result (excerpt):
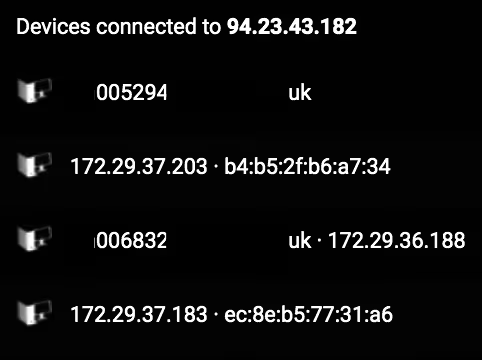
Figure 5: External Sites Summary; further infections.

We immediately identify 5 additional devices that made successful connections to the C2 IP address. In fact, the list above is abridged as we actually saw over 350 devices connecting to this and other C2 IP addresses. Notably, all observed devices appear to have a similar naming structure - this will become important in the next part of the analysis.

At this point we have answered all but the first question: ‘How did the infection occur?’

Darktrace started monitoring the network after the initial infection occurred and spread. Further research into the C2 IP addresses shows that they are associated with the Emotet trojan. This sophisticated malware often precedes banking trojan (e.g. Dridex) infections and is spread via phishing. We can thus assume that phishing was a likely initial infection vector.

How then did the infection manage to spread to so many devices?

Surely not all users clicked on suspicious phishing emails? Recent versions of Emotet have limited lateral movement capabilities. They mainly propagate via SMB brute forcing - trying administrative accounts and hard-coded password lists. The naming convention on the infected devices is very similar - this could indicate a similar build-process and setup of the devices. If a vulnerability - such as an administrative account with a weak password - existed on one of the devices, it might be present in all of the devices with a similar build.

Using Darktrace, the security team has now a solid understanding of the nature and size of the infection, the IoCs available to update firewalls and other preventive security controls and outstanding remediation-activities.

What would this investigation look like with traditional tools, not using Darktrace?

Detecting these covert banking trojans in the first place, let alone triaging them fully, can be a difficult challenge in itself. Current banking Trojan strains such as Dridex, Fedeo or Vawtrak keep updating the malware with new C2 addresses to avoid blacklisting. Initial detection could be at any stage of the attack lifecycle – likely it will be in the latter stages though, when considerable damage has already been done.

An analyst will have to log into various security devices to get close to the same level of visibility provided in Darktrace – web proxy logs, anti-virus logs, running PCAPs on infected hosts, SIEM logs. Having to switch between all those disparate security tools is not time-efficient and produces a fragmentary picture of what actually transpired.

Conclusion

A working hypothesis is that a single device was initially infected via phishing, allowing Emotet to spread to over 350 internal devices via SMB brute forcing. It took no longer than 90 minutes to come from an initial detection of the incident to this conclusion, which forms the basis for an actionable report.

The last thing a SOC needs is yet another tool producing a profusion of alerts. Using Darktrace’s machine learning and unrivalled network visibility, you can focus on the small set of relevant alerts and rapidly investigate those incidents according to their severity and priority.

Darktrace can reduce costs even if you bring in a third-party incident response team. You will be able to significantly speed up their ongoing investigation if they have access to Darktrace. Third-party incident response teams are expensive – their daily rates ranging between £2,000 and £3,000 per day. Cutting their work down from days to hours will result in cost and efforts saved.

Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Max Heinemeyer
Global Field CISO

More in this series

No items found.

Blog

/

AI

/

November 19, 2026

Microsoft Perception, Agentic Insiders and the Role of Behavioral Security

Default blog imageDefault blog image

This week at Ignite, Microsoft announced that Microsoft Perception is generally available. It is a significant milestone for the industry, and one we welcome as a Microsoft partner. Microsoft is putting an architectural bet at the center of its security strategy: AI has changed the speed of cyber, and defense must change with it.

At Darktrace, we’ve long held the same view, so it’s encouraging to see a partner of Microsoft’s scale articulate it so clearly and bring it to market.

Security gets a team of agents

Perception is Microsoft’s agentic security system. It orchestrates red, blue, and green team agents through playbooks in a closed loop: red agents simulate attacks, blue agents detect, triage and investigate, and green agents fix and remediate. Rather than adding another assistant to the SOC, it creates coordinated teams of agents that share context. Security teams set the guardrails and approve high-impact actions.

Microsoft frames this as a three-layer cyber stack: signals, sensors and actuators; a context layer; and agents, harness and models on top. Together with partner sources, the foundation produces more than 165 trillion signals per day.  

The announcement also makes a second point that matters just as much. Microsoft is treating AI agents themselves as a new insider-risk category. In its words, “Agents are the new insiders.” They work at machine speed, around the clock, with broad access to data, apps, tools and other agents, and like any insider they can make mistakes, be manipulated or be compromised. New capabilities such as Dynamic Agent Risk (now in preview) and dynamic Conditional Access controls are designed to assess and contain that risk as it changes.

Four truths about security in the agentic era

The announcement is built on four ideas, and together they describe the new reality security teams are defending:

  1. Static security can’t keep up. Microsoft validates what many security practitioners have observed; the window between a vulnerability’s discovery and its exploitation is collapsing from months to minutes. Manual triage can’t answer that pace. Autonomous detection and response is now a requirement, not simply a “nice to have”.
  2. Agents must be treated as insiders. The question for security teams is no longer only “who is this user?” but “what is this agent actually doing?” Identity tells you who an agent is. Policy tells you what it is allowed to do. Neither tells you whether its behavior is normal.
  3. Security is moving from signatures to behavior and context. Dynamic Agent Risk looks across identity, data, endpoint, cloud and network signals and asks whether an agent’s actions are drifting from the intent of its task. That is behavioral thinking, and it is philosophically close to the Adaptive AI approach Darktrace has pioneered.
  4. Machine-speed attacks demand machine-speed response. Humans set the objectives and guardrails. Autonomous systems do the work inside them, both detecting and acting. Microsoft’s design has agents investigate, recommend and, within approved boundaries, act, with security teams setting the limits. At this pace, the gap between knowing something is wrong and doing something about it has to close to seconds.

The opportunity: where control plane meets behavioral context

Perception is an extraordinary control plane for agentic security. The question for security leaders is how to make it even more effective in the environments they actually run.

Real enterprises are heterogeneous. They run AWS and Google Cloud alongside Azure, and OT, IoT and third-party identity alongside Entra. Increasingly they also run AI agents and MCP-connected systems that no single vendor’s telemetry fully covers. Microsoft’s architecture recognizes this, with more than 500 connectors into the wider ecosystem.

That is where Darktrace’s role is distinct. The challenge isn’t signal volume, where Microsoft’s scale is unmatched. It’s deeply understanding what is normal for a specific organization, across every system, identity and agent in it. Together, we deliver two complementary layers:

  • Microsoft brings global intelligence and orchestration. It tells you what is known, what it means and what to do about it.
  • Darktrace brings organization-specific behavioral context. It tells you what is unusual here, right now, across the organizations AI, people and infrastructure, even if it has never been seen before.

The difference shows up in the numbers. A large enterprise generates billions of signals. Darktrace turns them into thousands of incidents, narrows those to hundreds of AI-led investigations, and surfaces as few as 20 that merit a human’s attention. For an agentic SOC, that kind of evaluated, prioritized input makes agents faster, not busier.

As enterprises deploy more agents, the hard problem becomes behavior that is technically permitted but unusual, manipulated or inconsistent with the agent’s purpose. Consider an agent that normally reads Salesforce records during US business hours and suddenly starts enumerating SharePoint and opening unusual outbound connections. Each step may use valid access and approved tools, so identity and policy checks can all pass. Spotting it requires knowing the behavior is abnormal for this agent, in this environment, right now.

That is why one principle in Microsoft’s AI Transparency Initiative matters so much: organizations should be able to see what their AI accesses and does, and independently verify those actions.  

  • Identity and permissions answer “should this agent be allowed to do this?”
  • Behavioral defense answers “even though it is allowed, is what it’s doing normal?”

Deterministic controls around non-deterministic AI are the right foundation, and continuously learned baselines are how organizations can verify those controls are working. ‍

What to look for in an agentic SOC architecture

As organizations adopt platforms like Perception, we’d encourage them to look for three capabilities:

  1. Behavioral context in the control plane. Agents work best with high-confidence signals rather than thousands of raw alerts: here is the behavior that materially deviates from this organization’s learned normal.
  2. ‍Behavioral reasoning on demand. During an investigation, agents should be able to ask what changed around a given identity, device or agent in the last 24 hours, and get a clear answer. ‍
  3. Autonomous, coordinated response across the stack. Response should be as fast as the threat without being reckless: acting immediately when confidence is high, constraining or reversing actions when it isn’t, and keeping a human in the loop when it matters. Within policy and human-approval guardrails, it should target the abnormal behavior rather than the whole business process and span identity, endpoint and the wider environment.

These are the areas where we’re focused, and where we look forward to working with Microsoft and the broader ecosystem.

Response is where speed is won or lost

In the AI era, detection and investigation only matter if action follows quickly. Perception brings agentic orchestration to that problem, with security teams setting the guardrails and approving high-impact steps. Autonomous response from Darktrace takes a complementary approach: it responds on behavioral deviation, in a way that is proportionate and targeted. It can interrupt activity that is abnormal for that specific device, identity or agent while leaving normal business activity running.

The two approaches fit together naturally. Behavioral signals can tell an orchestration layer that something has changed and how confident the system is. Orchestrated playbooks can then coordinate wider containment across identity, endpoint and cloud, within the policies customers define.

The bigger picture

The industry’s architecture is converging on identity, policy, telemetry, behavior, autonomous reasoning and machine-speed response. Microsoft is building formidable pieces of that picture, especially identity, policy, telemetry and orchestration.

Behavior is the layer Darktrace is built to provide: an independent intelligence that continuously learns how humans, machines and AI agents normally act, detects the moment reality departs from intent, and can respond to that deviation in a targeted, proportionate way that keeps normal business running. When attacks move at machine speed, understanding what is abnormal and acting on it quickly have to go together.

Perception brings together what Microsoft knows and orchestrates the response across its stack. Darktrace helps organizations understand what is normal for them and act on what isn’t. Customers building their agentic security strategy will need both.

Congratulations to our partners at Microsoft on this milestone. We look forward to helping customers secure the agentic era together.

Learn more about Darktrace Behavioral Defense.

Continue reading
About the author
Kellie Regan
Director, Product Marketing - Cloud Security

Blog

/

AI

/

November 18, 2026

Agentic attacks in the wild: Inside three ARTEX investigations

Default blog imageDefault blog image

Key insights

·       Darktrace observed activity in several customer environments involving infrastructure and behaviors associated with reported ARTEX-enabled campaigns, including activity linked to China-nexus espionage and financially motivated attacks.

·       In the higher-confidence cases, known infrastructure appeared alongside beaconing, unusual TLS, reconnaissance, tunneling, script retrieval, SMB activity and external data transfer. One Azure case had no observed network command and control at all, only key listing and application identity activity.

·       ARTEX is now used by actors with different objectives. Identifying the framework can help locate relevant activity, while the behavior around the affected system provides the stronger evidence for understanding compromise and attribution.

‍

Introduction

Attackers have moved beyond using AI for phishing and are running agentic frameworks; open-source tools like ARTEX, CAIRN, PentAGI and Hexstrike that let AI agents scan, exploit and move through an environment with little human input [1]. ARTEX has moved quickly from an offensive security project into live intrusion activity. Since at least August 2026, the framework has been associated with espionage, financially motivated attacks and opportunistic campaigns across government, financial services, technology, defense, telecommunications and other sectors. The FBI has documented ARTEX activity spanning reconnaissance, exploitation, credential abuse, lateral movement, collection, command and control, and exfiltration [2].

Darktrace has observed activity in customer environments that overlaps with infrastructure, tooling and behaviors reported in several of these campaigns. The cases below highlight how those intrusions appeared on the network, including the activity visible before an analyst can determine which actor or framework may be responsible.

ARTEX as part of the attacker workflow

ARTEX is an open-source, multi-agent offensive security platform that converts high-level objectives into actions carried out by specialized agents [2]. Operators have used it to automate activity across the attack lifecycle, including scanning, exploitation, credential activity and post-compromise operations. Some reported intrusions moved from initial targeting to privileged access in under three hours [2].

The framework is now associated with actors pursuing different objectives and using different post-exploitation tooling. The original public repository was removed in October 2026, but archived copies and localized versions remain available. For defenders, ARTEX is more useful as context for an investigation than as an attribution shortcut.

Darktrace observations show the same point at network level. Infrastructure linked to reported ARTEX campaigns appeared alongside beaconing, tunneling, unusual TLS, reconnaissance, file retrieval and lateral activity.

Case 1: Espionage-linked activity

Darktrace observed activity associated with BLOODALCHEMY command-and-control (C2) infrastructure in two customer environments. In one environment, five devices communicated with nginxmysql[.]com and 45.153.126[.]223 between October 23 and November 2. Both indicators had previously been linked to China-nexus espionage activity involving ARTEX [4].

The connections were accompanied by suspicious beaconing, repeated successful connections and unusual self-signed TLS. One system began making suspicious TLS connections to nginxmysql[.]com on October 23. Beaconing followed on October 24, and SMB scanning appeared later in the sequence. Other affected systems subsequently communicated with previously unseen external endpoints.

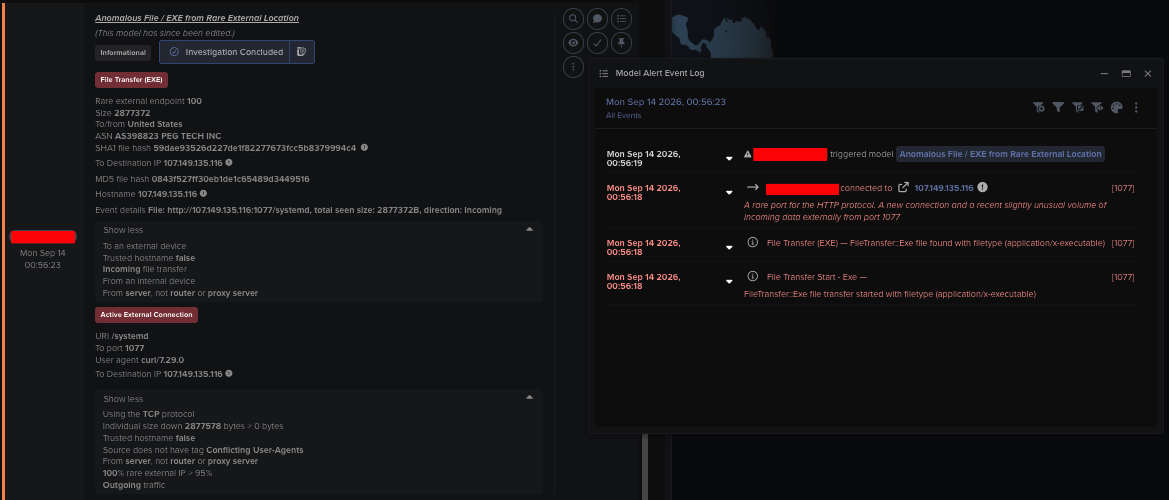
Prior to the observed C2, Darktrace detected curl requests retrieving executable and script content including /systemd, /wazuh, linux_amd64, u.sh and q.sh. Related telemetry included DRSGetNCChanges activity consistent with DCSync, LDAP enumeration, DNS zone transfers, network scanning, certificate downloads and SMB writes involving start.bat.

‍

Figure 1: Darktrace investigation showing suspicious network activity associated with infrastructure linked to reported ARTEX activity.

‍

Figure 2: Darktrace detection showing anomalous self-signed TLS activity during the espionage-linked investigation.

‍

BLOODALCHEMY has been reported in more than one China-nexus cluster [5]. SoftEther infrastructure observed in one environment provided another point of correlation with reported VAPOR PANDA tradecraft. The moderate-confidence assessment tying this to a Chinese nexus threat actor is based on infrastructure, victim context, tradecraft behavior that followed the initial connection, and public reporting.

Case 2: Financial-sector activity

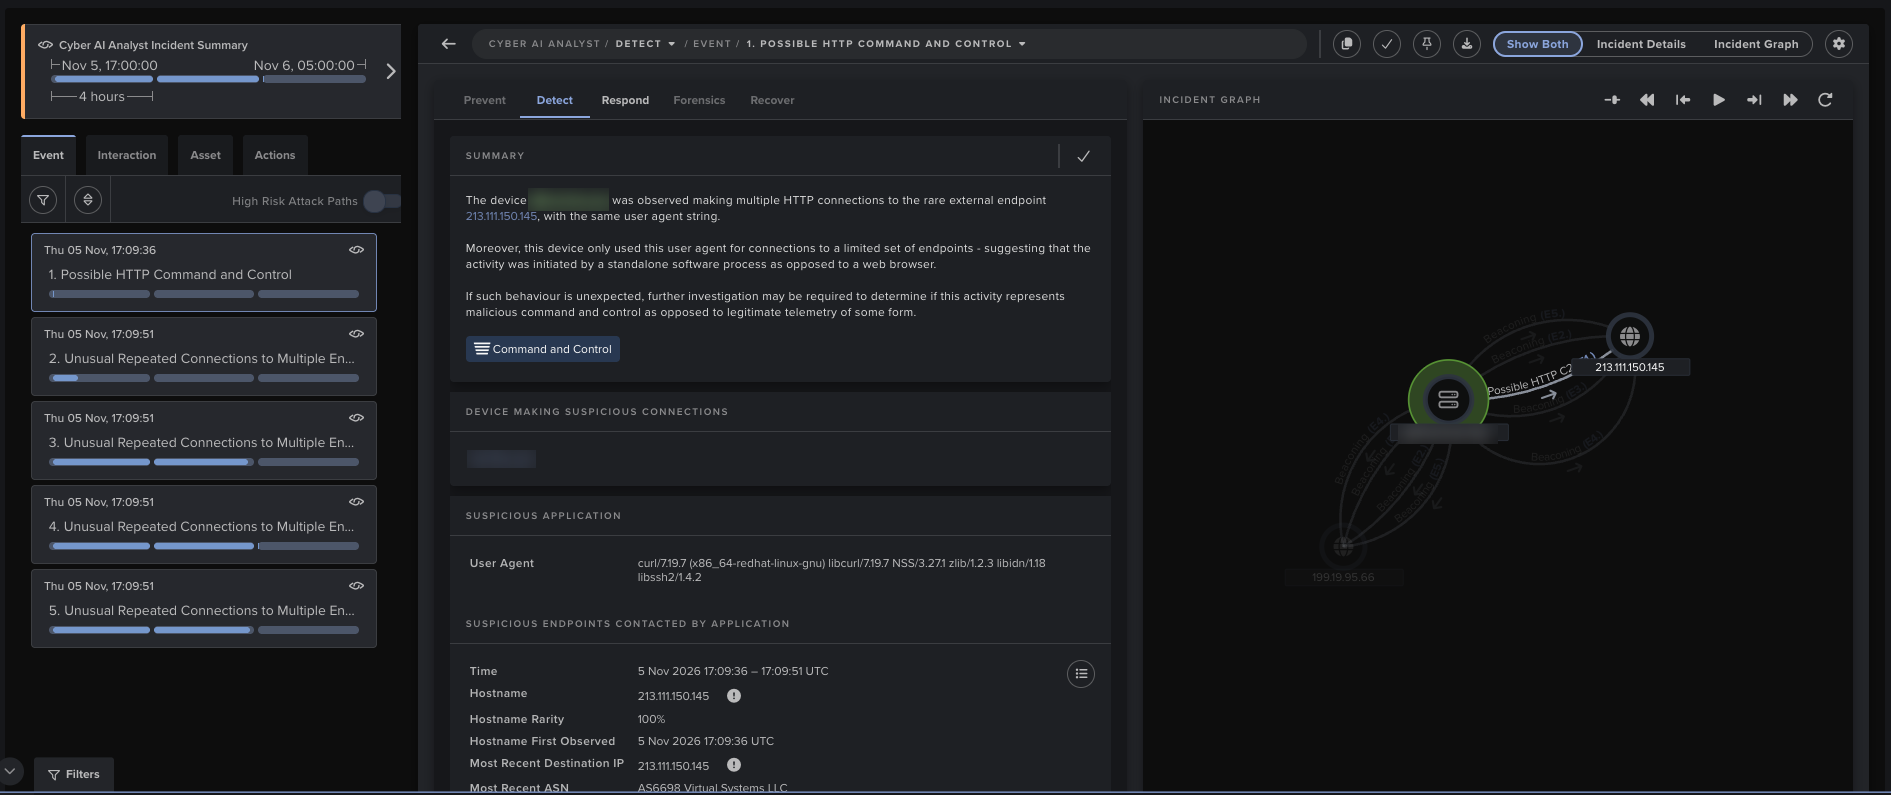
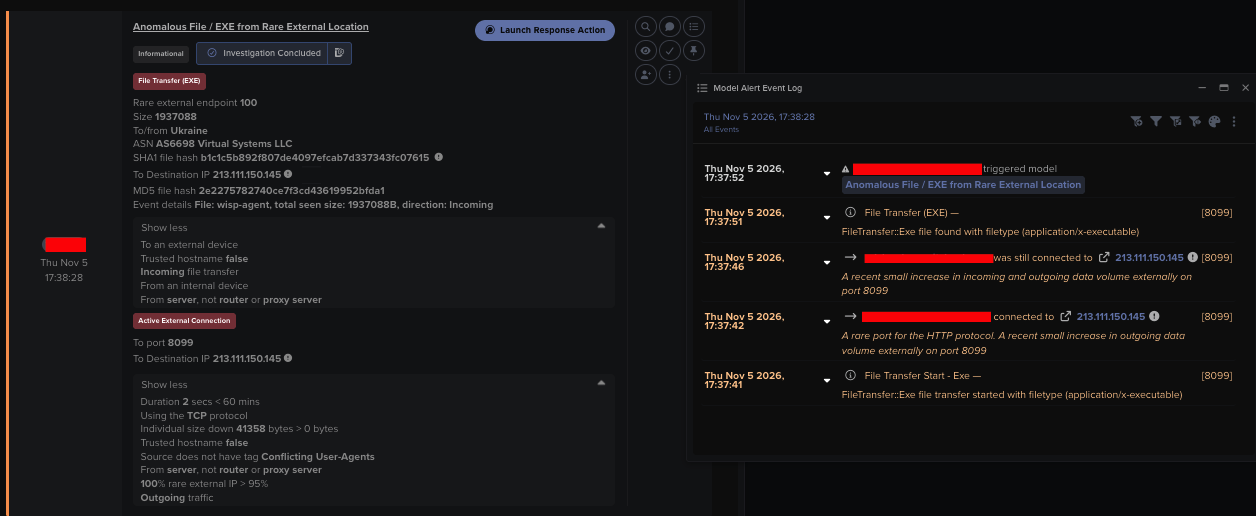
In early November, Darktrace observed activity in two financial-sector environments that overlap with reported ARTEX infrastructure. On November 5, a server connected to 213.111.150[.]145:8099 and downloaded wisp-agent, associated with WISP C2 activity.

‍

In a second environment, a device attempted connections to 85.11.167[.]52 on November 1 and 2. The connections occurred alongside beaconing to new and rare destinations, anomalous TLS, possible tunneling and unusual package downloads.

The device also communicated with temp[.]sh, ssh.localhost[.]run, localhost[.]run, termbin[.]com, pastebin[.]com and GitHub-hosted release infrastructure. The sequence showed potential tooling retrieval, C2, tunneling and use of external services capable of staging or moving data.

Figure 3: Darktrace investigation showing connections to new and rare external destinations during the financial-sector activity.

‍

Case 3: Credential collection in Azure

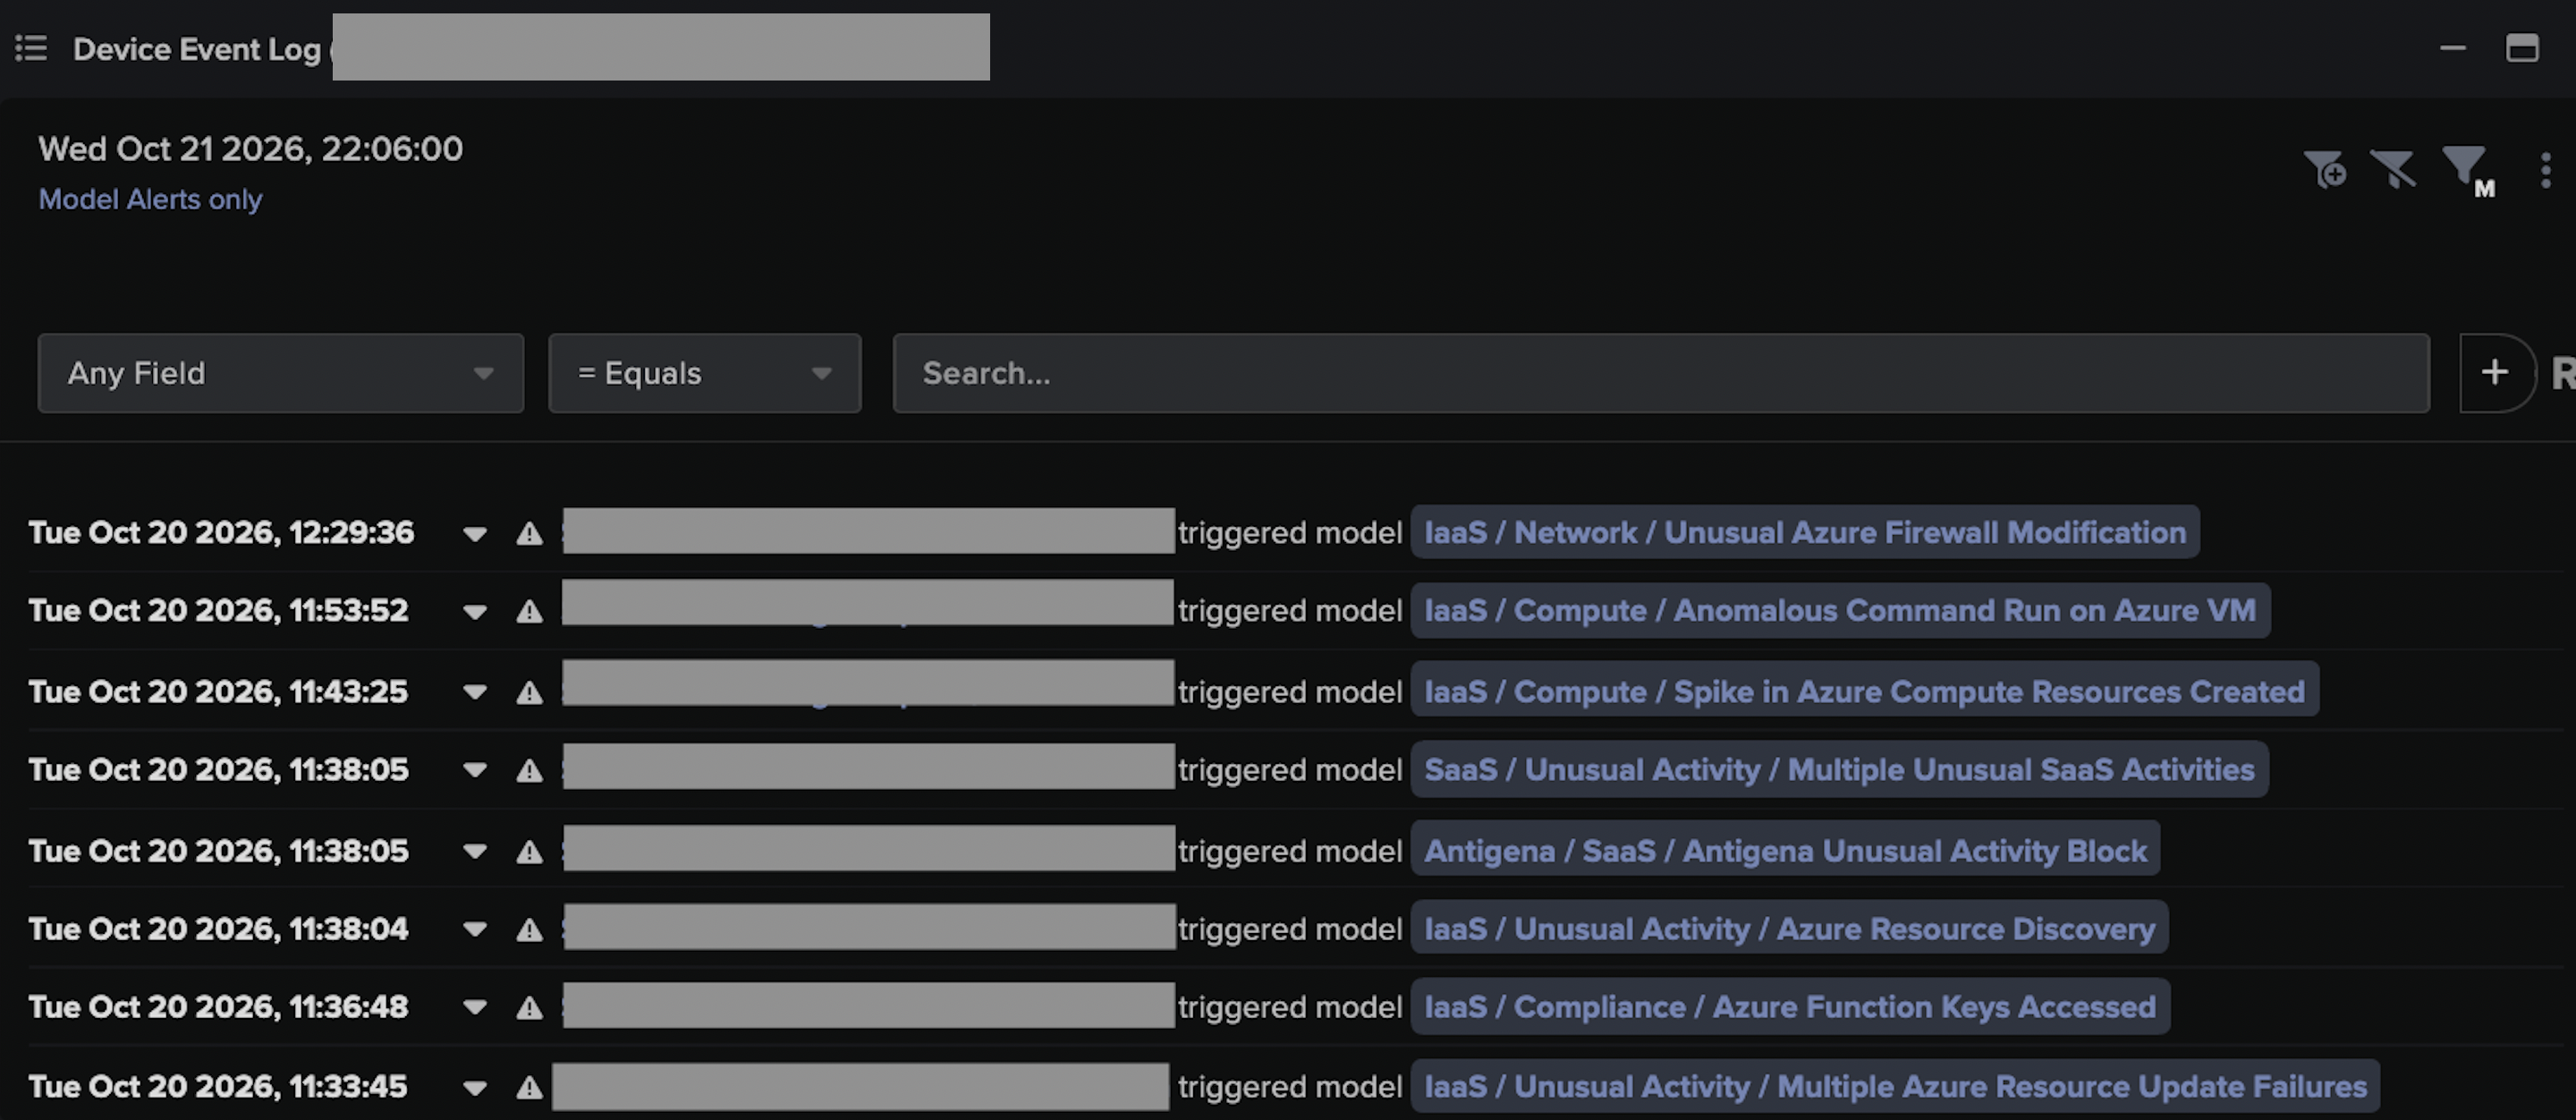
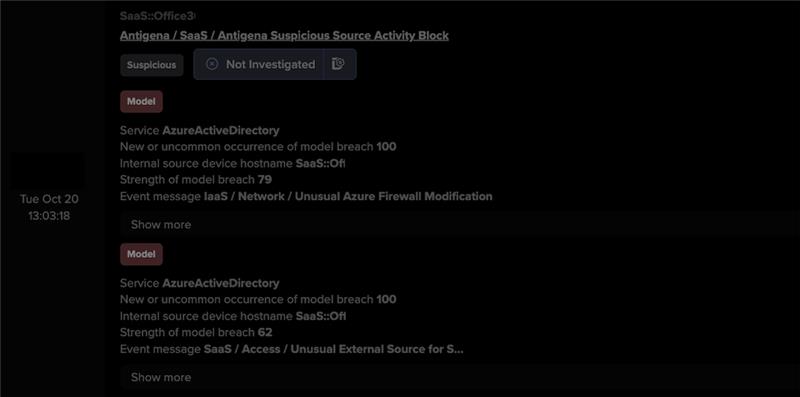
On October 20, Darktrace observed a sweep of credential collection in a customer’s Azure environment that is consistent with ARTEX use. The intrusion began with connections to the virtual network from 43.98.196[.]73 (Alibaba Cloud). Open-source scanning data associates the address with ARTEX.

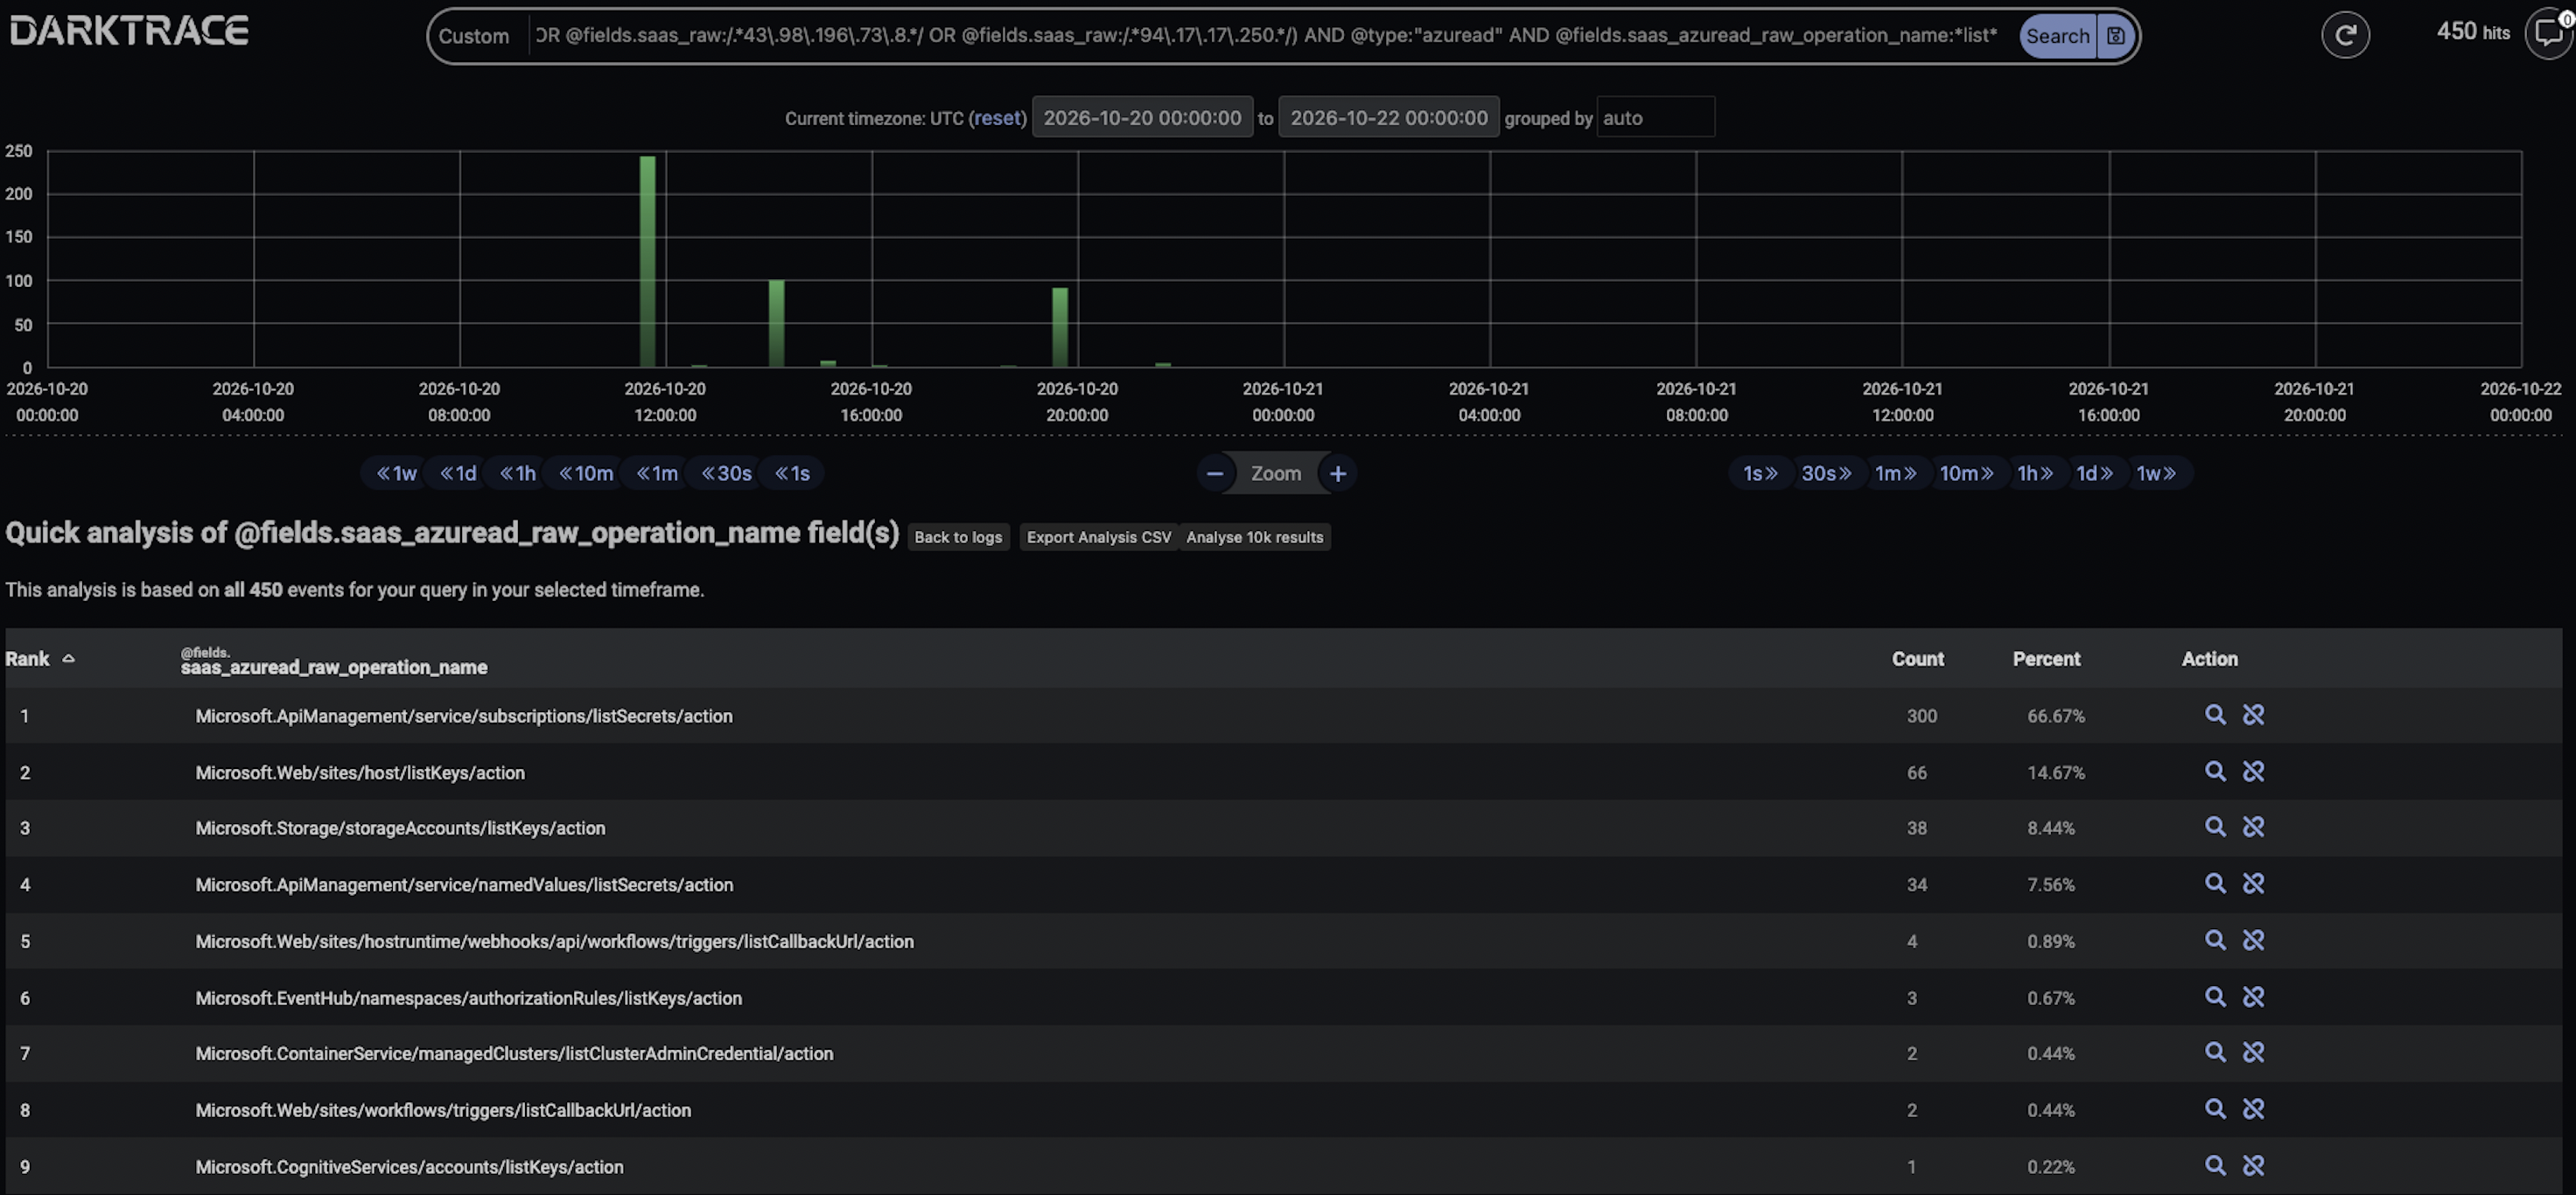
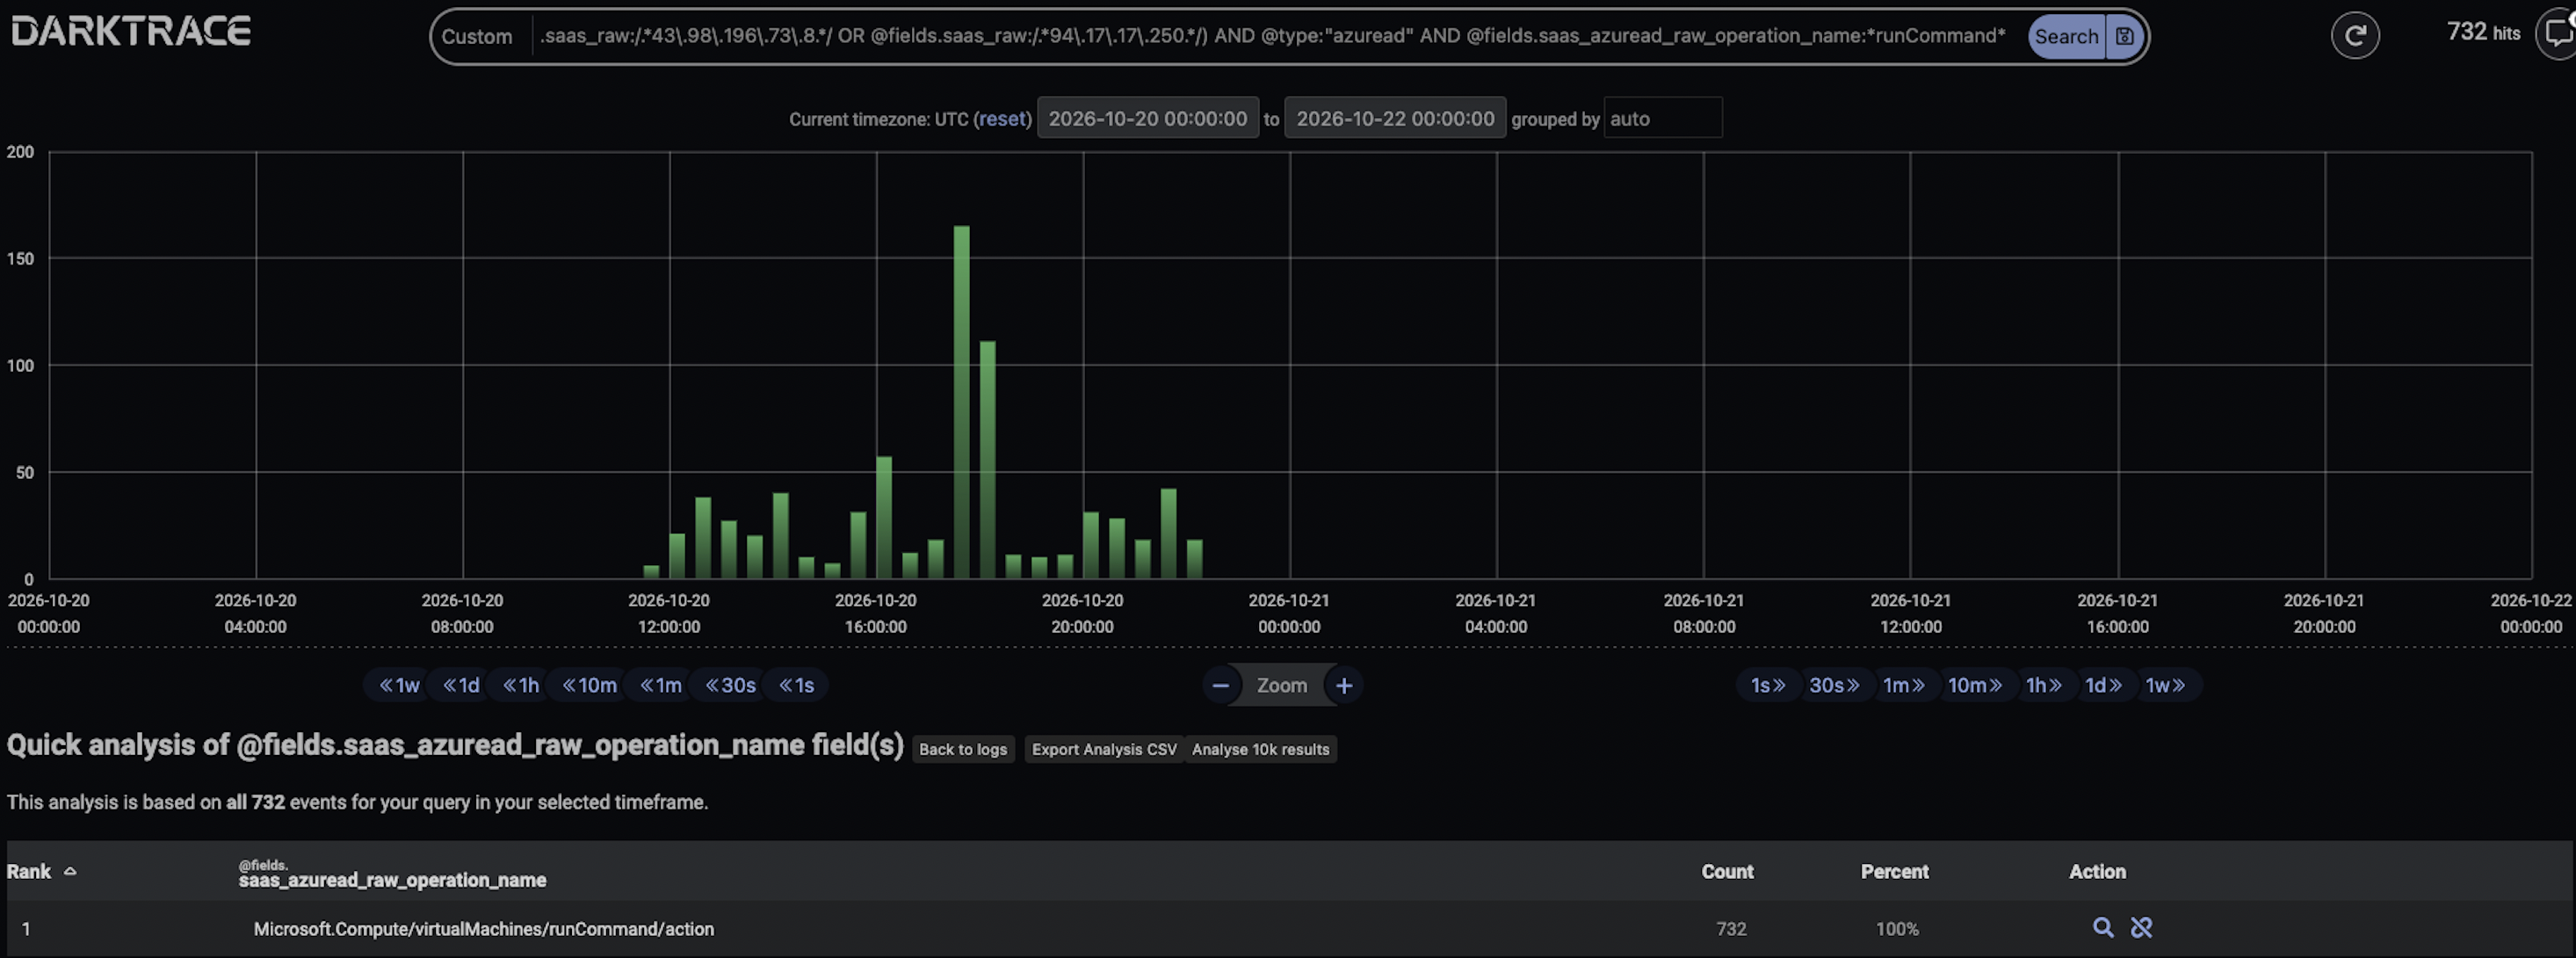
A compromised user identity made requests to the Azure Resource Manager API, though how it was compromised is unknown. The requests listed keys and secrets across API Management, web and function apps, Cognitive Services, Event Hubs, storage accounts and a managed Kubernetes cluster. With those credentials the attacker compromised multiple application identities. The attacker then used the application identities and the user identity to retrieve more credentials, change firewall and security rules and run scripts on virtual machines. Microsoft Defender alerts showed attempted execution of scripts related to Mimikatz and Impacket.

In a cloud environment, such privileged and enumerative operations are potentially indistinguishable from legitimate administrative actions. Consequently, the sequence and context of such operations signified more than any specific API call. There was no C2 traffic to match, and listing keys and using application identities are also what administrators and automation do. A compromised user, credential retrieval across several Azure services, new application identities, more credential collection and changes to security controls only made sense together, and by then access was spreading through the cloud environment.

‍

Figure 4: Darktrace Advanced Search showing Azure AD operation names associated with the activity.

‍

Figure 5: Darktrace Advanced Search showing the Azure Resource Manager action used to execute scripts.
Figure 6: Darktrace Device Event log window showing the triggered models related to the suspicious Azure activity.

‍

Shared tooling weakens attribution signals

The three cases looked different on the network: BLOODALCHEMY infrastructure and espionage-consistent tradecraft, WISP infrastructure in financial-sector systems, and Azure identity and control-plane activity with no C2 at all.

Shared tooling has complicated attribution for years, and ARTEX adds to it because the framework carries out more of the attack, so reconnaissance, exploitation attempts and some post-compromise activity can look the same whoever set the objective. Attribution still needs infrastructure, malware, victimology, timing and the sequence of behavior inside the environment, and an ARTEX link is one input to that. Moreover, the behavior and the agent will still be shaped by the biases, preferences, and tradecraft of its operators.

At its core, ARTEX’s planner and worker agents identify and record facts, while exploring intents. However, the way the Large Language Model (LLM) chooses its next steps toward an objective is shaped fundamentally by the skills and tools available in its context. This includes its starting context, as well as various possible Model Context Protocol (MCP) plugins and user-injected context (e.g. user input mid-operation). Operators still have preferred tradecraft, and this preference shapes the pathways the harness will provide to the LLM in context prompts. Even on the same platform, customization based on operator preferences and goals will remain a key facet of campaign and actor identification.

Detection and response

Across the Darktrace cases, the stronger signals came from behavior after the connection: beaconing, abnormal TLS, reconnaissance, unusual authentication, tunneling, script retrieval, SMB activity and outbound transfer. Automated activity also produced compressed bursts of requests, sequential enumeration and repeated attempts with small changes.

With agentic tools reaching privileged access in under three hours, analysts may have only a short window to connect scanning or authentication activity to credential changes, new administrative access, tooling retrieval or lateral movement. Keeping network, identity and cloud telemetry together shows what happened before and after the first match, and whether a connection was noise or an intrusion moving toward privileged access.

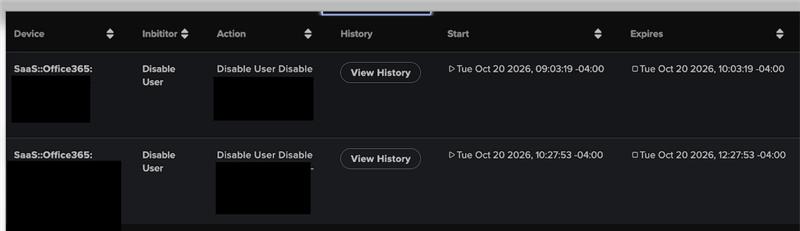
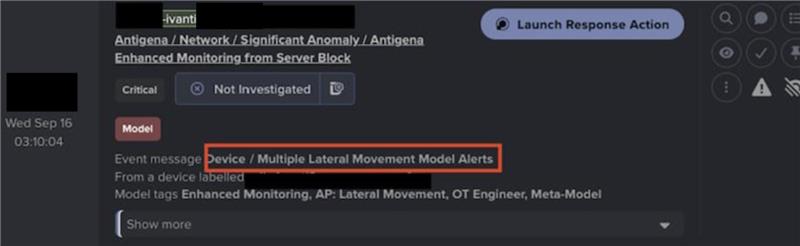
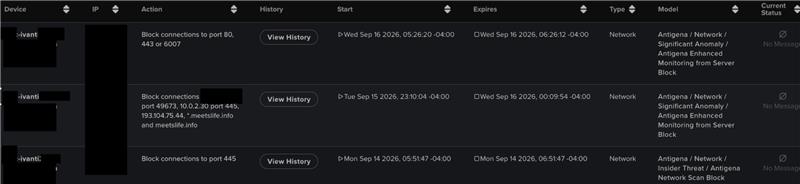
In some of these cases, Darktrace's Autonomous Response took or recommended action against the activity, including blocking internal connectivity over specified ports, inhibiting outbound connections with likely C2 endpoints, and/or disabling SaaS/IaaS user accounts. While many of these recommended actions required human confirmation due to deployment configuration preferences, had these actions been applied autonomously at the time of alert, the scope of activity would have been limited, thereby giving analysts time to investigate and respond.

‍

Figure 7: Autonomous Response blocking suspicious firewall modification activity.

‍

Figure 8: Autonomous Response summary for affected cloud users during the intrusion.

‍

Figure 9: Autonomous Response taking action against unusual lateral movement activity on an affected device.

‍

Figure 10: Autonomous Response summary for affected network users during the time of the intrusion.

ARTEX won’t be the last of these frameworks. The next ones will come with new capabilities and defaults, but an intrusion still must interact with the target environment, and that shows up in how systems, identities and applications behave even after the indicator has aged out. The harder intrusions to catch will have no infrastructure to match, just ordinary API calls and legitimate identities. Detecting those depends on knowing what normal looks like for each identity and device. Containing abnormal activity at machine speed can stop an intrusion progressing while analysts establish impact and its extent. Autonomous Response does not replace that human analysis, but rather augments defender teams' capabilities by extending the window for investigation.

‍

Credit to Nathaniel Jones (SVP, Global Threat Intelligence), Eugene Chua (Principal Analyst), Sam Lister (Senior Security Researcher), Adam Potter (Associate Principal Cyber Analyst)

Edited by Ryan Traill (Content Manager)

Appendices

Darktrace model detections

·       Anomalous Connection / Multiple HTTP POSTs to Rare Hostname

·       Anomalous Connection / Rare External SSL Self-Signed

·       Anomalous Connection / Suspicious Self-Signed SSL

·       Compromise / Large Number of Suspicious Successful Connections

·       Compromise / Suspicious Beaconing Behaviour

·       Compromise / Agent Beacon to New Endpoint

·       Compromise / Beacon to Young Endpoint

·       Compromise / SSL Beaconing to Rare Destination

·       Compromise / Suspicious TLS Beaconing To Rare External

·       Compromise / Possible Tunnelling to Bin Services

·       Device / Anomalous Github Download

·       Device / Anomalous Package Download

·       Device / Initial Attack Chain Activity

Indicators of compromise (IoCs)

nginxmysql[.]com

45.153.126[.]223

213.111.150[.]145

wisp-agent

85.11.167[.]52

43.98.196[.]73

192.121.47[.]20

www[.]ddduuuppp[.]com

89.46.234[.]50

sqlserver-sqlite[.]com

199.19.95[.]66

graphics-hook-filter64.dll

graphics-hook_config.bin

References

1.      Google. GTIG AI Threat Tracker - https://cloud.google.com/blog/topics/threat-intelligence/agentic-threat-activity-crosses-a-significant-threshold

2.      Federal Bureau of Investigation, Threat Overview of ARTEX Autonomous Penetration Testing Framework, FLASH-20261113-001, 13 November 2026: https://www.ic3.gov/CSA/2026/261113.pdf

3.      Microsoft Security Blog, Storm-0940 Uses ARTEX Agentic AI in ConnectWise Supply Chain Compromise: https://www.microsoft.com/en-us/security/blog/2026/10/21/storm-0940-uses-artex-agentic-ai-connectwise-supply-chain-compromise/

4.      CrowdStrike, VAPOR PANDA Uses ARTEX to Scale Global Campaign: https://www.crowdstrike.com/en-us/blog/vapor-panda-uses-artex-to-scale-global-campaign/

5.      Bitdefender, SilkParasite: Tracking a China-Nexus APT Across Central Asia: https://www.bitdefender.com/en-us/blog/businessinsights/silkparasite-tracking-china-nexus-apt-across-central-asia

‍

‍

Continue reading
About the author
Nathaniel Jones
SVP, Global Threat Intelligence
Your data. Our AI.
Elevate your network security with Darktrace AI