
ブログ
/
AI
/
November 9, 2023

Using Darktrace for Threat Hunting

Read about effective threat hunting techniques with Darktrace, focusing on identifying vulnerabilities and improving your security measures.
Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Brianna Luong (Leddy)
Sr. Technical Alliances Manager
Default blog image
09
Nov 2023

What is Threat Hunting?

Threat Hunting is a technique to identify adversaries within an organization that go undetected by traditional security tools.

While a traditional, reactive approach to cyber security often involves automated alerts received and investigated by a security team, threat hunting takes a proactive approach to seek out potential threats and vulnerabilities before they escalate into full-blown security incidents. The benefits of hunting include identifying hidden threats, reducing the dwell time of attackers, and enhancing overall detection and response capabilities.

Threat Hunting Methodology

There are many different methodologies and frameworks for threat hunting, including the Pyramid of Pain, the Sqrrl Hunting Loop, and the MITRE ATT&CK Framework.  While there is not one gold standard on how to conduct threat hunts, the typical process can be broken down into several key steps:

Planning and Hypothesis Creation: Define the scope and objective of the threat hunt. Identify potential targets and predict activity that might be taking place.

Data Collection: Refining data collection methods and gathering data from various sources, including logs, network traffic, and endpoint data.

Data Processing: Data that has been collected needs to be processed to generate information.

Data Analysis: Processed data can then be analyzed for anomalies, indicators of compromise (IoCs), or patterns of suspicious behavior.

Threat Identification: Based on the analysis, threat hunters may identify potential threats or security incidents.

Response: Taking action to mitigate or eradicate identified threats if any.

Documentation and Dissemination: It is important to record any findings or actions taken during the threat hunting process to serve as lessons learned for future reference. Additionally, any new threats or tactics, techniques, and procedures (TTPs) discovered may be shared with the cyber threat intelligence team or the wider community.

Building a Threat Hunting Program

For organizations looking to implement threat hunting as part of their cyber security program, they will need both a data collection source and human analysts as threat hunters.

Data collection and analysis may often be performed through existing security tools including SIEM systems, Network Traffic Analysis tools, endpoint agents, and system logs. On the human side, experienced threat hunters may be hired into an organization, or existing SOC analysts may be upskilled to perform threat hunts.

Leveraging AI security tools such as Darktrace can help to lower the bar in building a threat hunting program, both in analysis of the data and in assisting humans in their investigations.

Threat Hunting in Darktrace

To illustrate the benefits of leveraging Darktrace in threat hunting, we can walk through an example hunt following the key steps outlined above.

Planning and Hypothesis Creation

The initial hypothesis used in defining the scope of a threat hunt can come from several sources: threat intelligence feeds, the threat hunter’s own experience, or an anomaly detection that has been highlighted by Darktrace.

In this case, let’s imagine that this hunt is focused on a recent campaign by an Advanced Persistent Threat (APT). Threat intel has provided known file hashes, Command and Control (C2) IP addresses and domains, and MITRE techniques used by the attacker. The goal is to determine whether any indicators of this threat are present in the organization’s environment.

Data Collection and Data Processing

Darktrace can be deployed to cover an organization’s entire digital estate, including passive network traffic monitoring, cloud environments, and SaaS applications. Self-Learning AI is applied to the raw data to learn normal patterns of life for a specific environment and to highlight deviations from normal that might represent a threat. This data gives threat hunters a starting point in analyzing logs, meta-data, and anomaly detections.

Data Analysis

In the data analysis phase, threat hunters can use the Darktrace platform to search for the IoCs and TTPs identified during planning.

When searching for IoCs such as IP addresses or domain names, hunters can query the environment through the Omnisearch bar in the Darktrace Threat Visualizer. This search can provide a summary of all devices or users contacting a suspicious endpoint. From here the hunters can quickly pivot to identify surrounding activity from the source device.

Figure 1: Search for twitter[.]com (now known as X) as a potential indicator of compromise

Alternately, Darktrace Advanced Search can be used to search for these IoCs, but it also supports queries for file hashes or more advanced searches based on ports, protocols, data volumes, etc.
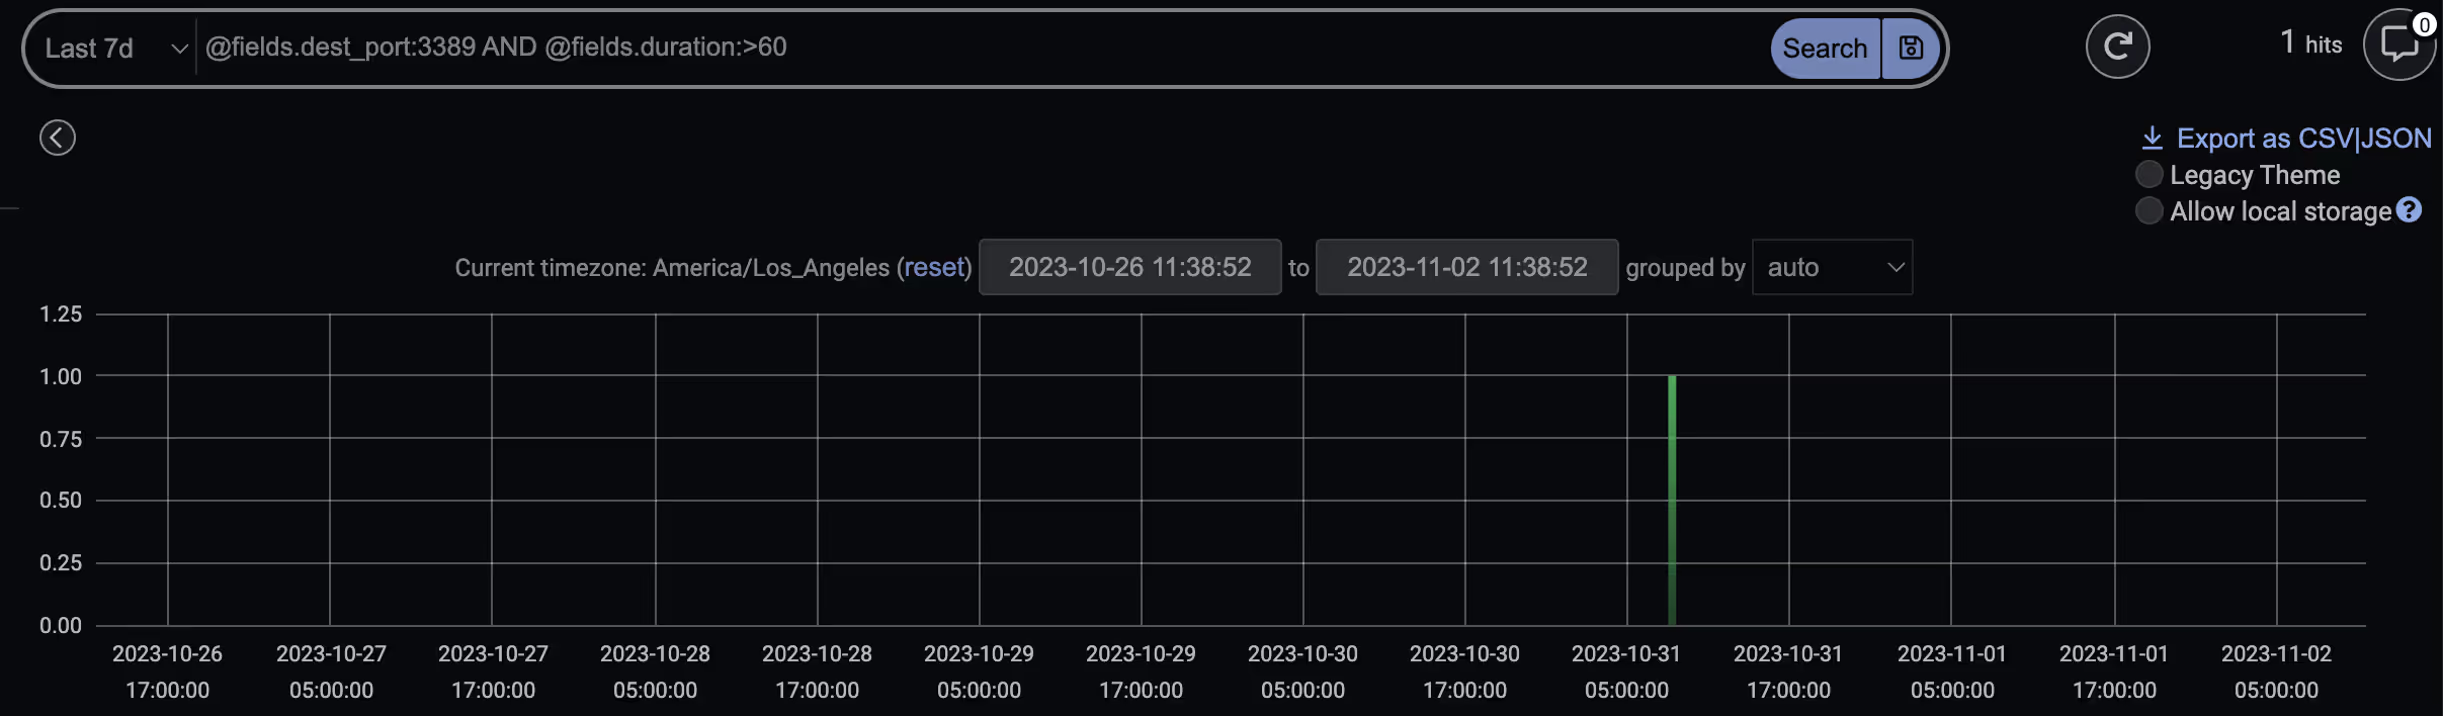
Figure 2: Advanced Search query for connections on port 3389 lasting longer than 60 seconds

While searching for known suspicious domains and IP addresses is straightforward, the real strength of Darktrace lies in the ability to highlight deviations from a device’s ‘normal’ pattern of life. Darktrace has many built-in behavioral models designed to detect common adversary TTPs, all mapped to the MITRE ATT&CK Framework.

In the context of our threat hunt, we know that our target APT uses the Remote Desktop Protocol (RDP) to move laterally within a compromised network, specifically leveraging MITRE technique T1021.001. As each Darktrace model is mapped to MITRE, the threat hunter can search and find specific detection models that may be of interest, in this case the model ‘Anomalous Connection / Unusual Internal Remote Desktop’. From here they can view any devices that may have triggered this model, indicating possible attacker activity.
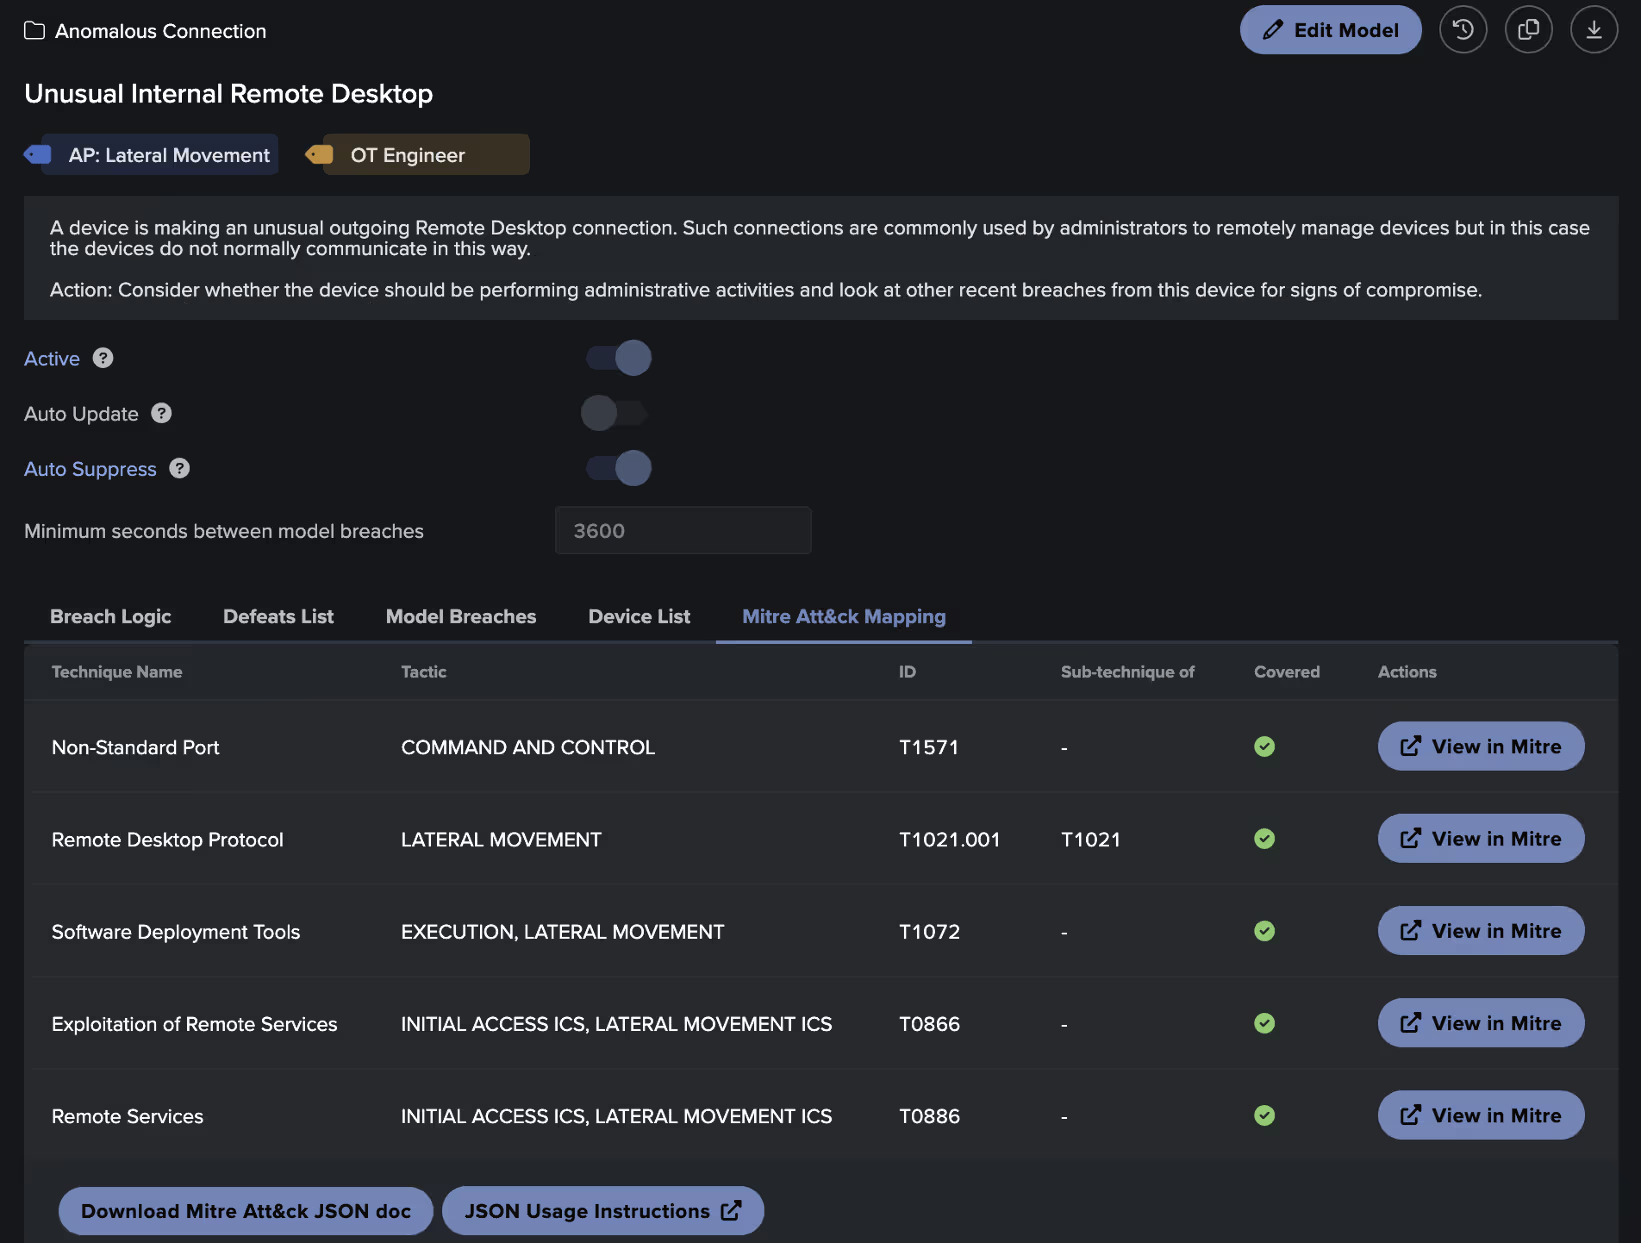
Figure 3: MITRE Mapping details in the Darktrace Model Editor

Threat hunters can also search more widely for any detections within a specific MITRE tactic through filters found on the Darktrace Threat Tray.
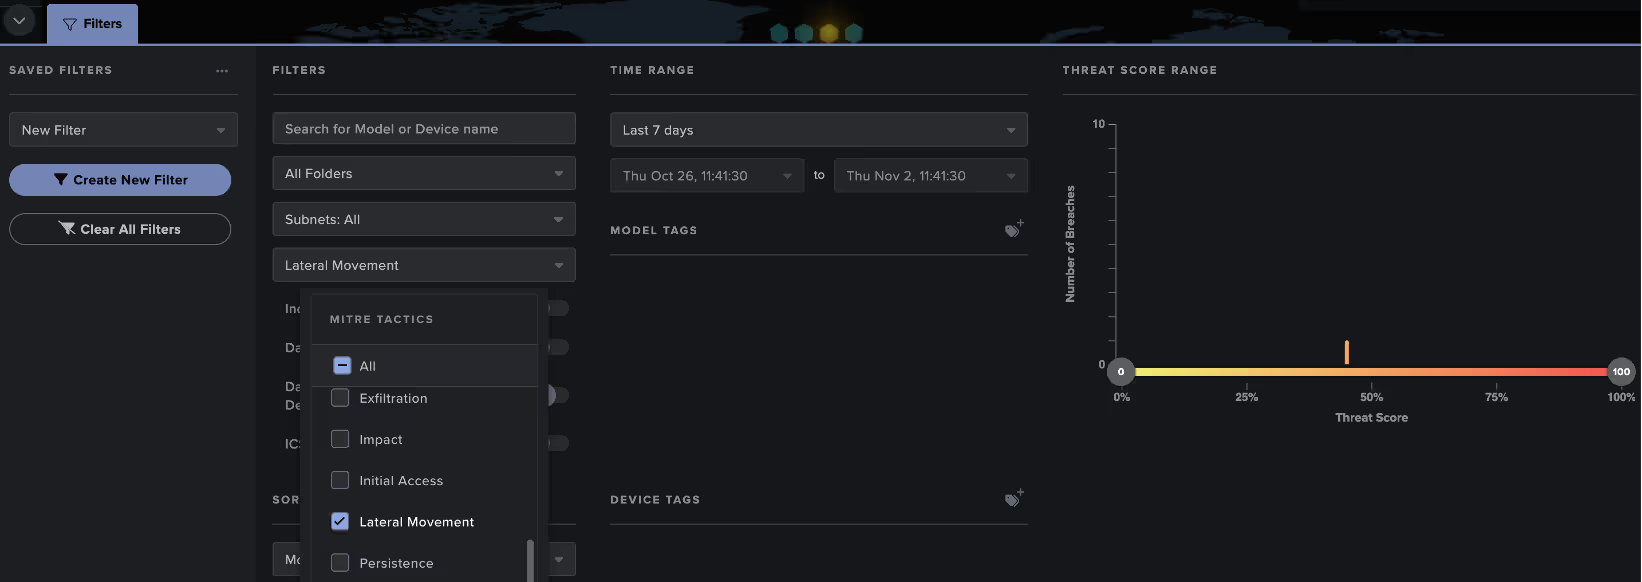
Figure 4: Search for the Lateral Movement MITRE Tactic on the model breach threat tray

Threat Identification

Once a threat hunter has identified connections, model breaches, or anomalies during the analysis phase, they can begin to conduct further investigation to determine if this may represent a security incident.

Threat hunters can use Darktrace to perform deeper analysis through generating packet captures, visualizing surrounding network traffic, and utilizing features like the VirusTotal lookup to consult open-source intelligence (OSINT).

Another powerful tool to augment the hunter’s investigation is the Darktrace Cyber AI Analyst, which assists human teams in the investigation and correlation of behaviors to identify threats. Cyber AI Analyst automatically launches an initial triage of every model breach in the Darktrace platform, but threat hunters can also leverage manual investigations to gain additional context on their findings.

For example, say that an unusual RDP connection of interest was identified through Advanced Search. The hunter can pivot back to the Threat Visualizer and launch an AI Analyst investigation for the source device at the time of the connection. The resulting investigation may provide the hunter with additional suspicious behavior observed around that time, without the need for manual log analysis.
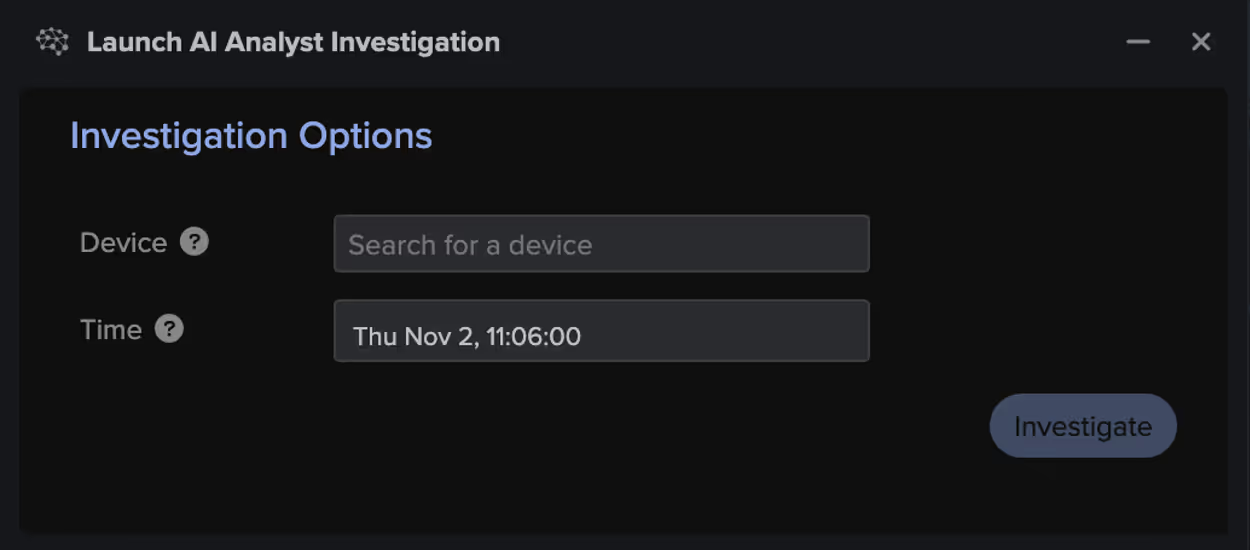
Figure 5: Manual Cyber AI Analyst investigations

Response

If a threat is detected within Darktrace and confirmed by the threat hunter, Darktrace's Autonomous Response can be leveraged to take either autonomous or manual action to contain the threat. This provides the security team with additional time to conduct further investigation, pull forensics, and remediate the threat. This process can be further supported through the bespoke, AI-generated playbooks offered by Darktrace / Incident Readiness & Recovery, allowing an efficient recovery back to normal.
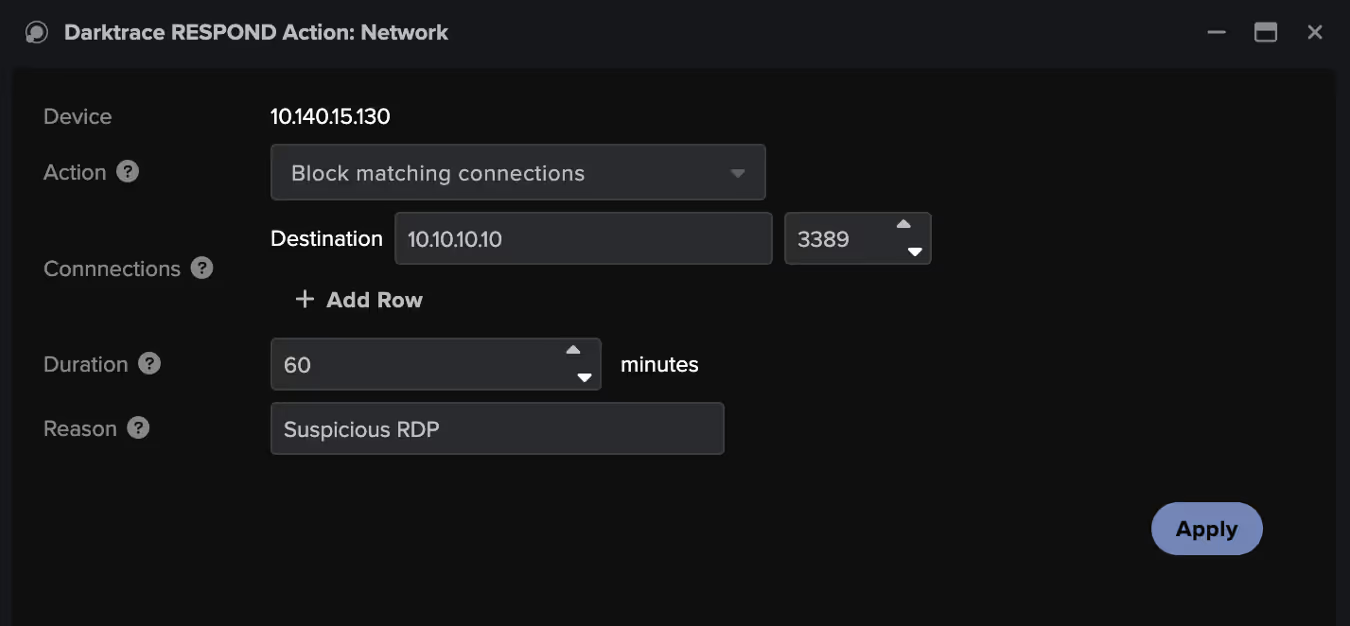
Figure 6: Example of a manual RESPOND action used to block suspicious connectivity on port 3389 to contain possible lateral movement

Documentation and Dissemination

An important final step is to document the threat hunting process and use the results to better improve automated security alerting and response. In Darktrace, reporting can be generated through the Cyber AI Analyst, Advanced Search exports, and model breach details to support documentation.

To improve existing alerting through Darktrace, this may mean creating a new detection model or increasing the priority of existing detections to ensure that these are escalated to the security team in the future. The Darktrace model editor provides users with full visibility into models and allows the creation of custom detections based on use cases or business requirements.
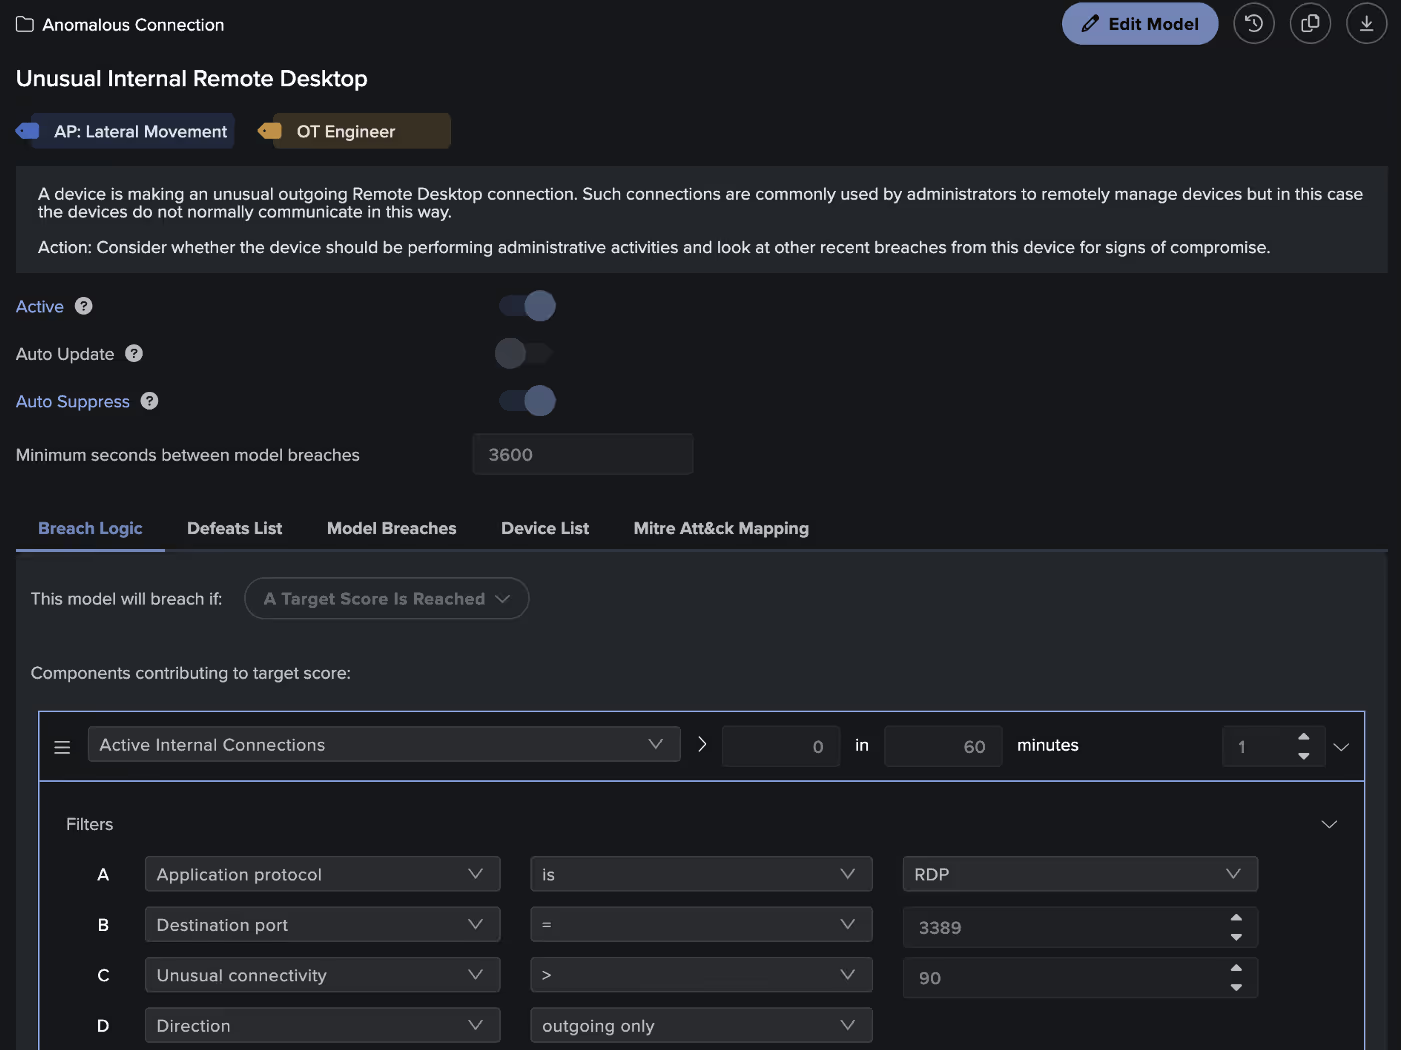
Figure 7: The Darktrace Model Editor showing the Breach Logic configuration

Conclusions

Proactive threat hunting is an important part of a cyber security approach to identify hidden threats, reduce dwell time, and improve incident response. Darktrace’s Self-Learning AI provides a powerful tool for identifying attacker TTPs and augmenting human threat hunters in their process. Utilizing the Darktrace platform, threat hunters can significantly reduce the time required to complete their hunts and mitigate identified threats.

[related-resource]

Get the latest insights on emerging cyber threats

Attackers are adapting, are you ready? This report explores the latest trends shaping the cybersecurity landscape and what defenders need to know

Inside the SOC
Darktrace cyber analysts are world-class experts in threat intelligence, threat hunting and incident response, and provide 24/7 SOC support to thousands of Darktrace customers around the globe. Inside the SOC is exclusively authored by these experts, providing analysis of cyber incidents and threat trends, based on real-world experience in the field.
Written by
Brianna Luong (Leddy)
Sr. Technical Alliances Manager

More in this series

No items found.

Blog

/

AI

/

November 18, 2026

Darktrace qualifies for NATO’s Cybersecurity Dynamic Marketplace

Default blog imageDefault blog image

Darktrace has been selected to join NATO’s Cybersecurity Dynamic Marketplace (CSDM), an initiative designed to give NATO faster, more flexible access to cybersecurity technology and services in support of its missions.  

Established by the NATO Communications and Information Agency (NCIA), the marketplace brings together qualified suppliers whose technical capabilities have been reviewed, helping NATO match specialist expertise to project needs and respond more quickly to changing operational priorities.

Qualified across all eight cybersecurity categories

The program’s first phase, known as Lot 1, covers eight cybersecurity categories. Suppliers can qualify in individual categories; Darktrace has qualified to compete for future work across all eight:

  • Identity, Credential and Access Management
  • Endpoint Protection and Platforms
  • Network and Perimeter Security
  • Cloud Security
  • Threat Detection and Analytics Platforms
  • Vulnerability and Exposure Management
  • Digital Forensics and Evidence Platforms
  • Professional Services

Darktrace’s qualification across all eight categories reflects the breadth of our technology and services.

Supporting government and defense organizations

Nation-state attacks, compromised suppliers, the rapid exploitation of security weaknesses and attackers’ growing use of AI are increasing pressure on public-sector organizations. At the same time, agencies are adopting cloud services, connecting the technology that runs physical operations, and introducing automation and AI. Security teams must manage these changes while keeping essential operations running and sensitive information secure.

Protecting these environments requires an understanding of how people, AI and connected systems interact, and the ability to recognize when their activity creates risk. Threats can span several systems, making it essential for security teams to connect related activity and respond quickly.

The Darktrace Behavioral Defense Platform™ supports this approach through unified visibility, continuous behavioral monitoring and autonomous response across AI, people and infrastructure.

At its core, Darktrace’s Adaptive AI™ continuously learns how each organization behaves, building a unique understanding of its people, AI agents and connected systems. This enables the platform to help identify activity that does not belong, connect related behavior across the organization, and investigate and respond to threats autonomously in real time, helping prevent disruption to essential operations.

Our selection builds on work to meet government security requirements internationally. Darktrace recently completed an independent assessment under Australia’s InfoSec Registered Assessors Program (IRAP) for Darktrace / NETWORK™ and Darktrace / OT™ against the Australian Government’s Information Security Manual PROTECTED-level controls. In the United States, Darktrace Federal continues to deliver the Darktrace technology to Department of War, Department of State, and Federal civilian organizations via its on-premises and FedRAMP CLASS D (High) Authorization platforms.

Together, these achievements demonstrate Darktrace’s ability to meet rigorous public-sector security requirements and reinforce its position as a trusted provider of mission-critical cybersecurity technology for government environments.

Meet us at NATO Edge 2026

Darktrace representatives will attend NATO Edge 2026, NCIA’s flagship technology event, in İzmir, Türkiye, from 17 to 19 November. We look forward to meeting government, military, and industry partners to discuss their cybersecurity priorities and how we can support them.

To learn more about the Darktrace Behavioral Defense Platform, visit the platform hub.

Continue reading
About the author
The Darktrace Community

Blog

/

Network

/

November 17, 2026

GTA VI Cyber Threats: Fake downloads, ransomware and account hijacking

Default blog imageDefault blog image

Key findings

  • Darktrace detected GTA VI-themed suspicious activity across organizations in multiple sectors ahead of the game’s release, showing how malicious gaming content can reach corporate environments outside the gaming industry.
  • Twelve Darktrace customer environments connected to gta6demo[.]asia, a domain that public threat research has associated with a fake GTA VI demo used to distribute the Vidar infostealer. Seven of the twelve communicated with infrastructure associated with AS56322 ServerAstra Kft as part of this connectivity.
  • Darktrace investigated ransomware activity at two European games companies. One incident involved DireWolf ransomware alongside reported data exfiltration. A separate Qilin incident included Active Directory reconnaissance, new administrative credentials, possible lateral movement and substantial cloud-storage transfers before ransomware deployment.
  • Another incident on a gaming organization involved a SaaS account hijack in which a compromised account authenticated from unusual IP addresses, created a new privileged account and subsequently sent a high volume of suspected malicious email. An administrative account later authenticated from rare endpoints.‍
  • Darktrace's new report highlights how threat actors continue to weaponize launch hype to breach corporate networks and target gaming infrastructure following the guilty plea of hacker Arion Kurtaj. These findings demonstrate that global enterprises remain actively exposed to franchise-related social engineering and exploitation attempts.

‍

GTA VI gives criminals an audience

Grand Theft Auto VI arrives on November 19 with the kind of attention few entertainment releases command [1]. Before launch, that interest is already being exploited by sites offering supposed demos and downloads.

During September and October 2026, Darktrace detected devices across multiple customer environments connecting to GTA VI-themed sites associated with suspicious activity. The organizations involved were spread across EMEA and the Americas and included Manufacturing, Finance, and Public administration and defense sectors.

Darktrace has also investigated multiple incidents affecting gaming organizations including ransomware and a SaaS account hijack. Those investigations show a separate side of the threat: attackers operating inside corporate infrastructure and accounts, sometimes well before the eventual impact becomes apparent.

Following a fake GTA VI download

On October 7, 2026, Darktrace detected a device making suspicious DNS requests for gta6-play[.]ru, an unofficial Russian-language GTA VI site that had also been flagged as likely malicious in open-source intelligence (OSINT).

‍

Figure 1: A screenshot of the suspicious endpoint gta6-play[.]ru .

‍

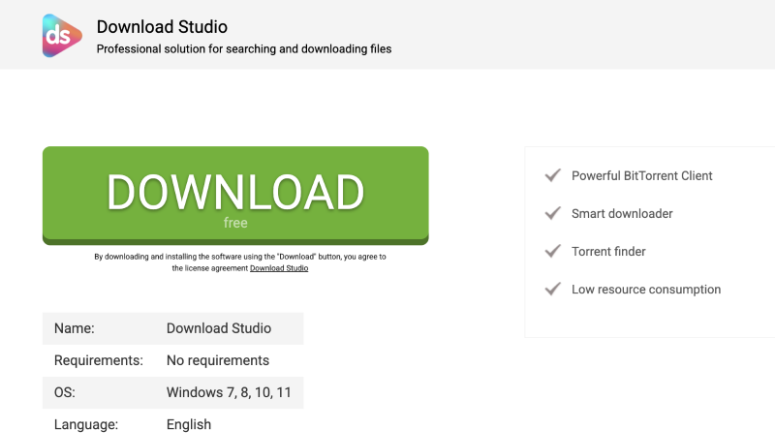
Figure 2: A screenshot of a “Download Studio” endpoint led to on gta6-play[.]ru.

‍

The site advertised a GTA VI download. The site led to a separate “Download Studio” page offering a Windows executable. Analysis found the file was packaged using InstallMate, a commercial installation framework, with an embedded .tsuarch section containing a compressed tiz3 archive.


Further examination identified functionality designed to inspect the environment in which the installer was running. This included checking registry entries for installed software and disk devices, enumerating network adapters, inspecting MAC addresses, and searching for running processes and window titles.


The installer also searched for processes associated with virtualization, debugging, and network analysis, including VMware and VirtualBox components, alongside debugging and monitoring utilities such as OllyDbg, WinDbg, Process Hacker, Process Monitor, Wireshark and Fiddler.

The presence of those checks did not prove that the executable was malicious. The installer contained functionality capable of extracting embedded files, but the investigation did not establish that it was being used to deploy a malicious payload. No definitive malicious payload or command-and-control infrastructure was identified. The software appeared to be InstallRex, which is classified by several security vendors as a potentially unwanted program.

That is still a useful finding; A user looking for GTA VI content could move from an unofficial gaming site to an executable that inspected the local environment, including checking for software commonly used by security researchers.

A second GTA VI lure appeared across twelve organizations

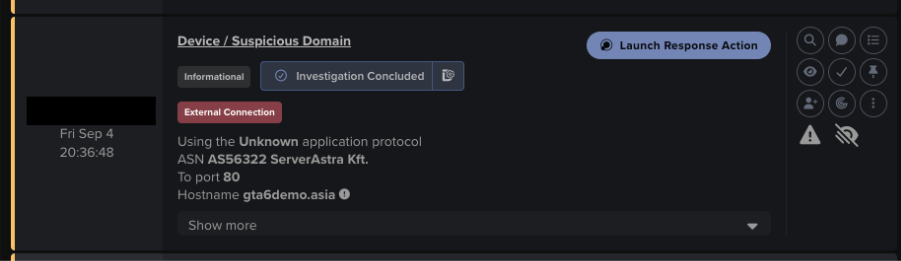
During September 2026, Darktrace alerted on HTTP connections to gta6demo[.]asia across twelve customer environments. Seven of the twelve communicated with infrastructure associated with AS56322 ServerAstra Kft as part of this connectivity.

‍

Figure 3: An example model alert generated due to a suspicious connection to gta6demo[.]asia.

‍

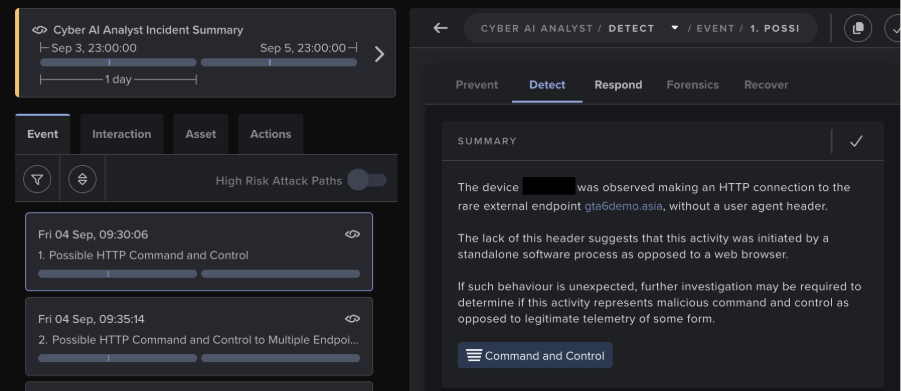
In a case affecting a UK-based customer, Darktrace’s Real-Time AI Analyst further investigated connections to gta6demo[.]asia and generated an incident due to the highly suspicious nature of the behavior.

‍

Figure 4: A Real-Time AI Analyst incident highlighting the suspicious activity for further investigation

‍

Public threat research has associated gta6demo[.]asia with a campaign advertising a fake GTA VI demo. Users clicking "Play Now" were reportedly directed towards an executable containing the Vidar infostealer [2].

There is a practical difference between this activity and an attack against a games company. The users encountering GTA VI-themed infrastructure can work anywhere. Darktrace saw the activity across several sectors outside Gaming, including Finance, Manufacturing, and Public administration and defense.

A major game release can therefore create security exposure well beyond its publisher. A search for a demo or unofficial download on a corporate device is enough to bring gaming-themed infrastructure into an enterprise environment.

Ransomware operators inside the gaming industry

The attacks Darktrace observed against Gaming companies themselves show different patterns.

In August 2026, Darktrace threat research identified possible malicious activity at a European game developer. Ransomware was ultimately deployed and data was exfiltrated, with the DireWolf ransomware group claiming responsibility.

Darktrace observed suspicious file downloads and beaconing from several devices to rare endpoints alongside Monero cryptocurrency mining, Active Directory and network reconnaissance, unusual administrative RDP connections, activity associated with data staging and HTTP-based exfiltration.

Much of the intrusion was therefore visible before ransomware appeared; the environment was already showing evidence of ingress tooling, external command-and-control communications (C2), reconnaissance, unusual administrative access and data movement.

A separate investigation in December 2025 provides a closer view of this pre-ransomware activity. A European games company was targeted by Qilin ransomware with Darktrace observing scanning and LDAP searches involving userAccountControl, which can expose information useful for identifying accounts and Service Principal Names within Active Directory.

New administrative credentials then appeared on a Domain Controller and the Domain Controller also generated scanning, anomalous RPC, SMB, and SSH activity, and NetShareEnum activity through srvsvc. Elsewhere in the environment, long Remote Desktop sessions and SMB enumeration appeared consistent with lateral movement.

Several devices also transferred data to cloud storage services including WebDrive and Amazon Web Services (AWS). In some cases, large downloads preceded subsequent uploads. Darktrace observed the transfer pattern, although the available telemetry does not establish that every transfer represented attacker-controlled exfiltration.

The activity preceding the Qilin deployment included Active Directory reconnaissance, privileged credential use, network and share enumeration, unusual remote access and significant data movement. Each appeared before ransomware became the defining feature of the incident.

SaaS hijacking shifts the attacker evidence

A separate investigation in May 2026 involved the hijacking of a SaaS account at a Gaming organization.

The compromised account authenticated from several IP addresses that were unusual for the organization. It then performed suspicious SaaS group administration, including creating a new privileged account. The account subsequently sent a high volume of emails assessed as likely malicious spam and potentially intended to compromise additional users.

The following day, an administrative SaaS account authenticated from rare endpoints, raising the possibility that further privileged access had been obtained.

The activity presented a different detection problem from the ransomware cases. Authentication from rare infrastructure, administrative changes, creation of a privileged account and subsequent email activity provided the strongest indications that a legitimate identity had been compromised.

For a Gaming company using hosted platforms for development, communication and business operations, a compromised account with the right permissions can provide considerable access without requiring the attacker to reproduce a conventional network intrusion.

Detecting the intrusion before impact

The ransomware investigations show why encryption should not be the first point at which an incident comes into focus. Darktrace observed LDAP and Active Directory-related reconnaissance, new privileged credentials, unusual Domain Controller activity, remote sessions, network enumeration and abnormal data movement before ransomware deployment.

The SaaS case produced different evidence: authentication from rare infrastructure, unexpected administrative changes and activity performed through a compromised account. GTA VI-themed activity required another approach again, following users through unofficial sites and redirects and examining the software offered for download.

GTA VI has put gaming back into the headlines ahead of its November release. The security activity around it is already visible beyond the games industry, while ransomware and account-compromise investigations show attackers operating inside gaming companies through very different routes.

For defenders, those routes leave evidence before the incident reaches its most damaging stage. The practical work is in recognizing those changes early enough to investigate them.

Credit to Gemma Stubberfield (Cyber Analyst), Ahmed Gardezi (Senior Cyber Analyst), Tara Gould (Malware Research Lead), Nathaniel Jones (SVP, Global Threat Intelligence)

References:

1.        https://www.rockstargames.com/VI

2.     https://www.malwarebytes.com/blog/threat-intel/2026/08/fake-gta-6-extended-look-and-demo-sites-deliver-an-infostealer

‍

‍

Continue reading
About the author
Gemma Stubberfield
Cyber Analyst
あなたのデータ × DarktraceのAI
唯一無二のDarktrace AIで、ネットワークセキュリティを次の次元へ